
Summary
- RFC 3993 let a DHCP relay attach a provider-assigned Subscriber-ID intended to remain stable when a customer used a different physical access path.
- The standard carried the value but left its assignment and meaning to provider configuration; that made the label useful for policy and potentially useful for long-term correlation.
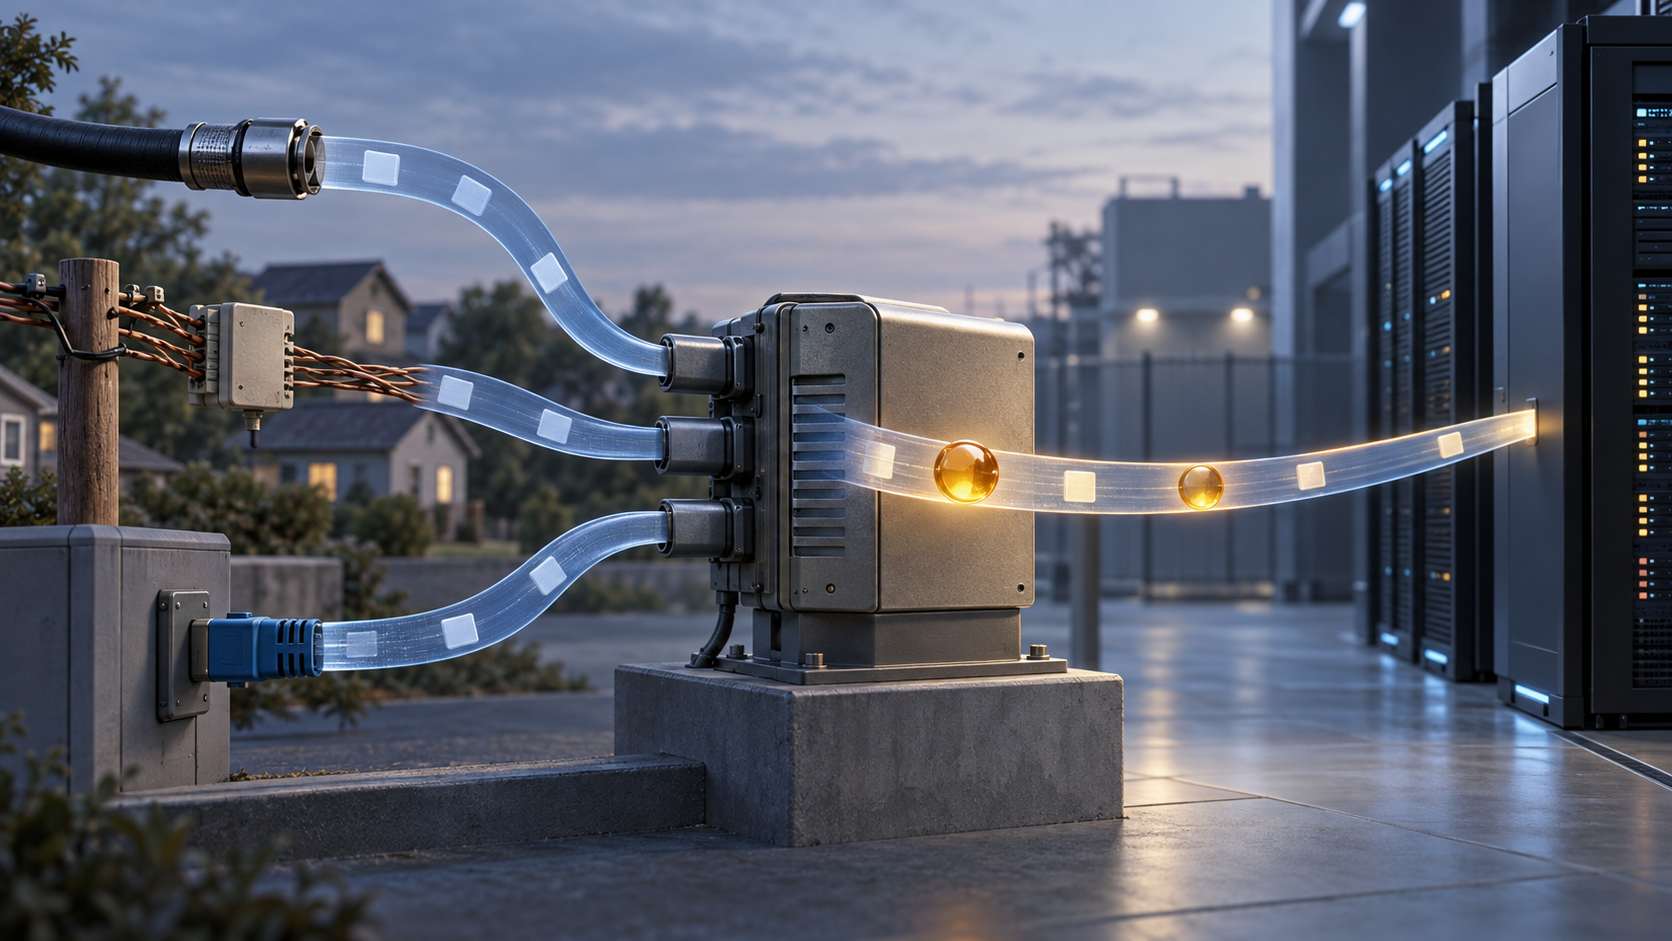
The cable could change while the account stayed
A DHCP server may need to make a decision about a client it cannot see directly. In a large access network, a relay receives a client’s local broadcast and forwards it to a central server. The relay can add information about where the request entered the provider’s network. The server can then return an address and configuration without every access segment needing its own local server.
That arrangement made the relay an observer as well as a messenger. RFC 3046, published in 2001, gave it a container for relay-agent information. Its early fields included Circuit-ID and Remote-ID: one could describe the incoming circuit, the other a remote modem. Such values helped a server distinguish lines and equipment, but they followed the network. Move the customer to another path and the circuit-dependent value might change even if the provider wanted the same administrative treatment.
RFC 3993 addressed that seam. Published in 2005, it added a Subscriber-ID suboption to the existing relay-agent information option. The intended value could be independent of the physical access structure and stay stable as a customer moved between paths or as the network changed. The provider could use it alongside circuit and remote identifiers rather than forcing one field to do both jobs.
The wire carried a value, not a definition
The specification’s restraint is the important part. Subscriber-ID is an NVT ASCII string, carried as suboption code 6 with a one-octet length. It must contain at least one octet and is not NUL-terminated. Those rules tell two systems how to find the value in a message. They do not tell either system what the characters mean.
RFC 3993 says that meaning is provider-specific. The provider assigns the identifier, and the mechanisms used to assign and configure it are outside the memo’s scope. The relay may be configured to include it. A server configured to support it may use it with other relay and client data when assigning an address or other parameters. Neither presence nor downstream use is mandatory.
That division makes the option portable without making it universal. One provider might map a value to a billing account; another could connect it to a service profile. The RFC does not require either model, and the same string need not name the same thing in another administrative domain. A DHCP packet therefore cannot, by itself, establish that a person, device, contract or entitlement has a particular identity. Those links live in the provider’s records and operational choices.
This was a small protocol addition with a consequential control boundary. The client does not supply the provider’s stable label as a self-asserted identity. A relay that the provider operates inserts it, and the central service may make an address or configuration decision from it. The value’s authority comes from the trust arrangement and the provider’s mapping, not from the spelling of the string.
Trust makes the convenience consequential
The relay-agent information option depends on a trusted relationship between relay and server. RFC 3993 warns that fraudulent data could contribute to service theft, exhaustion of scarce addresses, denial of service or unsuitable configuration. RFC 3046 describes the option’s return path: a recognizing server echoes relay information to the relay, which strips it before sending the response to the client. That keeps this provider-side control exchange distinct from a client-facing identity certificate.
The trust boundary can be strengthened. RFC 3993 points to perimeter defenses and recommends deeper protection through the separate DHCP relay Authentication suboption or IPsec. RFC 4030 specifies the Authentication suboption, including replay-detection procedures. Authentication can help establish that relay-option data came through an accepted path; it still cannot supply the provider-specific meaning that RFC 3993 intentionally leaves elsewhere.
Stability also creates a privacy tradeoff. A circuit identifier can reveal where a message entered the network. A subscriber identifier can follow the administrative subject across circuits. RFC 3993 warns that the value may identify a particular host or user if exposed. RFC 7819 later treats Subscriber-ID as a possible long-lived identifier that can connect activity over time. The benefit that reduces reconfiguration can also lengthen the period across which records are linkable.
RFC 4580 carried a similar idea into DHCPv6. It likewise leaves assignment and meaning outside the specification and limits the intended exchange to one administrative domain. That parallel confirms the design pattern, not automatic equivalence between a DHCPv4 label and a DHCPv6 label.
The RFCs establish the intended mechanism and its stated risks. They do not show how widely operators deployed it, whether a particular customer moved successfully, or what privacy controls a provider used. The history here is therefore a design boundary: DHCP could carry a provider’s stable label across a changing access topology, while the provider remained responsible for what that label meant and what decisions followed.
Sources
- RFC 3993 — Subscriber-ID Suboption
- RFC Editor record — RFC 3993 status and publication details
- RFC 2131 — Dynamic Host Configuration Protocol (DHCP)
- RFC 3046 — DHCP Relay Agent Information Option
- RFC 4030 — DHCP Relay Agent Authentication Suboption
- RFC 4580 — DHCPv6 Relay Agent Subscriber-ID Option
- RFC 7819 — Privacy Considerations for DHCP
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance