
Topic
Institutional Legitimacy
Within the Topic facet, Institutional Legitimacy topic intelligence connects articles that share a specific subject, signal focus, or monitoring theme. The page gives readers a richer path through related reporting, source evidence, market actors, and infrastructure implications, with enough context to understand why the topic matters across company movements, governance decisions, regional exposure, and operational risk. Readers can compare recurring signals, affected organisations, public evidence, market context, service continuity, procurement, competition, compliance, and strategic planning questions behind the subject instead of stopping at a thin list of matching articles. It explains what the topic covers, which infrastructure actors or policies are involved, what evidence supports the coverage, and why the subject may matter for operators, customers, investors, and policy readers.
Europe and Middle East Institutional Trends
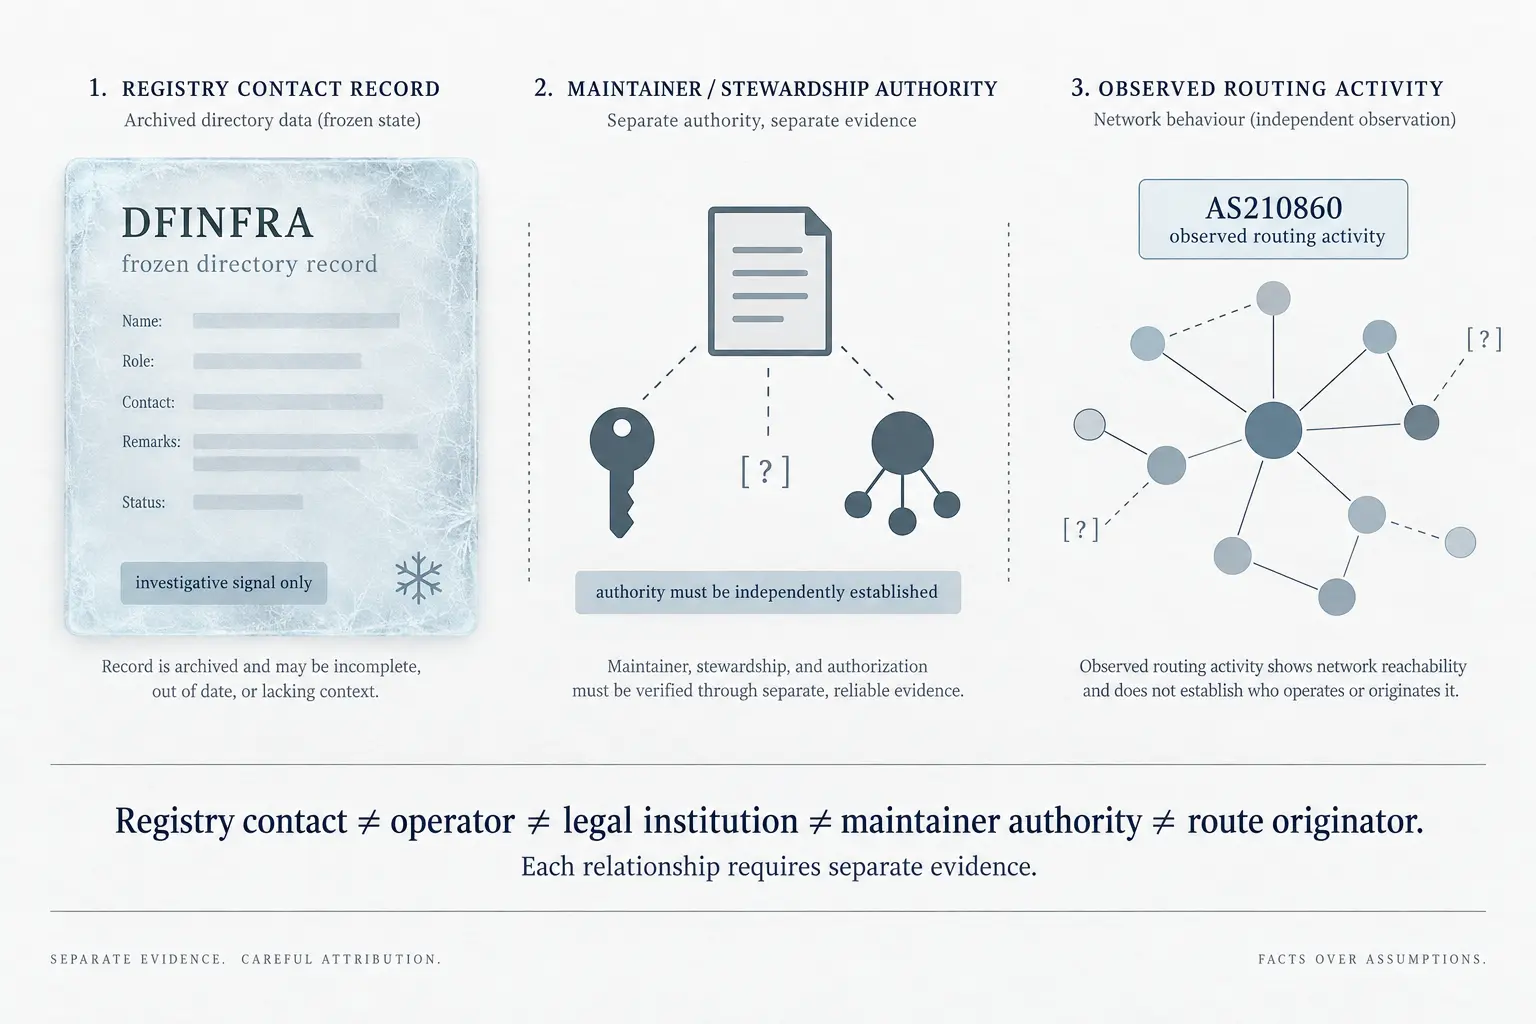
DFINFRA Is a Registry Signal, Not Yet Proof of an Operator
DFINFRA Is a Registry Signal, Not Yet Proof of an Operator intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that may follow. The Europe…

Global Institutional Trends
Who can challenge ISC’s practical authority?
ISC’s public pages show where its stewardship matters. They do not, by themselves, show who can contest consequential decisions or what remedy follows.

Story
DATAMATIX and AS210973: What Public Routing Evidence Can—and Cannot—Prove
DATAMATIX and AS210973: What Public Routing Evidence Can—and Cannot—Prove intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that may…

IETF
OpenPGP’s New Algorithm Numbers Rewrite the Test Vectors
Eight numbers are moving through OpenPGP’s standards machinery. In the published draft they are experimental values 100 through 107; in an open editing branch they are 37 through 44; in the public IANA registry those lower slots remain unassigned. The discrepancy is not cosmetic.…

IETF
ELA’s Voucher Arrives After the Device Identifies Itself
In a zero-touch join, the smallest interval can carry the largest governance consequence. A new device using the proposed ELA protocol authenticates a domain gateway, sends its credential identifier and waits while that gateway asks an enrollment server for authorization. Only in…

IETF
An Enrollment Voucher Arrives After Identity Leaves the Device
A constrained device can withhold its operational identity and still disclose enough to be enrolled. In Lightweight Authorization using EDHOC, that disclosure is deliberate: an authenticated domain authenticator receives the device’s enrollment identity and sends it to a trusted…

IETF
A Cryptographic Malfeasance Report Cannot Revoke Trust
Three time servers sign answers that cannot all be true in the order they were received. Roughtime lets a client preserve that contradiction as portable cryptographic evidence. Yet the proof does not name the guilty server, appoint the reviewer, alter a trusted-server list or…

Story
APNIC’s leadership-diversity consultation needs a measurable participation funnel
APNIC has documented who joined the first stage of its leadership-diversity consultation and what barriers they described. The next test is whether it can connect outreach, participation and proposed remedies to a broader leadership pipeline without identifying individual…

IETF
A Private Candidate Does Not Explain Why One Intent Won
Two engineers are authorized to change the same router. Each works in a private configuration branch, so neither can accidentally commit the other’s unfinished commands. Then both change the same node. The server can identify the collision and offer disciplined ways to resolve…

IETF
An OAuth Challenge Can Be Reused Unless the Server Says No
An OAuth client receives a fresh server challenge, builds a proof around it and sends the request. May the same challenge be used again? Revision 11 of the IETF OAuth working group’s attestation-based client-authentication draft gives a precise but surprising answer: the client…

Story
ARIN Described a Two-Person Rule for AI Drafts. It Did Not Describe the Receipt
ARIN’s public answer was unusually concrete: generative AI may assist a narrow class of drafts, the drafter remains responsible, and a second person reviews the result before release. The missing piece is not another principle but the durable record that proves those decisions…

IETF
DAWN Can Filter an Agent Record. Its Export Boundary Is Not in the Record
Revision 01 of a proposed architecture for discovering AI agents across organisations puts an Export Policy Engine at the boundary of every site. The gateway may choose which records each peer receives and strip sensitive fields before anything leaves. Yet the record that travels…

History
The RFC Called Them Truths. The Errata Kept Them Opinions: RFC 1925
A missing period can be verified. A universal truth cannot. That unexpectedly precise distinction appears in the errata record of RFC 1925, the April Fools’ document that gave networking twelve durable aphorisms. The archive can repair its punctuation and preserve its jokes; it…

IETF
An IETF Draft Gives the Ops Section Five Answers. Its Heading Shows None
Revision 07 of an IETF operations draft has made a useful idea much more precise: a future technical RFC would always carry an Operational Considerations section, but that section could legitimately do five different things. The same revision says a fixed location may help tools…

Story
APNIC’s NIR SIG Asked Four Charter Questions. Its Deck Shows One Unlabelled Result
An APNIC 62 charter-review deck asks seven National Internet Registries four different questions, then places one 86% support chart beside them without saying which question it answers. The proposed charter may still deserve support. But if the NIR SIG is to consolidate views for…

IETF
IETF’s ICMP Node-ID Draft Says “MUST”—and “Disabled by Default”
The latest IETF draft for identifying the node behind an ICMP error contains two instructions that look opposed when lifted out of context. Revision 05 says the new entity must be added when the ordinary response address may be limited public evidence, unless policy or security…

IETF
IRTF Chair Nominations Close Today. The Workload Has Two Speeds
The next IRTF Chair is being recruited for a role described with an unusually candid pair of numbers: about a quarter of normal working time, then full-time attention for roughly six weeks each year. Nominations close at 23:59 UTC on 8 September. The IAB should preserve that…

Story
The RIR Draft Calls the System Bottom-Up. Status-Change Consultations Stay Optional
The recommended RIR Governance Document describes the Internet Numbers Registry System as open and bottom-up. A few pages later, its new Article 2.7 says neither the RIRs nor ICANN are obliged to consult their communities when assessing a proposal to recognise or derecognise a…

Creators
Roy Arends and the hard work of changing DNS safely
Roy Arends helped write the 2005 specifications that made modern DNSSEC interoperable across implementations. Two decades later, his work at ICANN focuses on a harder operational problem: changing keys, error signals and delegation in a global system that no organisation can…

CASE FILE
W3C Combined Two Accessibility Calls. It Did Not Combine Their Mandates
Two calendars can become one without two institutions becoming the same institution. W3C’s Fixed Layout Accessibility Task Force has cancelled its separate call series and is moving its work into a joint accessibility meeting. That is a sensible reduction in coordination…