
Summary
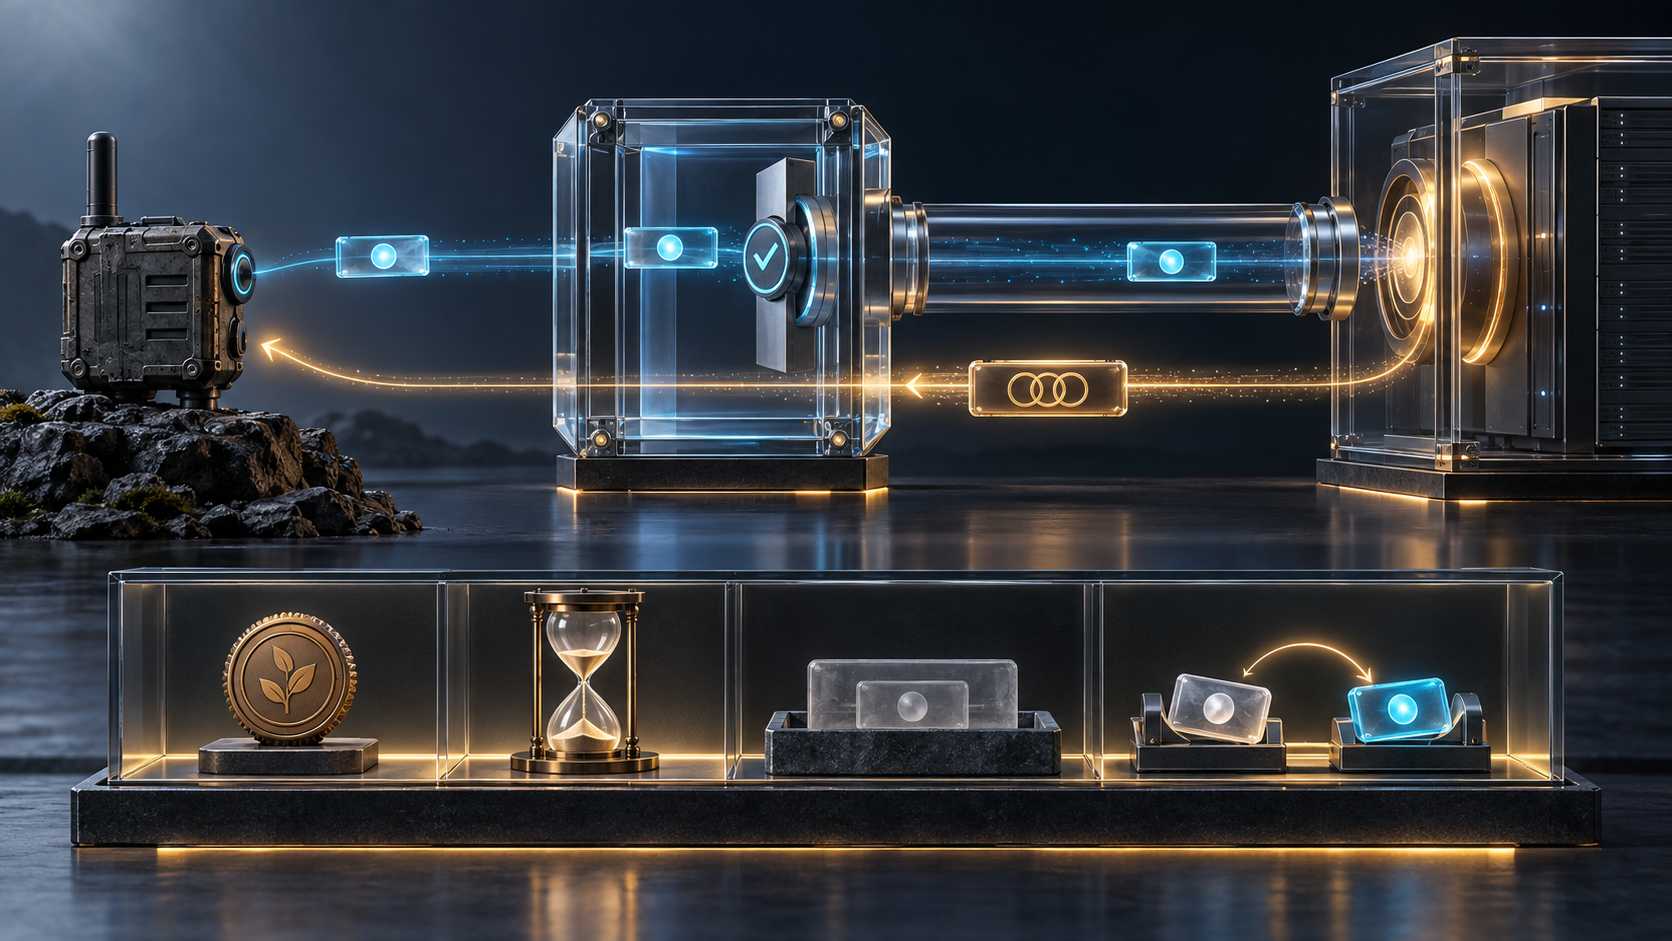
- ELA gives constrained-device enrollment a strong third-party authorization path: W evaluates U, V proves the credential it showed U, and the resulting voucher is bound to the EDHOC session, U’s identity and V’s credential.
- The security boundary is temporal. ELA intentionally reveals U’s identity to an authenticated V before U knows whether W will authorize the enrollment. A refusal can terminate the protocol but does not specify what V or W retain, correlate or disclose afterward.
- An identity-release receipt should govern purpose, recipients, retention, denial cleanup and the switch to a distinct operational identity. This is Daniel Kade’s editorial proposal, not an IETF field or requirement.
The decision follows the disclosure
Consider a sensor arriving at a new domain with no local account and no prior relationship with the network controller. It does know one distant authority. The device, called U in the draft, has the static public key and location of an enrollment server W. A nearby domain authenticator V wants to admit it. ELA lets the three participants test that relationship while reusing the compact EDHOC exchange.
The checked specification is draft-ietf-lake-authz-08, published on 6 July 2026. The Datatracker recorded its move into LAKE Working Group Last Call on 8 September 2026. At the 9 September 2026 research cutoff it remained an active Internet-Draft intended for Proposed Standard, not a published RFC; its process state may advance after that cutoff.
The sequence matters more than the cast. U begins EDHOC and presents ID_CRED_I, an identity that W can resolve unambiguously. V is authenticated to U, then uses that identity in its protected exchange with W. W applies a local authorization policy and evaluates whether this U may enroll through this V. V proves possession of the key associated with the same CRED_V it showed U. If the checks succeed, W’s result returns toward U as a voucher.
The voucher is not a loose permission slip. It is W’s assertion to U that W has authorized V. It is tied to the current EDHOC transcript through H_12, to U through ID_CRED_I, and to V through CRED_V; it may include opaque scope. Successful interaction with W is required before the exchange proceeds, and completion through message_4 means U and V are authorized to interact under the result.
That is a substantial cryptographic achievement. It reduces constrained-link traffic by running enrollment authorization alongside authentication, rather than building a second ceremony after the channel exists. It also makes substitution harder: a voucher for another device, authenticator or transcript is not the same object.
But U learns the answer after V has learned who U is. The draft says so plainly in its security considerations. EDHOC protects an initiator’s identity against passive observers and unauthenticated peers within its threat model; ELA intentionally reveals that identity to an authenticated V before authorization succeeds. Authentication establishes which credential V controls. It does not establish that V was entitled to receive and retain every identity sent while seeking authorization.
A valid voucher answers a narrow question
It is easy to use “authorization” as if it covered the whole encounter. ELA is more exact. W decides whether U may enroll with V. U verifies W’s approval of V in this session. The result can carry scope. None of those facts alone defines the legitimacy of W’s policy, who wrote it, whether it is current, how an erroneous entry is corrected or what downstream services will permit after enrollment.
Session binding and disclosure governance are similarly different. H_12 prevents the decision from floating free of the exchange. ID_CRED_I and CRED_V connect the decision to the relevant participants. Those bindings say nothing about whether an access log may preserve U’s identifier for a week, whether W may join it with manufacturer records, whether V may share a failed attempt with another controller, or how a device owner contests a mistaken denial.
The distinction is not an accusation about an implementation. The checked Internet-Draft defines a protocol, not a data-retention regime. Authorization policy is explicitly outside its scope. No cited source establishes that any deployment is retaining identities improperly. The point is narrower: cryptographic completeness cannot be used as evidence that the institutional lifecycle is complete.
An onboarding identity helps only when it can end
ELA offers an important mitigation. U may use an identity only for onboarding and later use a different operational identity. This can prevent routine traffic from carrying the credential exposed during enrollment. It can also make a captured onboarding identifier less useful for tracking ordinary device activity.
The word “may” is doing real work. The draft does not mandate a separate identity, prescribe its rotation, require it to be unique per domain, or order V and W to delete it after success or failure. A supposedly temporary identifier can become a durable correlation key if it is reused across networks, retained in denial logs or joined to the operational account.
The control therefore needs two edges. The first is release: before U sends ID_CRED_I, it should know the class of party represented by V, which W will receive the claim, the stated enrollment purpose and the promised handling of a refused attempt. The second is retirement: after successful enrollment, the system should record when the onboarding identity ceased to authorize anything and when the distinct operational identity became active.
Neither edge needs to expose more personal or device data. A useful record can hash or pseudonymize the session reference, name policy versions and preserve reason classes rather than publish raw identifiers. Data minimization is not the absence of accountability; it is accountability that does not create another tracking database.
Abort is not erasure
ELA can fail safely at the protocol level. W can refuse. The exchange can stop. Encrypted error information can guide U toward another V and remain bound to H_12. These are meaningful protections against continuing under the wrong authority.
Yet “the handshake failed” and “the disclosed identity no longer exists in institutional systems” are different statements. V may have operational logs needed for abuse control. W may need a short-lived record to prevent repeated attempts. An owner may need evidence to challenge an erroneous denial. Immediate deletion is not automatically correct, but indefinite silent retention is not automatically justified.
The appropriate unit is a declared disposition. A refusal might require immediate erasure of the raw identifier, a rate-limit token retained for a fixed interval, or a quarantined audit record accessible only to a named function. Whatever the choice, it should be connected to the policy W actually evaluated, not inferred later from a generic logging notice.
W’s required availability sharpens the issue. Online consultation can deliver a current decision and avoid stale local allowlists. It also creates a dependency: outages, unreachable locations and recovery procedures can decide whether devices join at all. A fallback that admits devices without W changes the security model; a fallback that queues identity-bearing attempts changes the retention model. Availability engineering and disclosure governance meet at the same failure path.
The identity-release receipt
The smallest useful addition is an identity-release receipt. It is not another voucher and should not be confused with one. The voucher proves the bounded authorization result. The receipt records the governance of information released in order to obtain that result.
Its first section identifies authority without publishing the device identity: the manufacturer trust anchor known by U and its version, W’s identity and location, V’s credential fingerprint, the class and rotation rule of the onboarding identity, and a privacy-preserving reference to H_12. This lets an auditor reconstruct which trust configuration governed the attempt.
The second section freezes purpose: the policy identifier and version used by W, the proposed enrollment domain, permitted recipients, approved use, retention deadline and onward-disclosure rule. If V and W are controlled by different organizations, the handoff is explicit. “Authenticated server” is not allowed to stand in for the receiving institution.
The third section records disposition: approved or denied, voucher scope and expiry if issued, a bounded denial reason, the required deletion or quarantine action and proof that it occurred. Success adds the point at which a distinct operational identity became active and the onboarding identity was retired. Correction and appeal contacts finish the record.
This proposal lives outside the current draft. It need not add messages to the constrained link. V or W could retain the receipt in an auditable store, while U receives a compact reference. The essential property is that the evidence of disclosure not disappear merely because the authorization result is cryptographically sound.
Strong protocol, deliberately incomplete institution
ELA should be credited for exposing rather than hiding its security trade. It protects identity from broad observation, authenticates the party that receives it and binds the resulting authorization to the session. It also tells implementers that the authenticated recipient learns the identity before the decision is known. That sentence is the correct place to start governance, not a reason to reject the protocol.
The larger mistake would be to demand that a key exchange become a privacy regulator, records schedule and appeals body. RFC 9528 already leaves credential trust decisions to applications. BRSKI and the voucher artifact family likewise separate cryptographic artifacts from manufacturer-anchor management and operational policy. Constrained enrollment repeatedly reaches the same boundary because the wire can carry an authority’s assertion but cannot make the authority legitimate by itself.
An enrollment voucher can prove that W authorized V for U in a particular exchange. It cannot prove that the earlier identity release had the right purpose, that a denial left no durable trace, or that a later operational account will not be correlated across domains. Those facts require a separate, inspectable promise.
Sources
- https://datatracker.ietf.org/doc/draft-ietf-lake-authz/
- https://datatracker.ietf.org/doc/draft-ietf-lake-authz/history/
- https://www.ietf.org/archive/id/draft-ietf-lake-authz-08.html
- https://datatracker.ietf.org/wg/lake/about/
- https://www.rfc-editor.org/rfc/rfc9528.html
- https://www.rfc-editor.org/rfc/rfc8995.html
- https://www.rfc-editor.org/rfc/rfc8366.html
- https://www.rfc-editor.org/rfc/rfc9031.html
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance