
Profile
Briefing
Briefing profile intelligence connects person, company, institution, and other entity coverage for readers comparing the subjects behind BTW.MEDIA reporting. The page helps compare public profiles, related events, evidence packs, role changes, operating footprints, governance exposure, organisational links, and market relevance while keeping organisation and people records distinct from ordinary news chronology. Readers can understand the subject behind the headline, the evidence supporting that profile, and the infrastructure or market relationships that make the profile relevant. They can see who or what the profile represents, which public sources support it, how it connects to companies, markets, governance bodies, or events, and what changes may deserve continued attention as the subject evolves.

IETF
A SUIT Update Can Be Signed Before Its Target Can Understand It
The latest SUIT update-management draft leaves a crucial pre-delivery fact with the deployment: which devices actually support the optional command on which a firmware update depends. A sound manifest signature cannot answer that compatibility question.
CASE FILE
The Successor Key Waited 30 Days. The Validator Fleet Did Not Share One Clock: RFC 9691
Day 30 can arrive on an operator’s calendar while thousands of RPKI validators are still on day 12, day one, or no timer at all. RFC 9691 gives a trust anchor a careful way to stage a successor key; it does not turn a dispersed relying-party population into one synchronized…
IETF
The Certificate Was Good for the Number. The Call Still Needed a Decision
STIR’s new OCSP profile can make a narrow and valuable statement in real time: this certificate is still valid for this telephone number. The discipline begins where that statement ends. It does not certify the human speaker, the purpose of the call, the safety of the request or…

IETF
An SR Policy-Scale Pass Is Not an ECMP Speed Result
A router can forward traffic while many Segment Routing policies are installed without proving how fast its multipath forwarding is. The IETF BMWG's 22 September revision puts both observations in the same test programme but, crucially, does not give them the same evidentiary…

CASE FILE
The Certificate Carried the Key. It Did Not Carry the Recipient's Yes: RFC 9690
An RSA public key can be valid, correctly encoded and usable for familiar RSA operations while saying nothing about whether its owner will accept RSA-KEM today. RFC 9690 makes that separation unusually explicit. For an operator, the result is not a cryptographic footnote but a…
Europe and Middle East Regional ISP
DFINFRA and AS210860: who answers when a registry contact's network goes silent
DFINFRA and AS210860: who answers when a registry contact's network goes silent intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that may…

IETF
LAKE's KEM Draft Drops a Four-Message Shortcut That Exposed Identity
A shorter handshake looked possible in July if the initiating device revealed its credential identifier at the start. The September working-group revision no longer offers that trade: its proposed KEM authentication flow has five mandatory messages, and the responder reaches its…

CASE FILE
The Proxy Joined the Path. It Did Not Join the Control Planes: RFC 9689
A legacy router can signal its half of an MPLS path while a controller programs the other half hop by hop. RFC 9689 shows how a PCECC proxy can make that migration path continuous. The dangerous shortcut is to let continuity erase the seam: one LSP may still contain two kinds of…
Latin America and Caribbean Datacenter
AI Brazil's 2026 contract record meets an unchanged stub network
AI Brazil's 2026 contract record meets an unchanged stub network intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that may follow. The…
IETF
The Server Marked the File Uncacheable. The Client Still Had to Obey.
NFSv4.2 is gaining a standard way for a server to tell clients that a file should not live in their data caches. The flag is useful precisely because it is narrow: it records an instruction, while compliance, durability and cross-client visibility still need their own evidence.
Asia-Pacific Regional ISP
A Mailbox Held Accountable: NEXGENET's Contact Surface After the July 2026 Validation
Behind three registered autonomous systems at a small Yangon LIR sits one self-referential role entity and one company mailbox. The freshest signal in the public record — an abuse-mailbox validation remark dated 7 July 2026 — says that surface is still maintained. What it does…

IETF
BGP Best-Path Review Asks What a Failed Forwarding Check Actually Does
A route may have a reachable next hop in a routing table and still lack the forwarding path that would carry its packets. An IETF early review says a draft meant to close that gap has not yet specified which state to test—or the consequence when the test fails.
IETF
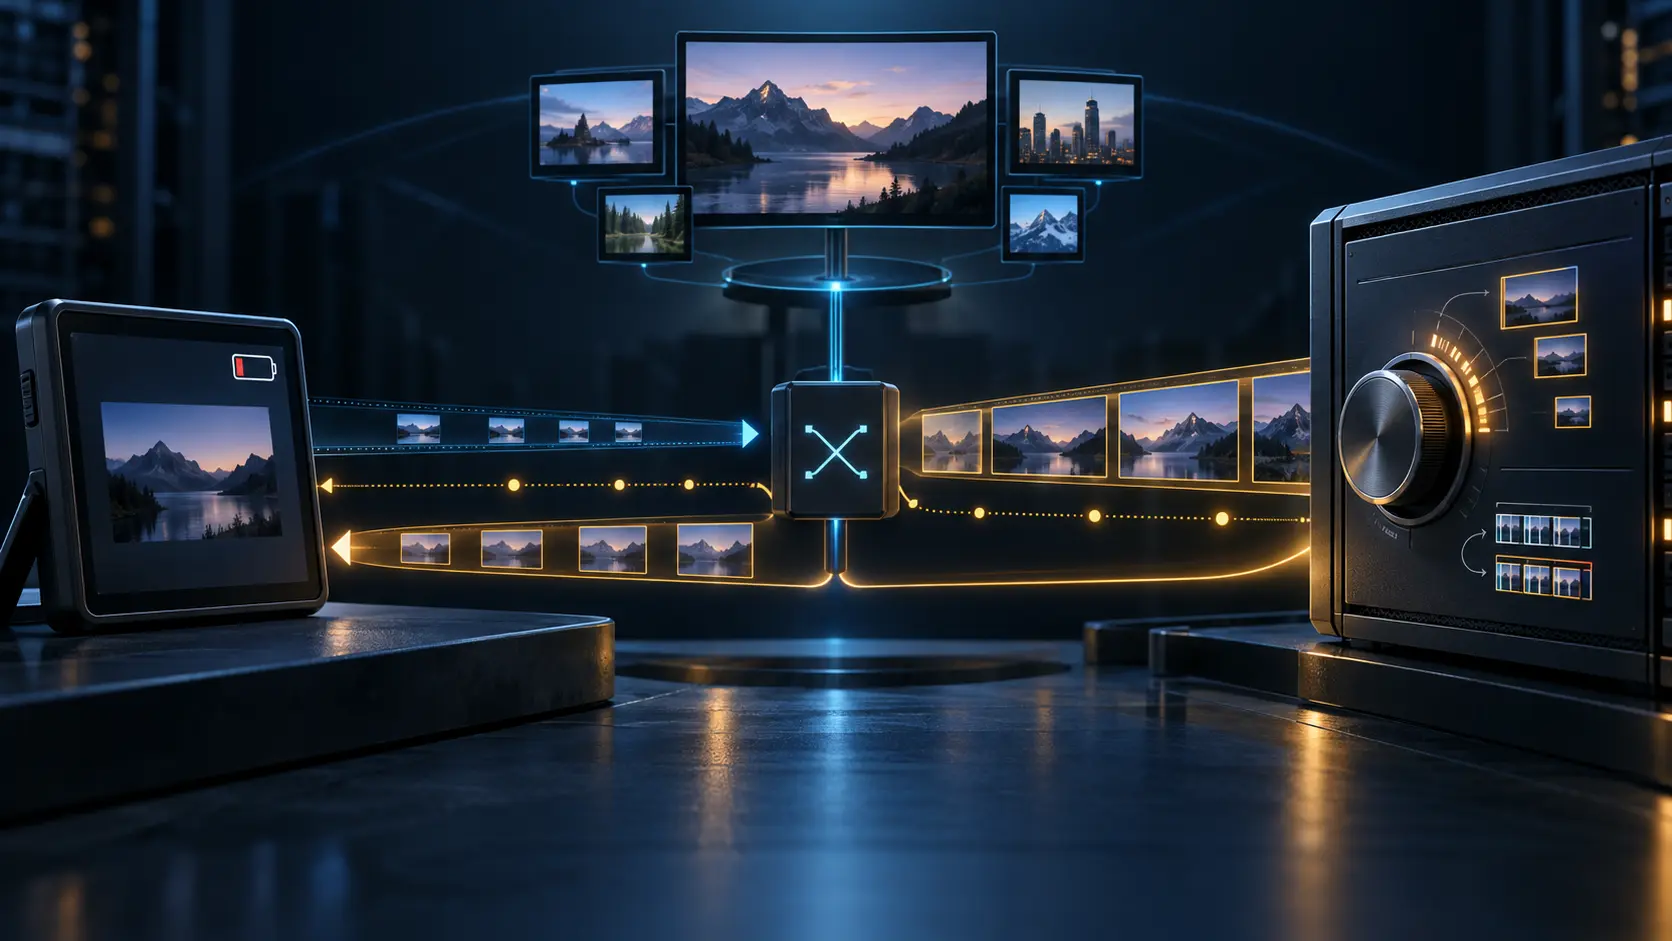
The Receiver Pays the Battery Cost. The Sender Still Chooses the Picture.
An IETF mechanism nearing publication lets a video receiver ask for fewer pixels or frames when its battery or decoder is under pressure. The request is useful precisely because it is not sovereign: the encoder, mixer, negotiated session and congestion controller still determine…

CASE FILE
The OID Was Right. One Missing NULL Changed the CMS Contract
Two systems can display the same friendly label—“RSA with SHA3-256”—and still disagree about the entity in front of them. RFC 9688 makes the reason unusually crisp: in CMS, the algorithm number is only one part of the wire contract, and the presence, absence or exact contents of…

IETF
HPKE's Successor Leaves Two Authenticated Modes with Its Predecessor
An IESG ballot now asks whether a new HPKE specification should replace RFC 9180. The replacement carries forward much of the scheme, but applications using the old sender-key authentication modes cannot treat a changed standards reference as a completed migration.

Europe and Middle East Cloud Services
Tideo Administration: Who Answers for a Dormant Danish ASN?
Tideo Administration: Who Answers for a Dormant Danish ASN? intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that may follow. The Europe…

IETF
The Device Proved Its Key. The Certificate Still Does Not Prove the Device Is Healthy
The IETF’s approved ACME device-attestation extension can bind a certificate request to a device or secure hardware module. That is a strong issuance receipt. It is not a live statement about the device’s health, owner or later use—and the issued certificate may deliberately…

CASE FILE
The Subscription Was Accepted. The Multicast Packet Still Had No Delivery Receipt
RFC 9685 lets a low-power IPv6 node subscribe to multicast or anycast service through Neighbor Discovery and lets a router redistribute merged listener state through RPL. Acceptance is a precise protocol receipt; it is not evidence that route state propagated, the right branch or…

Story
APRICOT 2027 Fellowship Bars AI-Drafted Applications
The current call asks applicants to describe their own operational work in their own words. It also gives a closing date: 12 October at 23:59 Hong Kong time.

IETF
A Source-Address Filter Cannot Diagnose Its Own Mistakes
An IETF Last Call exposes an awkward division of labour at the internet's border: a router can enforce a source-address rule, but the evidence that it blocked a legitimate sender may have to arrive from another network.