
Profile
Briefing
Briefing profile intelligence connects person, company, institution, and other entity coverage for readers comparing the subjects behind BTW.MEDIA reporting. The page helps compare public profiles, related events, evidence packs, role changes, operating footprints, governance exposure, organisational links, and market relevance while keeping organisation and people records distinct from ordinary news chronology. Readers can understand the subject behind the headline, the evidence supporting that profile, and the infrastructure or market relationships that make the profile relevant. They can see who or what the profile represents, which public sources support it, how it connects to companies, markets, governance bodies, or events, and what changes may deserve continued attention as the subject evolves.

IETF
Removing an OAuth Attester Is Not a Kill Switch for Issued Access
A new individual OAuth draft lets a client publisher withdraw an attester it once endorsed. The harder governance question starts after that edit: which authorization server has seen it, and what happens to access already granted?

IETF
DTPC Lets an Application Delete Yesterday Before the Network Sends Today
On a scarce delayed link, not every queued measurement deserves a journey. A new DTPC draft gives the application power to replace stale state before it becomes a bundle. The bandwidth saving is intelligible; the deletion authority needs a receipt of its own.
Europe and Middle East Regional ISP Trends
ALPSiX’s first three listed prospects already appear on AAIX’s roster
A public launch and a list of networks ready to connect are not yet evidence of incremental traffic. The new Carinthian exchange will have to show what it adds to a market where those same names already appear at AAIX.

IETF
A Proof of “We Cannot Tell” Still Has an Evidence Boundary
A new individual Internet-Draft proposes a verifiable receipt for a claim that remains unresolved under a defined body of evidence. Its most important control is not the cryptography at the end. It is the choice, made beforehand, of what evidence and possible worlds the proof is…

IETF
BGP Found a Reachable Address. It Had Not Yet Measured the Path That Would Carry the Packet
A new IDR draft confronts a quiet error in modern routing: the address BGP can reach may not be the tunnel, policy or SID that will carry the traffic. Its answer is not another universal metric, but a stricter evidence boundary around each path-resolution decision.

IETF
The Action ID Stayed the Same. The Validator Did Not.
The latest CAID draft holds the digest steady for entities both revisions accept, yet explicitly refuses some action entities that could carry valid identifiers under the previous draft. For an audit trail, the missing fact is not another hash. It is which rules were used when an…

Story
RIPE Labs’ RIPE 93 winners came after the publication gate
The contest named two winners on 22 September, but its rules put ordinary editorial review first. The 11-entry page records published entrants, not every submission made.

CASE FILE
The Name Was Allowed. Yesterday’s Address Blocked the Device: RFC 9726
A manufacturer can put the right service name in a MUD policy while a firewall enforces the wrong moment of that name. RFC 9726 exposes the hidden translation between DNS intent and packet rules—and why a clean policy file is not proof of a working or safe IoT device.

IETF
The Resolver Disclosed the Exception. It Did Not Authenticate the Answer
An emerging DNS signal can tell a client that a resolver suspended validation for a name. That is valuable candour. It is not a seal of truth, a defence of the operator's decision, or evidence that the application reached a safe service.

IETF
An Accepted AAuth Event Is Not an Agent's Decision
A new AAuth Events draft gives a resource an always-on place to send a signed event. Its `202 Accepted` response closes only the first hand-off: an agent may still be offline when the event's useful lifetime runs out.

IETF
The Parent Admitted the Boundary. It Did Not Promise a Road
A proposed DNS convention lets a public parent say that a child zone exists in another namespace while offering no public nameserver to reach it. The empty target is useful precisely because it is modest: it records a boundary without turning parent intent into proof of private…

IETF
Two Small Agent Budgets Can Authorize One Large Bill
An exploratory AAuth draft puts a hard ceiling on each agent token. The harder governance question sits one step upstream: who reserves against the person's total when several tokens are alive at once?
CASE FILE
The Signature Verified. The Resource Server Still Had a Decision to Make: RFC 9701
A signed token-introspection response can prove which authorization server issued a particular answer for a particular resource server. It cannot decide what that server should let a caller do now. RFC 9701 strengthens the receipt between two authorities; it does not merge them.
IETF
The Ladder Stayed in Cache. The Proof Still Had to Cross
SigTag proposes a smaller post-quantum DNSSEC response when a resolver says it already knows the signed Merkle Tree Ladder. That saves retransmission; it does not make cache state authoritative. The server’s omission, the resolver’s retained bytes, signer binding, validation…

IETF
A Valid Signature Is Not a Shared Trust Decision
An individual Internet-Draft on agent-action evidence has changed a deceptively small word in its evaluation model. The revised proposal asks a verifier to say separately whether an artifact checks out and whether this particular relying party is willing to rely on it.

IETF
The Certificate Shrunk. The Trust Decision Did Not
The Certificate Shrunk. The Trust Decision Did Not intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that may follow. The IETF…

CASE FILE
The File Was Routed to Haptic Hardware. That Does Not Mean the Effect Survived: RFC 9695
A media label reaches the one subsystem whose output can push back on the body. The registry can say where the entity belongs; only the endpoint can show what it understood, what it discarded, how it adapted the request, and whether the machine returned safely to rest.
Asia-Pacific Cloud Services
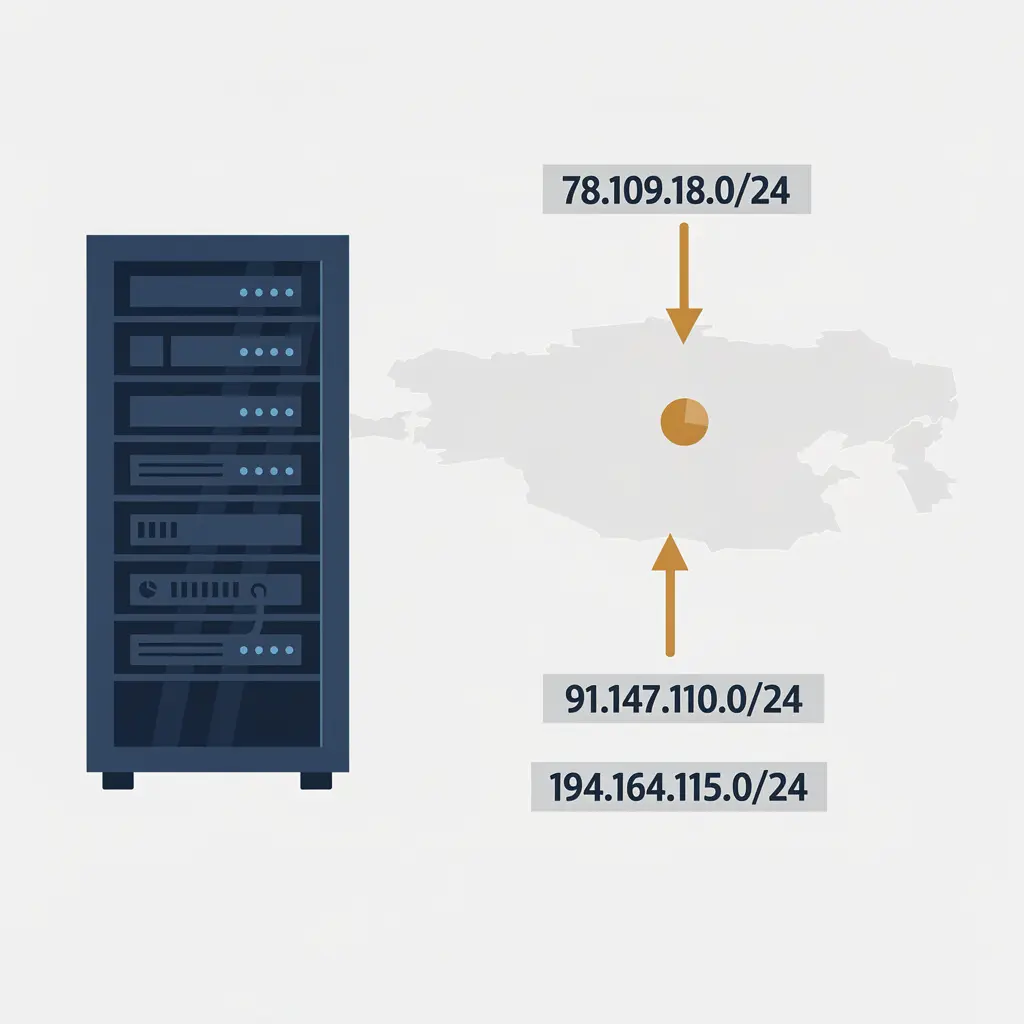
NovaCloud: two autonomous systems, one brand, and the gap between marketed cloud and routed reality
NovaCloud: two autonomous systems, one brand, and the gap between marketed cloud and routed reality intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure…
IETF
The Hop That Changed Nothing Can Still Disappear
A revised WIMSE proposal draws a sharp line between evidence that a message changed and evidence that an intermediary was present at all. The second question matters most when the intermediary forwarded the request untouched.

IETF
A SUIT Update Can Be Signed Before Its Target Can Understand It
The latest SUIT update-management draft leaves a crucial pre-delivery fact with the deployment: which devices actually support the optional command on which a firmware update depends. A sound manifest signature cannot answer that compatibility question.