
Primary Domain
Infrastructure
Within the Primary Domain facet, Infrastructure intelligence groups reporting by primary domain so readers can follow a focused area of internet infrastructure, governance, connectivity markets, or digital capital. The page brings together related articles, public evidence, institutions, companies, people, regional exposure, operating dependencies, and market context that may otherwise sit across separate category pages. It explains the domain, the likely actor class, the market or governance context, and the source material readers should use when comparing signals. Operators, analysts, and governance readers can see how the same domain appears across events, profiles, market shifts, public-source evidence, regional dependencies, and longer-cycle infrastructure decisions over time.
IETF
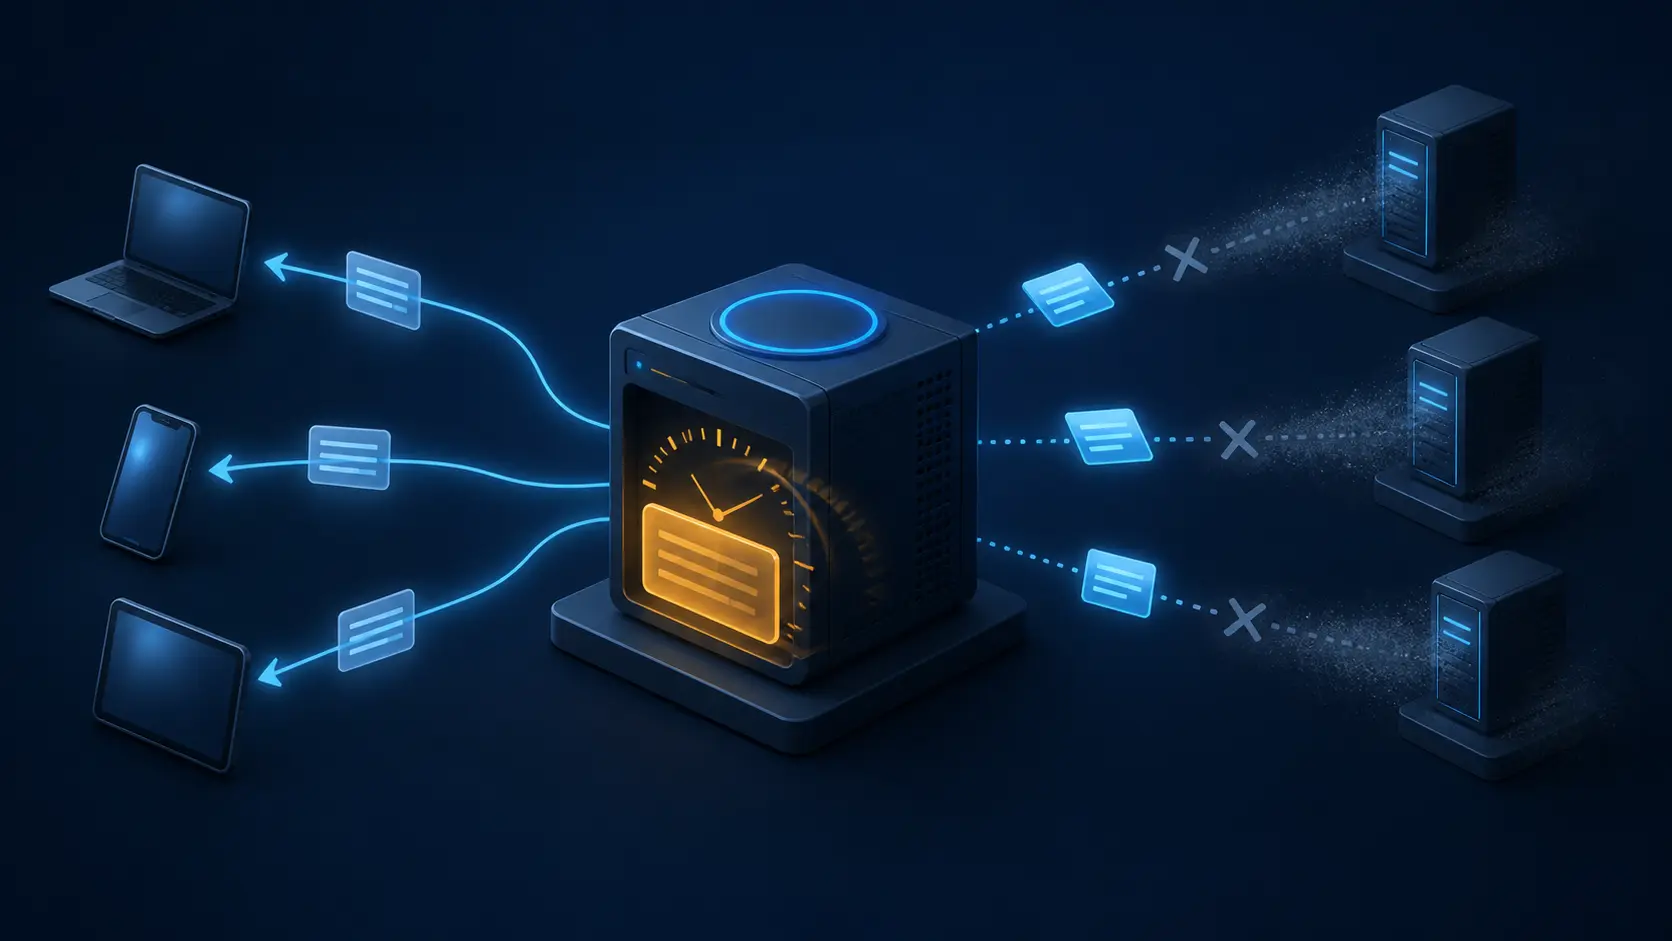
DNS Serve-Stale Lets the Recursive Resolver Decide When Expired Data Is Better Than Failure
A DNS record reaches the end of its TTL just as every authoritative server becomes unreachable. The old address may still preserve a working service—or it may lead users back to infrastructure the zone owner meant to retire. Serve-stale keeps resolution alive by giving the…

CASE FILE
Two Answers Said NOERROR. Only One Carried the New Zone
RFC 9660 can bind a DNS answer to the zone version that produced it. That makes a mismatch visible without pretending that one version token proves the zone is correct, the fleet has converged or users saw the same path.

Europe and Middle East Regional ISP Trends
A mapped pole is not a broadband route until access is cleared
A fibre planner can draw a convincing line through a village in minutes. The line follows existing poles, avoids an expensive trench and turns a difficult build into a short spreadsheet. Then a field team reaches the first pole and asks the question the map did not answer: can…
CASE FILE
The Timestamp Got Sharper. The Clock Did Not Gain Authority.
Send one NTP request through ordinary UDP port 123 and its arrival may be timestamped after software and queueing have already left fingerprints on the measurement. Wrap the same logical request in a PTP event message, and a compatible network card can timestamp it at the wire.…
CASE FILE
The Service Vanished. Its DNS Lease Did Not
A DNS Update Lease can make stale records expire without a cleanup command. It can also keep an authoritative answer valid long after the advertised service has stopped, because the server—not the requester—sets the operative publication horizon.

IETF
The Server Delayed the Cost of Belief: TCP's SYN-Flood Defenses
A TCP listener used to spend memory as soon as a stranger knocked. RFC 4987 explains how defenders moved that cost until the supposed client offered better evidence that it could hear the reply.
Story
AFRINIC Opened a Third Constitution Round. Every Comment Needs a Versioned Intake Record
AFRINIC’s Bylaws Review Committee continued constitutional consultation after the second-round deadline and narrowed attention to dispute resolution and safeguards around Resource Member termination. More time can improve the draft. It also creates a new recordkeeping duty: every…
Story
LACNIC and the economics of NRO coordination incentives
A regional Internet registry is not a shop that customers can abandon when service disappoints them. Internet number resources must remain unique, and each registry serves a defined region. That makes coordination indispensable. It also removes the most familiar market…

CASE FILE
The Message Had Expired. The Mailbox Had Not.
At noon, an offer in the inbox reaches the date chosen by its sender. At 12:01, the mail reader dims it. Search still finds it, the archive still holds it, and no deletion has occurred. That small separation is the point of the IETF’s newly approved work on the email `Expires`…

CASE FILE
The Catalog Went Empty. The Servers Obeyed
A DNS catalog zone can turn one compact, authenticated change into a new operating perimeter for an entire authoritative fleet. That efficiency is precisely why the catalog must be governed as executable authority rather than treated as a harmless list.
Story
AFRINIC Sought Three Appeal Committee Nominees. The Appointment Record Must Be Case-Ready
AFRINIC’s Board opened nominations for three Policy Development Appeal Committee profiles and set a short, explicit deadline. The call establishes an intake step, not a functioning adjudicative body. Readiness will depend on what comes next: a versioned record of appointment…
Story
LACNIC and the economics of ICP-2 reform
The rule for recognising an Internet registry is also a rule about who must bear the cost of proving that institutional change is safe. LACNIC makes that trade-off unusually visible: regional legitimacy is built through members and an open policy process, while recognition…
Story
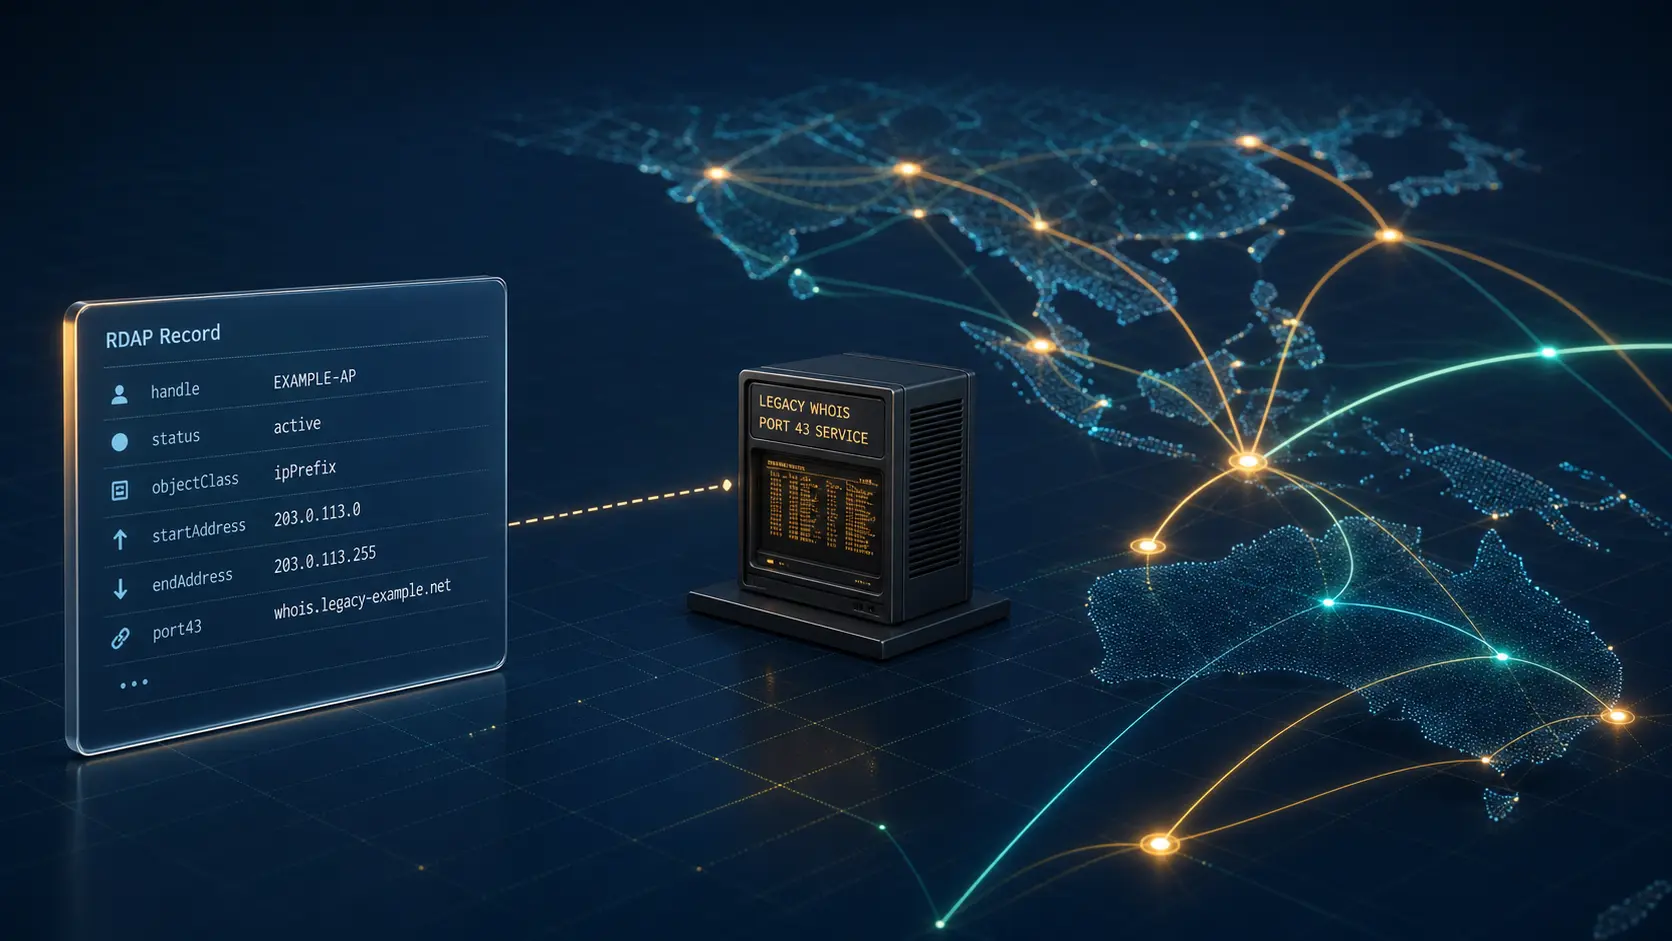
APNIC's RDAP port43 Points to a Legacy WHOIS Service, Not Network Authority
In a live APNIC RDAP record, `port43` names `whois.apnic.net`. That is useful evidence about where to query the legacy registration service—but it is not a statement about who operates, routes or controls the addressed network.
IETF
The First Sequence Number Could Not Be Only a Clock: TCP's ISN Defense
Every TCP connection begins by publishing a number. When that number followed one global clock too plainly, an attacker who could not see the connection could still predict enough of its state to impersonate a peer.

CASE FILE
The Route Said Valid. The Evidence Was Local.
One RPKI service fails. A customer network changes its view a second before its provider; the provider changes next, about five minutes later. If both networks export validation results as route attributes, one dependency failure becomes two waves of BGP UPDATEs. Nothing about…
History
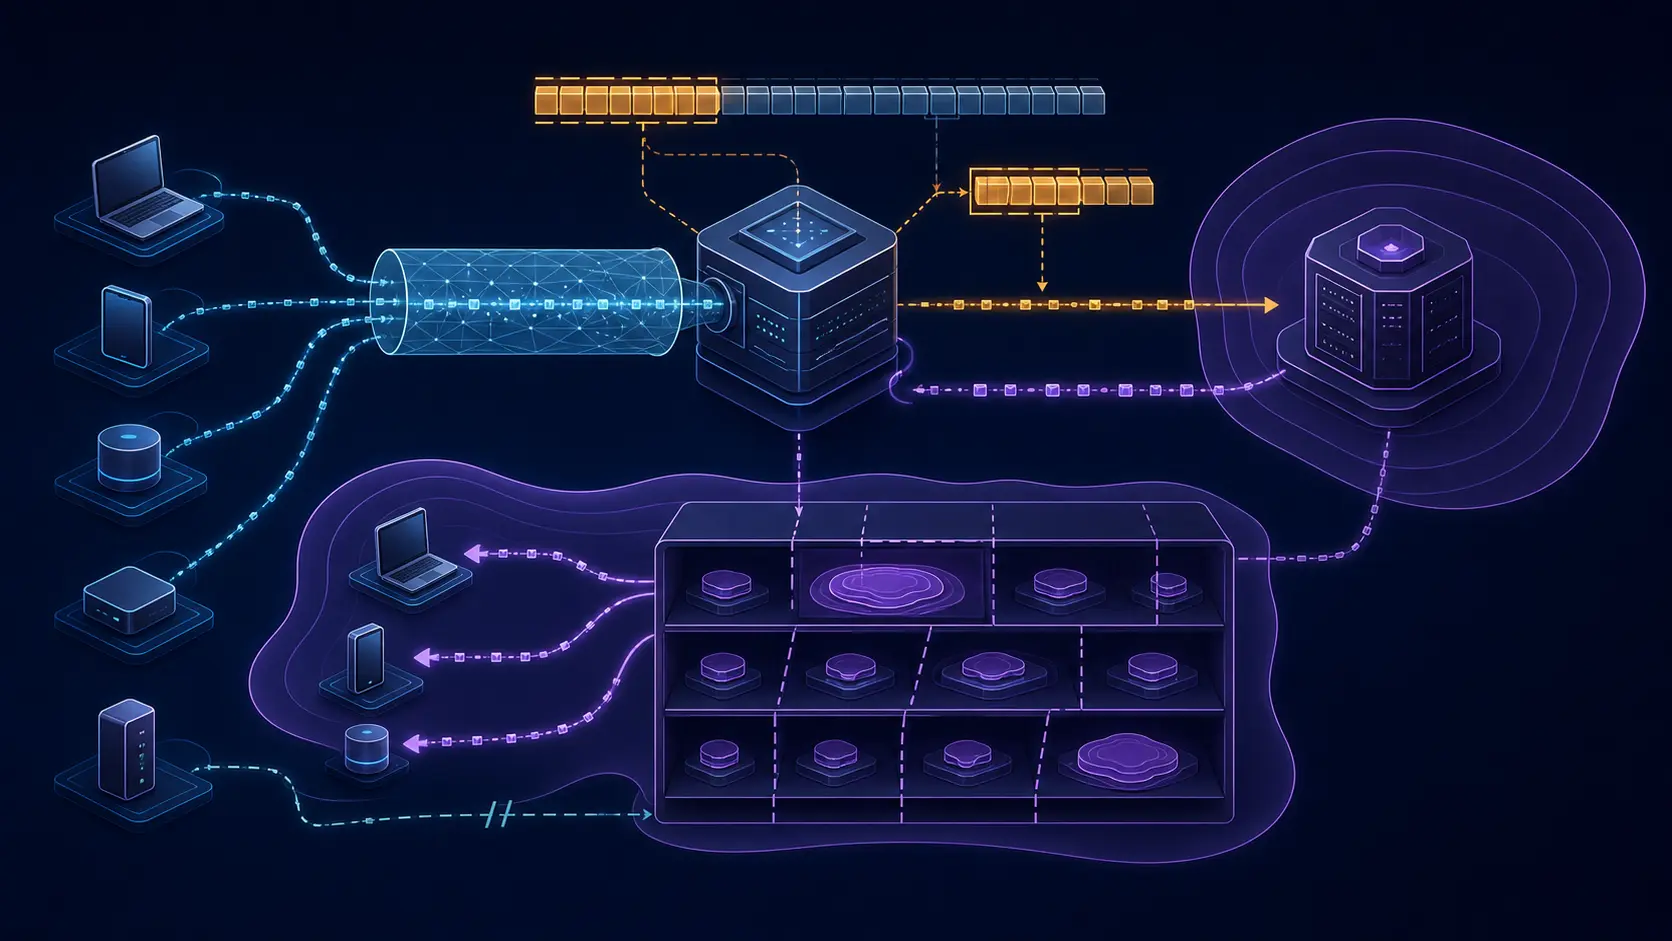
The Prefix the Resolver Sent on Someone Else’s Behalf: EDNS Client Subnet
A recursive resolver usually speaks to an authoritative server from its own address. EDNS Client Subnet changed the message: the resolver could send part of a client's network instead, asking the authority to tailor an answer for someone who had not made that upstream query. The…

CASE FILE
The signed chain skipped a delegation that still existed
NSEC3 Opt-Out allows a large parent zone to leave eligible insecure delegations out of its signed hash chain. That omission can be fully valid. It is also why the chain cannot serve as a complete delegation register: the proof authenticates a limited statement about a hash…
Europe and Middle East Datacenter Trends
A data-centre connection has no date at Gate 1
A site can have land, drawings and an impressive megawatt number while still lacking the one fact that makes its power plan schedulable: a confirmed grid-connection date.

Story
A Private Registry Still Needs Public Limits
LACNIC is private infrastructure governance with public consequences: legitimacy depends on a bounded mandate, published rules, evidence, review and an operational record that affected networks can understand.
IETF
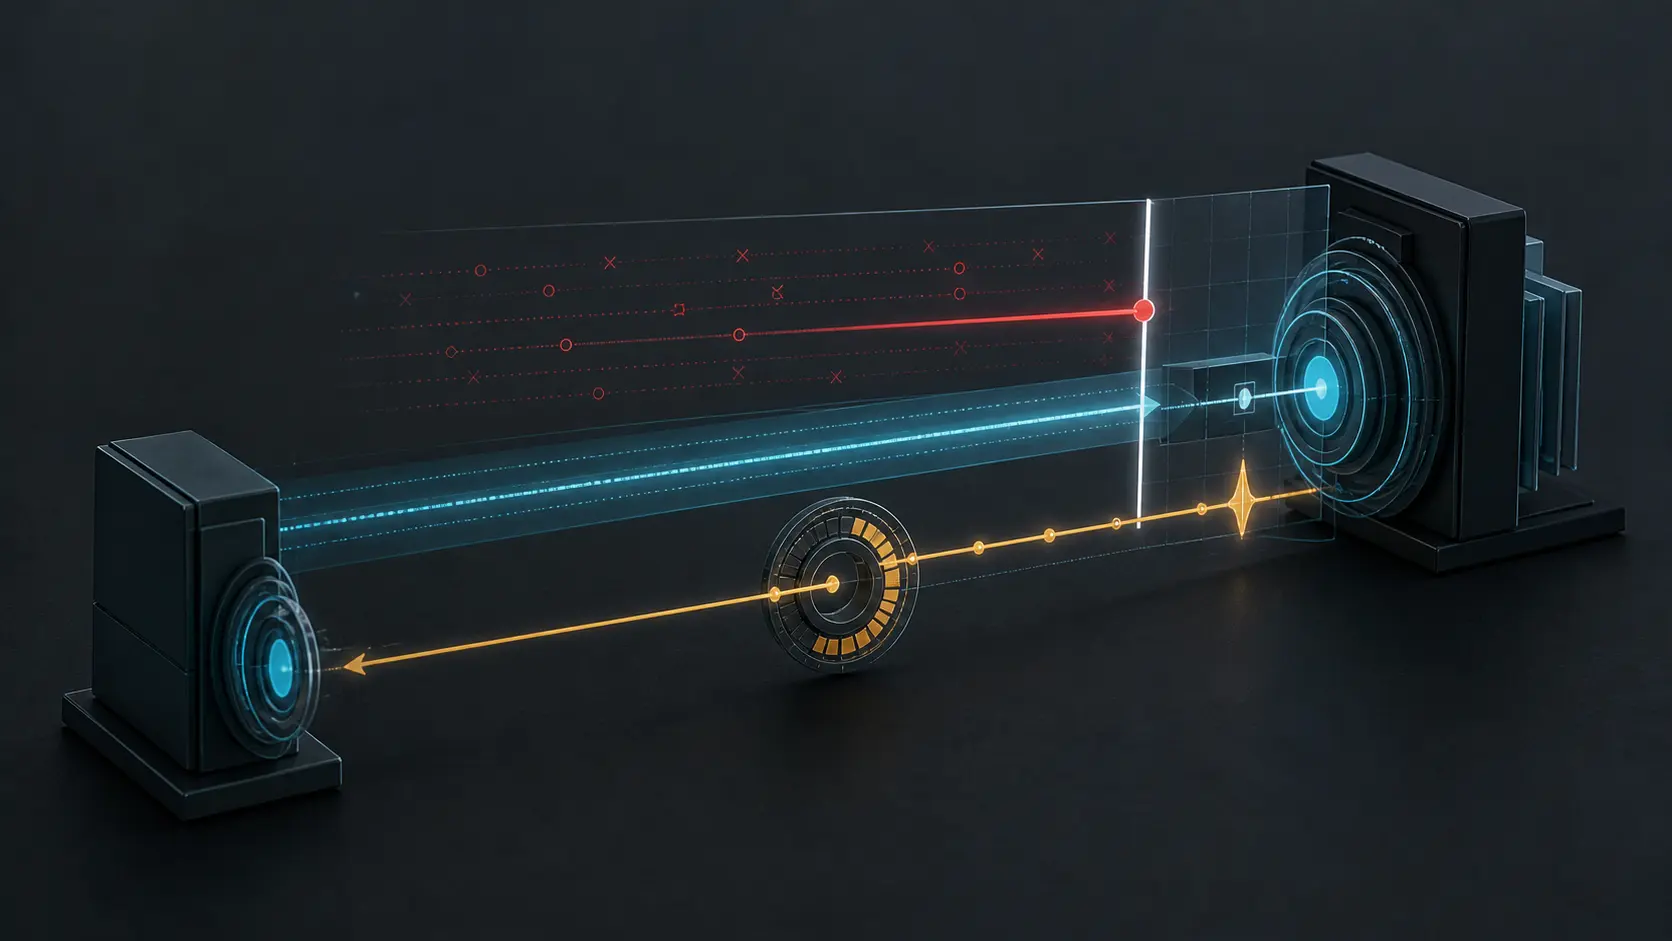
The Reset Had to Prove Itself: TCP's Challenge ACK Defense
A forged reset once needed only to land somewhere inside a moving receive window. RFC 5961 made destructive TCP control flags prove that they reflect the peer’s current state before one guessed sequence number can erase a long-lived connection.