
Content Type
Signal Briefing
Within the Content Type facet, Signal Briefing intelligence gathers BTW.MEDIA articles that share the same editorial format, helping readers compare briefings, profiles, risk notes, market analysis, and event coverage without mixing different kinds of evidence. The page explains how this content type frames internet infrastructure events, company movements, governance decisions, operational signals, and public evidence across the site. Readers can compare which actors or infrastructure systems appear most often, how source quality changes interpretation, and whether the material is a durable profile, a time-sensitive event, a strategic market signal, or a governance development. The result is a useful search page for operators, investors, customers, analysts, and policy stakeholders who need to understand the consequence, timing, and evidence behind similar article formats.

Story
APNIC’s RSC Verifier Returned After a 75-Minute Rollout Window
APNIC’s status record shows its public RPKI Signed Checklist verifier returning to operational status after 75 minutes of maintenance. The notice mentions a rollout-strategy change, but does not identify the release or any user impact; RSCs can also be checked locally.

Story
AFRINIC’s RPD Reply Drew a Boundary. The Scope Question Remains.
AFRINIC’s third Bylaws consultation closed on 30 August. A public exchange on the RPD list two weeks later separated formal article review from policy discussion, but did not spell out where entities should raise a bylaw’s effects on the policy process.

Story
RIPE’s first-ASN draft defers the route-policy record until use
RIPE’s first-ASN draft defers the route-policy record until use intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that may follow. The…

Story
The LACNIC Board ballot is set for November. Its English call says October.
LACNIC’s election index and dated timelines put the 2026 Board vote on 3–10 November. One English field in the detailed call instead says voting opens a month earlier; the Spanish call gives the November date.
Story
RIPE NCC’s new risk register starts with the whole organisation
A top-down view of high-impact risks changes where the discussion begins; the September Board minutes tie some treatments to the right budget.

Story
CEDIA’s FIRST Talk Leaves Critical CSIRT Decisions With People
At the LACNIC 46 co-located symposium, a 21 October session will describe DALIA’s AI-assisted triage and correlation while reserving critical decisions and containment for people. The abstract does not say how that boundary is enforced.

Story
ARIN’s Whois Snapshot Counts Query Types, Not the Organizations Behind Them
ARIN says 79% of Whois queries in a seven-day sample concerned IP addresses, while every one of the period’s ten most active queriers came from AWS addresses. The mix describes requests; it does not identify the organizations whose workflows may depend on them.

Story
APNIC begins reviewing its own IPv4 data as NIR checks advance
APNIC’s Q3 update places its own registry analysis inside a review that is moving from initial data work toward checks with national registries. It gives a timetable, but no findings.
Story
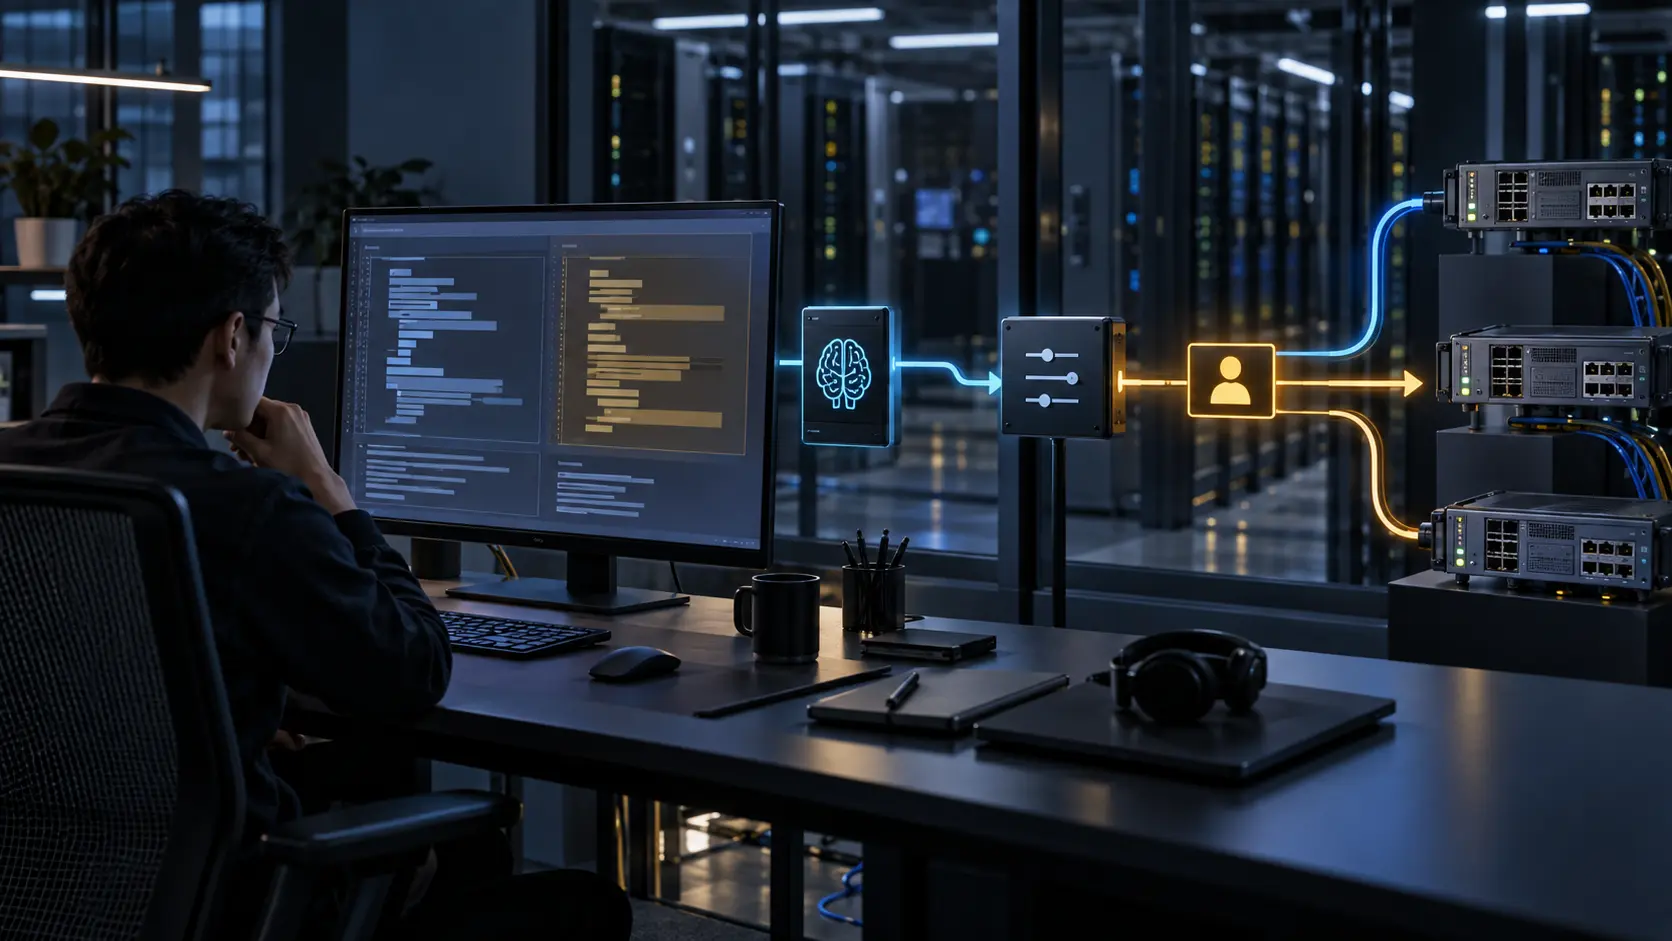
APNIC 62 put a Junos commit tool on the slide. Autonomy remained a future goal
An HPE presentation listed a Junos configuration-commit function. APNIC’s event report says reconfiguration remained human-supervised; production autonomy is not established.
Story
A new individual draft points to IPv6. ARIN’s space policy still includes IPv4
ARIN’s current space-address proposal still names both IPv4 and IPv6. September records point toward an IPv6-only direction and a separate IANA/NRO allocation model, but neither record is an adopted change.

Number Resource Society
An ASPA Is Not a Complete AS-Path Attestation
An ASPA can help an operator test whether an AS path is consistent with published customer-to-provider authorizations. That is valuable route-leak evidence. It is not a signature over every hop, a proof of route origin, a commercial contract, or a guarantee that the published…

Number Resource Society
A ROA maxLength Is Not a Traffic-Engineering Policy
A route can be RPKI Valid because a ROA’s maxLength admits its prefix length. That result proves a bounded origin authorization. It does not prove that the more-specific route was planned, approved, currently announced or preferred by the operator. Those are separate facts, and…
Number Resource Society
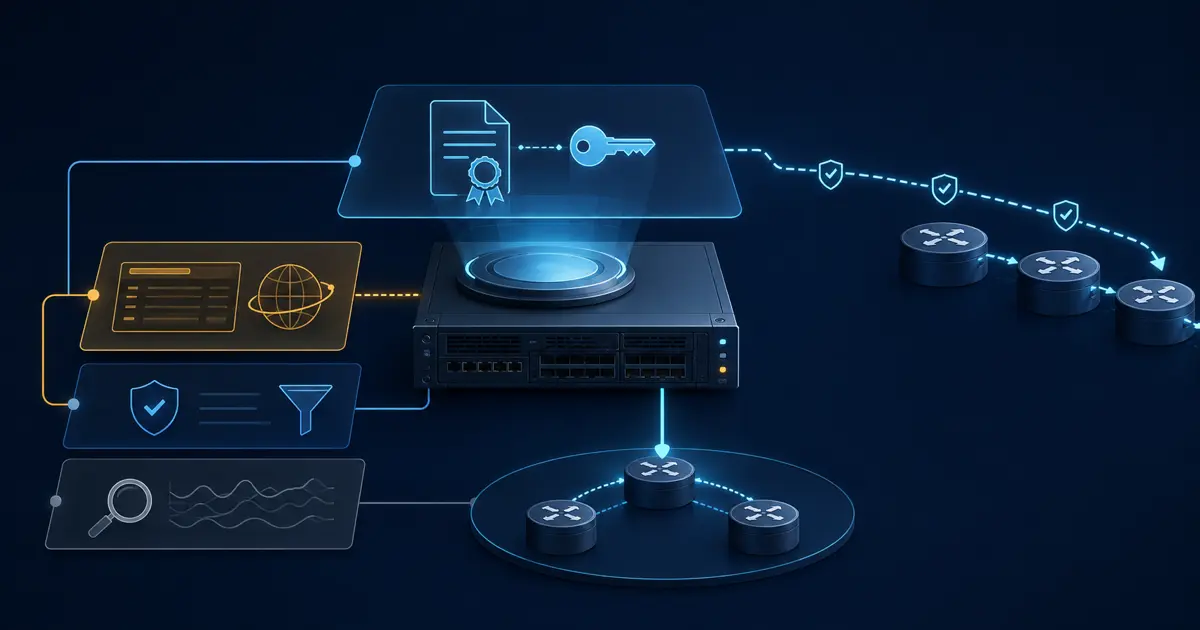
A BGPsec Router Certificate Is Not Route-Origin Authority
A BGPsec Router Certificate Is Not Route-Origin Authority intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that may follow. The Number…
Number Resource Society
A Ghostbusters Record Is Not an Incident Command Roster
An RPKI relying party can validate every byte of a Ghostbusters Record and still not know whether anyone is watching the listed channel when action is needed. The signed entity solves discovery of minimal CA-maintainer contact data; operational accountability begins where that…

Number Resource Society
A Trust Anchor Rollover Needs an Acceptance Ledger
An RPKI trust-anchor operator can publish a successor key without making every relying party ready to use it. The transition is a sequence of verified observations, not a launch date: a defensible record must show what was announced, what remained stable, which validators crossed…

Number Resource Society
An RPKI Publication Point Needs a Commit-to-Visibility Ledger
An RPKI publication server can accept an authenticated update atomically while relying parties still hold an earlier repository view. That is not necessarily a contradiction or a failure. It is a boundary between different authorities, protocols and observation times. A useful…

Number Resource Society
An ASN Transfer Needs a Routing-Identity Handover Ledger
An ASN Transfer Needs a Routing-Identity Handover Ledger intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that may follow. The Number…
Number Resource Society
An IPv4 Transfer Pre-Approval Needs a Registration-and-Expiry Ledger
An IPv4 transfer pre-approval answers a narrow question: how much address space a recipient may qualify to receive during a defined period. It does not identify a source, complete a transfer or prove that the registry has changed.

Number Resource Society
A ROA Change Needs an Authorization-and-Withdrawal Ledger
A route can be Valid while the organization behind it has already forgotten who approved the authorization, what changed, or how to reverse it. ROA governance needs evidence that joins intent, publication, observation and withdrawal—not another screenshot of a green status.
Number Resource Society
A RIR Representation Mandate Needs a Scope-and-Revocation Ledger
A public member list can show who has appointed a representative, but it cannot by itself show what that representative may do today. When the subject is Regional Internet Registry governance, authority needs a versioned record of scope, time, action and revocation rather than an…