
Summary
- Revision 04 of the active SAND Internet-Draft protects discovery bundles with BPSec, but lets an advertising node filter message types and instances by underlayer network, termination point and BP destination; the draft explicitly says neighbors can receive different, possibly non-overlapping, views.
- Receipt, authentication and storage are not route authority. Each receiver independently authorizes or culls discovered data, mutual-neighbor metrics need not agree, and attached-network advertisements require a separate routing-use decision.
- A defensible comparison needs an advertisement-projection receipt binding source, Security Source, Previous Node, destination, interface context, filter epoch, message time, supersession and receiver policy before anyone calls one map complete or the other inconsistent.
The first packet is easy to trust. Its Block Integrity Block verifies. The Source EID names the expected SAND participant. The receiving system can identify the previous hop. The payload is valid CBOR and the message type is understood. A green control appears.
The second packet is equally easy to distrust. It comes from the same source but contains a different set of convergence-layer instances and neighbors. A credential visible on one link is absent. A topology row shown to one destination never appears at the other. The instinctive incident label is “inconsistent advertisement.”
That label can be wrong even when every byte has been captured correctly.
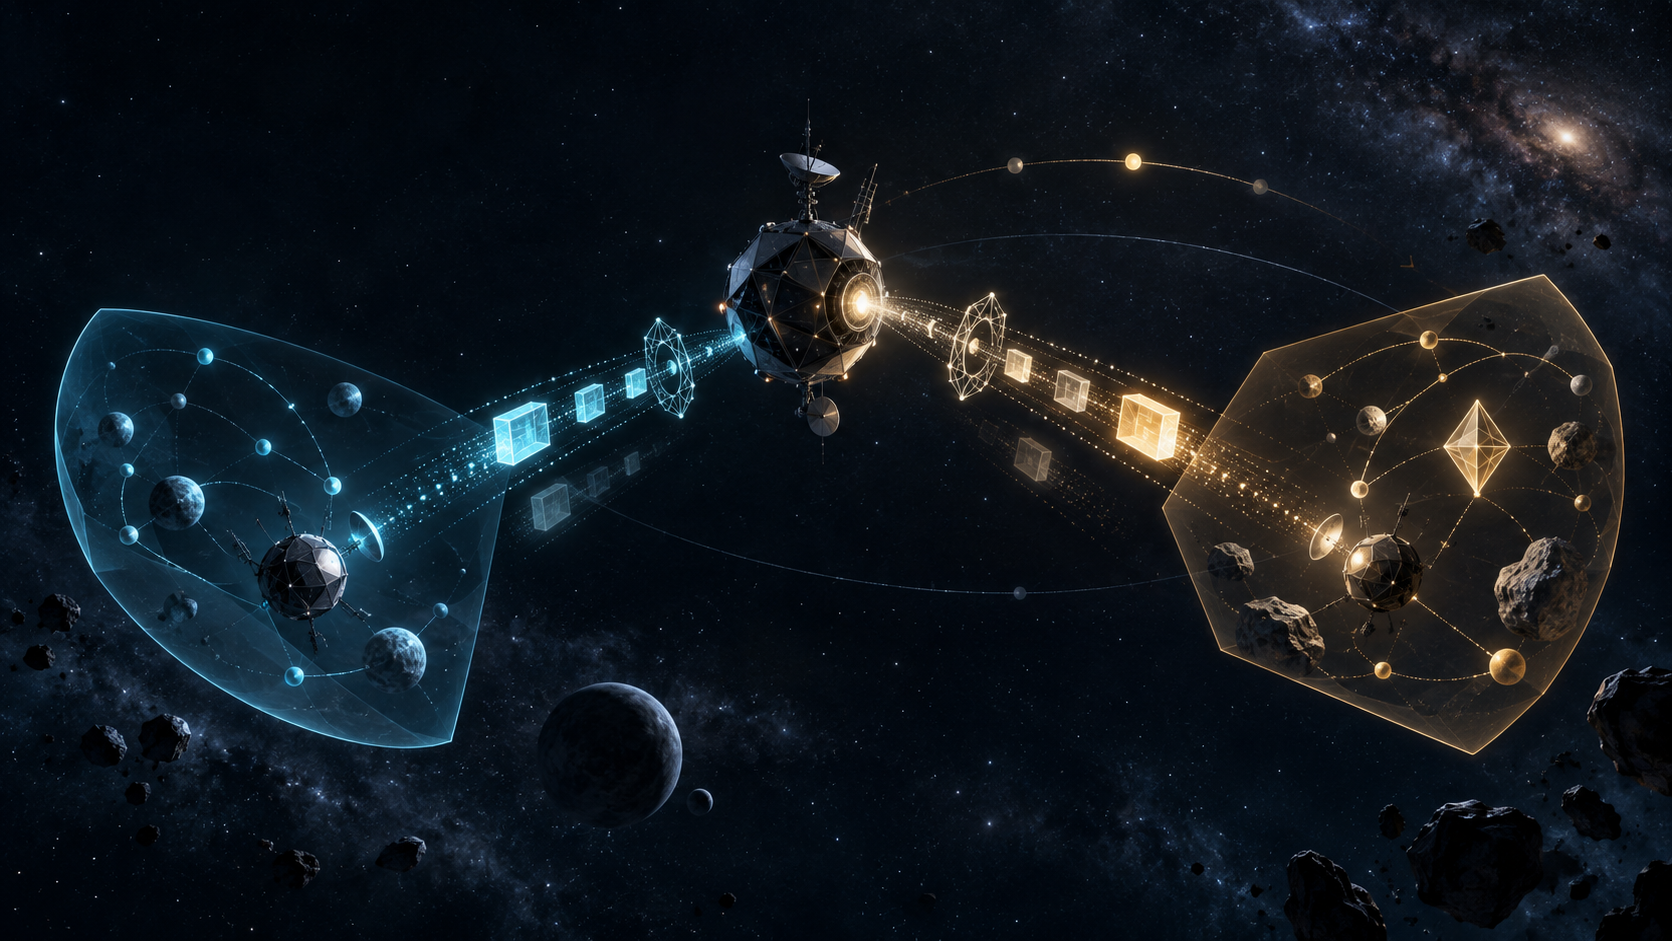
Revision 04 of Bundle Protocol Secure Advertisement and Neighborhood Discovery, or SAND, makes context part of the message's meaning. The advertising node chooses what kinds of data to send. It chooses which instances to include. It may condition those choices on the underlayer network, local termination point, BP destination or source, and on the security available for a singleton destination. The draft names the resulting condition plainly: different neighbors can observe different, possibly non-overlapping, sets of data associated with the same node. It calls this a kind of “split brain.”
That is not a loophole outside the protocol. It is an operational consequence described by the protocol. The mistake is to authenticate one scoped statement and then promote it into a global inventory.
Three identities travel near one another
A SAND Bundle begins with a source and a destination. For one-hop use it carries a Hop Count block with a limit of one. Forwarded bundles face a stricter rule because SAND handles a direct neighbor differently from a more distant source: the previous hop must be positively identified.
Revision 04 gives an order. An authenticated convergence-layer identity is preferred where available. Otherwise an authenticated Previous Node extension block can identify the forwarder. On the first hop, an authenticated Source Node ID can supply the identity. A forwarded bundle that did not come directly from its source may therefore carry both an original source and a distinct previous node.
BPSec protects the payload. The payload's Block Integrity Block has a Security Source that must identify the same node as the bundle Source EID, although local identity policy can allow different EIDs to refer to that node. A Previous Node block is protected separately, with its own Security Source identifying the previous node.
Those relationships are deliberate; they are not permission to flatten the fields. Source answers who originated the bundle. Previous Node answers who supplied this hop. Security Source identifies the principal whose key protects a targeted block. An implementation can correctly conclude that two EIDs identify one node and still need to preserve both values, the policy used to join them, and the block each signature covered.
Integrity protection establishes custody of the statement. It does not make every possible statement appear in the payload.
The sender owns the disclosure surface
SAND defines messages for solicitation, credentials, underlayer networks, convergence layers, resources, local topology, routing and endpoints. These are mandatory structures to understand, not mandatory disclosures to make.
The advertising node alone chooses which message types to advertise. A Data Solicitation tells it that another node wants certain data; it cannot override local policy. The sender also chooses which instances to include or exclude. It might suppress a termination point that is not enabled for discovery, avoid repeating a long-lived credential, or expose only data relevant to the link on which the message leaves.
Context-specific filtering goes further. A group-destination message might contain only enough information to attempt contact, while a protected singleton exchange reveals richer material. A private PKIX hierarchy can be advertised only on the underlayer that trusts it. IPv6 convergence-layer instances can be included on an IPv6-only termination point and omitted elsewhere. Destination, underlayer and termination-point filters can operate together.
The result is not one master map with transmission loss at the edges. It can be several intentionally different projections. One receiver's absence is not the sender's absence. It is not even proof that another receiver's presence is suspicious.
This matters because the initial zero-configuration group exchange described by the draft necessarily exposes plaintext payload unless additional confidentiality is used. Hiding DNS names, addresses, neighbor rows or credentials from a particular context can be sound security practice. The draft says filtering need not be symmetric across termination points. Symmetry is therefore not a conformance goal by default.
The receiver creates a second projection
Even a correctly delivered and authenticated message does not oblige a discovering node to use everything inside it. Receiver authorization is local. It can depend on message type, bundle source or destination, reception context, convergence-layer parameters, or previously discovered information about the advertiser.
The receiver can also cull data that it cannot use. An IP-only implementation may discard non-IP parameters. An address with no present route may be omitted from the local information base. Yet present unreachability is not timeless falsity: routing can change later. A receiver-side cull must therefore remain distinguishable from a sender-side omission.
Contextual authorization needs evidence that many software interfaces discard. The draft says the receiver must be able to relate a SAND message to its original enveloping bundle and to the local convergence-layer instance over which it arrived. If the application interface does not expose that detail, context-specific authorization might not be available. A normalized row in a topology database is insufficient when it has forgotten how the row entered the system.
By the time a dashboard renders a node, at least two filters may have acted. The sender decided what to disclose in that context. The receiver decided what to authorize and retain. Comparing dashboards without those two policy epochs compares outcomes while hiding causes.
Time can make equal messages unequal
SAND messages are full-state statements for their type, not incremental patches that depend on every earlier update. That design makes processing idempotent and accommodates duplicate delivery. It also creates a strict supersession rule.
For every source and message type, the receiver records Reference Time, using the bundle Creation Timestamp as a fallback. A message with an identical or earlier time must be ignored. Ordering uses DTN Time and then Sequence Number. Ignoring an older message is not a processing failure.
Consequently, two packet captures can both contain valid protected bundles while only one is eligible to change current state. A replay can waste resources but should not push the local view backward when supersession is implemented. Conversely, a sender that transmits only on state change can leave stale data alive if the superseding message is lost. Periodic timers, Validity Duration and Repetition Interval each alter the evidentiary meaning of silence.
“I received it” is not enough. An audit needs to know whether it was newer, valid for the decision window and processed rather than superseded.
A neighbor list is not an outcome ledger
Local Topology Advertisement can label a peer HEARD, SYMMETRIC or LOST. The words sound stronger than their protocol scope.
HEARD means this node received a message from the peer but has not yet seen itself in the peer's advertised topology. SYMMETRIC means the peer advertised this node, so at least one message has been received in each direction. LOST means nothing arrived within an implementation-defined timeout.
None of those facts proves stable capacity, a usable application path or successful delivery. Even mutual neighbors do not synchronize routing metrics. Revision 04 says equal values are neither guaranteed nor expected, and leaves reconciliation to the implementation. The metrics can also be tied to local termination-point indices that make sense only within the advertiser's own information base.
Router Advertisement is similarly bounded. A node can announce willingness values and attached-network patterns, including a gateway-like *:** pattern. But recording that claim, authorizing it for routing and actually sending traffic through it are different decisions. The security section warns that route leak and hijack risks apply without proper authorization and notes that BP has no equivalent of RPKI for this purpose.
An authenticated router advertisement is therefore not a route warrant. It is attributable input to a later authority.
Preserve an advertisement-projection receipt
The missing evidence object is an advertisement-projection receipt. This is an operational proposal, not a format required by revision 04.
The receipt begins with exact bytes: the protected bundle hash, bundle identity, source, Security Source, Previous Node, destination, hop limit, creation time and receipt time. It records which identity-validation path succeeded. It then binds the message to the send or receive underlayer, termination point and convergence-layer instance.
For every message type it records included instance identifiers, Reference Time, Validity Duration, Repetition Interval and the supersession decision. It identifies the sender filter or configuration epoch where available. On receipt, it records authorization and culling decisions with reasons. Finally it hashes the post-policy information-base projection.
The receipt ends before route or application authority begins. A route-installation decision needs its own accountable record. Forwarding observations and application outcomes need later evidence. The point is not to produce one enormous immutable log. The point is to stop one green “authenticated” flag from consuming six independent decisions.
With two receipts, an operator can classify divergence. It may be intentional scope, different policy epochs, staleness, a superseded message, local culling, an unsupported parameter, delivery loss, misconfiguration or unexplained behavior. Without receipts, every category collapses into an argument over screenshots.
What revision 04 does not establish
The status language must remain exact. Datatracker records an active DTN Working Group Internet-Draft published on 8 September 2026 and expiring on 12 March 2027. Its header says Standards Track; the Datatracker intended-status field was unset when this evidence was frozen. It is not an RFC, a final allocation or proof of deployment.
The implementation-status appendix names an example proof of concept. That appendix also says the information was supplied by contributors, was not verified, is not an implementation catalog and does not imply IETF endorsement. This article claims no adoption, interoperability result, product behavior, incident, route leak or outage.
The neighboring standards define important layers. RFC 9171 supplies BPv7. RFC 9172 supplies BPSec. RFC 8949 and RFC 8610 supply CBOR and CDDL. RFC 6130 provides a MANET neighborhood-discovery comparison. RFC 4593 and RFC 7908 explain routing threats, while RFC 6480 describes RPKI. None turns a scoped SAND advertisement into a universal map.
The conclusion is narrower and more useful. The protocol can authenticate who made one statement in one context. Governance must preserve the context before it decides what the statement means elsewhere.
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance