
Summary
- Guidelines 04/2026, adopted by the European Data Protection Board for consultation, set out five questions for deciding whether a GDPR fine should accompany or replace another corrective measure.
- The draft says minor infringements will generally draw a reprimand instead of a fine; a non-minor infringement creates a strong presumption for a fine, followed by an individual proportionality assessment.
A confirmed privacy breach does not decide the remedy by itself. A regulator may need to stop processing, order a correction, issue a reprimand, restrict an activity or impose a fine. The hard question is which measure answers the problem found, and why.
The European Data Protection Board (EDPB) has put that choice into a proposed five-step route. The September plenary also finalised separate Guidelines 3/2025 on the DSA–GDPR interplay; that work is distinct from the new method for choosing a fine. The EDPB adopted version 1.0 of Guidelines 04/2026 on 17 September for public consultation.
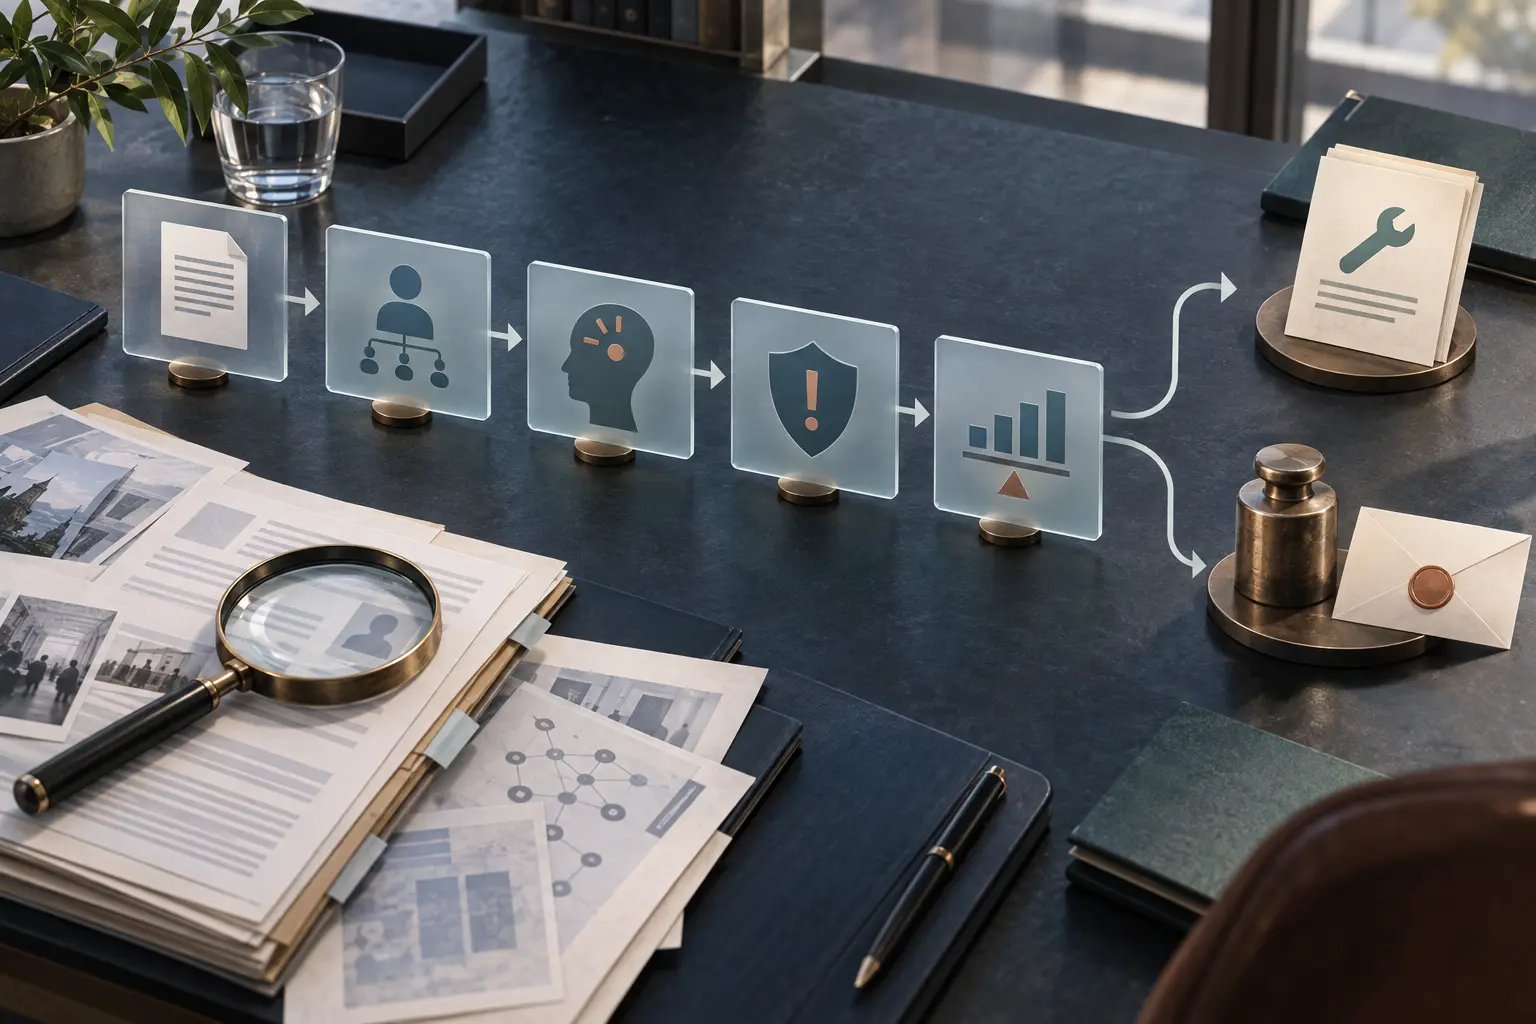
The draft asks the competent national supervisory authority to check, in order: whether the GDPR or national law makes the infringement fineable; whether the investigated party is the one bound by the breached duty; whether the conduct was intentional or negligent; whether the Article 83(2) factors point to a minor infringement; and whether a fine would be effective, proportionate and dissuasive in the case.
The fourth step gives the sequence its sharpest edge. The draft says that, as a general rule, a minor infringement should receive a reprimand rather than a fine. If the infringement is not minor, it says there is a strong presumption that a fine should be imposed. That presumption is not a tariff. The fifth step still asks whether the fine would serve its statutory purposes in the particular case, and whether there is reason to depart from the authority’s usual approach.
This is guidance about choosing a measure, not computing its price. The EDPB’s earlier Guidelines 04/2022 address calculation of the amount. A firm therefore should not read the new draft as a spreadsheet that converts a breach into a predetermined sum. Nor does it create a new fining power: the legal basis remains the GDPR, including Articles 58 and 83, and the decision belongs to the competent supervisory authority rather than to the EDPB as a board.
The Court of Justice had already framed the outer boundary in Case C-768/21, Land Hessen. It held that a data protection authority is not required to impose a fine whenever it finds a breach. It must choose and apply a corrective measure when that response is appropriate, necessary and proportionate to remedy the shortcoming and enforce the GDPR. The EDPB draft tries to make that discretion more legible across cases without removing the duty to enforce. It also says authorities need not follow a step that does not apply, and that its examples illustrate reasoning rather than create precedents.
The difference between a warning and a fine makes the sequence concrete. A GDPR warning concerns processing that is intended but has not yet become an infringement; the draft says it cannot be combined with a fine for that same conduct. A reprimand, order or restriction responds to a different legal situation and can serve a different purpose. Some corrective actions restore compliance; a fine also has a deterrent function. Treating every tool as interchangeable would obscure what the authority is trying to achieve.
The draft is open for feedback until 13 November 2026 at 23:59 CET. The EDPB says submissions will be published after screening only for unauthorised material such as spam. It asks contributors to remove personal information and document metadata they do not want made public; email addresses will not be published. The consultation is an opportunity to test whether the proposed dividing line between a minor breach and a strong presumption for a fine is clear enough to guide authorities without becoming an automatic rule.
Sources
- EDPB announcement of the September plenary
- Guidelines 04/2026, version 1.0
- Public consultation and submission conditions
- GDPR, Regulation (EU) 2016/679
- Court of Justice, Case C-768/21, Land Hessen
- EDPB Guidelines 04/2022 on calculating fine amounts
- EDPB overview of GDPR fines and corrective powers
- Court of Justice press release 149/24 on Land Hessen
- EDPB Guidelines 3/2025 on the DSA–GDPR interplay
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance