
Summary
- Revision 03 of the large-record draft is an active Internet-Draft, not an RFC or evidence of implementation, interoperability or deployment.
- Each endpoint advertises the largest inner plaintext it is willing to receive; the value is directional and does not reserve memory or command the peer to use it.
- TLS and DTLS handle an oversized record differently, while padding, application boundaries, scheduling and transport packetization remain separate concerns.
- Larger records alter AEAD usage accounting, so a changed ceiling needs a fresh key-lifetime budget rather than an inherited record-count threshold.
Permission is not capacity
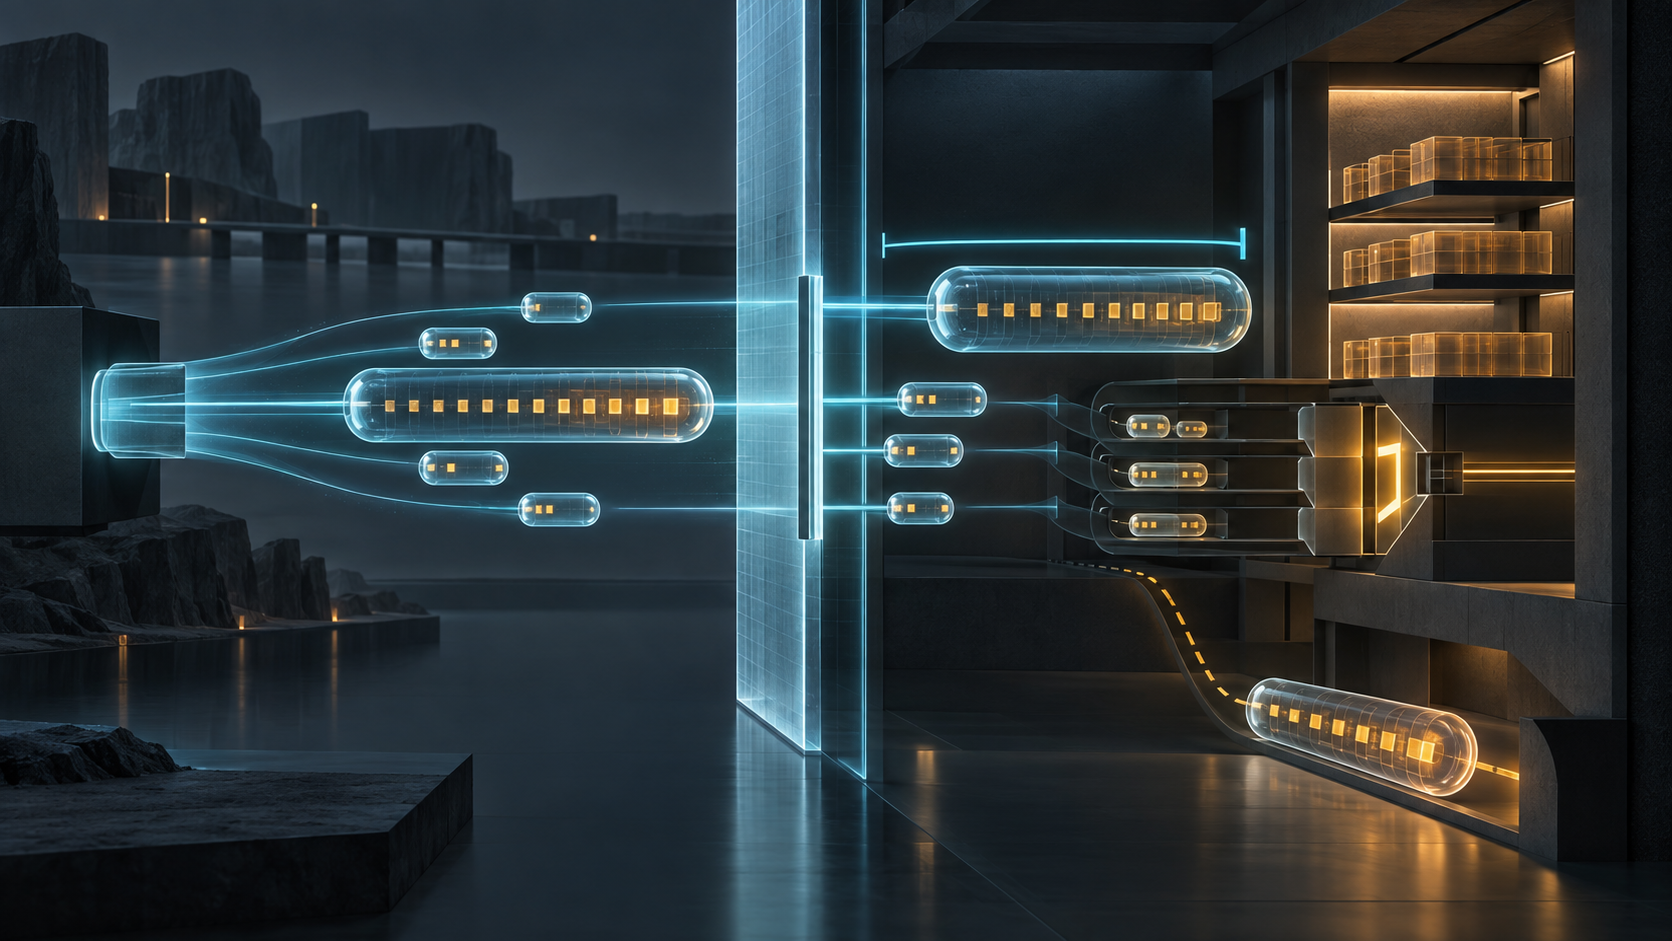
TLS 1.3 and DTLS 1.3 normally cap inner plaintext at 2^14 + 1 octets. The draft proposes a large_record_size_limit extension that can raise the advertised ceiling as high as 2^30 - 256, with 64 as the minimum valid value. Those numbers define what a receiver says it will accept on the wire. They do not describe how its allocator, queues or application behave under simultaneous demand.
That distinction disappears easily in infrastructure planning. A single maximum becomes a field named “record capacity”; the field is copied into a memory model; the model assumes that every accepted record has a dedicated buffer. Yet an implementation may stream, pool, fragment internally, apply backpressure or reject work for reasons above TLS. Conversely, an implementation can accept one maximum-size record in a laboratory and still fail when thousands of partial records occupy buffers concurrently.
The honest receipt is narrow: endpoint A advertised that endpoint B may send an inner plaintext record no larger than a stated number. It says nothing about bytes preallocated, concurrency supported, time allowed for completion, application queue space or the outcome of processing. Capacity requires its own evidence under load.
The two directions are different contracts
The extension does not negotiate one shared record size. Each endpoint declares what it is prepared to receive. A client may advertise one value and a server another. The server's outbound records are constrained by the client's declaration; the client's outbound records are constrained by the server's.
This means an endpoint may legitimately send a record larger than the value it advertised for its own receive direction. A dashboard that collapses both declarations into one number can report a false violation or, worse, conceal a real one. The minimum useful observation includes connection identity, endpoint role, direction, local policy value, advertised value, peer value and actual authenticated record length.
Nor does a large ceiling request large records. The sender remains free to choose smaller records because of latency, batching, congestion, application framing or local memory. Treating the ceiling as a target invites optimizers to fill every record even when the workload benefits from earlier authentication and delivery. A maximum is a boundary, not an instruction.
The bytes nobody sees still count
TLS 1.3 inner plaintext can include content type and padding. The draft's ceiling applies to that inner plaintext, not merely to the application payload that a dashboard finds interesting. Padding that pushes a record beyond the peer's value makes the record too large even when the visible content would have fit.
This matters for both conformance and resource models. A team may calculate buffers from average application chunks while a privacy policy adds variable padding. Another may test the maximum unpadded message and assume success transfers to the padded form. The permitted envelope must include every protected plaintext byte, while the capacity test must include the ciphertext expansion, parser state, authentication work and any retained upper-layer fragments.
Invalid extension values also have precise meaning. A value below 64 or above 2^30 - 256 requires a fatal illegal_parameter alert. That outcome proves rejection of a malformed negotiation value. It does not prove which configuration source created it, and it does not justify guessing a fallback ceiling after the handshake has failed.
TLS closes where DTLS usually discards
If a TLS receiver obtains a record beyond the allowed limit, the draft calls for a fatal record_overflow alert. The connection ends because the ordered stream cannot simply pretend the offending record never existed while preserving the record sequence.
DTLS has a different failure surface. An oversized datagram SHOULD be discarded and SHOULD NOT provoke a fatal alert. Datagram loss is already part of the transport model, and responding fatally to unauthenticated or attacker-amplified traffic can create a denial-of-service lever. Monitoring that expects the same alert in both protocols will therefore misclassify correct behavior.
The operational receipt should retain protocol, epoch, direction, observed record length, configured ceiling, authentication status where known, action taken and any alert. “Oversize rejected” is too coarse: a closed TLS association and a silently discarded DTLS datagram have different consequences, retries and user-visible symptoms.
A record is not an application message
The draft can reduce record-header and AEAD overhead by carrying more plaintext under one record protection operation. For some large-message DTLS uses it may also avoid fragmentation at an upper layer. Those are protocol motivations, not universal outcomes.
An application message can span records, and one record can contain portions of multiple messages depending on the protocol above TLS. A transport stack may segment a large TLS record across many packets. QUIC, TCP, SCTP and datagram applications have their own scheduling, congestion and reassembly behavior. Raising the TLS envelope therefore cannot prove that one application object arrives atomically or that fewer network packets are used.
This is where attractive arithmetic becomes misleading. Dividing payload bytes by record-header bytes gives an overhead ratio, not a service result. The missing terms include time until the complete record can be authenticated, packet loss, retransmission, receive-window pressure, application parsing, cancellation and the number of concurrent incomplete objects.
Fewer headers can coexist with slower delivery
A receiver generally cannot release authenticated TLS plaintext as trustworthy application data until the record's authentication check succeeds. A larger record can therefore extend the interval between the first byte arriving and the application receiving verified content. On a clean high-bandwidth path that cost may be small. Under loss, constrained buffers or interactive workloads it may dominate the saving from fewer headers.
The draft does not promise a latency improvement. It provides a larger permitted unit. Implementations and applications still choose batching and flush policies. Operators need distributions, not anecdotes: authenticated record sizes, time-to-authentication, queue residence, bytes held per connection, concurrent partial records, application completion time and tail latency under loss.
Throughput and responsiveness can pull in different directions. A policy that fills large records might improve bulk efficiency while delaying control messages behind a large protected unit. An endpoint may need separate policies for bulk transfers, interactive traffic and datagram messages even though the same extension syntax serves them all.
Cryptographic budgets move with size
AEAD safety limits are not a timeless number of records. They depend on the construction and, for schemes such as AES-GCM, on the amount of protected data and the number of blocks processed. The draft explicitly adjusts usage accounting when records can exceed the traditional TLS size, using a factor related to LargeRecordSizeLimit / 2^14 and more specific block reasoning where required.
An organization that raises the record ceiling but preserves an old KeyUpdate threshold can therefore spend a different cryptographic budget than its control assumes. Counting connections or records without size loses the variable that changed. The policy needs cipher suite, direction, key epoch, authenticated bytes, blocks or an approved conservative bound, record count and the event that rotated keys.
This is not evidence that large records are unsafe. It is evidence that the safety calculation must match the negotiated envelope. A draft-defined maximum does not amend an AEAD primitive's security analysis, and a successful handshake does not certify the operator's key-lifetime model.
Rollout needs a resource ledger
A defensible rollout begins well below the protocol maximum. Select ceilings by workload and endpoint class. Measure memory under adversarial concurrency, slow senders, cancellation, padding and partial reads. Verify TLS overflow termination and DTLS discard separately. Exercise asymmetric client and server values. Confirm that observability preserves direction rather than displaying one merged limit.
Then trace outcomes above the record layer. Did the record authenticate? Did upper-layer reassembly complete? Was the application message accepted? Did the service meet its latency and resource objectives? Each stage needs a denominator. “Large-record success rate” is meaningless if it mixes negotiated permission, transmitted records and completed application operations.
Rollback must also be explicit. Lowering an advertised ceiling affects new negotiations; it does not magically rewrite established connection state. A staged plan needs connection draining, compatibility behavior, key-policy alignment and a way to distinguish peer non-support from local disablement.
Sources and limits
The frozen packet contains revision 03 and its official record, history and references; the TLS Working Group; TLS 1.3 and its bis draft; DTLS 1.3; the existing record-size extension; DTLS over SCTP; MLS; QUIC; AEAD requirements; AES-GCM cipher suites; and the live IANA TLS extension registry.
These sources establish protocol and registry text. They do not establish a shipping implementation, deployment, adoption, interoperability result, throughput gain, latency reduction, memory saving, outage, attack or application result. The opening capacity test is a constructed case used to expose the missing receipt.
Sources
- https://datatracker.ietf.org/doc/draft-ietf-tls-super-jumbo-record-limit/
- https://datatracker.ietf.org/doc/draft-ietf-tls-super-jumbo-record-limit/history/
- https://www.ietf.org/archive/id/draft-ietf-tls-super-jumbo-record-limit-03.html
- https://www.ietf.org/archive/id/draft-ietf-tls-super-jumbo-record-limit-03.txt
- https://datatracker.ietf.org/wg/tls/about/
- https://datatracker.ietf.org/doc/draft-ietf-tls-super-jumbo-record-limit/referencedby/
- https://www.rfc-editor.org/rfc/rfc8446.html
- https://datatracker.ietf.org/doc/draft-ietf-tls-rfc8446bis/
- https://www.rfc-editor.org/rfc/rfc9147.html
- https://www.rfc-editor.org/rfc/rfc8449.html
- https://www.rfc-editor.org/rfc/rfc6083.html
- https://www.rfc-editor.org/rfc/rfc9420.html
- https://www.rfc-editor.org/rfc/rfc9000.html
- https://www.rfc-editor.org/rfc/rfc5116.html
- https://www.rfc-editor.org/rfc/rfc5288.html
- https://www.iana.org/assignments/tls-extensiontype-values/tls-extensiontype-values.xhtml
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance