
Summary
- Multipath QUIC revision 21 standardizes the machinery that lets a connection use and observe several paths, while intentionally leaving packet scheduling and detailed retransmission policy to each endpoint.
- A validated or available path proves protocol eligibility. It does not prove spare capacity, a distinct bottleneck, acceptable cost, user consent, correct stream placement, current failover readiness or a better application result.
- Operators should preserve an evidence chain from path observation to scheduler decision to delivered outcome, rather than treating path count or connection uptime as the result.
The incident bridge had two green indicators. The primary access path was validated. The second path was validated too. Both were marked available, both had connection identifiers assigned, and neither had been abandoned. Yet the transfer was stalling because the sender kept placing fresh traffic on the path that was already congested.
That is not a contradiction in the protocol. It is the distinction the protocol is designed to preserve.
The multipath extension for QUIC has reached an advanced standards stage. Revision 21 was approved by the IESG in March 2026 and entered the RFC Editor queue; as of 2 October it was awaiting a second editor. It is therefore important not to call the document an RFC yet. It is equally important to understand what the work already specifies and what it deliberately does not.
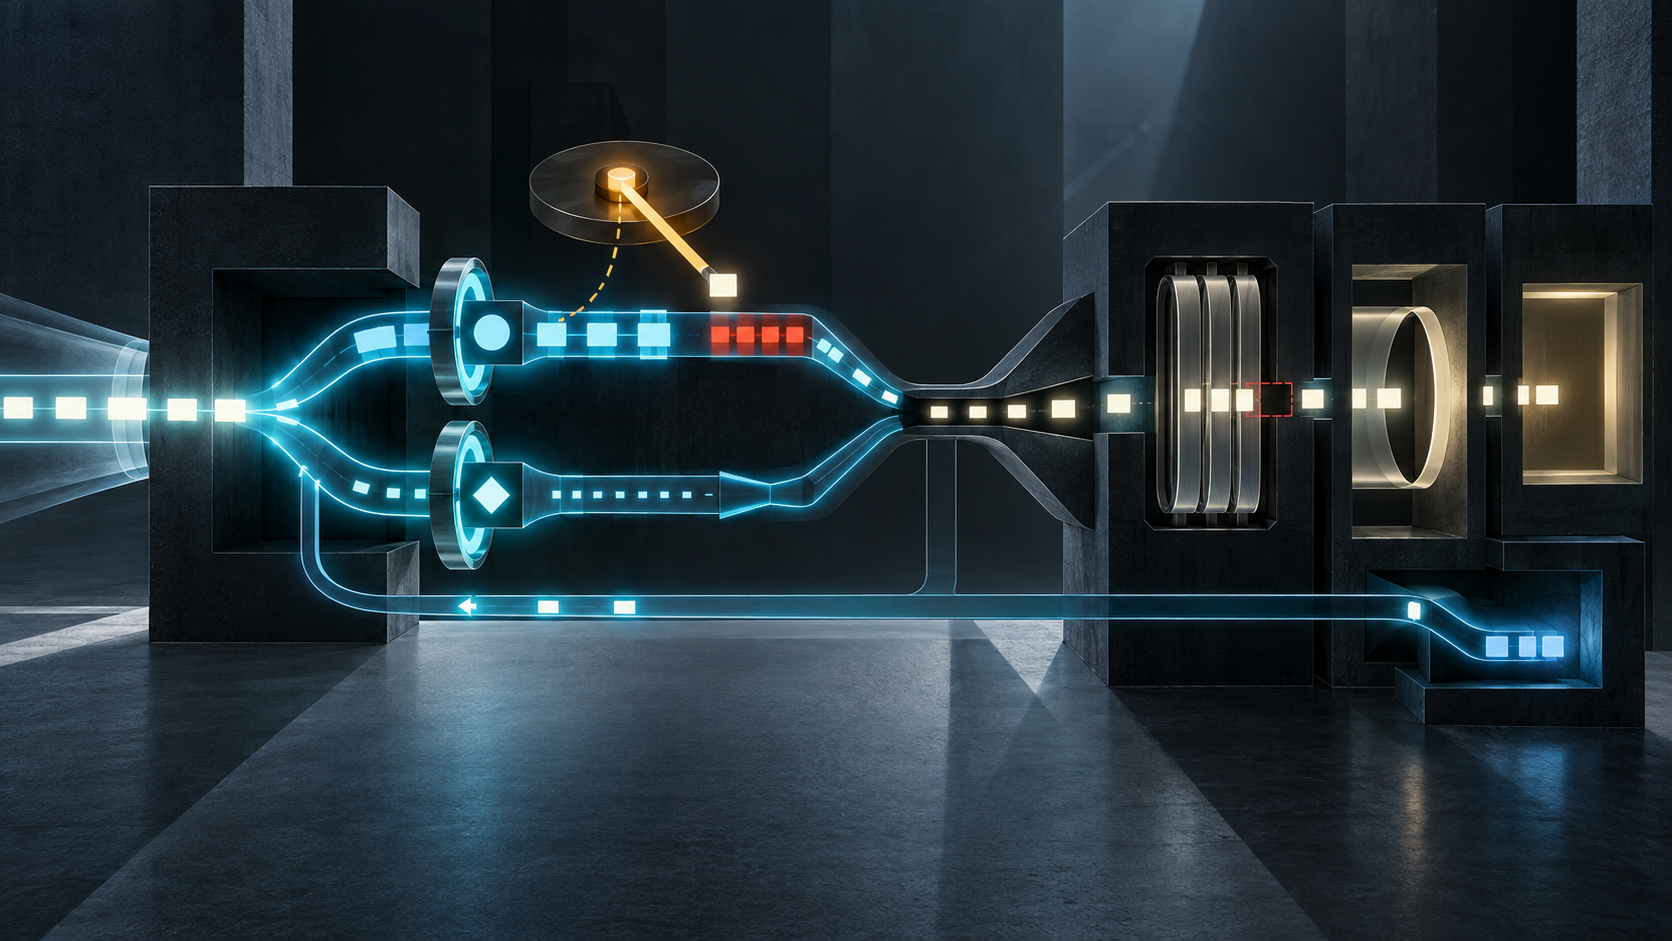
The extension supplies shared transport mechanics. Endpoints negotiate multipath capability. A path identifier can distinguish paths even when their address four-tuples are the same. Each path has its own packet-number space beginning at zero. Connection identifiers bind protocol state to paths. A client initiates a path and the server validates it. PATH_ACK frames report receipt, path-status frames communicate availability or backup preference, and path-abandonment frames close a path's role. Recovery and congestion state are maintained per path.
This is substantial work. It prevents two implementations from inventing incompatible meanings for a path number, acknowledgement or abandonment. It gives an operator observable state that did not previously exist in one interoperable vocabulary. But the common vocabulary stops before the allocation decision.
Revision 21 says an endpoint may use its own logic to split traffic when a peer marks a path available. It leaves packet scheduling to the implementation and application. It also leaves the detailed strategy for retransmitting lost data out of scope: an implementation may retransmit on the same path, another path, or several paths. Address discovery, and the policy for creating and tearing down paths, remain outside the common specification as well.
The consequence is simple: there is no standards-defined answer to the incident commander's question, “Why did the next byte go there?”
Valid is a narrow and useful word
Path validation establishes that the peer can receive packets at an address and helps constrain amplification. It does not measure unused capacity. A path can be valid and saturated. It can be valid and expensive. It can be valid while sharing the same last-mile bottleneck as another path. It can be valid while a corporate policy forbids it for a particular data class. It can be valid while a user has exhausted the cheap part of a cellular allowance.
Even path identity must be handled carefully. Revision 21 permits multiple path identifiers to use the same four-tuple. That allows protocol state to be separated where an implementation needs it; it does not manufacture a new fibre, radio channel or upstream queue. Counting path IDs and reporting “two independent routes” would replace a protocol fact with an unsupported infrastructure claim.
The AVAILABLE and BACKUP signals are preferences, not service guarantees. AVAILABLE suggests that the peer can use its own logic to distribute traffic over that path. BACKUP asks the peer not to send traffic there while another usable path exists. If every path is marked backup, the draft gives no special rule for choosing among them. An endpoint may also ignore the peer's preference. These choices are defensible because endpoints possess different application and platform knowledge. They also make local policy an explicit part of the outcome.
Precise telemetry can still be mislabelled
Multipath measurements have another trap. PATH_ACK may travel back on a path different from the one that carried the acknowledged packet. The resulting round-trip observation includes the forward path, the acknowledgement path and the scheduler's choice. The timestamp can be exact while a dashboard label such as “path 3 latency” is causally wrong.
The same caution applies to congestion. Revision 21 maintains separate congestion-control state for each path. That is necessary because paths can behave differently. It is not proof that the paths traverse different bottlenecks. RFC 6356 explained the fairness problem for coupled multipath congestion control in another transport context: several subflows sharing a bottleneck should not win more than their fair share merely because they are coordinated inside one connection. A multipath QUIC implementation needs an explicit position on shared-bottleneck behaviour; separate state alone cannot answer the question.
Application delivery adds a further layer. When packets carrying one ordered stream travel over paths with different delays, the receiver may have later bytes while it waits for an earlier gap. A rapid retransmission on the nominally faster path does not prove that the application saw the data earlier. QUIC packet numbers, acknowledgements, recovered bytes and application-visible stream delivery are related observations, not interchangeable ones.
Path maximum transmission units may differ, even when two path IDs use the same four-tuple. An implementation can simplify its behaviour by using a conservative common size, but that is its policy. A loss recovered on another path may require different framing. A report that only records “retransmission succeeded” omits which path, packet size, loss range and delivery consequence made success meaningful.
Build the evidence ledger around decisions
A credible operating record begins before the scheduler chooses. It should retain, at minimum:
- the addresses, connection identifier and path identifier observed at the time;
- the validation evidence and its age;
- the local and peer path-status signals, with direction and timestamp;
- measured loss, congestion state, PMTU and acknowledgement route;
- any evidence that paths share or do not share a bottleneck;
- the scheduler version, policy inputs and reason code;
- the bytes, stream class and sensitivity of the traffic assigned;
- the cost, quota, roaming, jurisdiction and user-consent constraints consulted;
- retransmission choices and reordering experienced;
- application-visible completion, deadline or quality result; and
- the fallback or rollback action actually available.
No single field proves the service outcome. The value lies in the chain. It lets an investigator distinguish “the second path was unusable” from “the second path was usable but disfavoured,” “the scheduler chose badly,” “both paths shared a queue,” and “transport recovery worked but ordered delivery still missed its deadline.”
This is also a security boundary. A compromised or buggy endpoint can manipulate local policy without violating the syntax of the extension. A network can expose a valid path that should not carry regulated traffic. A peer's availability signal cannot attest to a local cost ceiling. Automation should therefore consume path signals as inputs, not as authorisations.
Standards progress does not certify an implementation
IESG review records show that reviewers examined questions including scheduler policy, path count, quota and consent. The approved document can be sound while those deployment choices remain local. Standards approval is evidence that the protocol text passed its process; it is not a certificate for a vendor's scheduler, a mobile plan, a topology claim or a particular service-level objective.
The practical test is counterfactual. If the selected path performs badly, can the operator reconstruct the information available when the choice was made? Can it show whether the alternative was validated then—not merely now? Can it reproduce the scheduler decision? Can it tell whether an acknowledgement returned elsewhere? Can it identify the application outcome and compare it with the promised outcome?
If the answer is no, the organisation has multipath capability without multipath accountability.
That may still be useful. The extension can improve resilience and permit new scheduling strategies. But a leadership claim should remain bounded: the system had two protocol-eligible paths; this implementation applied this policy; under these measured conditions, it produced this result. Removing any of those clauses turns a testable statement into a slogan.
Sources
- https://datatracker.ietf.org/doc/draft-ietf-quic-multipath/
- https://datatracker.ietf.org/doc/draft-ietf-quic-multipath/history/
- https://datatracker.ietf.org/doc/draft-ietf-quic-multipath/references/
- https://datatracker.ietf.org/doc/draft-ietf-quic-multipath/referencedby/
- https://datatracker.ietf.org/doc/html/draft-ietf-quic-multipath-21
- https://www.ietf.org/archive/id/draft-ietf-quic-multipath-21.txt
- https://www.ietf.org/archive/id/draft-ietf-quic-multipath-21.xml
- https://www.rfc-editor.org/rfc/rfc9000.html
- https://www.rfc-editor.org/rfc/rfc9001.html
- https://www.rfc-editor.org/rfc/rfc9002.html
- https://www.rfc-editor.org/rfc/rfc9312.html
- https://www.rfc-editor.org/rfc/rfc6356.html
- https://www.rfc-editor.org/rfc/rfc8684.html
- https://www.rfc-editor.org/rfc/rfc8041.html
- https://www.iana.org/assignments/quic/quic.xhtml
- https://datatracker.ietf.org/doc/draft-munizaga-quic-alternative-server-address/
- https://heng.lu/running-code-primary-the-patch-needed-to-preserve-the-internet-original-design/
- https://heng.lu/minimum-initial-specification-localized-future-decision-voluntary-adoption-internet-coordination-system/
- https://heng.lu/on-reality-layers-symbolic-power-and-why-clarity-feels-so-hostile/
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance