
Summary
draft-tulshi-oauth-transactional-access-tokens-00proposes a JWT access token for one resource server and one short transaction, with a fresh authorization-server policy decision on every request.- The five-minute token does not make its refresh token, client credential, consent or client authority five minutes long; token validity, replay control, execution and outcome still require separate receipts.
The first revision of Transactional Access Tokens was posted on 29 September 2026. It is an individual Standards Track Internet-Draft, not an OAuth Working Group document, IETF consensus or an RFC. No source reviewed for this article establishes an implementation, interoperability result or deployment. Its value today is architectural: it exposes where a short-lived credential can narrow an action and where durable authority remains untouched.
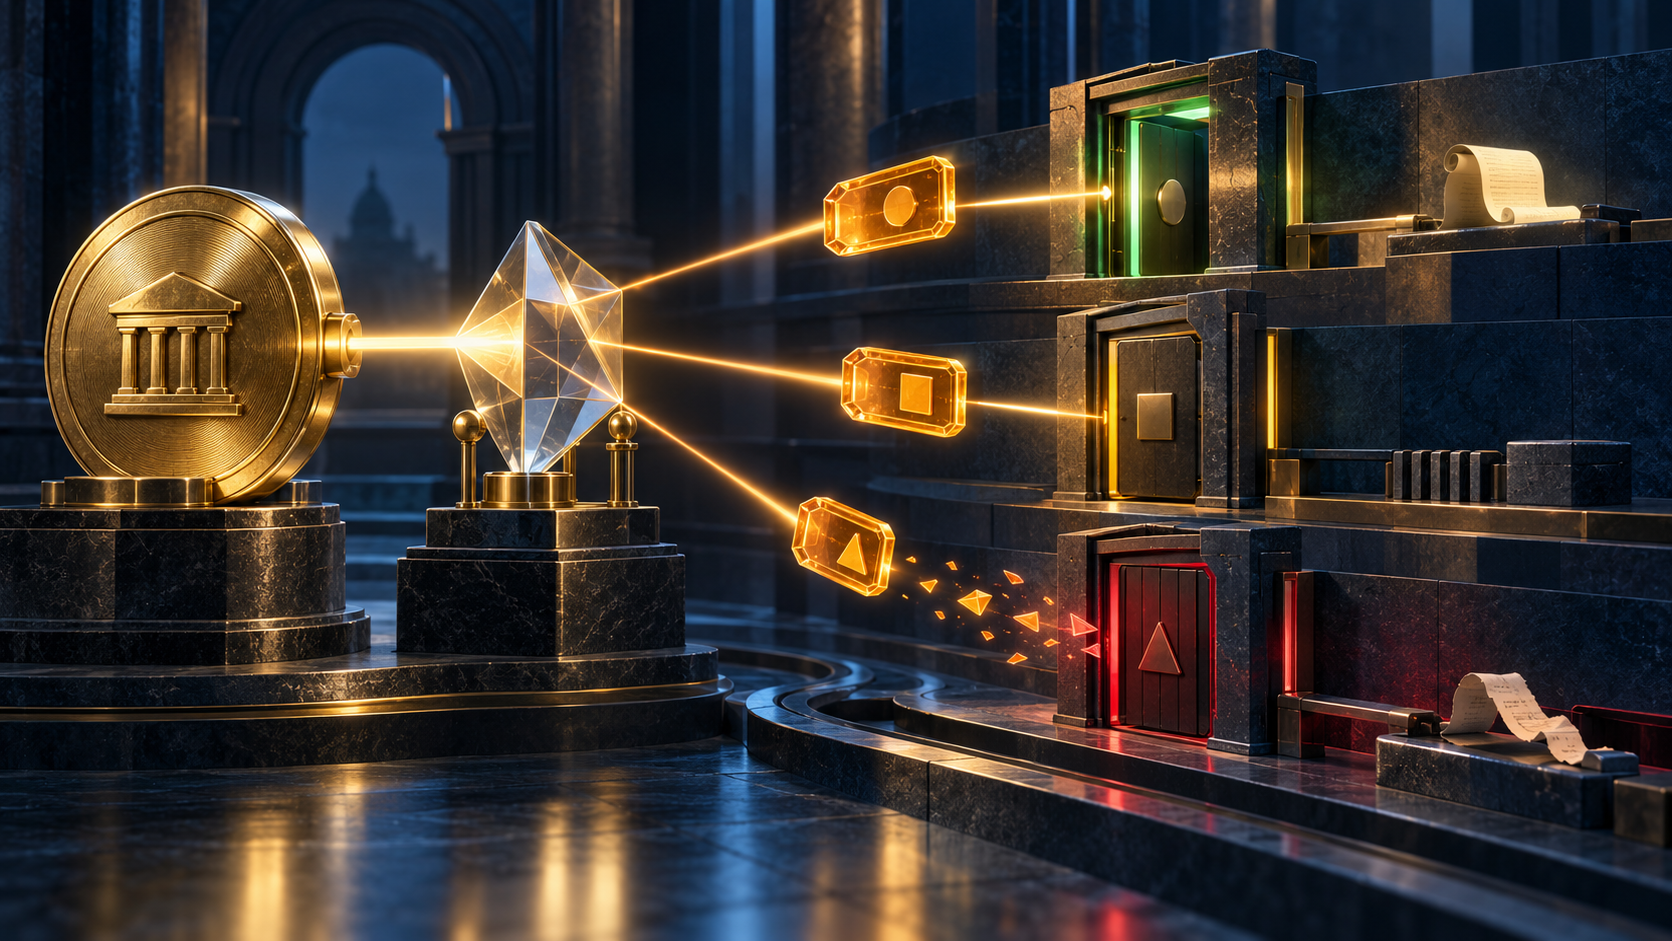
The proposal defines a Txn-AT as a profile of the RFC 9068 JWT access token. Its JOSE type is txnat+jwt, deliberately different from the ordinary at+jwt. Its audience must identify exactly one resource server. It carries a required transaction identifier, or txn, plus authorization-server-asserted transaction context in tctx and optional requester context in rctx. The recommended interval from issue to expiry is no more than 300 seconds.
Those are useful limits. A consumer that does not implement the profile should reject the unfamiliar token type instead of accepting it and discarding the transactional meaning. A resource server sees a token intended only for itself. Another resource server receives a different txn value for the same underlying transaction, so the two values should not be directly linkable without the authorization server.
But the control chain begins before the token. The client asks with a token-exchange grant, refresh token or client credential. The authorization server must evaluate policy on every request and may deny even when that durable credential is valid. A new transaction also returns an opaque handle with at least 128 bits of entropy. The handle can request additional Txn-ATs for other resource servers in the same transaction.
That gives an operator six distinct records. The durable credential explains why the client could ask. The policy receipt explains why this transaction and audience were approved. The handle connects later requests to the same transaction. The Txn-AT records what one resource server was told. An internal Transaction Token carries selected context inside that server's trust domain. A later execution record says what the service actually did.
Collapsing these records into “authorized” loses the improvement. A valid refresh token does not guarantee a later request should pass policy. A valid handle does not guarantee another resource should be added. A valid Txn-AT does not prove that the operation executed, executed once or completed. A downstream Txn-Token does not prove that external consent covered every internal effect.
The draft's most important sentence may be its admission that consent and client authority remain durable while tokens become per-transaction. User interaction need not occur for every transaction. An authorization code can obtain a refresh token once; later requests can proceed without the user. Client credentials are another durable root. If either is stolen, an attacker still has to pass current policy, but it can continue asking.
The security claim therefore rests on the quality of repeated evaluation. Policy must use current subject, client, attestation, resource, authorization details and environment. The server must not copy client-supplied context into tctx or rctx without evaluating it. A cryptographically valid token can still carry a bad conclusion if the policy used stale data, misunderstood scope or merely signed the client's claim.
The audience-specific txn also has a narrower privacy effect than its name suggests. It prevents two resource servers from joining a transaction by comparing that field alone. Yet client_id remains common. Tokens are issued close together. Subject identifiers may be pairwise only if the server actually configures them that way. Context can contain a distinctive amount, destination or workflow label. Above all, the authorization server can link the internal transaction to every audience.
One suggested construction derives each external identifier with HMAC over a server-side transaction reference and the audience. That avoids a mapping table, but makes key custody and retired-key retention part of the audit system. Compromise of the derivation key plus server-side references exposes cross-resource correlation. The server becomes both the policy chokepoint and the privileged observer.
Replay remains explicit. A bearer Txn-AT may be replayed during its short lifetime; the draft accepts that risk to keep resource servers stateless. It recommends DPoP or mutual TLS and permits a server that needs single use to track jti, but does not require that state. Five minutes can be a long window for a non-idempotent payment, deletion or infrastructure change.
Nor is txn an application idempotency key. It identifies a transaction from the authorization layer. It does not define whether two HTTP requests represent one business effect, whether a retry is safe or how to compensate after the first of several resource servers commits. The application still needs its own request identity, duplicate-effect rule, execution receipt and recovery path.
Token-type separation is where running code should be least forgiving. A Txn-AT resource must reject ordinary access tokens when transactional semantics are required. It must reject a trust-domain txntoken+jwt. Internal workloads must reject an external Txn-AT in place of the internal Transaction Token. Registration metadata saying a client requires Txn-ATs is not evidence that every route enforces the rule.
This is the thin-layer test. The common format can preserve issuer assertion, exact audience, evaluated context and provenance. It should not declare the authorization server's policy to be universal truth or the token to be proof of outcome. A local policy decision is valuable precisely because another decision remains possible when evidence, risk or resource changes.
Sources
- https://datatracker.ietf.org/doc/draft-ietf-oauth-transaction-tokens/
- https://datatracker.ietf.org/doc/draft-tulshi-oauth-transactional-access-tokens/
- https://datatracker.ietf.org/doc/draft-tulshi-oauth-transactional-access-tokens/history/
- https://heng.lu/minimum-initial-specification-localized-future-decision-voluntary-adoption-internet-coordination-system/
- https://heng.lu/on-reality-layers-symbolic-power-and-why-clarity-feels-so-hostile/
- https://heng.lu/running-code-primary-the-patch-needed-to-preserve-the-internet-original-design/
- https://openid.net/specs/openid-connect-core-1_0.html
- https://www.ietf.org/archive/id/draft-ietf-oauth-transaction-tokens-11.txt
- https://www.ietf.org/archive/id/draft-tulshi-oauth-transactional-access-tokens-00.txt
- https://www.rfc-editor.org/rfc/rfc6749.txt
- https://www.rfc-editor.org/rfc/rfc7519.txt
- https://www.rfc-editor.org/rfc/rfc7591.txt
- https://www.rfc-editor.org/rfc/rfc8417.txt
- https://www.rfc-editor.org/rfc/rfc8693.txt
- https://www.rfc-editor.org/rfc/rfc8705.txt
- https://www.rfc-editor.org/rfc/rfc8707.txt
- https://www.rfc-editor.org/rfc/rfc9068.txt
- https://www.rfc-editor.org/rfc/rfc9396.txt
- https://www.rfc-editor.org/rfc/rfc9449.txt
- https://www.rfc-editor.org/rfc/rfc9700.txt
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance