
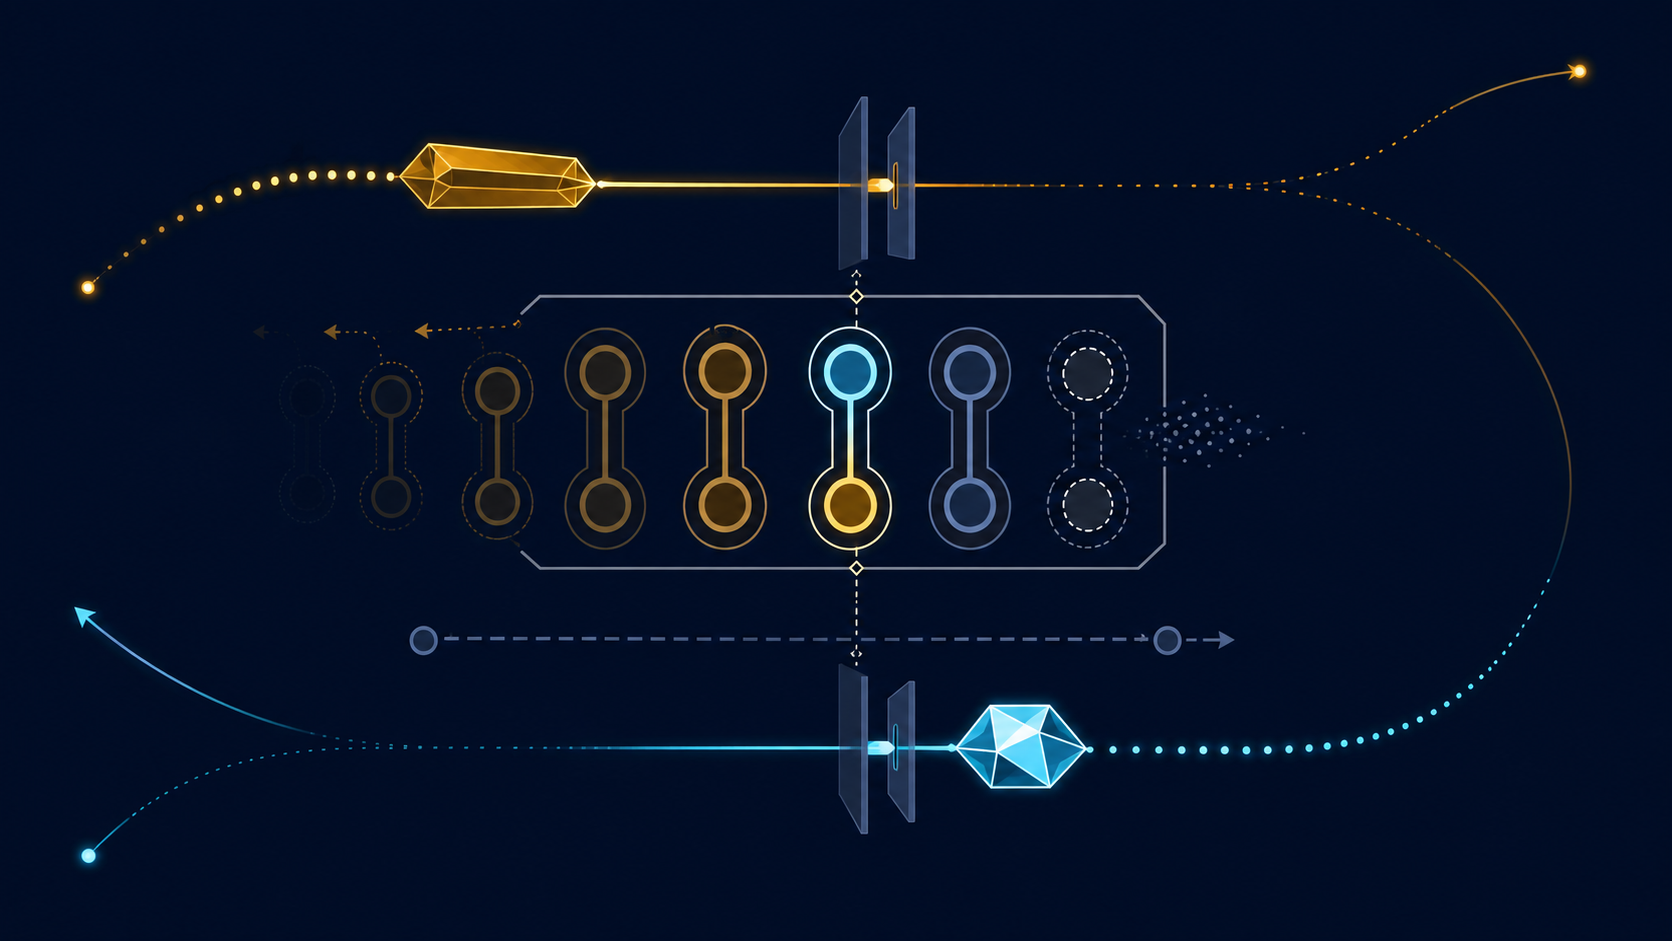
Summary
- Interleaved NTP reports a more accurate transmit timestamp for an earlier packet, but it needs a correctly matched and protected chain of state across exchanges.
- RFC 9769 requires uniqueness, single use, mode checks and basic-mode fallback because a timestamp without custody can be paired with the wrong packet and corrupt the measurement.
- Origin matching is not authentication, asymmetric-delay protection, source selection or a clock-update receipt; those decisions remain separately accountable.
The packet leaves the server before the best transmit timestamp is available to the NTP process. A network driver or hardware clock can observe the departure close to the wire, but by then the packet field has already gone. Putting that later knowledge into the packet that already left would require time travel.
RFC 9769 chooses a less theatrical solution. Send the accurate timestamp in the next packet.
That sentence sounds like a formatting trick. It is actually a custody problem. Once the timestamp for one transmission travels inside a later response, the receiver must prove which earlier exchange it belongs to. The server must retain the right pair long enough to find it, prevent the same identifier from naming two different transmissions, consume the match only once and retreat to basic mode whenever the chain breaks. Precision has improved; the amount of state that must remain coherent has also increased.
This is the boundary that matters for leadership. A better observation is not automatically a better truth claim. It becomes usable only when its lineage survives.
Why the accurate time arrives late
The basic NTPv4 exchange uses four times. The client records when its request left. The server records when that request arrived and when the response left. The client records when the response arrived. From those four observations, it estimates offset and round-trip delay.
The server's transmit time is awkward. A user-space implementation needs to place a value in the packet before asking the operating system to send it. Queuing, system calls, drivers and hardware then add delay after that estimate. A driver or network interface can stamp the actual departure more accurately, but the improved value becomes visible only after transmission.
One possible protocol would send a second packet carrying the correction. RFC 9769 rejects that shape because it invites amplification and can introduce packet-length asymmetry. Interleaving instead carries the previous response's transmit timestamp in a later response. It changes no NTP header and negotiates no new extension field. The existing origin, receive and transmit fields carry new relationships.
That economy is a minimum initial specification in Heng Lu's sense. It reuses the smallest shared surface that can carry the evidence. It does not pretend the reuse is free.
The origin field becomes a custody handle
In basic client/server mode, the response origin field echoes the transmit time of the current client request. The client compares it with saved local state and rejects a mismatch as bogus.
In interleaved mode, the client places the server's receive timestamp from the last valid response into the next request's origin field. The server searches its retained receive/transmit pairs for that value. If it finds the corresponding prior response, it can return the accurate transmit timestamp that became known after that response left.
The origin value is therefore a handle into server memory. It says: find the response in which you reported receiving this earlier request, then return the timestamp associated with that response's departure.
The match is exact but narrow. It does not identify a human, an organization or even an authenticated peer. RFC 9769 permits the server to partition saved state by source IP, but advises against using the UDP port because RFC 9109 allows clients to randomize the port on every request. NAT, address sharing and path changes keep network coordinates from becoming durable identity.
Treating an origin match as authentication would collapse two reality layers. It proves correspondence with a retained value. It does not prove who is entitled to use the correspondence.
Uniqueness is what keeps two histories apart
Suppose two server responses receive the same saved receive timestamp. A later origin value could match both. The server might return the transmit time of the wrong response, and the client could build one measurement from two unrelated exchanges.
RFC 9769 therefore requires transmit and receive timestamps to be unique enough for reliable mode detection and matching. A sender must not emit equal receive and transmit timestamps. If a clock lacks the resolution to distinguish them, one value can be moved by a single NTP fractional unit—about one quarter of a nanosecond. That adjustment is not a claim that the physical event happened later. It is an identifier-preservation device beneath the clock's useful precision.
This is an instructive distinction. A timestamp field can serve as both a time observation and a protocol correlation token. When those purposes diverge, the record must say which property a change protects. Otherwise an auditor may mistake a uniqueness adjustment for measured chronology.
The server must also consume a matched receive timestamp. It cannot use the same saved value again to classify another request as interleaved. Single use prevents one piece of history from authorizing multiple incompatible pairings.
Missing state means fallback, not invention
The first client/server exchange is basic. Only after the client has a valid response can it form an interleaved request. The server may discard old timestamp pairs to cap memory. A lost request or response can be tolerated if the needed pair remains in the queue. If the pair has gone, the server must not approximate or select the nearest value. It may respond only in basic mode and save fresh state for a later attempt.
This fallback rule is the protocol's strongest statement of epistemic discipline. A server unable to prove continuity does not label a response interleaved. It returns a less precise but correctly scoped measurement.
Operators often reverse that priority. They preserve the attractive high-precision label while silently filling a missing association from cache, address or timing proximity. That turns uncertainty into false accuracy. The correct availability response is degradation with provenance, not synthetic continuity.
RFC 9769 also warns clients not to rely on interleaved service. Attackers can fill or churn the server's timestamp store, including through spoofed traffic, forcing useful state to be dropped. Interleaving is an opportunistic improvement. Basic mode remains part of the operational contract.
Two valid responses form one measurement chain
Basic mode can use one valid request/response exchange at a time. Interleaved client/server mode needs two consecutive valid responses because the later packet delivers the prior transmission's accurate time. The client must protect the intervening state. An invalid response should not overwrite the values required to complete a later valid measurement.
This creates a temporal transaction. The first response is not merely old data; it opens state that the next response may close. A monitoring system should therefore record the association identifier, prior and current packet hashes, origin match, saved-pair age, whether the pair was consumed, mode classification and loss history. Logging only the final offset hides the chain whose integrity made it possible.
The RFC offers two four-timestamp sets after a successful interleaved exchange. The recommended set for delay-filtering clients describes the previous exchange. Another combines later observations to estimate a more current offset, but its much longer interval makes the delay estimate more sensitive to frequency error between the clocks. “Current” and “stable” are not the same optimization target.
The consumer owns that choice. The wire protocol supplies observations; it does not decide which estimator fits an operator's risk.
Symmetric and broadcast modes expose different boundaries
Interleaved symmetric mode is not just client/server mode with both arrows enabled. Peers can transmit on different schedules and may send more than one packet between receptions. RFC 9769 therefore limits when a peer may interleave: the association must support it, no intervening transmission may have occurred after the last valid reception, and the previous transmission must have been the sole response. The mode should be disabled by default and explicitly configured on the active side.
Those restrictions protect sequence identity. Without them, a missing response can make a remote transmit time pair with the wrong local receive time and produce a large error that still looks numerically precise.
Broadcast mode uses another arrangement. A packet carries its own approximate transmit time and the previous accurate transmit time in the origin field. A capable client should compare that origin against the preceding packet and decline interleaved synchronization when the gap is implausibly large. Broadcast does not measure path delay by itself; a client needing that evidence should use client/server mode.
One protocol family thus contains three different custody contracts. A dashboard that reports only “interleaved enabled” erases the conditions that decide whether a measurement is interpretable.
Better correlation does not authenticate time
RFC 5905's origin check and RFC 9769's extended matching make blind off-path forgery harder when values are unpredictable. They do not provide cryptographic identity. RFC 9769 warns against leaking receive timestamps and recommends randomizing every bit of client request timestamps so an attacker cannot easily guess the expected value.
RFC 8633 treats unexpected origin values as a monitoring signal and warns that control interfaces can disclose expected state. The security paper behind these recommendations shows how predictable or exposed client state enables off-path manipulation. These are operational reasons to protect the custody handle, not reasons to call it an identity credential.
Network Time Security adds authenticated key establishment and authenticated NTP exchanges. Even NTS does not defeat an on-path adversary who delays packets asymmetrically without modifying them. RFC 7384 treats delay as its own security problem, and RFC 8915 points to multiple sources or paths as partial mitigation.
The evidence chain is therefore longer than the timestamp pair:
- the packet fields must parse and match the intended exchange;
- the state pair must be unique, retained and unused;
- authentication must establish the communicating party where required;
- path-delay assumptions must remain credible;
- source filtering and selection must accept the sample;
- local clock policy must decide whether to slew, step or ignore;
- applications must separately show any effect that depended on the clock.
No earlier receipt can stand in for a later one.
Precision increases the duty to preserve provenance
High-resolution numbers encourage institutional overconfidence. A nanosecond-shaped value looks more authoritative than a millisecond-shaped one even when its association is missing. RFC 9769 teaches the opposite lesson: the better timestamp is useful because the protocol does more work to preserve its context.
That is running-code primacy applied to time. The RFC defines a possible exchange. An implementation trace can show which mode ran. A protected state record can show the pairing. A source-selection log can show why the sample survived. A clock-control record can show what changed. An application record can show whether that change mattered. Publication of the standard proves none of those outcomes.
The leadership decision is not whether precision is desirable. It is whether the organization can preserve the chain that makes precision honest.
Sources
- RFC 9769 — NTP Interleaved Modes
- RFC 5905 — Network Time Protocol Version 4
- RFC 9109 — NTPv4 Port Randomization
- RFC 7384 — Security Requirements of Time Protocols
- RFC 8633 — Network Time Protocol Best Current Practices
- RFC 8915 — Network Time Security for NTP
- The Security of NTP's Datagram Protocol
- Heng Lu — Running-Code Primacy
- Heng Lu — Minimum Initial Specification, Localized Future Decision, and Voluntary Adoption
- Heng Lu — On Reality Layers, Symbolic Power, and Why Clarity Feels So Hostile
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance