
In brief
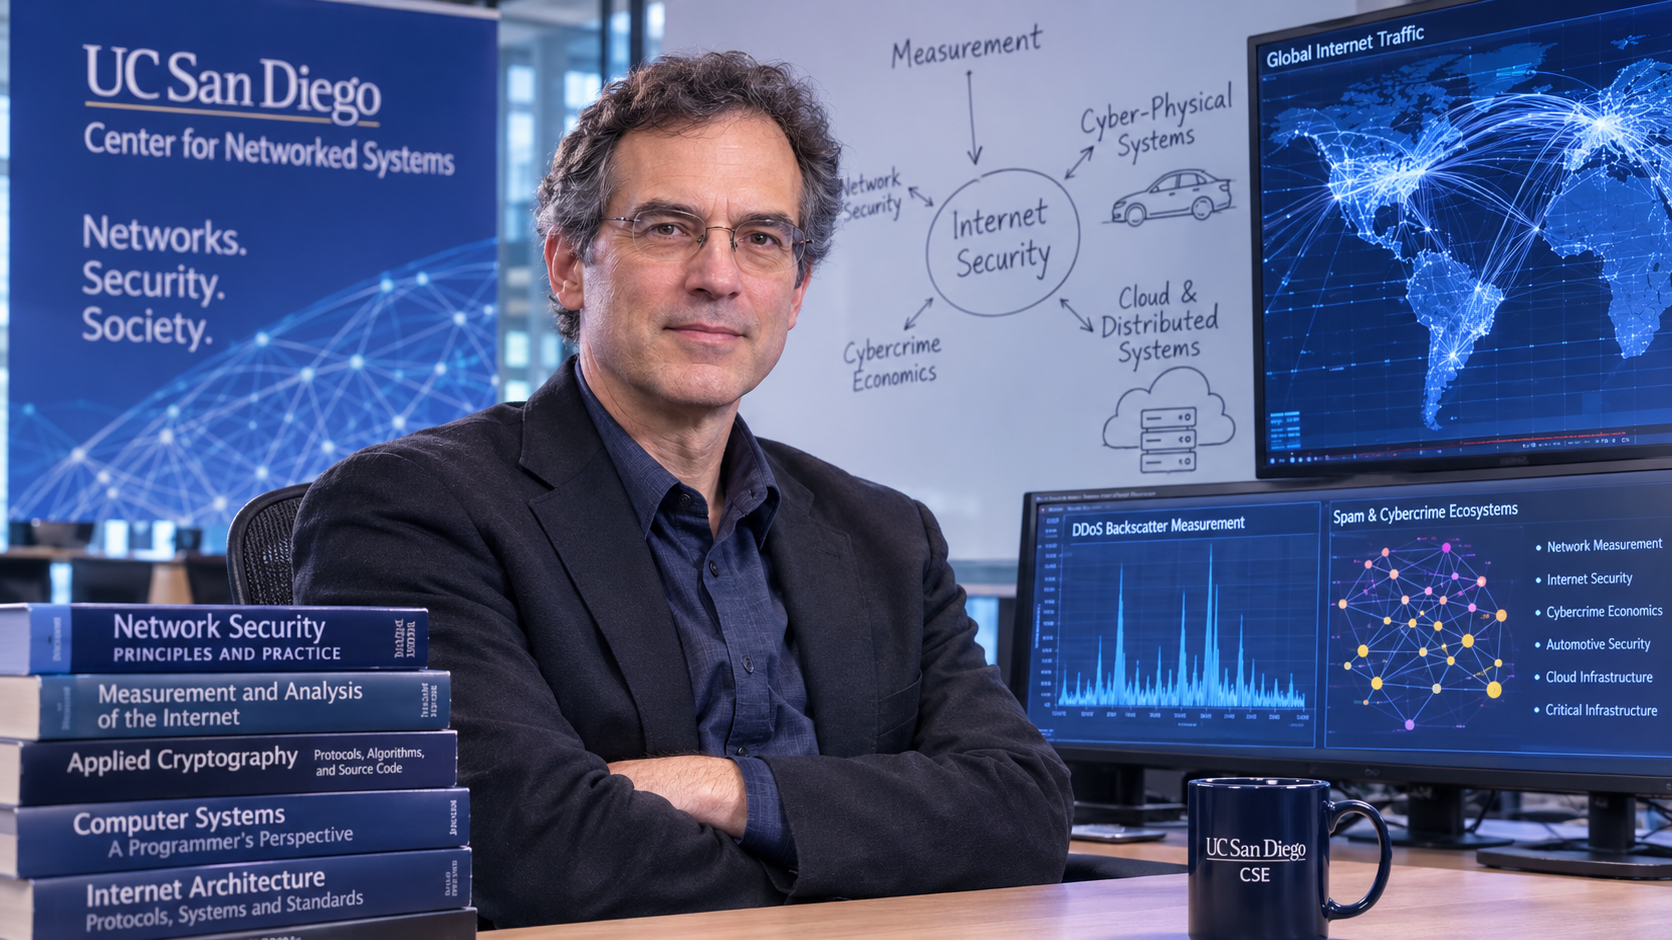
- Stefan Savage is the Irwin and Joan Jacobs Professor at UC San Diego and a researcher in empirical systems security whose work spans the measurement of network attacks, cybercrime economics, cloud systems, vehicles and other connected infrastructure.
- Early work on probabilistic packet marking and backscatter turned denial-of-service into a measurable systems problem, while keeping assumptions about deployment, spoofing and vantage points explicit rather than presenting any single method as a universal view of all attacks.
- Later research traced spam and counterfeit-drug markets through domains, affiliates, fulfilment and payment relationships, showing that distributed abuse can depend on concentrated commercial chokepoints whose effectiveness must be tested after intervention.
- Large-team automotive-security research connected experimental compromise to vehicle architecture, disclosure, update governance and public safety. Its evidence concerns the specific systems tested and should not be reduced to a single story about “hacking a car”.
- Savage’s enduring influence is associated less with one invention than with a method: isolate the mechanism, build a measurable system, preserve uncertainty, identify an institution with real leverage and test whether intervention changes the attacker’s economics or the system’s behaviour.
The packet was never the whole attack
The most useful fact about an attack is often not in the packet that arrives, but in the system that made the packet economically useful. A DDoS campaign depends on machines, source-address spoofing, network paths and the victim’s response. A spam business depends on affiliates, domains, hosting, fulfilment, payment processors and customers. A remote vehicle exploit depends on the architecture connecting externally accessible components to networks and devices relevant to safety. Throughout Savage’s career, these chains have repeatedly moved from background context to subjects of measurement.
This approach matters because a security incident is easily described at the wrong level. A packet flood looks like a purely network-level problem until the defender asks which machines produce it, which source addresses can be forged, which networks carry it and which mitigation service has sufficient visibility to respond. Spam appears to be a content problem until the business is decomposed into acquisition, hosting, fulfilment and payment. A vehicle exploit looks like one software bug until the attack path crosses a radio, head unit, internal buses, control units, cloud services and software-update processes.
Savage’s work is not unified by a single protocol or product. It is unified by an empirical question: what can be observed well enough to replace intuition with bounded but testable evidence? Early research on probabilistic packet marking asked whether a victim could reconstruct the path of spoofed traffic without requiring every router to retain every packet. Backscatter studies used responses sent to forged source addresses to estimate denial-of-service activity through a network telescope. Later research traced commercial dependencies in spam and illicit-drug markets.
Automotive studies mapped trust boundaries in connected physical systems. Cloud research tested assumptions about shared infrastructure instead of treating a provider’s promised isolation as a given.
The key word is “bounded”. None of these instruments sees everything. Packet marking depends on deployment and the nature of attack traffic. Backscatter sees attacks that produce the relevant class of responses. Payment-chain research depends on observable transactions and entity resolution. Vehicle experiments concern particular models, software versions and attack chains. A strong empirical result does not erase these boundaries; it makes them clear enough for another researcher, operator, bank, manufacturer or policymaker to decide whether the evidence is sufficient for a particular action.
Savage joined UC San Diego in 2001 and is now the Irwin and Joan Jacobs Professor in Computer Science and Engineering. He received a bachelor’s degree in Applied History from Carnegie Mellon University in 1991 and completed a PhD in Computer Science at the University of Washington in 2002. His career includes the 2015 ACM Prize in Computing, a 2017 MacArthur Fellowship and election to the National Academy of Engineering in 2023. UC San Diego reported in 2023 that his publication record had exceeded 150 peer-reviewed papers.
These honours matter as evidence of recognition, but not as a substitute for attribution. Major systems and studies associated with Savage involved co-authors, students, research staff and partner institutions.Practical Network Support for IP Tracebackwas written with David Wetherall, Anna Karlin and Tom Anderson. Backscatter work involved David Moore and Geoffrey Voelker, among others. Kirill Levchenko, Damon McCoy and wider teams participated in the cybercrime-economics programme. Automotive-security studies involved Tadayoshi Kohno, Stephen Checkoway and many co-authors. An accurate profile is not a sole-inventor story. It is the story of a researcher and research-environment builder who helped make security claims testable with data, while repeatedly returning to the limitations of the data itself.
Traceback began with deployment constraints, not a promise of perfect attribution
The 2000 paperPractical Network Support for IP Traceback, written with Wetherall, Karlin and Anderson, addressed a structural weakness in denial-of-service defence. Attackers could forge source addresses, leaving victims with packets from which the real path was difficult to determine. Retaining the complete history of every packet at every router was unrealistic, while a global logging system would have created its own storage, privacy and deployment problems.
The proposed response was probabilistic packet marking. A router would sometimes record fragments of path information in packets passing through it. After receiving enough attack traffic, a victim could combine those fragments and reconstruct probable routes. The design sought to add evidence without requiring every router to remember every packet and without assuming a single, centrally managed global tracing service.
The work mattered both because it was practical and because its assumptions were explicit. Reconstruction depended on packet volume, marking behaviour, route stability and the nature of the attack traffic. Fragmentation and spoofing patterns affected what the victim could recover. The mechanism also required router changes and deployment—something a paper could propose but could not impose across the public internet. Even a reconstructed route identifies infrastructure along a path; it does not prove the legal identity of the person or organisation behind an attack.
That boundary is easily lost when “traceback” becomes shorthand for “attribution”. Network evidence can narrow an investigation, identify likely ingress points, help operators coordinate and show which providers are positioned to act. On its own, it does not establish intent, ownership or culpability. The 2000 work is better understood as an effort to make an opaque event progressively more explainable, rather than as a universal mechanism that solved source attribution.
This distinction also anticipated Savage’s later logic. A security problem cannot always be solved by a theoretically complete system that the whole world must deploy at once. A more deployable approach looks for evidence that existing or incrementally modifiable infrastructure can reveal. Such an instrument may be incomplete, but its incompleteness can be analysed and its output combined with other institutional knowledge.
Traceback therefore belongs to the history of infrastructure for another reason: it raised the question of where responsibility for measurement should sit. Routers could add data. Victims could reconstruct paths. Operators could interpret them. Other institutions still had to decide which response was legitimate. The paper did not collapse these roles into one system, and that separation remains useful when security controls cross independently managed networks.
Backscatter turned unused address space into an observatory
Denial-of-service traffic with forged source addresses causes replies to be sent to addresses that did not originate the request. If some forged addresses fall within a large observed block of unused space—a network telescope—the unsolicited replies become a sample of attack activity. Savage’s backscatter work with Moore, Voelker and others used this side effect to estimate attack frequency, duration and victim types.
The method was powerful because it required cooperation from neither attacker nor victim. The instrument observed traffic reaching dark address space and inferred events elsewhere in the network. Infrastructure that appeared unused became a sensor. Instead of collecting incident reports only from organisations willing to disclose an attack, researchers could observe a distributed phenomenon through an independent vantage point.
This was not a complete census. The method was better at seeing attacks that used sufficiently random spoofing and caused victim responses capable of reaching the telescope. Non-spoofed botnets, other reflection patterns, traffic filtered upstream and attacks against services that did not generate the expected replies could be under-represented or entirely invisible. Estimates were also affected by routing to the telescope and by the size and location of the observed address block.
That is precisely why the measurement was strong: not because bias was absent, but because it could be identified and investigated. The instrument defined the population it could see. Within that population, researchers could compare duration, victim classes and intensity without presenting the sample as every DDoS attack on the internet.
Attack practices also change the relationship between an instrument and its population. Modern botnets may send traffic with genuine source addresses, use reflectors or employ protocols that create different side effects. A method built around one era’s spoofing must be revalidated rather than repeated as an eternal census. An adversary can alter the observation process itself simply by changing the attack mechanism.
Network telescopes remain important because unsolicited traffic also reveals scanning, worms, misconfiguration and other forms of network behaviour. Their long-term value depends on stable routing, careful data handling and time series long enough to distinguish structural change from short-term noise. When operators or policymakers begin relying on these observations, the telescope itself becomes measurement infrastructure, with requirements for access, privacy, governance and continuity.
The backscatter programme also made another recurring theme in Savage’s work explicit: visibility is created by vantage points, and every vantage point has an institutional politics. Who controls the address space? Who can access packet data? Which identifiers are retained? Which victims are notified? What happens when law enforcement requests information? A technically elegant instrument can create institutional power because it determines which events become visible enough to support action.
Worms made time part of the security boundary
Research into worms extended the same empirical logic from individual attacks to propagation. A worm is not only malicious code but a process moving through a population of vulnerable machines under constraints imposed by scanning strategy, address space, software distribution and defensive speed. Modelling that process makes response time part of the security architecture.
The practical value is comparative. Defenders can examine how patching, filtering, rate limiting, address blacklisting or coordinated response changes propagation. A model does not know the exact vulnerable population or predict every adaptation by an attacker. It provides a framework for testing how sensitive outcomes are to unknowns and how quickly a defence must work before the population changes irreversibly.
This research helped establish time as a systemic security variable. A vulnerability may be known while a fleet remains unpatched. An automated attack may move faster than ordinary change control. The defensive problem is not merely discovering a flaw, but shortening the interval between disclosure, patch availability, testing and deployment without creating a new outage.
The same trade-off now appears in cloud images, operating-system fleets, software supply chains, network appliances, connected vehicles and managed devices. Faster patching reduces the exposure window but increases the operational risk of rushed change. Slower validation protects service stability but leaves the vulnerability open for longer. An organisation must make this interval explicit rather than treating “patch available” and “risk removed” as the same event.
Savage’s broader availability research reinforces this conclusion: technical mechanisms operate inside institutions. A containment design that succeeds in an experiment may fail where operators have incomplete inventories, incompatible software, asymmetric incentives or no authority over the systems generating traffic. Security becomes a scheduling and coordination problem as much as a code problem.
Historical work on worms therefore remains relevant even as particular malware and network conditions change. The enduring question is: how quickly can an adversary exploit the structure of a population compared with the speed at which defenders can observe, decide and deploy? The answer depends on tooling, ownership, communication and risk tolerance, not only on the exploit.
Cybercrime economics followed the money through distributed infrastructure
Research into spam and counterfeit medicines changed the unit of analysis. Counting unwanted messages could estimate volume, but it did not explain why the business persisted. Savage and colleagues connected domains, affiliates, hosting, fulfilment and payment relationships to reconstruct parts of the value chain. The visible technical infrastructure was highly distributed, while commercial dependencies could be much more concentrated.
This concentration created a different kind of intervention point. Removing one compromised server or domain might be cheap for an offender. Losing an acquiring bank, card-processing relationship or durable fulfilment channel could be far more expensive. The research helped show why security policy can sometimes be more effective when directed at the economics of a system rather than its most visible technical artefact.
This conclusion is easy to overstate. Entity resolution across domains, merchants and payment records remains uncertain. Test purchases reveal only observable transactions. Companies may share infrastructure without being the same organisation. Payment relationships can change quickly. Some markets depend on intermediaries that a dataset cannot see. Research ethics and legal constraints limit data collection.
The defensible conclusion is therefore narrower: in the markets measured, distributed abuse depended on commercial relationships concentrated enough to be mapped and potentially influenced. That is stronger and more precise than claiming that the whole cybercrime economy has a single payment chokepoint. The next empirical question follows immediately: what happens after intervention at that chokepoint?
Here Savage’s method shifts from descriptive mapping to intervention research. A security study may identify a dependency, but it matters only if changing it alters the adversary’s costs or behaviour. After action by a bank, processor, hosting provider or domain registrar, researchers must measure substitution, duration, displacement and unintended consequences. Otherwise, a temporary decline can easily be mistaken for durable success.
The shift also redistributes responsibility. Network defenders may see malicious traffic but have no leverage over the business model. Banks and card networks may influence settlement but require merchant-level evidence compatible with their legal authority. Regulators and law enforcement can act in ways unavailable to researchers. Research is particularly useful when it builds an evidential bridge from a measured mechanism to an institution genuinely capable of changing the system.
A payment chokepoint matters only when replacement is costly
The word “chokepoint” sounds more durable than the evidence usually permits. In practice, it is a dependency sufficiently scarce, expensive or slow to replace that intervention genuinely changes an attacker’s operating economics. If an illicit merchant loses one bank and opens another account the same day without appreciable friction, the intervention has not removed the structural dependency. It has merely rerouted the business.
This is why before-and-after measurement matters. Researchers can examine transaction success, observable sales, domain churn, pricing, campaign volume or migration to other intermediaries. A decline in one channel may mean reduced demand, successful disruption, displacement to another processor or a measurement gap created by the intervention itself. Causal inference becomes difficult precisely because intervention changes the observed system.
Alternative payments further alter the map. Cryptocurrency, intermediated digital wallets, account-based payment systems and new settlement channels may weaken some dependence on conventional acquiring banks while creating new dependencies around exchanges, off-ramps, identity systems and liquidity. An old chokepoint may disappear; the system rarely becomes entirely free of dependencies.
This is especially important for policy because of collateral effects. A payment processor, hosting company or domain provider may serve legitimate users alongside abusive ones. A network block may affect unrelated traffic. Merchant identity may be uncertain. The party with operational leverage therefore needs evidence proportionate to the reversibility and severity of the action.
Temporary monitoring, rate limiting or additional verification may be justified at a lower confidence threshold than a public accusation, irreversible account termination or legal sanction. This is not a weakness of empirical security but recognition that measurement and governance must correspond. A bounded result can support a bounded response while further measurement tests whether escalation is warranted.
The deeper contribution of cybercrime-economics research is not the proposition that banks can “solve spam”. It is the reframing of criminal markets as systems with measurable dependencies and replaceable components. Security policy becomes a question of elasticity: how much cost can defenders impose at one dependency before the adversary moves, and how expensive is that transition?
Vehicle security turned software architecture into a public-safety issue
The automotive-security programme involving Tadayoshi Kohno, Stephen Checkoway, Karl Koscher and many others attracted attention because its demonstrations were concrete. Modern vehicles contained internal networks, electronic control units and external interfaces whose trust assumptions had developed in different engineering domains. The research showed that compromise could cross those boundaries and reach functions far beyond the entertainment system.
Reducing the work to a single “car-hacking” episode obscures its systemic contribution. The programme mapped architecture, demonstrated attack paths, coordinated disclosure and forced a broader industry discussion about the lifecycle security of machines that remain on the road for years. It connected software updates, diagnostics, wireless access, supplier boundaries and safety consequences.
The experiments concerned specific vehicles, components, software versions and test conditions. They did not prove that every model had the same attack path or that researchers could remotely control any vehicle. Industry responses involved manufacturers, suppliers, regulators, later researchers and internal security teams. Collective credit matters because the vulnerability was a property of an ecosystem, not one line of code.
The operational meaning is that connectivity turns a vehicle into part of digital infrastructure. Wireless interfaces, cloud services, mobile networks, diagnostics, update systems and internal buses form a chain. An exploit may move from consumer-facing software to safety-relevant functions when trust boundaries are weak. A fix may require not only a patch but changes to segmentation, update governance, supplier contracts, monitoring and recall processes.
This also changes the economics of the software lifecycle. Vehicles may remain in service far longer than ordinary consumer software. Hardware replacement is expensive. Owners do not always install updates promptly. Suppliers maintain components on different schedules. A vulnerability can persist across a fleet even after the manufacturer has prepared a technical fix.
Responsible disclosure is therefore inseparable from the engineering result. Premature publication may expose owners before remediation reaches the fleet. Excessive delay leaves a serious threat hidden. Researchers and manufacturers must agree sufficient time and detail for a practical response while preserving the public value of the result. No universal disclosure rule can resolve this tension because severity, exploitability and update capability vary.
The vehicle programme anticipated a wider cyber-physical shift. Connected medical, industrial and aviation systems face similar questions: external connectivity crosses physical processes, software lives longer than web services, suppliers share responsibility and safety consequences limit tolerance for experimentation. Savage’s continued participation in vehicle-security research in 2026 demonstrates the field’s continuing relevance, but claims about present systems must remain tied to specific documented platforms and projects.
Cloud side channels tested assumptions about shared infrastructure
Cloud computing creates another kind of security boundary. Customers share hardware, networks and control systems while expecting isolation strong enough to prevent one tenant learning about or influencing another. A provider can describe its isolation model, but empirical security asks whether observable behaviour supports it.
Savage’s cloud and side-channel work belongs to this tradition: testing assumptions about shared infrastructure rather than accepting architectural promises as given. Co-residency signals, placement behaviour or hardware leakage can make the separation of formally isolated tenants an empirical question. Specific mechanisms change along with provider schedulers, processors, virtualisation layers and mitigations.
This pace of change makes historical caution particularly important. A side channel demonstrated on one cloud generation may be mitigated or irrelevant in a newer architecture. Conversely, a new accelerator, memory subsystem or placement policy may create another leakage path. The enduring contribution is the method of testing isolation in the environment where it is claimed, rather than extrapolating one experiment indefinitely.
Cloud research also returns Savage’s work to infrastructure economics. Shared systems are valuable because multiplexing increases utilisation and lowers computing costs. Isolation mechanisms make such sharing acceptable. If the security boundary weakens, the economic advantage may be undermined by customer demand for dedicated resources, additional controls or separate environments.
The measurement challenge again concerns visibility. A tenant sees only part of the scheduler and hardware. The provider has more operational telemetry but may not disclose it publicly. Researchers may have to infer placement or leakage indirectly. A result can therefore be technically correct while its significance for the broader population remains uncertain if the proportion of affected infrastructure is unknown.
This is a familiar pattern in Savage’s work: an instrument creates a bounded view, and interpretation must remain within that boundary. A demonstrated mechanism is strong evidence that an assumption can fail under stated conditions. It is not a census of all providers, regions or hardware generations. The next question is whether a provider can detect, mitigate and verify the issue at fleet scale.
Measurement changes the politics of who is asked to act
Measurement does more than describe a threat. It can redirect attention and responsibility. When denial-of-service is estimated through backscatter, network operators and mitigation providers receive evidence about attack scale. When spam campaigns are mapped through payment relationships, banks and card networks become security actors. When vehicle interfaces are shown to cross safety boundaries, manufacturers, suppliers and regulators face a problem that can no longer be left to an ordinary IT team.
This redistribution of responsibility is one reason empirical work has policy consequences. Technical communities often focus on the actor closest to the packet or vulnerable code. A system map may show that another actor has far greater leverage. That finding is uncomfortable because the intermediary did not create the abuse and may serve many legitimate customers. Intervention transfers not only risk but cost.
The party asked to act needs evidence suited to its authority. A network operator may require prefixes, paths and traffic signatures. A bank needs merchant and transaction evidence. A manufacturer needs a reproducible vulnerability and the affected architecture. A regulator needs a record supporting proportionate action. Research that identifies a chokepoint but does not build an evidential bridge to the responsible institution may create a headline without enabling practical intervention.
Savage’s work repeatedly built such bridges, although outcomes differed across domains. Some mechanisms changed how an entire field measured a problem. Others influenced disclosure or industry practice. Still others identified intervention points whose long-term effects are difficult to separate from adaptation. An accurate profile must keep these categories distinct rather than turning influence into a universal claim of policy success.
There is also a converse risk. Institutions with authority may demand unattainable certainty where a reversible defensive step is justified. Security decisions rarely enjoy perfect attribution. A mature process distinguishes reversible from irreversible action, states the confidence attached to each and measures the result after deployment.
This discipline protects both sides of the decision. It prevents bounded measurement from being stretched into a punitive conclusion unsupported by the evidence, and prevents uncertainty from becoming an excuse for inaction when a limited protective measure is proportionate. Measurement gains authority not by claiming omniscience but by matching its evidential strength to a particular decision.
Research ethics become harder when the observed population did not consent
Internet-security measurement often observes people and systems that did not volunteer for a study. A telescope receives traffic from attackers, victims and misconfigured devices. A spam investigation may make test purchases and gather commercial records. Vehicle research may reveal a flaw whose publication affects owners and manufacturers. The ethical question is not an appendix; it determines what may be measured, retained, published and used to support action.
Researchers must minimise harm, protect sensitive data, coordinate disclosure and avoid turning measurement into a new attack surface. They must also describe uncertainty so that policymakers or companies do not treat an inferred entity relationship as proven identity. The more actionable a dataset becomes, the greater the cost of a false positive.
The same problem appears in intervention research. Identifying a payment chokepoint may prompt action against an intermediary serving legitimate commerce as well as abuse. Measuring vulnerability at scale may expose systems before owners can patch them. Publicity may accelerate remediation while also educating adversaries. Ethical review must therefore consider not only whether the underlying data are accessible, but the mechanism of response.
Responsible disclosure is one practical bridge. Researchers may coordinate with vendors and institutions before publishing high-impact flaws, allowing time for remediation while preserving the ability to document the finding. The process remains contested: vendors may request more time, researchers fear indefinite delay, legal risk may affect publication and incomplete fixes leave users exposed.
Measurement ethics also covers collateral traffic and data retention. A network telescope may receive identifiers or payload fragments that researchers did not seek. Payment studies may touch real customer transactions. Vehicle experiments may require expensive or scarce hardware. An instrument must be designed not only for technical validity but for accountable access.
Savage’s work is most useful when these limits remain inside the narrative. Measurement creates leverage by turning anecdotes into evidence. It also creates power for the party that defines the sample, assigns labels to actors and chooses an intervention. A mature empirical-security programme makes that power visible, documents uncertainty and evaluates what happened after other institutions acted.
UC San Diego became part of the measurement infrastructure
Savage’s institutional role is closely connected to UC San Diego and the Center for Networked Systems. Official pages have used the terms director and co-director at different times, so the exact current title should be dated rather than silently compressed into one permanent formulation. The more durable fact is that UC San Diego has remained his academic base since 2001 and that centre leadership forms part of the environment through which research is organised.
A research centre is infrastructure in a different sense from a router or telescope. It assembles faculty, students, engineers, industry relationships, equipment, datasets and administrative support over enough time for a project to become a sustained programme rather than end with one paper. Large empirical studies often depend on access that no individual researcher could maintain alone.
This structure explains why collaborative authorship is not merely a courtesy. Students and co-authors design mechanisms, write code, conduct experiments, negotiate data access and interpret results. Industry partners may provide systems or disclosure channels. External institutions may supply measurement vantage points. The centre coordinates these resources without making every result automatically the achievement of its senior leader.
Centre leadership also changes the form of a researcher’s influence. Agenda-setting, mentorship and industrial collaboration determine which questions become tractable and which datasets are available. A senior researcher can influence a field by building an institution for repeatable measurement, not only by publishing its most highly cited paper.
This institutional effect is difficult to measure. Publication counts and awards show output and recognition, but do not reveal which infrastructure costs were covered by grants, which access came through collaborators or how many failed experiments preceded a public result. The source material does not support a consolidated laboratory budget or a complete funding map.
The absence of a clean financial figure is not a defect in the profile. University research is funded through appointments, federal and foundation grants, centre partnerships, industry support and project-specific arrangements. Editorial discipline requires naming the type of support when documented without turning collaboration into ownership or claiming that a sponsor controlled the outcome.
Awards recognise a programme, not sole ownership of its results
Savage received the ACM Prize in Computing in 2015, became a MacArthur Fellow in 2017 and was elected to the National Academy of Engineering in 2023. A 2023 institutional account from UC San Diego reported more than 150 peer-reviewed papers. These are strong indicators of sustained influence in systems and security.
They do not, however, resolve attribution within multi-author research. Traceback, backscatter, payment intervention and automotive-security work involved collaborators whose ideas, code, measurements and institutional support were necessary. Students and research staff often built the systems that made studies at scale possible. Centres supplied equipment, access and continuity.
This distinction matters more than etiquette. Infrastructure knowledge survives when methods, datasets and institutional practices outlast one researcher. A centre that trains students and maintains measurement systems can create a lineage of work. A profile that concentrates every achievement on a senior figure hides the mechanism through which the field actually develops.
Such simplification also creates a technical error. A reader who believes one person “invented” a programme may assume that person controls every implementation, dataset or later extension. In practice, co-authors move to other institutions, datasets acquire new stewards and follow-on work changes the method. Collaborative attribution more accurately shows where knowledge and decision rights reside.
Savage’s awards should therefore remain recognition of a broad programme. They are not technical evidence that a particular mechanism is correct, do not prove that a particular intervention caused a policy outcome and are not evidence of company ownership or personal wealth. Available materials do not establish a general commercial-ownership claim or support estimates of personal net worth or equity.
The portfolio extends beyond cybercrime economics
Savage is often associated with empirical measurement of cybercrime, but his portfolio spans networking, systems security, availability, cloud infrastructure and cyber-physical systems. This breadth matters because the methods do not produce the same kinds of output or authority.
IP traceback research developed protocol and algorithmic mechanisms to help defenders reconstruct probable attack paths from packet evidence. Backscatter measurement used network telescopes to estimate attack activity. Worm research examined propagation and containment. Spam and e-crime studies mapped commercial dependencies. Payment-intervention research asked whether economic chokepoints could change behaviour.
Automotive work tested vehicle architecture and remote attack chains under controlled conditions. Cloud research investigated co-residency and leakage from shared infrastructure. Disclosure work translated technical evidence into remediation processes. Teaching and mentorship continued the programme as human-capital infrastructure through students who carried its methods into other organisations.
Each field has its own practical limit. Traceback did not become a universal global service. Backscatter has sampling bias. Worm models depend on historical network conditions and an unknown vulnerable population. Cybercrime markets adapt. Payment systems can be replaced. Vehicle findings are tied to models and versions. Cloud providers change schedulers, hardware and mitigations.
The unifying asset is neither a specification nor a commercial product. It is a way of turning hidden dependencies into observable mechanisms. Savage is therefore difficult to compare with a single “competitor”. CAIDA and other measurement groups operate related internet-observation infrastructure. Security-economics researchers study incentives and markets. Commercial threat-intelligence companies collect proprietary abuse data. Automotive-security laboratories test other manufacturers and architectures. Law-enforcement bodies possess investigative authority and evidence unavailable to academia.
These groups overlap with Savage’s work without replacing one another. A commercial threat-intelligence provider may have current customer telemetry unavailable to researchers, while its methods and datasets may be less open. A university telescope may provide reproducible long-term evidence while seeing only one class of traffic. Law enforcement may compel information without publishing its methods. Academic researchers may reveal architecture and causality without authority to carry out direct remediation.
The comparison clarifies the role: Savage’s distinctive contribution is the sustained search for measurable dependencies and intervention points across technical and economic systems. The approach is strong precisely because it relies on unusual datasets, collaborative teams and an explicit willingness to state what an instrument cannot see.
Funding, ownership and geography set boundaries around the story
Savage’s work is funded through university appointments, research grants, centre partnerships and project-specific support. Industry-sponsored research and centre membership may provide equipment, data access and engineering relationships. Funding alone neither confirms nor refutes a finding, but the funder, project and conflict-disclosure context should remain visible.
The available evidence does not provide a current audited personal laboratory budget. Nor does it support a general company-ownership claim, an estimate of personal net worth or a consolidated financial value for the entire research programme. Awards may include fellowship or recognition funding, but should not be used as evidence of wealth.
The institutional base is in San Diego, California, while the systems studied are global. Attack traffic crosses countries. Hosting and payment chains pass through different jurisdictions. Vehicle supply chains involve manufacturers and suppliers in several regions. Cloud infrastructure is globally distributed. The geographical meaning of the work therefore lies more in its systems and samples than in the university’s address.
A vantage point in one address block or commercial market does not automatically represent the whole world. Geography becomes part of the sampling model. Payment relationships vary by country. Hosting markets have different levels of concentration and enforcement. Disclosure law differs by jurisdiction. Vehicle models and software versions are released unevenly.
The same is true historically. Savage completed doctoral work at the University of Washington in Seattle before moving to UC San Diego in 2001. Early network conditions reflected the architecture and attack practices of their era. Later research moved into commercial payment systems, cloud platforms and cyber-physical infrastructure. Continuity lies in the empirical method, not in an assumption that one dataset or intervention applies identically across decades.
Limitations that cannot be removed with a single qualification
Vantage-point bias is the first structural limitation. Every telescope, transaction feed, test platform or experimental fleet sees only part of the system. Better instrumentation can reduce uncertainty, but no vantage point becomes a complete census simply because its dataset is large.
Adversary adaptation is the second. Attackers may change protocols, providers, domains, payment methods, exploit chains and operational timing after intervention. A result that was accurate before action may become less representative precisely because the action changed the system.
Entity resolution is the third. Domains, affiliates, processors, campaigns and infrastructure must be linked through noisy records. Shared services can make unrelated actors look connected, while deliberate obfuscation conceals real relationships. False links distort both market structure and the legitimacy of intervention.
Collaborative attribution is the fourth. Major results have many authors and partner institutions. Simplifying the story around a prominent senior researcher creates a heroic narrative that is editorially attractive but technically inaccurate.
Disclosure risk is the fifth. Publishing an exploit may help defenders and attackers. Delay leaves users exposed. Appropriate timing depends on severity, patchability, fleet-update capability and the readiness of affected institutions to act.
Research ethics is the sixth. Measurement may collect unsolicited traffic, involve test purchases or touch real systems. Privacy, collateral harm and assumptions of informed consent differ from ordinary laboratory experiments because the measured population may not know it is being observed.
Causal intervention claims are the seventh. Markets change for several reasons at once. A decline after a payment intervention does not prove that the intervention alone caused it, while a later rebound may reflect adaptation rather than failure of the original measurement.
Historical technology drift is the eighth. Internet architecture, botnets, payment methods, cloud hardware and vehicle software change quickly. Older work may remain methodologically important while becoming a weak description of current operational conditions.
Award overreach is the ninth. Prestigious honours summarise a career in broad language. They do not replace mechanism-level attribution or current production evidence.
Current-role ambiguity is the tenth. Official UC San Diego pages have used both director and co-director for Savage’s role at the Center for Networked Systems. The exact current title should be checked when material rather than smoothed into a permanent formula.
These constraints are not footnotes weakening the programme. They are part of its central lesson. Empirical security earns credibility when the relationship between instrument, population and conclusion remains visible.
Measurement gains authority only when its blind spots remain visible
Empirical security research gains influence because it replaces speculation with observations that other institutions can use. The same influence creates a risk: a striking dataset may appear more complete than its vantage point permits. A network telescope, a set of test purchases or an experimental vehicle can reveal a mechanism with exceptional clarity while leaving large parts of the population outside its view.
Backscatter illustrates the problem well. Unsolicited replies reaching dark address space made a class of spoofed-source attacks measurable without cooperation from attackers or victims. The inference was strong because its assumptions could be stated. Attacks using other addressing or reflection patterns were less visible. As adversaries adapted, the relationship between instrument and population changed.
Cybercrime supply-chain research created another vantage point. Domains, affiliates, fulfilment services and payment relationships revealed dependencies that packet counts did not. Concentration in acquiring or settlement created leverage, but identification remained probabilistic and markets could adapt. A payment intervention that reduced observed sales through one channel might simply displace transactions elsewhere.
Vehicle research added the disclosure problem. Demonstrating a path from an external interface to safety-relevant functions could accelerate repair and public understanding, but publication timing affected owners and manufacturers who had not agreed to participate in the study. The work’s value depended on controlled testing, collaborative attribution and a disclosure process that gave affected parties a genuine opportunity to respond.
These examples explain why intervention and measurement should be designed together. A study identifying a chokepoint should specify in advance the observable change expected from successful action. It should also identify plausible substitutes and collateral effects. An institution can then choose a proportionate, reversible response before moving to irreversible action.
Authority to act remains outside the paper. Network operators, banks, manufacturers and regulators have different tools and legal duties. Researchers can explain a mechanism and assess its significance, but do not inherit an institution’s power merely by supplying evidence. Conversely, an institution should not demand impossible certainty when limited defensive action is justified.
Long-term research infrastructure matters because adversaries adapt. Datasets, telescopes, experimental platforms and industry relationships must survive long enough to test whether an observed effect persists. Students and collaborators carry methods into new settings and often build the systems that make evidence possible. A profile concentrating every result on a senior researcher loses the institutional mechanism through which empirical security accumulates knowledge.
The enduring method is to find a narrow dependency within a large problem
Across denial-of-service, worms, spam, payments, cloud systems and vehicles, one move recurs: a broad threat is decomposed into mechanisms that can be observed. An attacker may be distributed, but traffic has paths. A market may use thousands of domains, but payments may converge. A vehicle may contain many components, but trust crosses particular interfaces. Once a dependency is visible, defenders can ask which actor has the authority to change it.
The method reaches its limit when the system adapts faster than measurement. Attackers learn which channels are observed. Encryption and service consolidation conceal detail. Legal and commercial relationships change. The relevant metric may shift from packet volume to account creation, from card payments to another settlement system or from a vehicle interface to a cloud service. A successful measurement programme must change its instrument along with the system.
The public-interest test is concrete. Does the work improve the ability to estimate scale, explain a mechanism or evaluate an intervention? Does it preserve collaborator credit and evidential limits? Does it lead to a response whose effects are measured rather than assumed? These questions are stricter than asking whether a paper was influential and closer to why empirical security matters to infrastructure operators.
The standard for future work is therefore demanding but practical. New measurements should state their vantage point, preserve collaborator credit, disclose ethical controls and define the observation that would weaken the conclusion. Interventions should be evaluated long enough to reveal substitution. Institutions acting on evidence should retain responsibility for proportionality and error.
Savage’s enduring contribution is a discipline of decomposition. A large threat is reduced to traffic, dependencies, incentives and decision points that can be observed. The result does not make the adversary completely visible. It gives operators and policymakers a better basis for asking which institution can intervene, which action is proportionate and which observable result would show that the system genuinely changed rather than merely moved.
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance