
Summary
- Singapore’s National Cybersecurity Command Centre (NC3) is being expanded to fuse threat intelligence, find exposed critical systems, block known malicious domains and coordinate incident response.
- The operating test sits with infrastructure owners: a national warning must become a logged repair without taking a live service down.
Singapore wants its cyber defenders to see across institutional borders. Attackers already do.
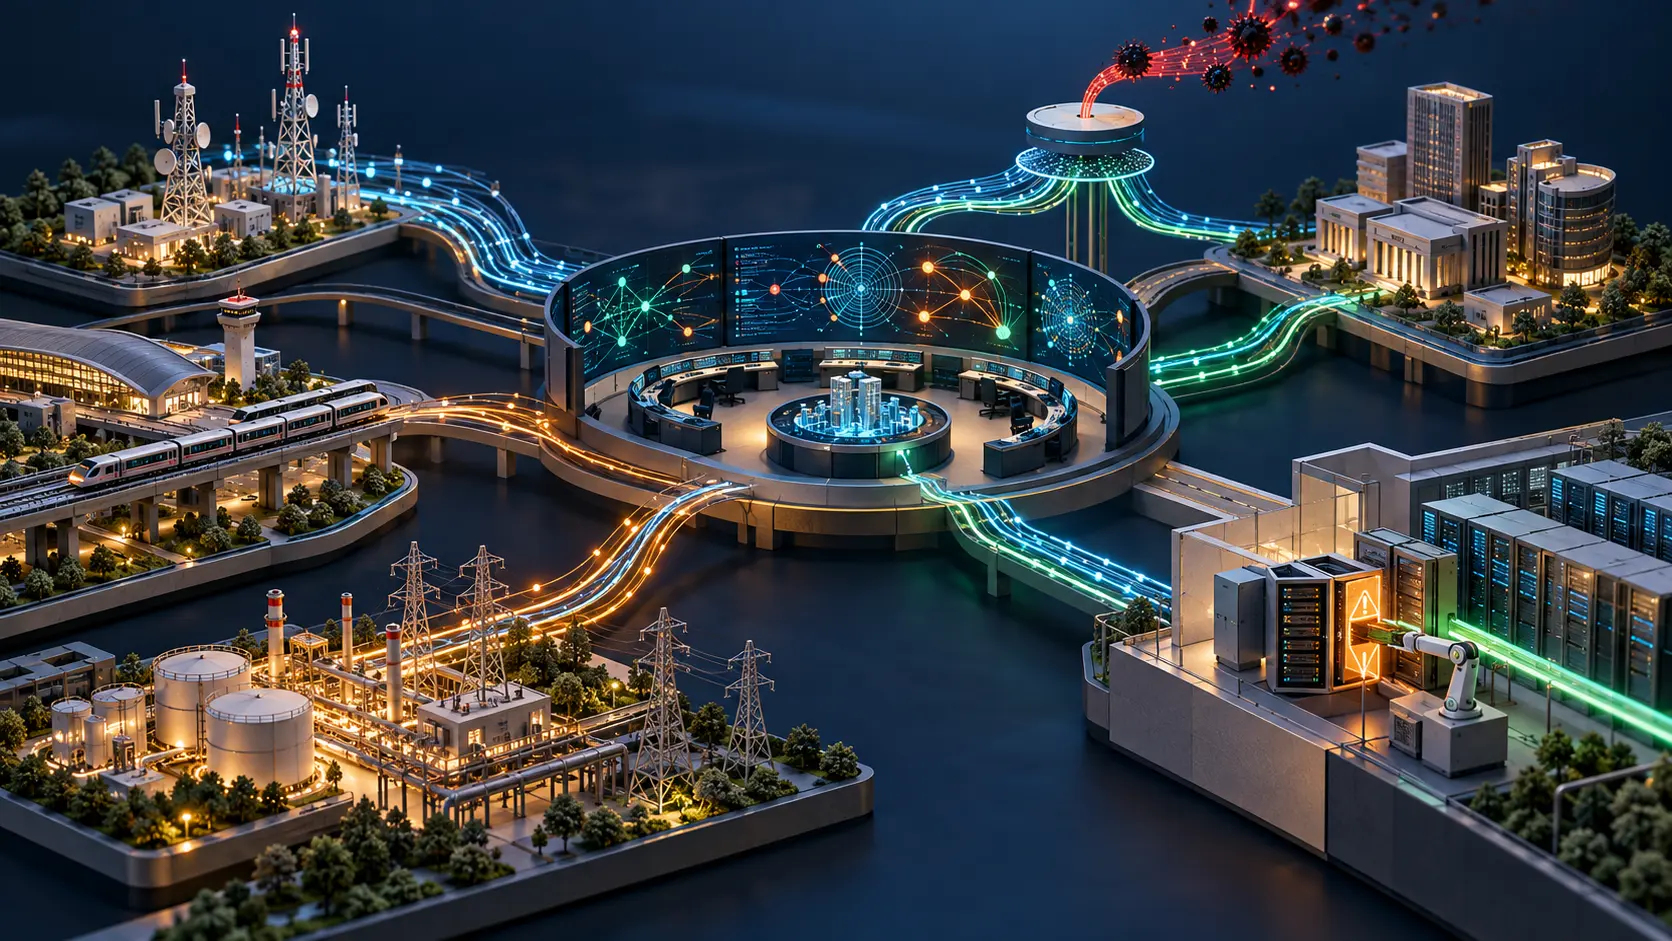
The National Cybersecurity Command Centre (NC3), run by the Cyber Security Agency of Singapore (CSA), is becoming the operations hub for a national cyber picture. Its announced upgrades span five jobs: combine threat intelligence, operate a Protective Domain Name Service (PDNS), map internet-facing critical systems, feed selected operators’ detection tools into the centre, and use AI-enabled systems to coordinate major incidents.
NC3 moves information from separate organisations into one operating view. A vulnerable asset can now surface at national level before its owner has chosen how to fix it.
Singapore’s telecom response shows why the distinction matters. In Operation CYBER GUARDIAN, the four major operators first detected activity linked to UNC3886 and notified CSA and the Infocomm Media Development Authority. Government agencies and the operators then worked together for more than eleven months. More than 100 defenders took part. CSA says the response closed access points, added remediation measures and expanded monitoring.
The first alarm came from the network owners. The government supplied scale, coordination and additional intelligence. NC3 is designed to make that collaboration routine: fuse information from government, CII owners, security companies and international partners; give CSA a view of exposed internet-facing systems; and help owners prioritise severe or actively exploited vulnerabilities.
The patch still lands on somebody’s production system. A central view can identify a vulnerable service and raise its priority. The owner schedules the change, tests the fix, manages supplier dependencies and keeps customers connected while the work happens. The warning becomes useful when the organisation that controls the system can act on it.
PDNS adds a second kind of control. Singapore plans to block access to known malicious domains before a connection reaches a user, using powers under the Online Criminal Harms Act. That moves defence upstream, ahead of each company’s local filtering. The Act also sets out reconsideration and review-tribunal appeal routes for access-blocking directions. At national scale, the speed of a block and the speed of correcting a bad block belong on the same operating dashboard.
The new centre will also integrate proprietary detection systems developed by the Centre for Strategic Infocomm Technologies with selected CII owners. AI-enabled tools are intended to track incidents, prepare operational assessments and help plan next actions. The control room can put more people and information around a decision; the owner still has to make the production change and carry its service risk.
CSA’s 13 October announcement describes the capabilities and says they will continue to develop. It gives no count of connected CII owners, no asset-coverage total and no target for the time between a vulnerability alert and verified closure. Those figures would show whether NC3 has become an operating system for national defence or a very impressive meeting place.
The next useful scorecard is plain: how many owners share telemetry; how quickly they acknowledge a severe exposure; how long remediation takes; whether service stayed available; and how quickly a PDNS block can be reviewed and corrected. Singapore has built the case for a common picture. The patch ledger will show whether the picture changes the network.
Sources
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance