
Summary
- The 2 November SR Policy YANG revision 09 replaces one generic forwarding count with input and output accounting points. Input octets exclude the encapsulation this policy later adds; output octets include it.
- Only the input side records the Binding-SID transit subset. The output side has aggregate packets and octets without that subset, so an output-minus-input byte delta cannot be labeled transit growth or delivered traffic.
The router did not acquire new customers between two counters. It wrapped packets. The July revision 08 offered a broad pkts and octets forwarding group. The November revision gives it two accounting points with different byte definitions. The difference matters whenever a dashboard puts the two numbers on one graph and calls the gap “traffic.” The IETF record shows an active SPRING working-group draft, so this is a proposed management schema rather than a report from an installed router.
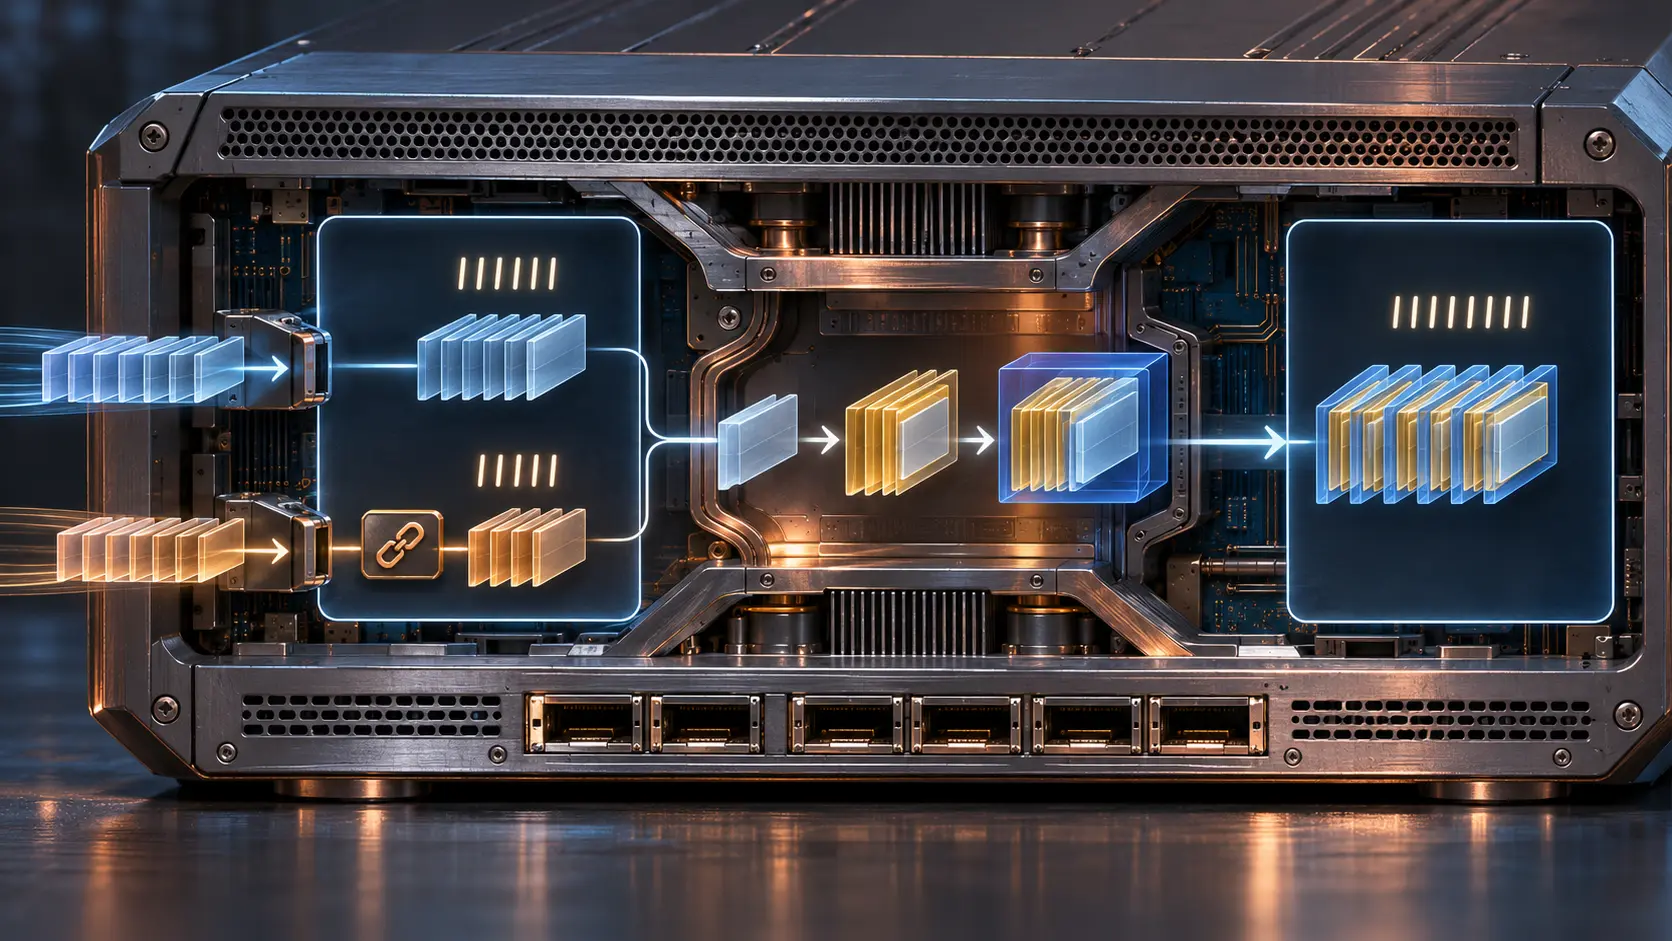
At the input point, immediately before the SR Policy applies its outgoing encapsulation, pkts and octets count all traffic. transit-pkts and transit-octets are the included subset steered into the policy by its Binding SID. Those input octets include the packet’s existing headers and payload, but leave out MPLS labels or outer IPv6 and Segment Routing Header bytes that this policy will add. At the output point, after encapsulation, aggregate octets include those new labels or headers. The output grouping has no transit-only columns: the draft says retaining the input steering classification there is not generally feasible.
SR Policy architecture RFC 9256 describes candidate paths and segment lists; revision 09 gives the management view a way to follow their operational identities. A forwarding-path entry has a headend-assigned path ID and a mandatory reference to its explicit or computed operational segment list within the same candidate path. NMDA RFC 8342 distinguishes intended configuration from operational state. Reading a configured segment list, a computed list and a forwarding-path counter as if they were one timeless object can hide a path switch as easily as a byte-definition change.
Output may be larger because the policy added header bytes; input transit counts cannot be carried over to a missing output transit series. The draft contains no named router trace matching both points, path identity and collection epoch. Such a trace would show the actual header cost and whether packet forwarding stayed on the selected path.
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance



