
Summary
- RIPE ABUSE is a control surface that routes reports and tests whether a published mailbox can receive and respond to validation messages. It is not a public incident-management log.
- The decisive handoff is from registry information to the resource holder or organisation responsible for handling the report. RIPE NCC can administer the registry and pursue contact validation, but the available evidence does not establish it as a general regulator of network activity.
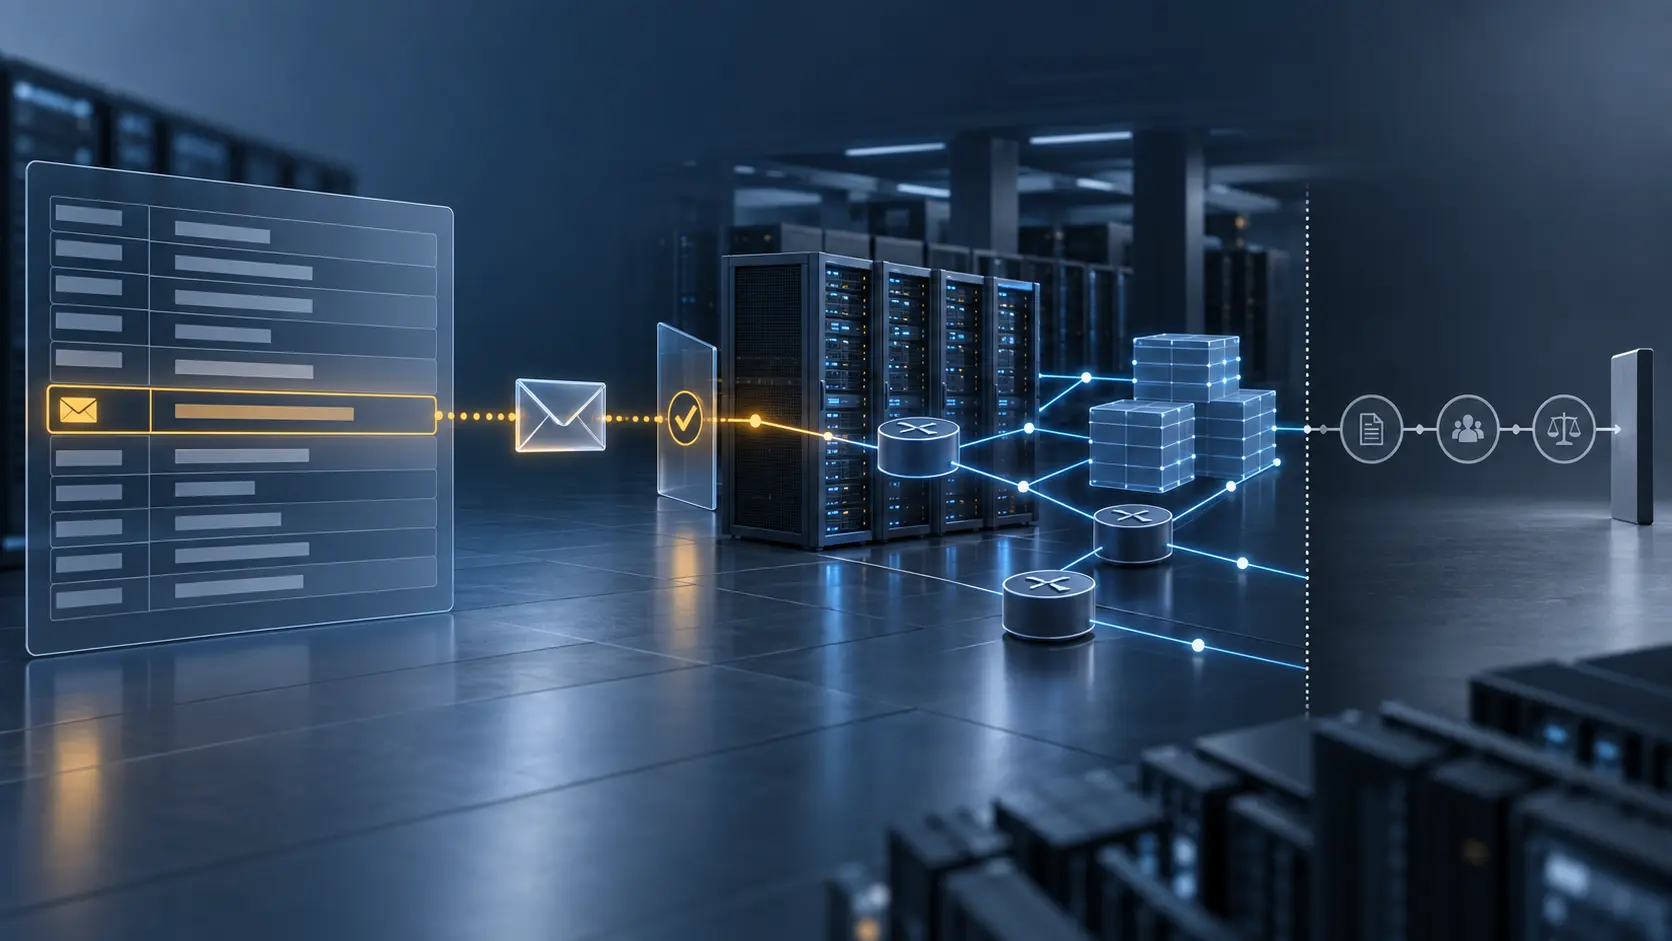
A network abuse report moves through several different systems, even when the sender sees only one email address. The first system is the registry: it publishes an abuse contact associated with an Internet number resource. The second is the mailbox: it must be reachable and able to respond to a validation message. The third is the operator’s internal process: someone must receive the complaint, assess it and decide whether a technical or administrative action is warranted. The fourth may be an escalation route outside the registry, depending on the conduct, the parties involved and the authority with jurisdiction.
The operational risk comes from treating those systems as interchangeable. A public contact can be present while a mailbox is unattended. A mailbox can pass a validation test while a specific report receives no meaningful response. A report can be handled while the underlying service remains active. A service can be interrupted without the public record showing why. The registry makes a route visible; it does not automatically expose the full control chain behind that route.
The starting point is the abuse-c attribute. RIPE-563 describes it as identifying the contact responsible for handling abuse reports associated with Internet number resources. The same framework places ordinary handling with the relevant resource holder or organisation, not with the registry as a substitute operator. https://www.ripe.net/publications/docs/ripe-563
That distinction matters for continuity. A report addressed through RIPE ABUSE is not a command sent through the routing system. It is a request entering an organisation’s abuse-handling process. The process may connect to network operations, hosting, security, legal or customer-support teams. Whether it produces a result depends on the organisation’s own authority, incentives, staffing and access to the systems involved. The public registry can identify the intended doorway without showing what happens inside the building.
The first control: making a route publishable
The registry requirement is about usable information. RIPE-767 sets requirements for maintaining accurate and usable registry information, including abuse-related contact information where applicable. That creates a baseline condition: a person or organisation seeking recourse should be able to identify where a report is meant to go. https://www.ripe.net/publications/docs/ripe-767
This is a real operational control, but it is narrower than a promise of remediation. A directory entry can be stale, misdirected or connected to an organisation that lacks the power to change the service generating the complaint. Even a correct address can only transmit the report. It does not decide whether the claim is credible, whether the conduct violates a contract or law, or which technical measure is proportionate.
For operators, the practical value is observability. A changing abuse contact can alter where external parties send urgent information. A missing or unusable contact can increase the time required to identify a responsible team. But the contact is a routing dependency, not evidence of the quality of the response. The difference is similar to the difference between a monitored port and a completed incident response: reachability reduces one failure mode, while resolution requires many more decisions.
The second control: testing the mailbox
RIPE NCC operates an abuse-c validation process. The published documentation describes testing whether an abuse mailbox can receive and respond to validation messages. https://www.ripe.net/manage-ips-and-asns/db/support/abuse-c-validation The associated procedure explains that RIPE NCC sends validation messages to contacts connected to Internet number resources and provides a process for follow-up when the contact cannot be validated. https://www.ripe.net/manage-ips-and-asns/db/support/abuse-c-validation/abuse-contact-validation
Mailbox validation answers a specific question: can the published route receive and respond to the registry’s test? That is more useful than a purely declarative contact field. It creates a measurable check on one part of the chain and gives the registry a basis for follow-up. Failure to complete validation can affect the status of the abuse contact in the RIPE Database, according to the available documentation.
But the test has a bounded meaning. It does not establish that the mailbox is continuously monitored. It does not establish that a report from a third party will be read by the same person who answered a validation message. It does not measure response quality, investigation speed or the technical effect of an operator’s action. Nor does it prove that a harmful service has stopped.
The distinction is important because validation is visible while case handling is usually private. An outside party may be able to observe that a contact exists, and the registry may record a validation state, but the public record generally does not reveal the internal ticket, evidence review, customer decision or network change associated with a particular complaint. Validation can therefore reduce uncertainty about reachability without eliminating uncertainty about accountability.
The handoff to the resource holder
The largest change in control occurs after the report is delivered. At that point, the relevant resource holder or organisation becomes the operational actor described by the abuse-contact framework. Its role may be direct or delegated, but the registry field itself does not perform the investigation. RIPE-563 describes the contact as responsible for handling reports associated with the resource while leaving operational handling with the relevant organisation. https://www.ripe.net/publications/docs/ripe-563
This creates a chain with different owners:
- The registry publishes the contact association.
- RIPE NCC tests and follows up on the registry contact’s validity.
- The resource holder or designated organisation receives and handles the report.
- Network, hosting or security personnel decide what operational measure to take.
- A regulator, court, law-enforcement body, provider or other authority may exercise a separate power when the case falls within its mandate.
The chain is not necessarily linear. A complainant may also use a hosting provider’s abuse process, a platform’s reporting system, a national authority or a court. The relevant remedy depends on what must be changed. If the problem is a broken contact, registry administration may matter. If the problem is malicious traffic, only the operator or an upstream provider may be able to change the service path. If the conduct is unlawful, an authority with investigative or judicial powers may be required.
This is why the phrase “RIPE ABUSE took action” needs precision. The available sources support claims about publishing requirements, validation and registry follow-up. They do not establish that RIPE NCC investigated a particular complaint, ordered a technical shutdown or guaranteed a durable correction. The actor with the ability to alter the service may be different from the actor able to validate the contact.
What registry escalation can and cannot show
Failure to complete abuse-contact validation can trigger follow-up actions and may affect the contact’s status. That gives RIPE NCC an administrative lever: it can challenge the reliability of the registry route and apply consequences within the registry process. https://www.ripe.net/manage-ips-and-asns/db/support/abuse-c-validation
The lever is meaningful because registry data supports coordination across networks. A degraded contact can make it harder for external operators, security teams and affected parties to reach the responsible organisation. A follow-up process can pressure the holder to maintain a usable contact. It can also signal that the public route should not be treated as verified indefinitely.
Yet an administrative consequence is not the same as a merits decision on the underlying abuse. The validation process tests the contact route. It does not, on the evidence available here, determine whether a complaint is true, whether a customer breached a policy, whether a server should be disconnected or whether damages occurred. Those questions belong to other operational or legal processes.
RIPE-706 places RIPE NCC in the administration of Internet number resources and the application of community-developed policies. The available material does not establish RIPE NCC as a general regulator of all network activity conducted using registered resources. https://www.ripe.net/publications/docs/ripe-706
That boundary is not a weakness in the registry record. It is the architecture of the system. A numbering registry needs mechanisms for identity, allocation, data quality and policy administration. It does not thereby acquire every power needed to investigate content, inspect customer systems, compel a technical remedy or adjudicate disputes. Confusing registration authority with operational enforcement can send complainants to the wrong institution and make operators accountable for powers they do not possess.
The evidence gap after delivery
For an external observer, the most consequential part of the chain is also the least visible. Public documentation can show what a contact field is intended to do, how validation works and what registry requirements apply. It cannot, by itself, show that a particular report was acknowledged, investigated, remediated or prevented from recurring.
That evidence gap should shape reporting and operational decisions. A researcher tracing an abuse report should record at least four separate states: publication, reachability, response and remediation. A validated contact supports the second state. It does not automatically support the third or fourth. A response email may support evidence of communication, but not necessarily the accuracy of the operator’s conclusion. A routing change or service shutdown may show an intervention, but not necessarily that the original cause was removed.
The same discipline applies to the resource holder. Maintaining an accurate abuse contact is a registry obligation where applicable, but it does not by itself establish that RIPE NCC must resolve the incident or compel a particular technical remedy. https://www.ripe.net/publications/docs/ripe-767 The holder may have contractual, regulatory or internal obligations beyond the registry framework, but those require their own evidence.
For network operators, this produces a practical checklist rather than a single compliance badge:
- Is the published contact assigned to a role that can receive the report?
- Does the mailbox accept and answer validation messages?
- Is there an internal queue that distinguishes urgent network abuse from routine correspondence?
- Can the organisation identify who has authority to change the affected service?
- Can it preserve a record of the decision without exposing sensitive complainant data?
- Is there an escalation route when the resource holder cannot act?
The public registry can answer only part of that checklist. It can help identify the route and, through validation, test part of its reachability. The remaining controls belong to the operator and to whatever authority has power over the underlying conduct.
A control surface, not a case ledger
RIPE ABUSE is therefore best understood as a control and accountability surface. It links a public resource record to a contact function, gives RIPE NCC a basis for validating that function and provides external parties with a starting point for recourse. Its value is greatest when each stage is interpreted accurately.
The contact is not the incident. Validation is not investigation. Registry follow-up is not a merits judgment. A resource holder’s role is not the same as RIPE NCC’s administrative role. And a public record of the route cannot substitute for evidence of what happened after delivery.
The next step after a report belongs to whoever can make the relevant decision. Sometimes that is the resource holder. Sometimes it is a hosting or transit provider. Sometimes it is a national authority or court. The registry can improve the odds that the report reaches the right doorway, but the available evidence does not show that the registry controls every room beyond it.
For continuity, that boundary is the central fact. A functioning abuse contact reduces one point of failure in the Internet’s inter-organisational response system. It does not remove the need for accountable operators, documented decisions and an authority capable of imposing the remedy when voluntary or contractual processes fail.
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance