
Primary Domain
Security
Within the Primary Domain facet, Security intelligence groups reporting by primary domain so readers can follow a focused area of internet infrastructure, governance, connectivity markets, or digital capital. The page brings together related articles, public evidence, institutions, companies, people, regional exposure, operating dependencies, and market context that may otherwise sit across separate category pages. It explains the domain, the likely actor class, the market or governance context, and the source material readers should use when comparing signals. Operators, analysts, and governance readers can see how the same domain appears across events, profiles, market shifts, public-source evidence, regional dependencies, and longer-cycle infrastructure decisions over time.

IETF
The ACME Key Rotated. Yesterday's DNS Authorization Still Works
The newest ACME DNS persistence draft turns routine key rotation into an accounting problem. A retired signing key may be unable to place another order while its public thumbprint still keeps an earlier DNS authorization usable.

IETF
Who Owns the Label After the Proof Verifies?
A Key Transparency proof can establish that a directory answered consistently and still leave an operator with the wrong question. The IETF’s latest review asks who is acting, who owns the binding and who must keep watching after access has changed.

History
When the Standard Outlives Its Authors: The Orphaned Stewardship of RFC 2350
Every network operator who has ever drafted a computer security incident response plan has, knowingly or not, touched the work of a working group that stopped existing nearly twenty-five years ago. RFC 2350 — 'Expectations for Computer Security Incident Response', published as…

CASE FILE
The Value Was the Same. The Reconstructed Bytes Were Not: Deterministic CBOR
The signer and verifier held the same decoded map, agreed on every field and still computed different signature inputs. Nothing in the value had changed. One encoder had merely exercised freedoms that the other had silently removed. The failure was not “CBOR versus cryptography.”…

CASE FILE
The Proof Was Unlinkable. The Envelope Was a Fingerprint: BBS Signatures
Two BBS proof values arrive at different verifiers. The bytes do not betray that they came from the same signature. Yet both presentations carry the same rare header, the same ten-slot credential shape, the same unusual disclosed indexes and a public key used for only twelve…

CASE FILE
The Registry Said `co`. The Handshake Had Said Nothing: RFC 9952
The same two bytes appear in an IANA row, a DNS service advertisement and an endpoint configuration. Yet the packet trace contains no ALPN extension. All three records may be accurate. None can be promoted into the missing wire event.
CASE FILE
The Primitive Kept Its Name. The Reuse Rule Changed: RFC 10032
Three adjacent functions accept an AEGIS key and nonce. One encrypts and authenticates, one emits a keystream after discarding authentication, and one creates a MAC under the only reuse exception in the document. The shared primitive name is technically accurate. Treating it as…

IETF
IDMEFv2 Makes 204 a Receipt—and Leaves the Retry Ledger to the Alliance
A security sensor submits an alert, the connection fails before the response arrives, and the manager may already have stored it. Revision 07 gives a 2xx reply unusually useful meaning. It does not tell a consortium how to classify the next POST.

CASE FILE
The Signature Verified. It Did Not Name the Approvers: RFC 9591
An auditor receives a valid Schnorr signature, the group public key and the exact message. The equation checks. The approval list is still missing. RFC 9591 makes that result possible by design: FROST compresses several signing shares into one ordinary-looking signature. The…
CASE FILE
The Capability List Said EdDSA. It Still Had Not Named the Curve: RFC 9864
An algorithm name can look like a complete answer while leaving the decisive parameter somewhere else. A service that advertises `EdDSA` has said less than many capability systems assume: it may support Ed25519, Ed448, or a locally constrained interpretation. RFC 9864 repairs…

CASE FILE
The Backup Restored the Key. It Also Restored Yesterday's State: RFC 9802
Two signing appliances wake from the same clean backup. Each holds the right private-key material. Each produces a signature that validates. Yet if both consume the same one-time index, the apparent recovery has broken the security assumption that made the signatures trustworthy.…

IETF
RFC 9787 and the Moment a Draft Becomes a Message: Encryption, Commitment and Cross-Device Custody
A protected email draft is not merely an early copy of a sent message. RFC 9787 treats it as a different authority state: unfinished text may need confidentiality from the mailbox service while remaining unreadable to intended recipients and unendorsed by the user's ordinary…
North America Cloud Services Trends
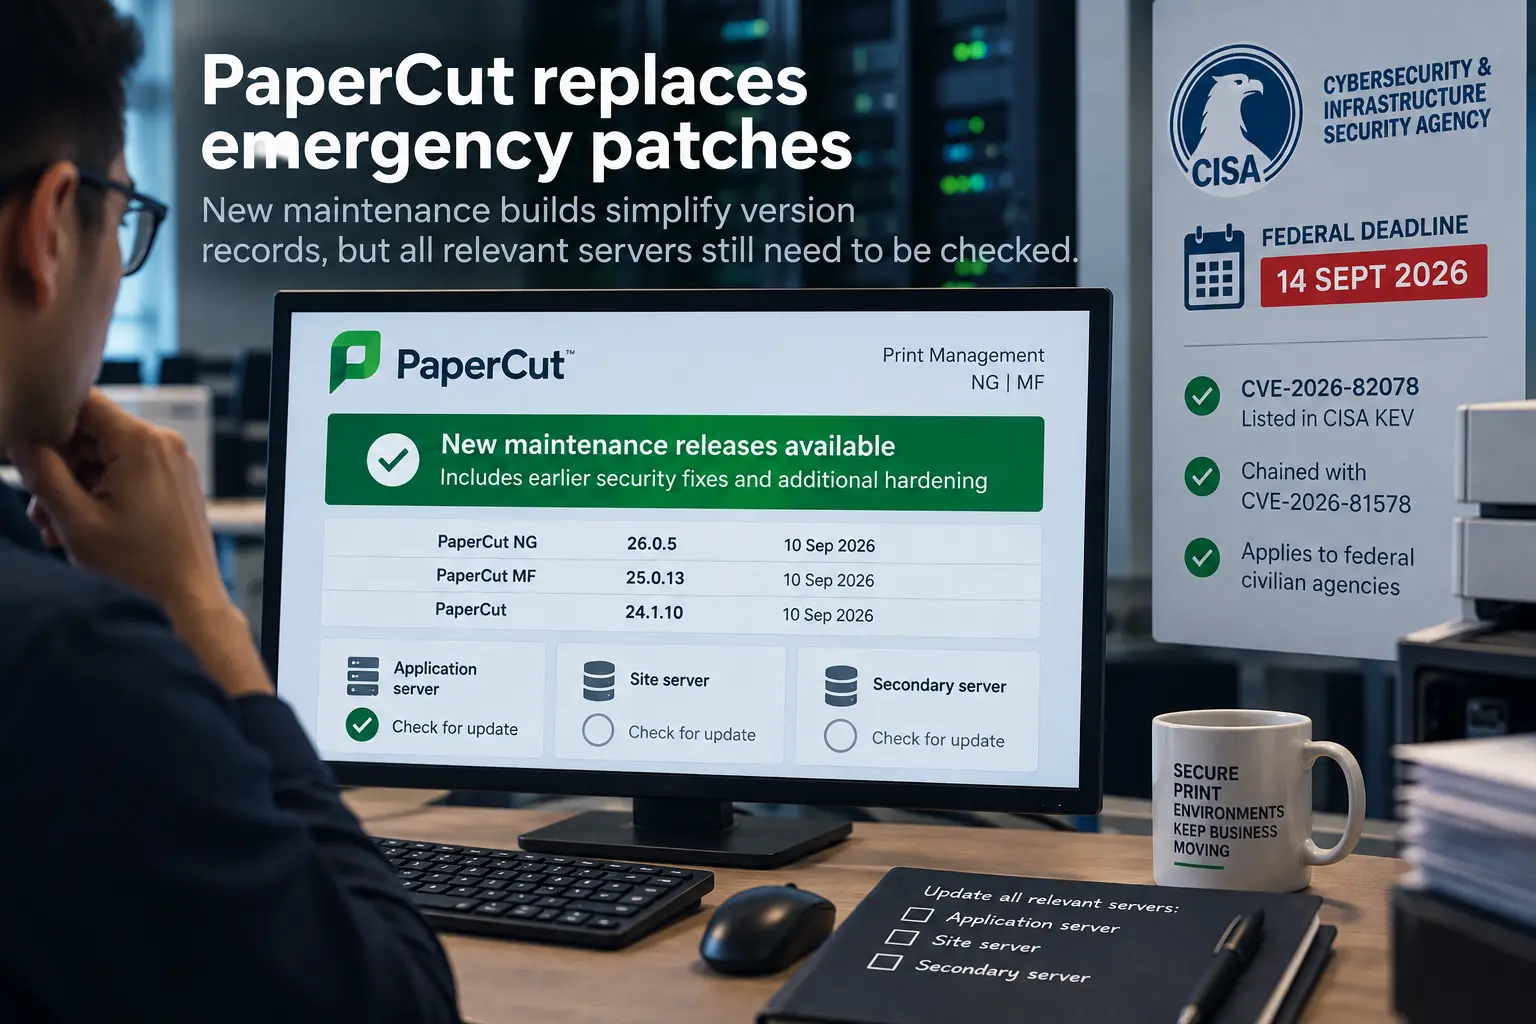
PaperCut replaces emergency patches as CISA deadline passes
PaperCut's new maintenance builds give administrators clearer version records, but site and secondary servers still need to be checked.

North America Cloud Services Trends
CISA deadline passes for exploited ScreenConnect flaw
ConnectWise says the flaw affects ScreenConnect clients, not servers, leaving providers to verify updates across the endpoints they support.

Europe and Middle East Institutional Trends
EU cyber reporting starts with 24-hour deadline
Manufacturers must notify authorities before an investigation is complete, then follow with fuller findings and remediation details as the technical picture develops.
IETF
The Message Had One Security Badge. Its Layers Did Not Share One Status: RFC 9787
The comforting part of an encrypted-mail interface is the badge. The difficult part is deciding exactly which bytes are entitled to it. RFC 9787 makes that boundary explicit: one received message gets one cryptographic summary, calculated only from the contiguous protection…

CASE FILE
The object survived five spellings. Which bytes were signed? RFC 9804
RFC 9804 gives SPKI S-expressions a precise route between readable notation, channel-safe transport, canonical octets and local memory. The route is reversible only when each transition is evidenced. A familiar-looking expression, a display hint or a successful parse cannot by…

Story
APNIC's Honeynet Logged 1.27 Million Events. That Is Not 1.27 Million Attacks
An APNIC 62 presentation turns one deliberately exposed server into a useful security instrument. Its headline, however, moves between attacks, attack events and events—three labels that cannot safely share one number.
IETF
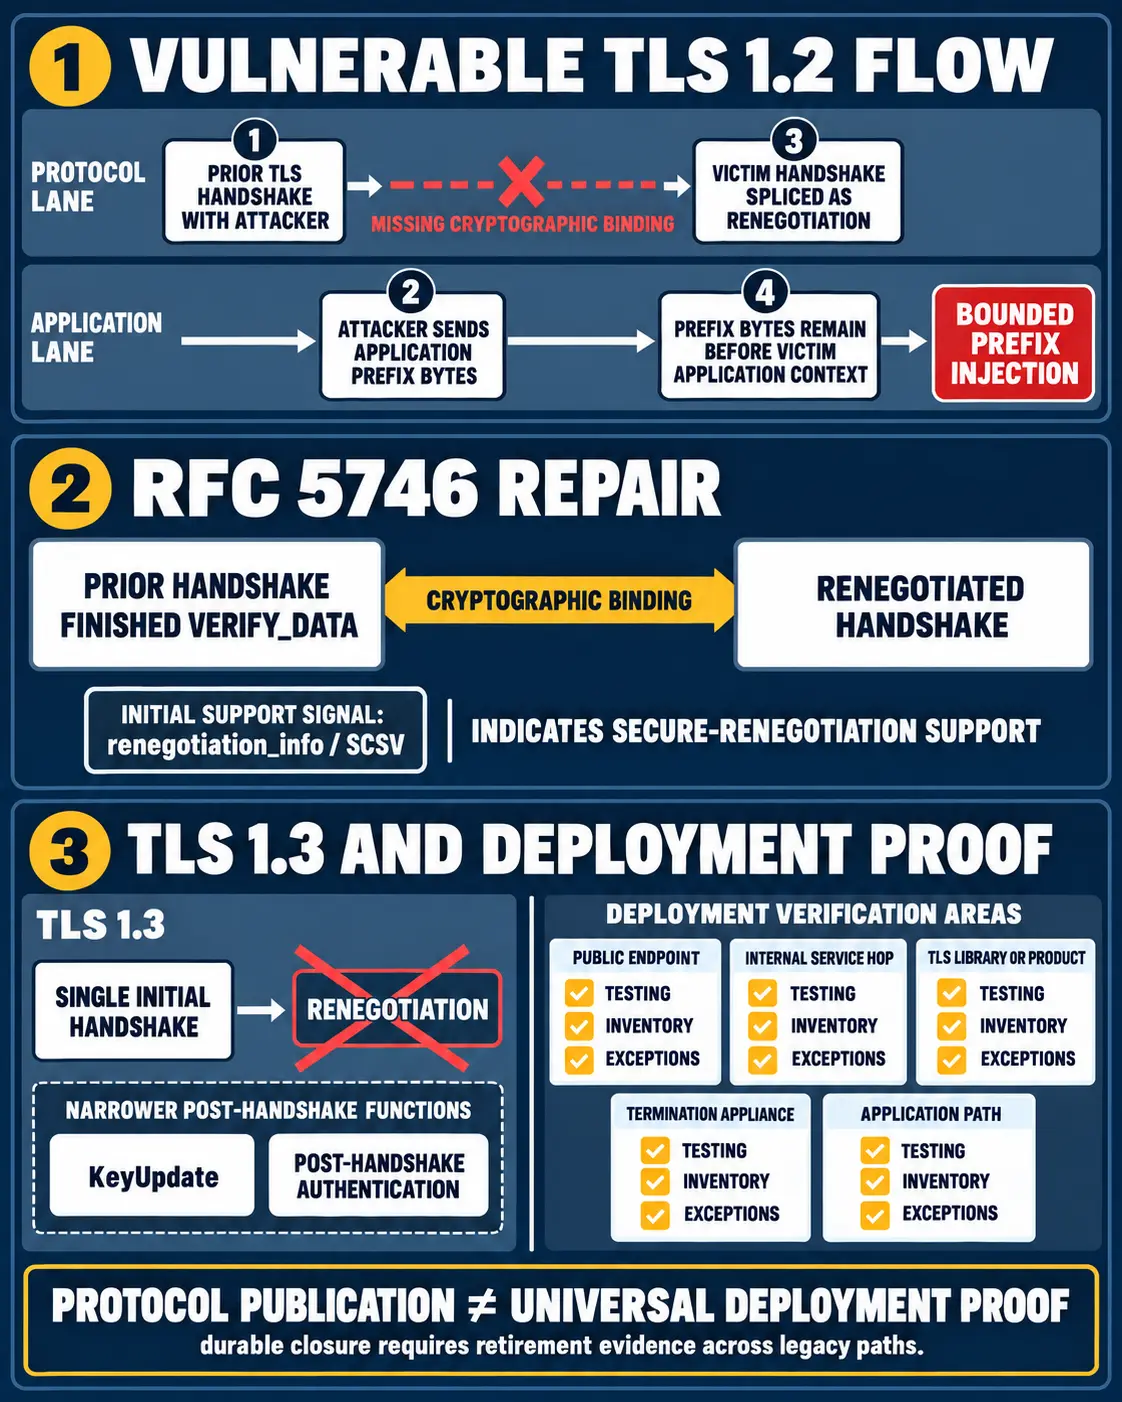
TLS Renegotiation Was Repaired. Deployment Closure Is a Separate Claim.
The IETF repaired a dangerous ambiguity in TLS renegotiation. That repair changed the protocol. It did not, by itself, prove that every older library, appliance, endpoint and application path had stopped accepting the unsafe behavior.

IETF
The Transform Was Agreed. The Replay Was Not Yet Rejected: RFC 9827
RFC 9827 gives IKEv2 a broader and more honest contract for packet sequence numbers. The selected Transform ID describes what should be true when an SA's packets enter the network; it does not certify sender coordination, receiver anti-replay policy, the packet stream that…