
Summary
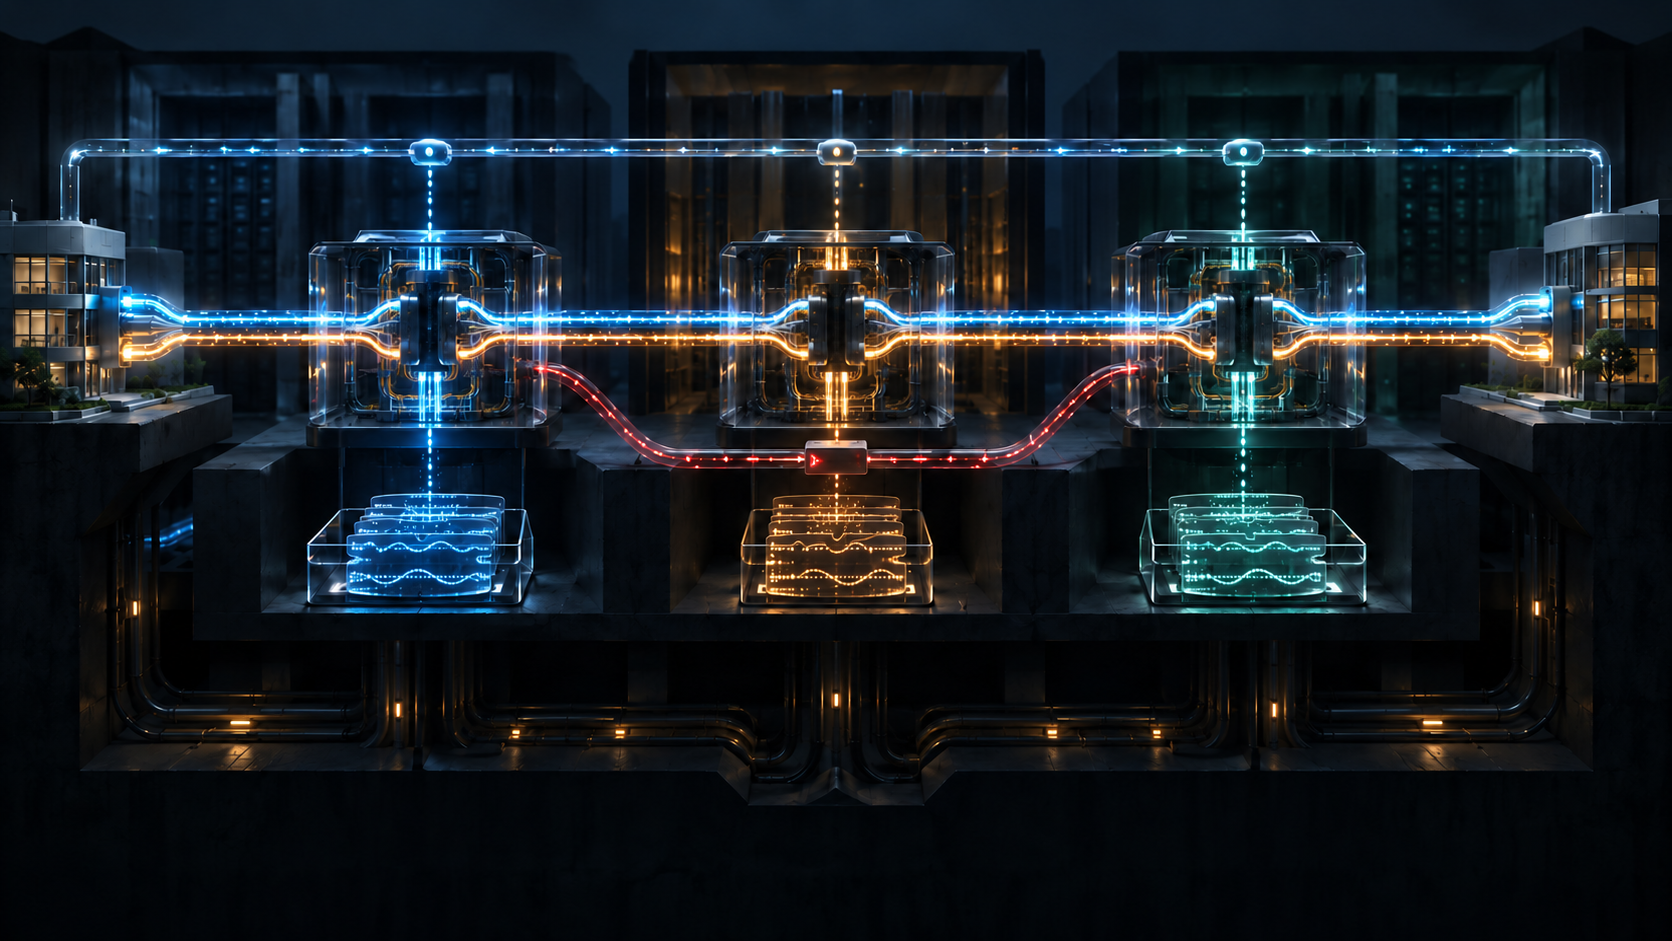
- A multi-segment pseudowire behaves as one point-to-point PW, but each S-PE terminates adjacent PSN tunnels and switches control and data planes between distinct segments.
- The service can therefore appear continuous while setup, label binding, OAM, congestion, protection, security and traffic receipts remain local to different edges and domains.
One service is a promise of composition
The customer does not buy a list of internal segments. Two attachment circuits should behave as though a single point-to-point wire joins them. RFC 5254 preserves that service model while allowing the provider path to cross several packet networks, tunnels, routing areas or administrative domains.
Its definition contains the tension. An MS-PW is two or more contiguous PW segments that behave and function as one point-to-point pseudowire. The first and last devices are terminating PEs. Between them, switching PEs join the segments. The word “one” describes the emulated service; it does not erase the devices and decisions that compose it.
At an S-PE, the preceding PSN tunnel ends and the succeeding tunnel begins. The S-PE switches the control plane and the data plane from one PW segment to the next. A path may contain several such boundaries. If the service crosses two providers, the boundaries also move evidence between organisations that may not share topology, management access or security policy.
The useful abstraction is therefore not a universal receipt. A customer-facing state can say that the pseudowire is available while leaving open which segments were established, which tunnels carry them, whether both directions were cross-connected, where a defect began and what traffic reached the far attachment circuit.
The PW route is not every tunnel route
RFC 5254 defines the PW route as the ordered set of S-PEs between the T-PEs. Each segment is in turn carried by a PSN tunnel, whose own route can be explicitly chosen or selected locally. The RFC deliberately places the routing of those tunnels outside the requirements it sets for the pseudowire.
That distinction prevents a common evidentiary collapse. Knowing the S-PE sequence does not reveal the physical or label-switched path inside every domain. Knowing that a tunnel is up does not prove the correct PW label was bound to it. Knowing the correct binding does not prove packets crossed the S-PE in both directions.
Setup can be static, signalled along an administratively predetermined route, or signalled along a dynamically selected route. A static label and a dynamic FEC are different kinds of receipt. The resulting service may look identical, but an investigation must know which control model created each segment and which system was authoritative for that decision.
RFC 5254 says a signalled MS-PW is successful only when all segments have been successfully established. This is a valuable transaction boundary. It still proves setup, not later forwarding. The state can become stale after a tunnel change, a cross-connect error, a queue failure or a protection event.
Admission occurs at every segment
Each S-PE maps a PW segment to a PSN tunnel. The mapping may follow signalled attributes or local policy, and admission control is performed for every segment. One edge can accept while another refuses. One domain can reserve resources while another uses a different representation or provisioning system.
The requirement for an all-segments setup result does not make those decisions identical. A durable record should preserve the request presented at each boundary, the label or identifier selected, the tunnel chosen, the policy version and the admission result. Without those intermediate receipts, an end-to-end “up” field is impossible to explain when the composition changes.
The two directions of a PW segment terminate on the same pair of PEs, but this does not make their operational state symmetric. Labels, queues, counters and defects can be directional. A control-plane cross-connect may exist while one forwarding direction is impaired. Evidence that normalises both directions into a single value hides the very asymmetry needed to diagnose the service.
OAM needs two distances at once
RFC 5254 requires multi-segment OAM to provide at least the capabilities available to single-segment pseudowires. It also calls for both segment and end-to-end mechanisms so a defect can be detected and localized. An OAM span may run from T-PE to T-PE, T-PE to S-PE or S-PE to S-PE.
Those scopes answer different questions. An end-to-end probe can show that the composed path failed, but may not identify the broken segment. A segment probe can localize a boundary without proving the complete customer path. Both are necessary precisely because one service is assembled from more than one execution surface.
Every PE must agree on a common OAM mechanism. An S-PE has to propagate tunnel defects to affected pseudowires, preserve the direction of notifications and pass T-PE-to-T-PE OAM transparently. It should also behave as a segment endpoint. Passing an end-to-end message and originating a local observation are separate roles and should leave separate records.
Static segments do not escape this requirement. Where adjacent S-PEs have no signalling peering, in-band OAM still needs to relay PW or attachment-circuit defects. Configuration is an instruction; OAM is an observation. Neither is evidence that customer traffic achieved its intended result.
Protection changes the path, not the question
Protection may cover one PW segment, several contiguous segments or the entire end-to-end path. A failure detector can trigger a switchover, but a switchover command is not proof that the backup admitted the service, installed both directions or carried traffic.
Later specifications make the difference more concrete. RFC 7771 addresses S-PE protection for static MS-PWs, and RFC 8104 addresses fast protection at pseudowire endpoints. Their existence reinforces the evidence ladder: failure observation, protection selection, state installation and recovered forwarding are distinct transitions.
An incident system that closes a ticket when it sees “protection activated” skips the most important receipt. The organisation needs to observe the post-switch path and measure the service after the transition. Otherwise a successful control action can mask an unsuccessful recovery.
Quality does not cross domains by assertion
Each domain may use different tunnel technologies and class-of-service representations. RFC 5254 therefore requires mappings at administrative boundaries and expects the PEs to bind segments to tunnels with suitable attributes. A continuous service label does not guarantee that delay, loss or priority semantics survived every translation.
Congestion is similarly local before it is end to end. Every domain must implement congestion control, and an MS-PW must not cross an unprovisioned best-effort path without another adequate scheme. RFC 6073 later states that each segment handles congestion independently, even though sharing congestion information could improve end-to-end mitigation.
A provider can therefore hold a valid setup receipt and still lack a service-performance receipt. Performance OAM for delay, jitter and loss is required because topology and admission do not measure experience. A defect notification is not a latency measurement; a clean connectivity check is not an SLA result.
Domain crossing expands the security ledger
At an inter-provider boundary, a label received from a neighbour is accepted under local rules. That local admissibility does not prove end-to-end authenticity. A transit domain or failed S-PE may inject, redirect, mirror or hijack PDUs. RFC 5254 allows mechanisms for end-to-end PDU authenticity because segment setup alone does not close that risk.
The management view is also divided. Remote management across domains should be possible, but may be disabled for security. Missing visibility from one console does not mean missing state; a populated console does not prove the data path. Audit design must tolerate protected local evidence while retaining correlation identifiers and time bounds that allow the end-to-end service to be reconstructed.
The right record begins with the attachment circuits and intended T-PE endpoints. It names the chosen setup model and S-PE sequence. For every segment it retains labels, tunnel binding, policy generation, admission, directional cross-connect, CoS mapping, protection state and segment OAM. It then joins those facts to end-to-end OAM, performance measurements, forwarded traffic and customer outcome.
Lu Heng's reality-layer discipline turns the architecture into a leadership rule. A composed service is real, but its unity belongs to the service layer. Segment acceptance, switching state, defect propagation and observed delivery remain different realities with different custodians. The abstraction stays trustworthy only when it can be reversed into the receipts that made it true.
Sources
- RFC 5254: Requirements for Multi-Segment PWE3
- RFC Editor record for RFC 5254
- IETF Datatracker record for RFC 5254
- RFC 3985: PWE3 Architecture
- RFC 3916: Requirements for PWE3
- RFC 4447: Pseudowire Setup and Maintenance Using LDP
- RFC 5085: PWE3 VCCV
- RFC 5885: BFD for PWE3 VCCV
- RFC 5659: Multi-Segment PWE3 Architecture
- RFC 6073: Segmented Pseudowire
- RFC 6478: Pseudowire Status for Static Pseudowires
- RFC 7267: Dynamic Placement of Multi-Segment Pseudowires
- RFC 7771: S-PE Protection for Static MS-PWs
- RFC 8104: Pseudowire Endpoint Fast Failure Protection
- Lu Heng: Running-Code Primacy
- Lu Heng: On Reality Layers
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance