
Summary
- Revision 02 of Additional Authentication Method Reference Values proposes an
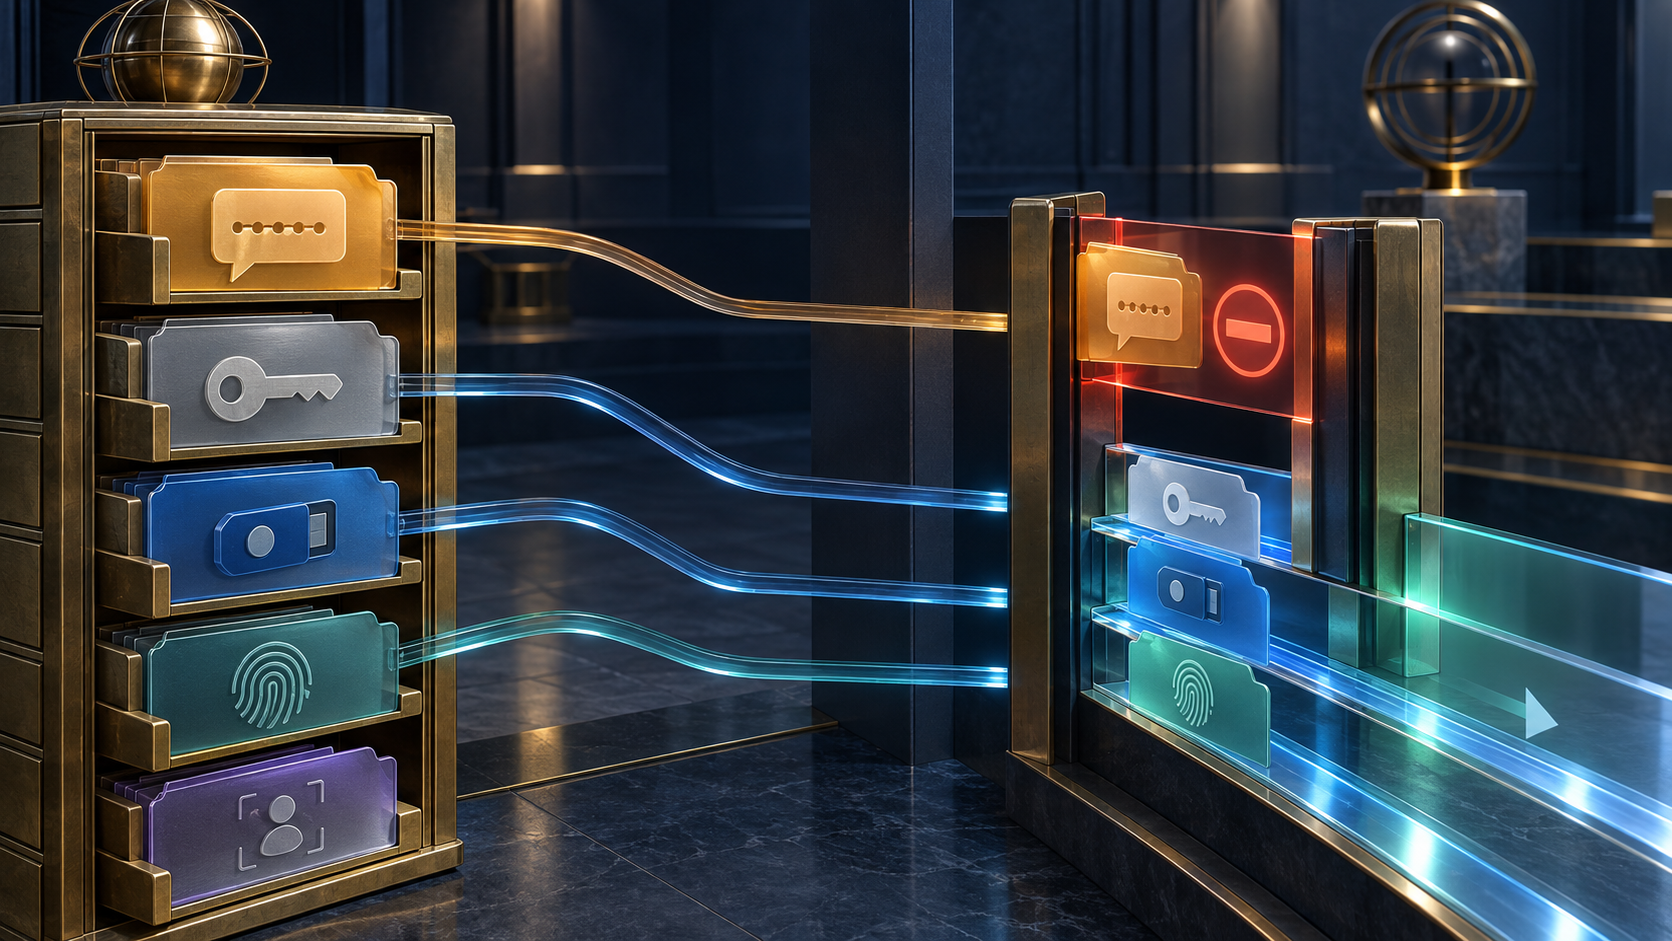
sqavalue for security-question answers and, in the same definition, warns that current NIST guidance does not consider security questions acceptable authentication secrets. - That is not a contradiction to hide. It exposes the correct boundary: a registry can name a method that exists without certifying its security, authorising its use or assigning it an assurance level.
A registry has to describe reality even when policy should reject part of that reality. draft-skyfire-oauth-amr-values-02, posted on 2 October 2026, makes this unusually visible. Its proposed sqa value would let an issuer report that security-question answers participated in authentication. The draft immediately cautions that current NIST guidance does not accept those questions as authentication secrets.
The proposal adds several other method references: application confirmation, behavioural signals, email, one-time codes, URL interaction, push approval, facial liveness and passkeys. Revision 02 renamed an earlier psk proposal to passkey to avoid confusion with pre-shared keys, removed a proposed call value and instead updates the description of the existing tel value. These are vocabulary-maintenance decisions, not security verdicts.
The distinction is already embedded in the architecture. OpenID Connect separates amr, which records methods used, from acr, which identifies an authentication context class. RFC 8176 standardises short method identifiers and even shows pwd and kba together in an example. The active IANA registry still contains kba. None of that says knowledge-based authentication is suitable for a present-day high-consequence transaction.
NIST's current model draws the policy line more sharply. It says knowledge-based authentication questions do not constitute an acceptable secret for digital authentication under its guidelines. Its authenticator requirements also prohibit prompting subscribers to use knowledge-based questions when choosing passwords. Registry history and current security policy therefore occupy different layers: one preserves a name; the other determines whether an organisation may rely on the named method.
The proposed bg value needs similar discipline. It can cover silent network phone-number authentication, device recognition, geolocation and other background signals. NIST treats fraud indicators such as geolocation as useful risk inputs, but says they do not change the authentication assurance level and cannot substitute for an authentication factor. A receiver must not convert “background method observed” into “strong authentication achieved.”
Nor does a signed token solve the semantic problem. JWT validation can establish issuer, audience, integrity and time constraints when implemented correctly. RFC 8725 explains why receivers still need explicit algorithm, issuer and audience policy. Cryptography authenticates the assertion that a method was reported; it does not make the method acceptable.
The IANA process is deliberately narrower. The active AMR registry uses Expert Review to allocate stable, non-colliding names. At capture time, the proposed revision-02 values were not yet active entries, and the Datatracker record was an individual Internet-Draft with no stream or standards level. Even if a value is later registered, registration will settle spelling and reference, not deployment policy.
An operator therefore needs two records. The first is the interoperable observation: which method identifier the issuer asserted, under which issuer, token and vocabulary version. The second is the local decision receipt: whether that method was allowed, restricted, accepted only in combination, or forbidden for this account, action, jurisdiction and risk tier; which policy version decided; and what exception or remediation applied.
Heng Lu's Minimum Initial Specification supports precisely that split: standardise the smallest common symbol, then leave future decisions local. Running-Code Primacy asks what mechanism actually executed rather than what label appeared. Reality Layers prevents a registry allocation, issuer assertion, assurance class, risk signal and relying-party authorisation from collapsing into a single green status.
The useful message of sqa is not that security questions have been rehabilitated. It is that systems may still need a precise name for a method they intend to detect, restrict, migrate or eliminate. A registry should be able to tell the truth about what exists. Security leadership must still decide what is allowed to count.
Sources
- https://datatracker.ietf.org/api/v1/doc/document/draft-skyfire-oauth-amr-values/
- https://datatracker.ietf.org/doc/draft-skyfire-oauth-amr-values/
- https://datatracker.ietf.org/doc/draft-skyfire-oauth-amr-values/history/
- https://datatracker.ietf.org/wg/oauth/about/
- https://heng.lu/minimum-initial-specification-localized-future-decision-voluntary-adoption-internet-coordination-system/
- https://heng.lu/on-reality-layers-symbolic-power-and-why-clarity-feels-so-hostile/
- https://heng.lu/running-code-primary-the-patch-needed-to-preserve-the-internet-original-design/
- https://openid.net/specs/openid-connect-core-1_0.html
- https://pages.nist.gov/800-63-4/sp800-63/model/
- https://pages.nist.gov/800-63-4/sp800-63b/aal/
- https://pages.nist.gov/800-63-4/sp800-63b/authenticators/
- https://www.iana.org/assignments/authentication-method-reference-values/authentication-method-reference-values.xhtml
- https://www.ietf.org/archive/id/draft-skyfire-oauth-amr-values-00.txt
- https://www.ietf.org/archive/id/draft-skyfire-oauth-amr-values-01.txt
- https://www.ietf.org/archive/id/draft-skyfire-oauth-amr-values-02.html
- https://www.ietf.org/archive/id/draft-skyfire-oauth-amr-values-02.txt
- https://www.ietf.org/archive/id/draft-skyfire-oauth-amr-values-02.xml
- https://www.rfc-editor.org/rfc/rfc7519.html
- https://www.rfc-editor.org/rfc/rfc8176.html
- https://www.rfc-editor.org/rfc/rfc8725.html
- https://csrc.nist.gov/pubs/sp/800/63/4/final
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance