
Summary
draft-ietf-mpls-stamp-pw-21says rate limiting on the control-plane punt path is indistinguishable from actual network loss to STAMP and can therefore be reported as packet loss.- A loss alarm should preserve the test session, encapsulation, both endpoint limiters, both directions, ECMP and MTU conditions, reverse-context lookup and independent data-plane evidence before it authorises a fault verdict or traffic change.
A red number with two possible histories
The dashboard does not look uncertain. It says that a pseudowire lost seven per cent of its test packets. A threshold changes colour. A ticket is created. The next automation is ready to move traffic or page a supplier.
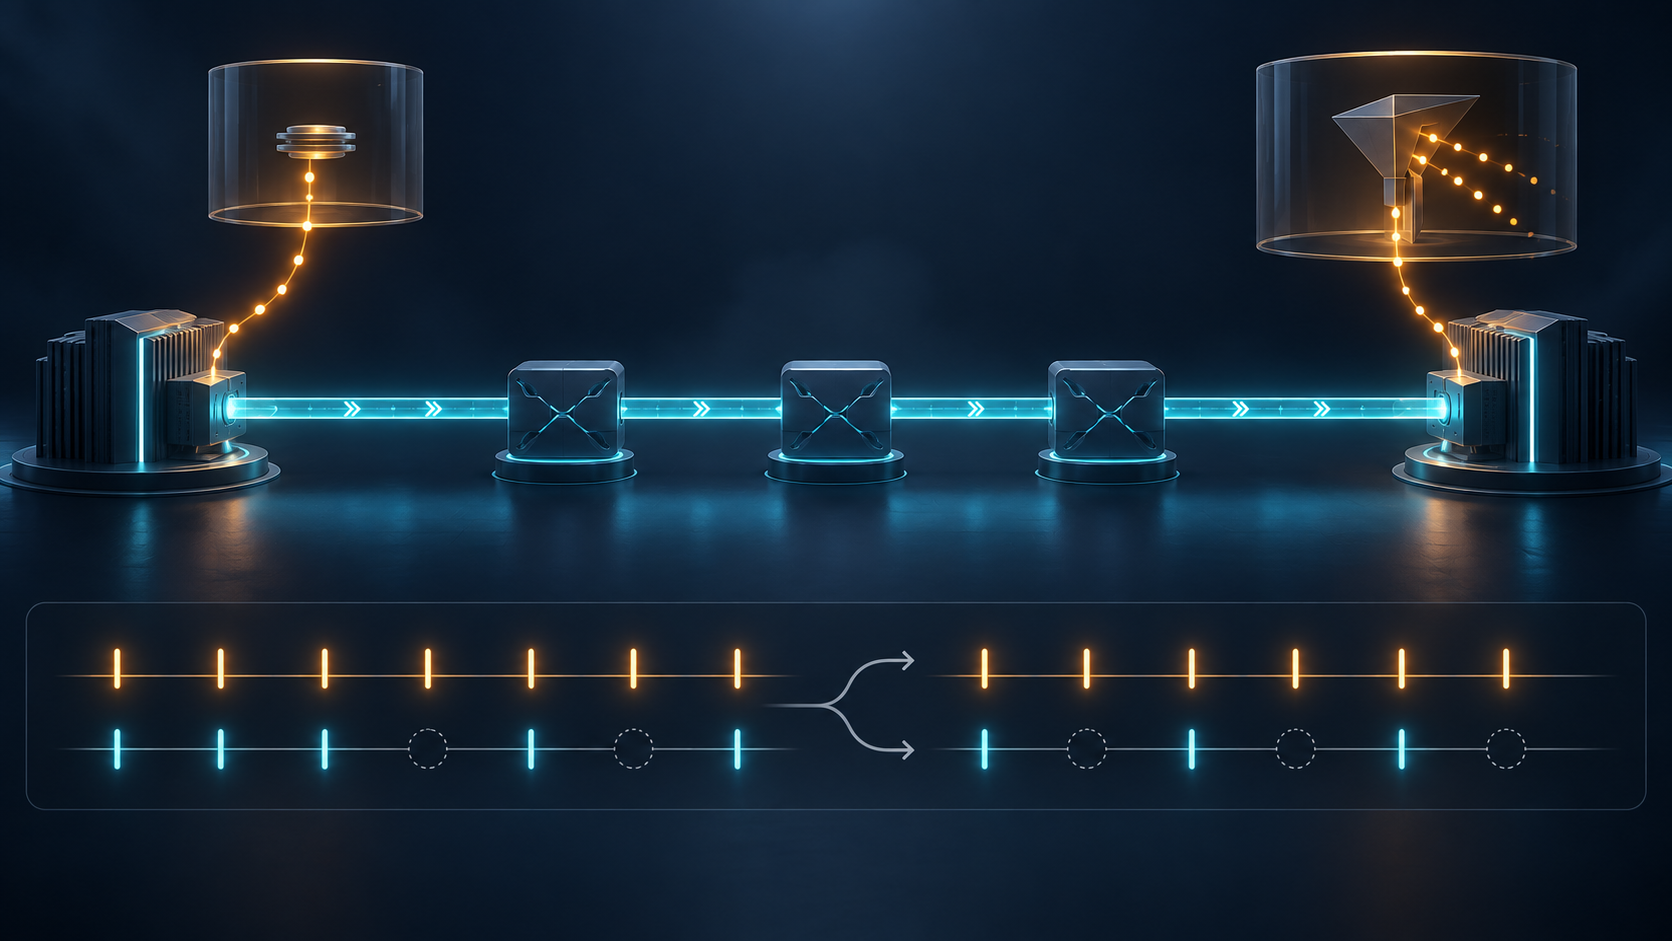
One history fits the screen: the network dropped the probes on the path. Another also fits it. The probes crossed the MPLS path, reached the provider-edge endpoint and were sent upward for exception processing. The node’s control-plane limiter, doing the protective job it was configured to do, discarded some of them before STAMP could return a reply. From the sender’s point of view both histories end with the same missing packet.
That is not a theoretical criticism imposed from outside the standard. Revision 21 of draft-ietf-mpls-stamp-pw says it directly. Every test packet processed at a Session-Sender or Session-Reflector consumes control-plane CPU and memory. Rate limiting is therefore required as protection against denial of service and excessive load. The same paragraph says that policing on this punt path is indistinguishable from actual loss in the network and can be reported as packet loss.
The sentence changes the authority of the metric. STAMP can establish that an expected test response did not complete the measurement cycle. It cannot, from that absence alone, decide where the packet disappeared or whether the customer data flow suffered the same fate.
The draft is advanced, but it is still a draft
The current text is revision 21, dated 10 September 2026. The IESG approved it on 14 September and sent it to the RFC Editor queue the following day. Its history records continuing editorial and IANA work. It is intended to become a Proposed Standard and, if published, to update RFC 8762 and RFC 8972. It is not yet an RFC.
Its scope is also bounded. The document covers point-to-point label-switched paths and point-to-point single-segment pseudowires inside one administrative domain. Point-to-multipoint cases and multi-segment pseudowires remain outside it. No sentence in the draft proves that a named network deploys the mechanism or that a particular alarm has been misclassified.
Those limits matter because the article is about a protocol property, not an incident. The property is already important enough that standards review forced it into explicit operational text. The revision history shows an Area Director asking that the interaction between punt-path policing and loss measurement be stated clearly: when the control-channel method sends every probe to the control plane at both ends, policing can look like network loss and be reported as such. Revision 21 addressed the comment.
Review did not create the ambiguity. It stopped the specification from hiding it.
A test packet is deliberately not ordinary traffic
STAMP measures by sending a test packet from a Session-Sender to a Session-Reflector and receiving a reflected packet. Timestamps can support one-way and round-trip delay, delay variation and loss calculations. RFC 8762 supplies the base protocol; RFC 8972 supplies optional extensions and a session identifier.
MPLS complicates the exercise because the probe must resemble the traffic whose path it claims to measure while still being intercepted at the correct endpoint. The draft defines two forms. Format 1 carries an IP/UDP header. Format 2 omits IP/UDP and uses new Generic Associated Channel types to distinguish sender and reflector packets. Both carry a non-zero STAMP Session Identifier. Without the ordinary IP/UDP tuple, Format 2 combines that identifier with the received LSP or pseudowire context and locally provisioned session parameters.
The packet follows the label stack toward the provider edge. It is then excepted from ordinary forwarding and delivered to control-plane processing. A TTL value, a control word or a Generic Associated Channel Label may participate in that termination mechanism. Exactly one exception method is provisioned for a session.
This design is necessary. It is also why the probe and the service packet have different fates at the last step. The service packet is forwarded. The test packet is deliberately removed from the forwarding path and given to a protected processor. That processor has its own queue, CPU budget and limiter. A measurement intended to describe the data plane therefore ends inside a second resource domain.
Protection and measurement share the same symptom
Removing the limiter would not solve the problem. An endpoint that reflects every offered test packet without constraint could expose its control plane and reverse path to accidental overload or deliberate attack. The draft correctly keeps throttling and message protection.
The operational task is to make the limiter visible to the measurement verdict. Revision 21 says operators should know when limiting was applied—for example through the UDP ports used by Format 1 or the LSP/PW context and channel type used by Format 2—so that alerting can correlate policing with failure notifications. It also says incoming throttling should not be more stringent than the bandwidth allocated to the test traffic, because otherwise the limiter itself can manufacture invalid results.
RFC 5085 supplies older VCCV guidance for the same control-channel boundary. The draft applies its recommendation that ICMP and MPLS LSP Ping traffic stay below five per cent of the associated pseudowire bit rate to STAMP as well. That percentage is a protection rule, not a certificate of measurement validity. A correctly configured aggregate limiter can still affect an individual session when several tests, attacks or other control messages share the same resource.
The useful alarm is therefore not “the path lost seven per cent.” It is “seven per cent of expected STAMP cycles did not complete during this interval; endpoint limiter counters, path evidence and service observations are attached.” The first sentence assigns cause. The second preserves evidence.
The reverse direction has its own authority
A reflected packet is not a receipt generated outside the network. It must find a reverse-direction LSP or pseudowire context and traverse it. For a G-ACh test, the reflector uses the received packet’s PW label or ultimate LSP label to identify that context. If it cannot find the reverse context, it must discard the received test packet and must not send a reply.
The sender sees silence. Again, silence is not one fact.
Capacity is also directional. The reflector can generate a return rate comparable to the forward test rate. The draft requires the reverse direction to be provisioned independently and to account for cases in which it has less capacity. A forward path may be healthy while the reply path, reverse punt path or reflector context fails. A round-trip result combines those domains unless the operator retains enough information to separate them.
This is where a single loss percentage becomes institutionally convenient and operationally dangerous. A supplier responsible for the forward path may be blamed for a reverse endpoint condition. An automation may reroute the service even though only the measurement return path was constrained. A second test may then consume more control-plane capacity and deepen the apparent failure.
Same label stack is an aim, not a universal proof
The draft carefully tries to align test and data forwarding. The probe uses the same label stack, can include the service label, and accounts for control words and entropy labels. Yet path fidelity remains conditional.
Format 1 carries IP addresses that can differ from those of the actual data flow. On equipment that applies IP-based ECMP, those addresses may select a different path. A GAL should not affect ECMP on conforming equipment, but the draft warns that non-conforming equipment can use it in a way that sends the probe elsewhere. Where that risk exists, a control-channel type that adds no label is preferable.
Packet size creates another boundary. G-ACh, GAL, IP/UDP and optional padding add overhead. The complete probe must fit the LSP or pseudowire MTU independently in both directions. An oversized G-ACh probe is dropped instead of fragmented and can appear as packet loss. That event is real, but it describes the probe’s envelope; smaller service traffic may continue.
A broken LSP produces the opposite danger. A Format 1 packet with routable addresses may be forwarded by MPLS or IP over another path and still reach a reflector. The test can then report success for a path it did not traverse. Non-routable addresses and domain-edge filtering reduce parts of this risk, but reflected traffic and same-domain routing leave residual cases. Format 2 avoids IP forwarding, yet incorrect MPLS forwarding can still produce an invalid measurement.
The lesson is not that active measurement lies. It is that its claim must carry the conditions under which the probe represented the service.
Authentication protects a packet, not its interpretation
STAMP supports integrity protection, and the MPLS draft carries that protection into the headerless Format 2 because the calculation covers the STAMP packet itself. This helps prevent a forged packet from being accepted as a valid member of a session.
It does not prove path fidelity. It does not prove that a missing packet was dropped in transit. It does not make a limiter counter appear in the STAMP loss value. It does not turn an authenticated return into evidence that the corresponding customer flow used the same ECMP member.
The security section is explicit about attacks on interpretation. An injected reflected packet can corrupt delay and loss results. An injected sender packet can consume return and punt-path capacity. A party able to suppress probes can make a healthy LSP or pseudowire look failed. Integrity, rate limiting and path validation are different controls because they answer different questions.
The receipt a loss alarm should carry
A defensible operational record should join at least twelve items without pretending they are one event:
- the exact draft or RFC revision and the test semantics in use;
- the Session Identifier, sender and reflector, and locally provisioned session parameters;
- the LSP or pseudowire context and the direction under test;
- Format 1 or Format 2, IP version and ports where present, channel type, control word, GAL or TTL mechanism, label stack and packet size;
- the configured test rate and allocated bandwidth for each direction;
- the sender and reflector punt-path limiter policy, counters and timestamps;
- packets sent, received and reflected, plus the relevant T1–T4 timestamps;
- reverse-context lookup success or discard evidence;
- MTU and encapsulation-overhead checks in both directions;
- the ECMP and entropy assumptions, including evidence of non-conforming treatment;
- independent data-plane counters or other observations covering the same interval; and
- the alert, confidence, causal classification, operator decision, follow-up test and clearance evidence.
This record lets a monitor say something useful before it knows the cause: probe-path loss was observed. It lets an operator ask which boundary failed. It lets leadership decide when the evidence is sufficient for a customer statement, supplier escalation, traffic move or control-plane change.
The hierarchy matters. A missing return is evidence of an incomplete measurement cycle. Correlated limiter activity is evidence of a plausible local cause. Independent service loss is evidence that customer traffic was affected. A traffic move is an authorised intervention. Restored probes and restored service are separate recovery receipts.
Running code deserves to decide what happened, but only when the record preserves which code path ran.
Sources
- Current MPLS STAMP draft
- Draft history and review record
- Revision 21 plain text
- RFC 8762 — STAMP
- RFC 8972 — STAMP optional extensions
- RFC 5085 — Pseudowire VCCV
- RFC 7708 — GAL as a VCCV channel
- RFC 7325 — MPLS forwarding requirements
- RFC 6790 — MPLS entropy labels
- RFC 8085 — UDP usage guidelines
- Running-Code Primacy
- The Stability Fallacy
- On Authority, Belief, and the Internet’s Addressing System
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance