
Summary
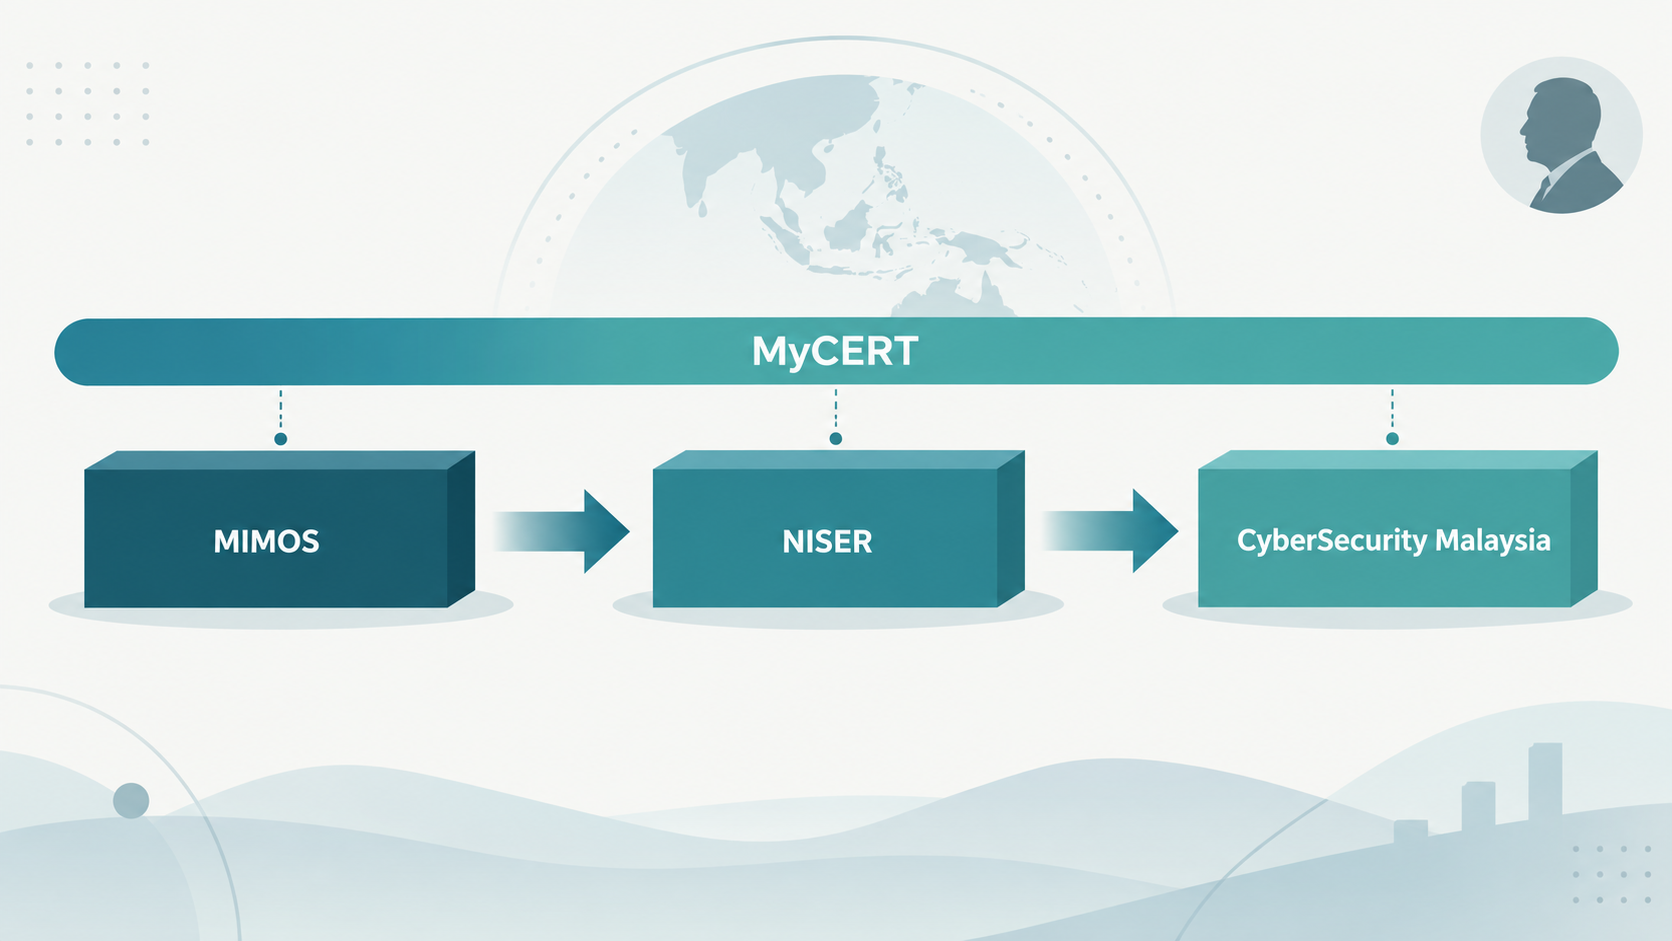
- MyCERT’s documented history shows an incident-response function established in 1997, placed within NISER when NISER was formed inside MIMOS in 2001, recognized by FIRST with membership dated 13 May 2003, and carried into the later CyberSecurity Malaysia structure.
- The record supports a bounded contribution by Dr. Mohamed Awang Lah to the security initiatives associated with MyCERT, but does not establish that he alone founded, staffed, controlled or personally handed over the function.
The useful question is what survived
The public history of Malaysia’s early internet infrastructure often places its most visible technical leaders at the centre of every later outcome. That framing is understandable: people make choices, assemble teams and translate technical possibilities into institutions. But it can also collapse several different kinds of power into one biography.
For MyCERT, the more precise question is not whether Mohamed Awang Lah mattered. It is what, if anything, remained operationally legible after the work associated with his earlier roles had become part of a larger institutional system.
The available record points to continuity of a function rather than continuity of one person’s authority. CyberSecurity Malaysia’s institutional history describes MyCERT as a function formed in 1997, subsequently placed under the National ICT Security and Emergency Response Centre, or NISER, when NISER was established within MIMOS in 2001. The same history describes NISER’s later separation from MIMOS and its rebranding or officialization as CyberSecurity Malaysia on 20 August 2007. The institutional chronology is set out by CyberSecurity Malaysia.
That sequence matters because each step changes the institutional container while preserving a recognizable national incident-response capability. It is evidence of organizational persistence. It is not, by itself, evidence that Awang Lah personally directed the 2001 placement, the later separation from MIMOS or the 2007 reconstitution.
A function established before the later brand
MyCERT’s own account presents it as Malaysia’s national computer emergency response team operating within the CyberSecurity Malaysia structure. The institutional identity therefore predates the name under which many readers now encounter it. MyCERT’s official description places the team within that later institutional framework.
This distinction prevents a common historical error: treating the current organization as if it had appeared fully formed at the moment CyberSecurity Malaysia received its later public identity. The record instead describes an older incident-response function moving through successive administrative arrangements.
The 1997 origin date and the 2001 NISER placement are not interchangeable claims. The first concerns the emergence of MyCERT as a function. The second concerns an institutional change in which NISER was created inside MIMOS and MyCERT was placed under that structure. The difference is important for accountability. A founding date does not identify every person who staffed the function, and an administrative placement does not identify the individual who authorized it.
The evidence also does not supply a named personnel handover. It shows institutional placement and later continuity, but not a documented chain in which a specific successor received the function directly from Awang Lah. That absence should narrow the claim, not erase the institutional evidence.
Recognition beyond the originating institution
An externally maintained team record provides a separate marker of continuity. FIRST identifies MyCERT as a member team and dates its membership to 13 May 2003. FIRST’s team directory records the membership date and team identity.
The date does not prove that MyCERT was founded in 2003. Nor does membership prove who controlled its internal operations. Its value is different: it shows that the incident-response function was recognized as an organizational team during the period in which MyCERT was associated with the NISER-era institutional transition.
That is a meaningful distinction between personal reputation and institutional capability. A person may be celebrated for helping create a function, but an external team registry records that the function had acquired an identity that could participate in an international professional network. The record therefore supports a modest but consequential inference: by 2003, MyCERT was not merely an idea attributed to an individual; it was an institutionally legible team.
APCERT’s regional member records likewise place MyCERT within the Asia-Pacific incident-response community and associate it with the Malaysian cybersecurity institutional structure. APCERT’s member information provides regional context for MyCERT’s organizational identity. That present-facing evidence cannot establish the precise date of the earlier MIMOS-to-NISER placement, but it reinforces the point that MyCERT’s continuity is observable through team and institutional records rather than only through a founder narrative.
An ITU country profile offers another external description of Malaysia’s cybersecurity institutions and the national incident-response role associated with MyCERT. The ITU profile provides external country-level context. Such a summary should not be used to manufacture a date it does not state, but it helps distinguish the team’s national function from any one individual’s biography.
Where Awang Lah belongs in the story
The most defensible personal attribution is bounded. A profile published by MY.NeuTrans associates Dr. Mohamed Awang Lah with network-security initiatives during his MIMOS tenure that resulted in the formation of MyCERT. That account is relevant because it connects him to the work surrounding the function’s emergence. It is also subject-affiliated, so it cannot independently establish sole authorship, personal ownership or continuing control.
The Internet Hall of Fame profile supplies a separate biographical record of Awang Lah’s contribution to Malaysia’s early networking and internet development. The profile documents his broader role in the country’s early internet history. It should not be stretched into a specific claim about MyCERT unless the relevant wording is explicit. Recognition for broad networking leadership is not proof that he personally founded, staffed or later governed every institution associated with that history.
This is where the article’s person-centred focus becomes useful. Awang Lah’s role can be treated as a question of observable responsibility: which initiatives were associated with him, during which institutional period, and with what evidence? The answer may support credit for helping shape security capacity. It does not support converting an institutional chronology into a sole-actor story.
The distinction is especially important because institutional continuity often depends on work that is difficult to personalize: operating procedures, team membership, reporting relationships, technical routines, funding arrangements and administrative mandates. The reviewed records show the function’s movement through institutional structures. They do not reveal a complete personnel map or prove that one individual transferred the capability in a formal handover.
Continuity without a named handover
The strongest mechanism visible in the record is structural rather than biographical. MyCERT was established, placed within a new departmental structure, recognized by an external professional organization and later carried through a separation and reconstitution of the host institution. That sequence is enough to demonstrate continuity of an organizational function across institutional change.
It is not enough to answer every question about how the capability was preserved. We do not have, in this record, a named successor, a dated transition memorandum, a staffing list covering each phase or a contemporaneous operating manual showing which practices were transferred. Those missing artifacts limit what can fairly be said about personal legacy.
A careful account therefore separates three propositions:
- MyCERT existed as an incident-response function before the later CyberSecurity Malaysia identity.
- The function was placed within NISER in 2001, recognized by FIRST in 2003 and carried through the later institutional transition described by CyberSecurity Malaysia.
- Dr. Mohamed Awang Lah is associated by a subject-affiliated account with security initiatives resulting in MyCERT, but the available records do not establish sole control or a named handover.
The first two are institutional claims. The third is a bounded attribution claim. Combining them into “Awang Lah controlled MyCERT across every transition” would exceed the evidence.
What the record changes about leadership history
This narrower reading does not diminish Awang Lah’s importance. It makes the attribution more durable. A person-centred history is strongest when it identifies the boundary between a leader’s demonstrated contribution and the institutional processes that outlasted the role.
For Malaysia’s early internet infrastructure, that boundary is visible in MyCERT’s chronology. The function survived because it became attached to organizations, professional recognition and public mandates. Those mechanisms are different from personal authority. They can preserve capability after leadership changes, but they also make it impossible to attribute every later result to the person most closely associated with the beginning.
The practical lesson extends beyond this one history. When a cybersecurity function moves through reorganizations, researchers should look for records of placement, external membership, successor teams and operating mandates before assigning personal credit. A title or retrospective profile may identify a meaningful contributor. It cannot substitute for evidence of who made each governance decision, who staffed the team or who controlled the function after a transition.
MyCERT’s documented continuity is therefore neither a founder myth nor an impersonal administrative footnote. It is a record of a capability becoming institutional. Mohamed Awang Lah belongs in that story as a bounded contributor to the security initiatives associated with its emergence. The public evidence does not show that the institution—and everything it later did—remained his personal project.
The unresolved part
The next evidentiary step would be a contemporaneous record identifying the people, procedures or formal decisions that carried MyCERT from one institutional setting to the next. That could include appointment records, transition documents, team rosters, operational reports or testimony from named successors and collaborators.
Until such records are located, the most accurate conclusion is also the most specific one: MyCERT’s institutional continuity is documented more clearly than any personal handover. That is not a weakness in the history. It is the boundary that keeps a consequential technical leader from being credited with powers the record does not assign.
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance