
Summary
- A successful
COMPRESSreply activated bidirectional compression immediately after the206line ended and provided no in-session command for turning it off. - After application compression began, later
STARTTLS,AUTHINFOandMODE READERtransitions were barred; using TLS, account authentication and compression together required that exact order. - Compression ran before SASL and TLS protection, so dictionary scope, observable lengths, flushing and corrupt-stream failure became security and operational decisions rather than mere bandwidth settings.
The last clear line
The server writes 206 Compression active and terminates the reply with CRLF. Those are the last uncompressed response bytes. The very next octet belongs to a different connection grammar: commands and replies in both directions now pass through the selected compressor.
That boundary in RFC 8054 is unusually exact because ambiguity would destroy the stream. If one endpoint begins DEFLATE one byte early, or the other one byte late, neither sees valid NNTP lines. The client therefore may not pipeline COMPRESS; it must receive the verdict before sending anything else.
Failure leaves the old connection grammar intact. A malformed algorithm name, an unsupported algorithm and a resource failure have distinct rejection paths. Success is different. It changes the shared state immediately and for the rest of that connection.
Compression was a layer, not a special reply
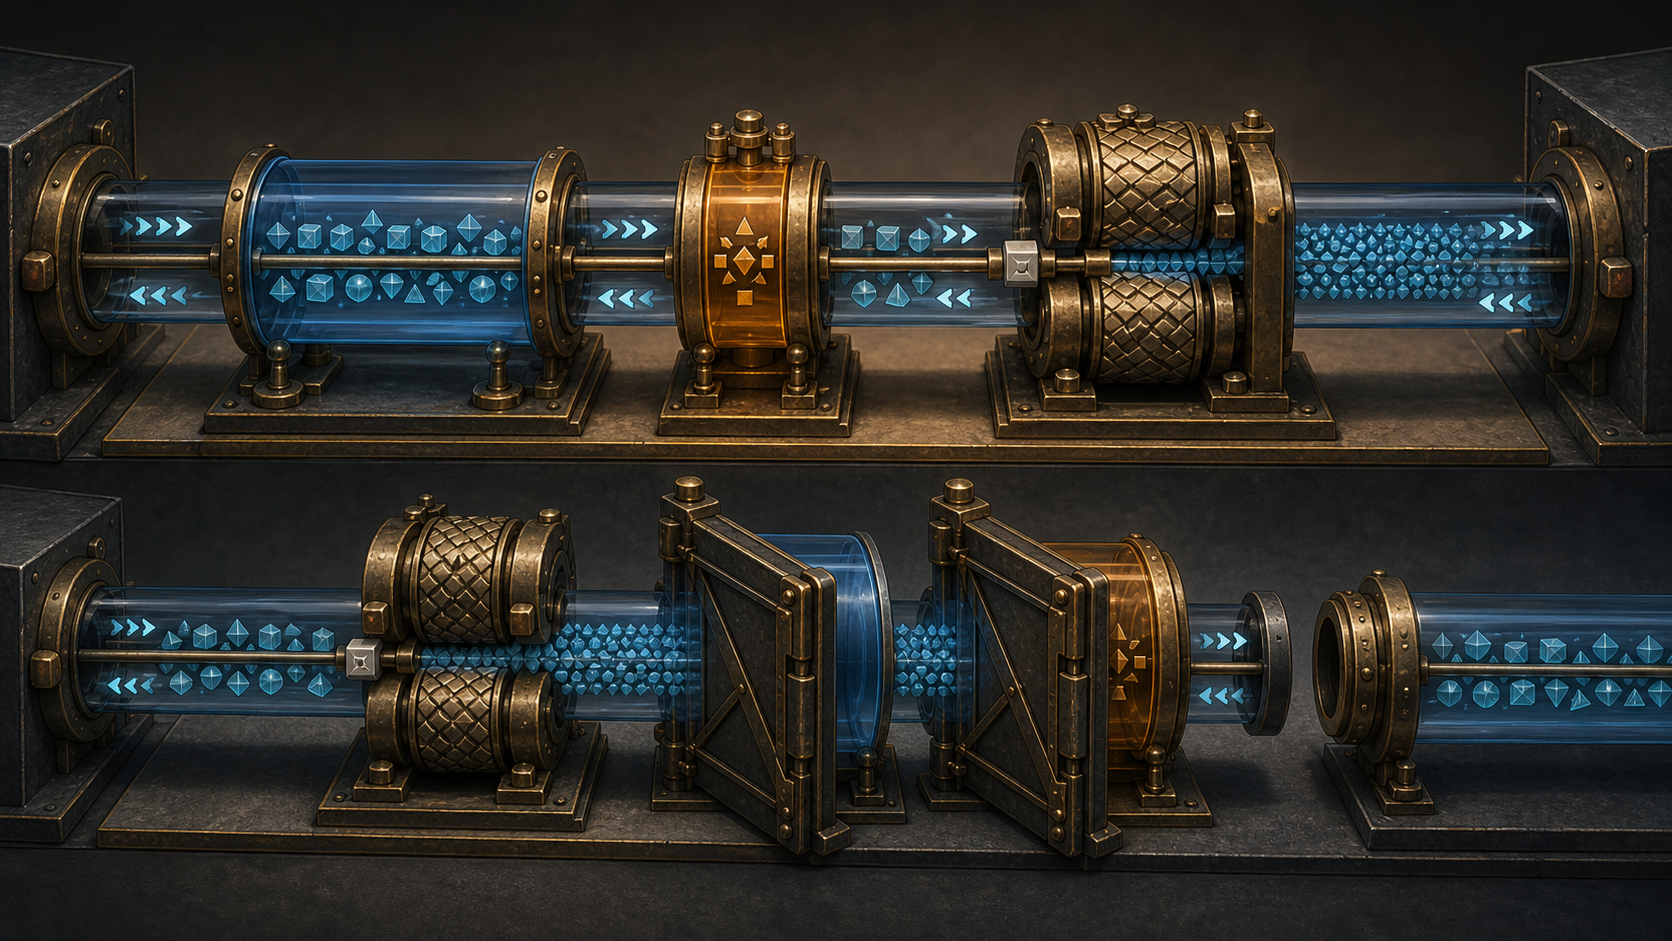
Earlier, unstandardized mechanisms compressed selected server responses. That saved bytes in one direction and required each command to acquire its own compressed variant. RFC 8054 instead placed one lossless layer beneath every later NNTP command and response.
The change covered both directions. Repeated client commands could benefit alongside large server lists, article headers and text bodies. The informative measurements in the RFC found some multi-line responses highly compressible, while short replies and encoded attachments often saved much less. Those examples describe workloads studied by the specification, not a current deployment benchmark.
DEFLATE, defined in RFC 1951, was the sole standardized algorithm and mandatory implementation for the extension. Each sender could choose its own reasonable compression level; the opposite decompressor had to adapt. Symmetry applied to the existence of the layer, not to tuning decisions.
The shortcut that removed later choices
A running compressor carries history. RFC 8054 therefore treated its activation as a one-way connection transition. Once compression was active, the server stopped advertising COMPRESS and STARTTLS. A later valid command for either received 502. MODE READER was also unavailable after the transition.
There was no UNCOMPRESS. A client wanting plain NNTP again had to use QUIT and create a new connection. That rule prevented the two endpoints from disagreeing about whether their next bytes were raw protocol or compressed stream state.
Current capabilities mattered more than remembered capabilities. RFC 3977 allows a capability list to change during one session. RFC 8054 specifically forbids relying on a cached COMPRESS result from an earlier connection because compression can weaken encryption. Yesterday's advertisement could not authorize today's transition.
A password could not follow the compressor
Compression reduces length by exploiting similarity. Encryption can hide content but still reveal the length of the compressed result. If an attacker can influence some plaintext and observe changing ciphertext lengths, shared patterns may disclose information. RFC 8054 cites CRIME and BREACH as examples of that risk class.
Credentials were the clearest avoidable secret. After a successful application-level COMPRESS, an unauthenticated client was forbidden to attempt AUTHINFO. The server could omit the capability or show it without usable arguments, and a syntactically valid authentication command received 502.
The command order followed from this boundary. A client that wanted all three properties first used NNTP STARTTLS as defined in RFC 4642, then authenticated with the mechanism in RFC 4643, and only then requested application compression. Choosing bandwidth first sacrificed the ability to add those protections later on the same connection.
This did not make the three operations equivalent. TLS protected a transport link. AUTHINFO established the account identity accepted by the server. COMPRESS changed representation. None inherited the authority of another merely because the protocol required an order among them.
The bytes met the layers in reverse on arrival
RFC 8054 specified composition explicitly. Before transmission, NNTP data passed through application compression first, then any SASL security layer, then TLS. A receiver reversed the sequence: TLS processing, SASL processing and finally decompression returned the NNTP bytes.
Compression must precede encryption to find repetition. That same placement exposes why dictionary scope matters. Public material and confidential articles should not share compression history beneath an active security layer. The RFC also prefers avoiding a shared dictionary between distinct confidential articles where practical; clearing the DEFLATE dictionary is one possible mitigation.
The standard does not declare every compressed encrypted session unsafe. It refuses to hide the trade-off. Implementations should not automatically enable compression under a security layer unless the user has knowingly chosen it.
Shared state made corruption terminal
Every byte submitted for compression had to reach the output and be flushed enough for the peer to decompress it completely. A sender could change compression level around data that would not benefit, but the receiver still depended on one continuous valid stream.
If either side received invalid or corrupted compressed data, it immediately closed the connection. There was no attempt to search forward for the next NNTP command. Once the decompressor's history ceased to match the compressor's history, a plausible line boundary could not restore the missing state.
This failure rule resembles the negotiation rule. Both protect a single shared fact: what transformation governs the next byte. Reconnection creates a clean fact. Guessing inside the old stream does not.
Order became a security property
The IANA NNTP Parameters registry records the COMPRESS capability and DEFLATE algorithm. Registration gives implementations common names and references; it does not certify that a server supports them or uses them safely.
NNTP compression succeeded as a general layer because it stopped multiplying command variants. The cost was a more consequential state machine. 206 did not merely promise smaller traffic. It committed both endpoints to a remembered transformation, removed later transitions and made confidential ordering visible in operational policy.
The lesson sits in the sequence rather than the algorithm. Encrypt, authenticate, then compress if the risk is accepted. A performance layer could come last because, once it began remembering the conversation, some earlier security choices were no longer safe to make.
Sources
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance