
Summary
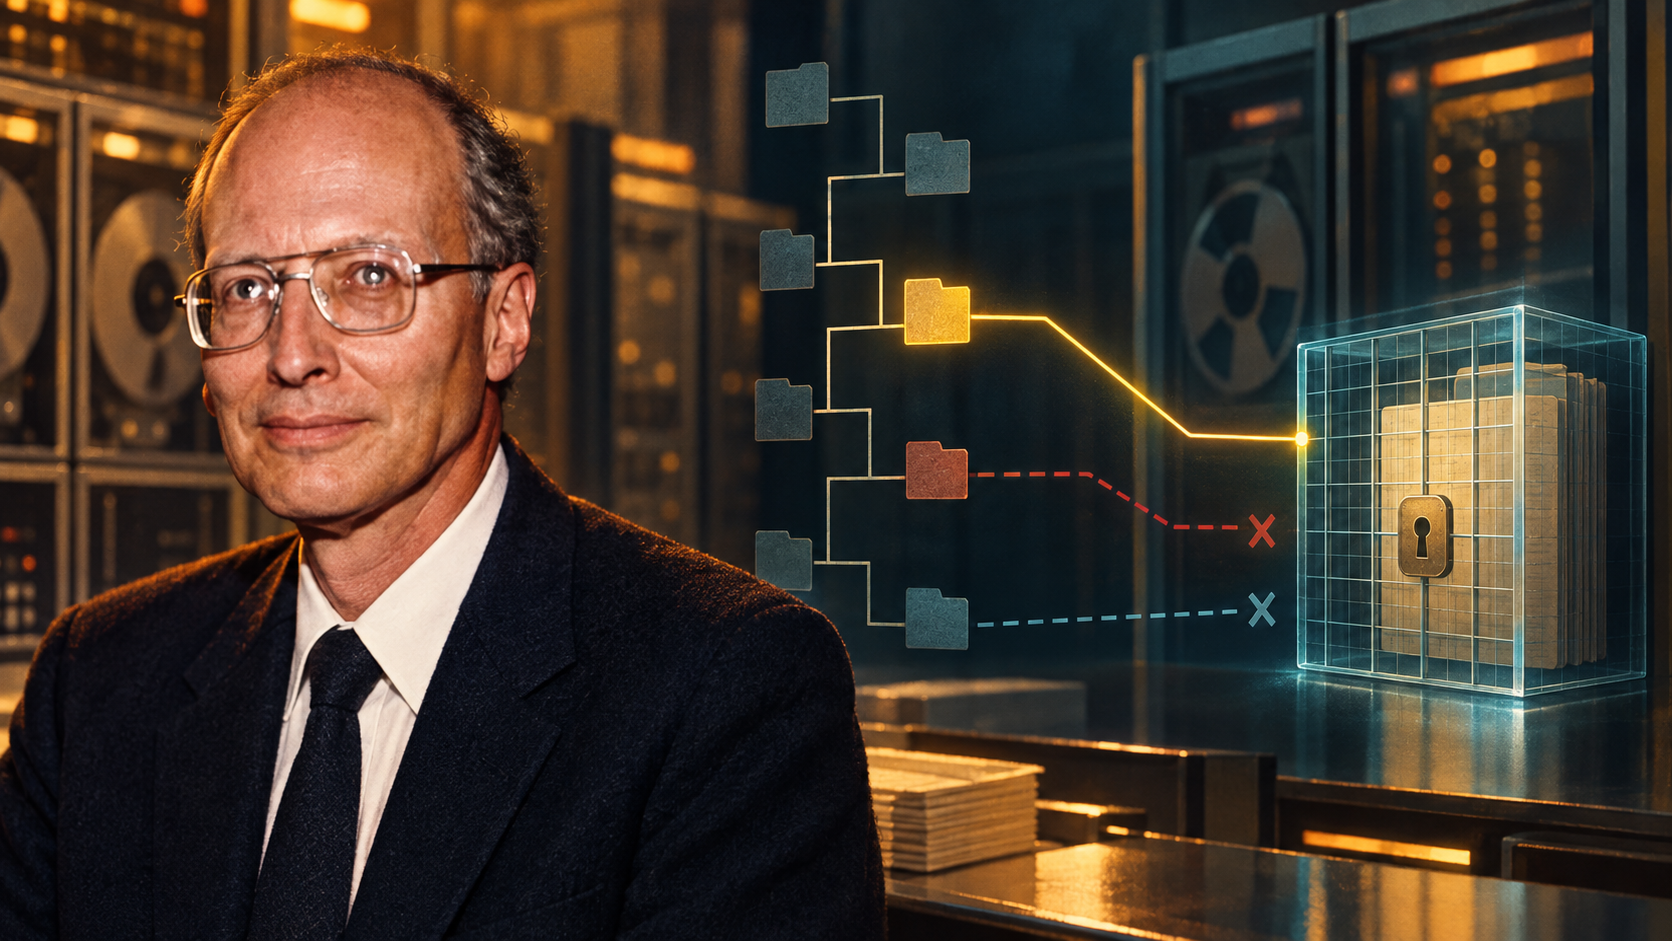
- In Jerry Saltzer’s 1974 Multics case study, a link was retained as a naming convenience but stopped carrying access privilege; the referenced segment’s access-control list decided what a process could do.
- Separating location from authority made revocation and audit more coherent, yet it did not recover copied information, validate the policy itself or remove the problem of stale remembered decisions.
Imagine lending a colleague a file by placing an entry in the colleague’s own directory. The entry finds the original file, but it also helps determine how that colleague may use it. When the loan ends, the owner cannot simply change one rule beside the file. Someone must alter the borrower’s directory. To discover everyone who still has access, an auditor must search directories across the system.
That was the weakness Jerry Saltzer drew from the Compatible Time-Sharing System when he compared it with Multics. CTSS links named an original file and commonly added restrictions on the permitted modes of use. Their flexibility had a cost: the same person might receive different rights through different links, revocation was awkward, and an access inventory required a broad search that could itself disclose information about other users.
Multics kept the useful half of the idea and discarded the dangerous half. A link remained an indirect address. It helped a process locate a segment. It did not confer access. Authority lived with the referenced item, in its access-control list.
The decision follows the segment
Saltzer’s paper describes Multics as a storage system built from named segments. A segment was both a unit of cataloguing and a unit of separate protection. When a process tried to gain access to a catalogued item, the system compared the process’s principal identifier with entries on the item’s access-control list. The applicable entry also specified a mode: a segment might be readable, writable or executable, while directories and message queues had their own operations.
This arrangement answered two questions in different places. A pathname or link answered which segment was meant. The access-control list answered whether this principal could perform this operation. A different route to the same segment did not silently manufacture a different grant.
The distinction changes who can withdraw a decision. In the CTSS example, authority was partly scattered among link records in borrowers’ directories. Multics placed the decisive list beside the protected item. An owner or administrator with the relevant control could update that list without first collecting every alias. A protection audit could inspect the rules attached to the item instead of treating every name in the system as a possible hidden grant.
That did not make Multics administration flat. Principal identifiers could include a person, project and compartment. More specific list entries took precedence over broader ones. Directories carried initial access-control lists whose contents were copied to newly created items. Authority over directories also structured who could alter the lists below them. The gain was not the disappearance of policy; it was a more legible place in which policy took effect.
Why a convenient inheritance was abandoned
Saltzer’s account is especially valuable because it records a rejected design, not only the final diagram. An earlier Multics arrangement treated a directory’s initial list as a common appendix to every item below it. One change could then produce different results for different items because of the way entries combined and were ordered. Users had difficulty predicting the consequences.
The system moved to copying the initial list when an item was created. That choice was less dynamically flexible: changing the directory default would not rewrite every existing item. But it made each item’s current rules more self-contained and understandable. The paper repeatedly frames protection as a tradeoff among expressive power, ease of comprehension and implementation cost. A feature that makes elegant abstractions but leaves administrators unable to foresee the effect of a change is not necessarily a security improvement.
The link decision follows the same logic. Putting restrictions on every path offers local customisation. It also creates several locations that may disagree about one protected item. Keeping the path as a path and the grant as a grant reduces the number of places that must be reconciled when a person joins a project, leaves it or changes roles.
Complete mediation includes remembered decisions
The later tutorial that Saltzer wrote with Michael D. Schroeder gave the broader principle a familiar name: complete mediation. Every access to an item should be checked for authority. In the 1974 case study, Saltzer makes the operational difficulty explicit. A continuously running system may remember an access decision for later use. Designers must then decide how a change in authority reaches those local memories.
This is where a simple slogan becomes an engineering obligation. Checking a rule at the moment a file is opened or a segment is mapped is not the same as checking it before every byte is touched. If an allowed mapping, handle or local cache remains usable after the central list changes, the revocation has not reached every place that relies on the older decision. The article’s historical evidence does not prescribe one modern invalidation mechanism. It supplies the question an operator must answer: which remembered decisions still survive?
A useful authorization record therefore needs more than an “allowed” flag. It needs the principal that asked, the item that was resolved, the operation requested, the rule version consulted, the decision time and the lifetime of any resulting handle. A revocation record needs its own completion evidence: which caches, sessions, mappings or delegated credentials were invalidated, and what later attempt demonstrated the new state?
Revocation has a hard boundary
Separating links from grants makes withdrawal more tractable; it does not make information reversible. Saltzer notes that someone who is entitled to read a segment can copy it. Removing the original permission does not reach into that copy. Controlling information after authorised release was still a research problem.
Nor did the paper present Multics as flawless. It described incomplete mechanisms and published weaknesses, including a large collection of modules in the most-protected area that could in principle compromise the system. The candid lesson is stronger than a victory story. A clean authority boundary helps reviewers see what must be trusted; it does not prove that the trusted part is small, correct or immune to mistakes.
The modern temptation is to call every shareable reference “access.” A URL is circulated, an alias appears in a workspace, or a handle survives in a client, and the visible reference is treated as the grant. Saltzer’s contrast suggests a sharper ledger. Record naming separately from authorization, authorization separately from use, and revocation separately from invalidation. The link may continue to name the file. Whether it opens the file should remain a fresh question.
Sources
- Saltzer — Protection and Control of Information Sharing in Multics
- Saltzer and Schroeder — The Protection of Information in Computer Systems
- Basic Principles of Information Protection
- Descriptor-Based Protection Systems
- The State of the Art
- Formal publications of Jerome H. Saltzer
- Brief biography of Jerome H. Saltzer
- Curriculum vitae of Jerome H. Saltzer
- Jerome H. Saltzer’s MIT home page
- MIT Multics History
- Multics—The First Seven Years
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance