
Policy continuity, legitimacy, and accountability signals across internet governance institutions.
Governance
Governance
Internet governance intelligence tracks institutions, policy processes, standards activity, registry operations, accountability disputes, and implementation signals that affect internet infrastructure. BTW.
RIR WatchdogCase FileNumber Resource SocietyICANNIETFHistory of InternetNOGs

RIR Watchdog, Case File, NRS, ICANN, IETF, History of Internet, and NOG sessions.
Coverage prioritizes implementation evidence and institutional behavior over declarative positions.
Latest Coverage
Latest from Governance
7,793 articles

IETF
Radia Perlman and the Appointed Forwarder That Had to Stop Forwarding
A TRILL switch may still hold the appointment for a VLAN while its safest legal action is to drop the native frames it would normally handle. That is not a contradiction in the standard. It is the moment when recorded authority and permission to act must be read as separate…

Story
AFRINIC Whois mnt-domains Authorizes Reverse-Domain Records, Not DNS Service Operation
A database key can authorize the creation of a reverse-domain record while every DNS query to the supposed service still times out. In the AFRINIC Database, `mnt-domains` identifies a maintainer with authority over child domain-entity creation. It is evidence about registry…

NANOG
The Mailing List Is an Operations Room, Not a Legislature
NANOG's mailing list is valuable because operators can expose a fault, compare evidence and correct a diagnosis in public. That practical authority should not be confused with permission to speak for networks whose operators did not join the thread.

CASE FILE
The IAB Gave Post-Quantum Authentication Evidence Another Week. It Still Needs a Chain of Custody
The extended deadline invites one more week of operational evidence. The harder task begins after a paper arrives: keeping measurements, disclosure choices, workshop synthesis and eventual standards work from collapsing into one unsupported claim.

IETF
An MPLS Echo Response Is Not Bidirectional Proof Until the Requester Validates the Return Path
A valid echo response may come from an intermediate point reached when the probe’s TTL expires. Its arrival proves that a responder answered from that position; it does not prove that the intended reverse LSP exists or carried the response.

History
The Bit That Made Routers Report Their Limits: IPv4 DF and Path MTU Discovery
One IPv4 flag began as a prohibition: do not split this datagram. Path MTU Discovery turned that refusal into a measurement loop. An oversized packet would be discarded, a router would report the narrow link, and the source would learn what the path could carry—provided the error…

History
Readable Without a Parser Did Not Mean Safe to Parse: RFC 1874
In 1995, one MIME label tried to preserve two truths about the same structured document. A person without SGML software might still read its general meaning; a machine with SGML software might interpret far more than the visible lines. RFC 1874 called the first case `text/sgml`…
Story
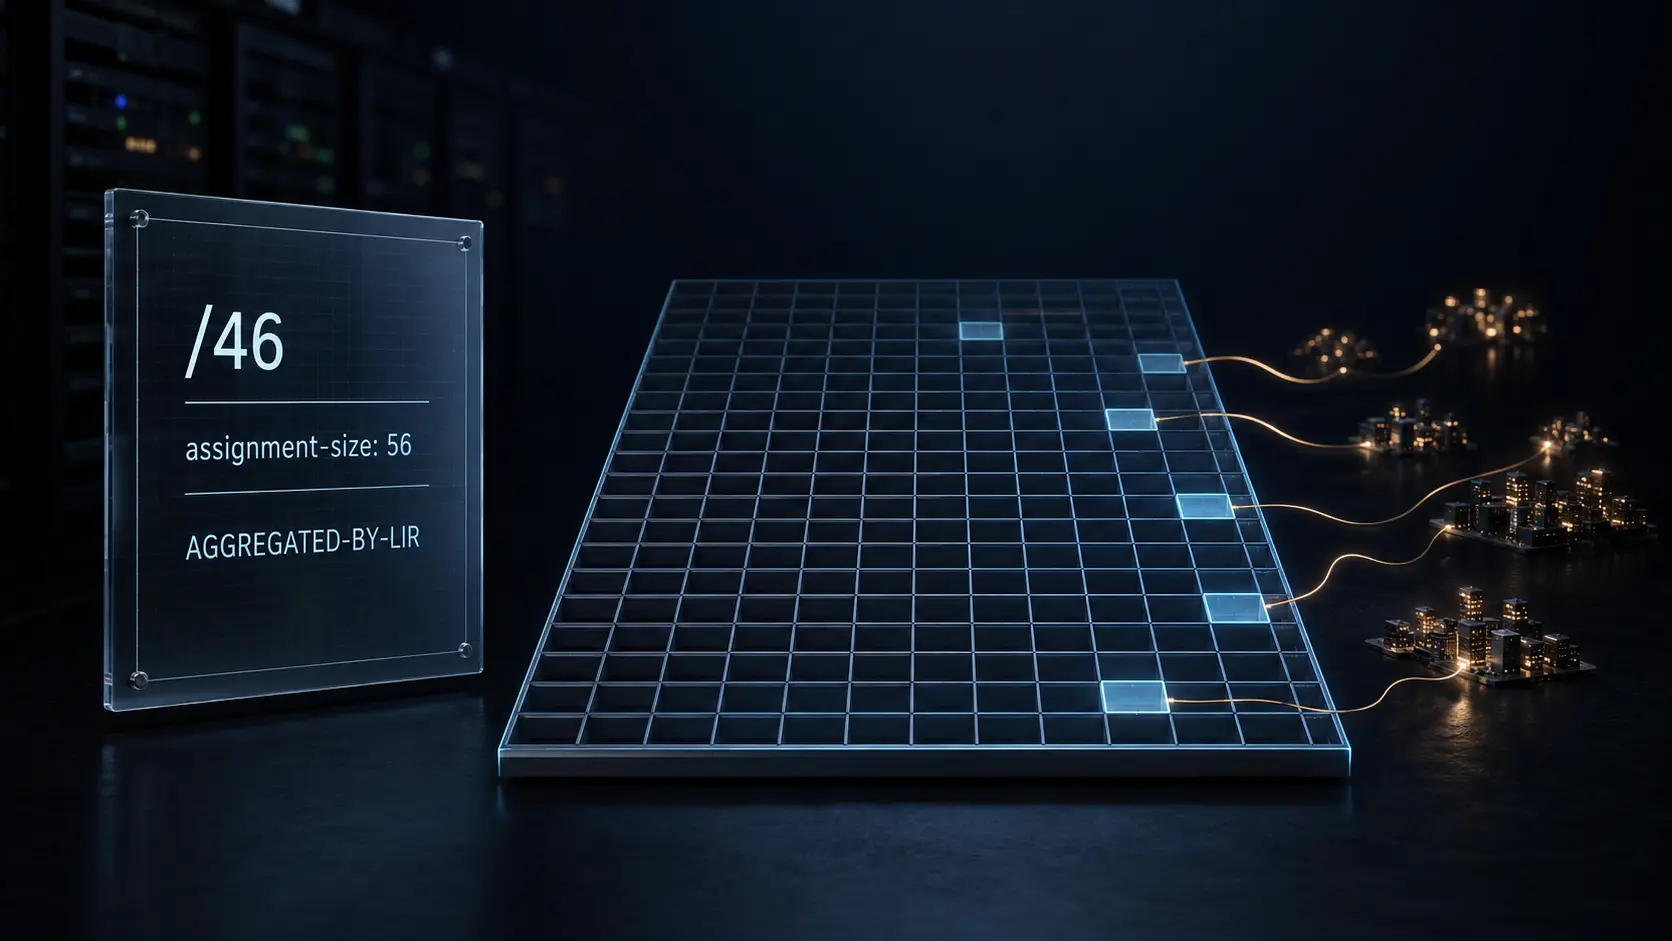
RIPE assignment-size Describes Aggregated IPv6 Assignments, Not Active Subscribers
A `/46` contains 1,024 possible `/56` prefixes. When a RIPE Database entity pairs that aggregate with `assignment-size: 56`, the arithmetic is exact—but the tempting subscriber count is not. The field records the size used for End User assignments inside an aggregate…

Story
AFRINIC's IPv6-for-IPv4 Rule Needs a Control Test
An AFRINIC draft would make access to remaining IPv4 conditional on an IPv6 plan and measured deployment. The incentive is defensible; the unresolved question is whether the measurement follows the operator's own work or outcomes controlled by customers and external networks.
CASE FILE
A security.txt File Needs a Live Disclosure-Channel Receipt
The `Expires` line says the coordinates are still publishable. It cannot tell a researcher whether anybody is listening. That gap between a fresh file and a working response operation is where a small disclosure-channel receipt becomes useful.

CASE FILE
The Message Was Encrypted. Its Headers Still Needed Their Own Receipts: RFC 9788
An encrypted-mail badge compresses a complicated evidence chain into one reassuring symbol. RFC 9788 shows why the symbol cannot answer which header was hidden, which sender identity was authenticated, what an intermediary changed, or where a reply may safely go.
IETF
VIRP Moves Write Authority Outside the Gate, but Its One-Use Grant Is Still Unbuilt
Revision 07 of VIRP proposes a sharper control boundary for autonomous network operations: the automation gate keeps a read-only device identity, while a separate service decides whether any write may proceed. That is a real change in where authority sits. It is not yet the…

CASE FILE
An OSPS Baseline Claim Needs a Version, a Level and a Date
“OSPS compliant” looks tidy in a supplier register. It is also incomplete. The Baseline is versioned, divided by project maturity and explicitly assessed at a point in time; a useful claim must preserve those coordinates and the evidence behind them.

History
The Departure Packet Asked Everyone to Forget. It Could Not Prove They Did: RFC 1868
In 1995, a dial-in user could leave one communications server and return through another while the local network kept sending packets to the first. RFC 1868 proposed a sixteen-byte correction: broadcast an unusual ARP Reply that told every peer to delete the departed address from…

Story
APNIC’s Registry API Returns Batch Results Without a Request-Item Field
APNIC’s Registry API can accept several creates, updates and deletes in one batch. Its public schema then reduces each result item to `status` and `message`, without declaring which request item the row answers. That is not evidence of a failed API. It is a small contract gap…

CASE FILE
The Key Was Known. It Was Not Yet Trusted
A self-signed DNS update arrives at a parent carrying a new key and an instruction to delete the old one. The signature proves that somebody holds the new private key. It does not prove that this somebody may change the child's delegation. As DNSOP's 7 September Last Call reaches…

CASE FILE
A CA Audit Is Not a Certificate-Issuance Verdict
An annual assurance report can show that a certificate authority’s controls were examined over a bounded period. It cannot, on its own, answer the smaller and more consequential question a relying party often needs to ask: why was this exact certificate for this exact name and…
History
The Message Reached the Partner’s System. The Transaction Had Not Been Accepted: RFC 1865
A purchase order can cross the Internet without crossing the final boundary that matters. In 1996, RFC 1865 described a dedicated SMTP connection delivering EDI directly to a trading partner’s system and called that delivery assured. The phrase was useful at the transport layer…

CASE FILE
Four Bits Looked Like IP. They Were Not: RFC 9790 and the End of Payload Guessing
An MPLS router can see `0x4` after the label stack and reach for an IPv4 hash. RFC 9790 explains why those four bits cannot carry that conclusion on their own.

CASE FILE
A GitHub Actions workflow_run Trigger Is Not an Artifact-Trust Verdict
A GitHub Actions `workflow_run` trigger can create a useful separation between an upstream check and a downstream, more privileged workflow. It does not establish that the upstream result, the artifact consumed downstream, or a later target operation deserves trust.
Session Map
Governance Branch
RIR Watchdog
Five regional sessions tracking allocation policy, board legitimacy, and institutional continuity.
Open RIR WatchdogCase File
Long-cycle governance dossiers with legal, election, and institutional stress analysis.
Open Case FileNumber Resource Society
Membership, charter, and resource-governance intelligence from the NRS ecosystem.
Open NRS SessionICANN
DNS coordination, accountability frameworks, and global multi-stakeholder process dynamics.
Open ICANN SessionIETF
Protocol standardization trajectory and interoperability risk under fragmented policy conditions.
Open IETF SessionHistory of Internet
Long-cycle infrastructure history used for governance interpretation and structural forecasting.
Open History SessionNOGs
Operator-level implementation intelligence from APRICOT plus regional and national NOG ecosystems.
Open NOGs Session