
Summary
- ARIN’s 28 July 2026 release accepts non-human service accounts and lets REST calls carry API tokens in an
Authorizationheader; URL tokens remain supported. - Two requests submitted in 2022 reached closure after the release: one for machine accounts, one for a less loggable home for the key.
The URL has many virtues. It tells a browser where to go, a proxy what to fetch and a server which record is in question. It also has a habit of turning up in logs. An API secret is a poor passenger for that journey.
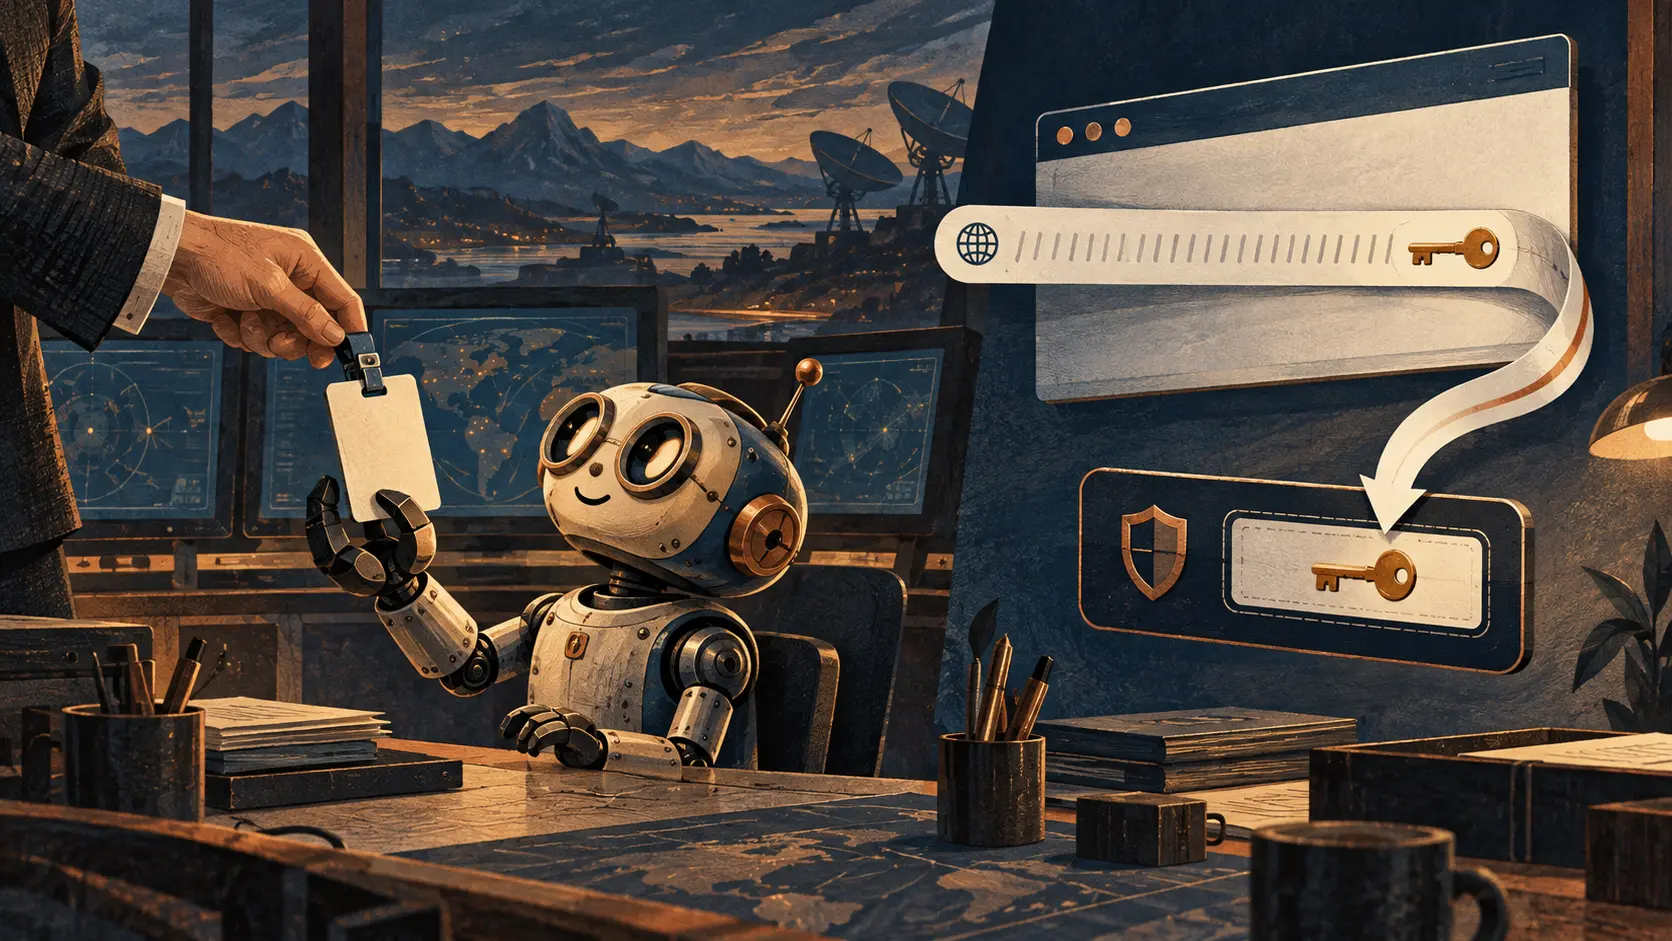
On 28 July 2026, ARIN Online added a preferred alternative: send the key in the HTTP header as Authorization: ApiKey <API_KEY>. The old URL parameter still works. ARIN says the header is the more secure method; the change gives operators a route that keeps the secret out of the URL itself.
That closes Suggestion 2022.5, submitted on 11 February 2022. Its author pointed to a familiar operational nuisance: systems often log whole URLs, so a key placed there can travel into logs read by people who never needed the credential. ARIN agreed that a header was the best alternative and put the work on its engineering roadmap. The suggestion closed on 29 July 2026, one day after the feature release.
The same release removed a different gate. ARIN Online now accepts non-human service accounts. Suggestion 2022.11, filed on 15 April 2022, asked for those accounts so integrations could use an identity built for automation. ARIN’s original objection was attribution: if an API changed a record, the organisation needed to identify who had made the change. In April 2022, ARIN accepted that service accounts would help customers and said removing the restriction required little work. The door finally opened four years later.
Treat the two changes as separate controls. The service account names the automated actor; the header carries its secret outside the URL. ARIN’s Reg-RWS guide still ties modifications to an ARIN Online account linked to a Point of Contact with authority over the record. The API key authenticates the call; the linked POC supplies the record authority.
ARIN’s key guide makes the housekeeping unusually concrete. A key does not expire, can be deactivated at any time, and is shown in full only when created. Users can create multiple keys to track specific requests or report access. The 2024 API-key consultation also discussed IP-address-range limits, but ARIN placed that work in a separate investigate-and-scope lane. The July 2026 release announces header support; the range question has its own timeline.
This is a quiet but useful repair to the automation model: machines can now have names of their own, and their credentials can stop riding in a field built to be copied into logs. The next job is assigning a human owner to each machine identity and deciding who can retire its key.
Sources
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance



