
Open standards body with worldwide implementation impact.
Governance / IETF
IETF
IETF governance intelligence tracks institutions, policy processes, standards activity, registry operations, accountability disputes, and implementation signals that affect internet infrastructure. BTW.
GlobalProtocol GovernanceInteroperability Risk

Protocol process and standards legitimacy.
Spec-to-implementation gap across vendors and operators.
Major standards shifts usually affect systems over 120d+ cycles.
Latest Coverage
Latest from IETF
1,015 articles

IETF
A BGP Confederation Hides Internal Topology Without Erasing Internal Policy Authority
A large network can divide itself into smaller BGP policy domains while still presenting one autonomous-system number to the outside world. RFC 5065 makes that boundary operationally useful, but not costless. The Member-AS structure hidden from external peers still decides how…
IETF
An Origin Validation Community Carries a Trust Decision Without Delegating Import Policy
An Origin Validation Community Carries a Trust Decision Without Delegating Import Policy intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences…

IETF
QUIC DATAGRAM Keeps Message Boundaries, Not Delivery Guarantees
A QUIC DATAGRAM frame can carry a complete application datagram without retransmission or ordering relative to other DATAGRAM messages. That makes it useful for time-sensitive information, but it does not turn local submission or packet acknowledgment into a receipt for the…

IETF
A 65,535-Octet BGP Message Is a Negotiated Capacity, Not Network-Wide Permission
A router can accept a 65,535-octet UPDATE from one peer and still be unable to carry that announcement across the next session. RFC 8654 expands the BGP envelope only after a bilateral capability signal. At mixed-support boundaries, the operator inherits a harder decision…

IETF
ACME Can Match the Constraint. Trust Still Arrives Out of Band
A certificate-automation server can verify a signature, reject an expired token and compare two encoded constraints byte for byte. None of those checks answers the prior question: why was this issuer entitled to authorize that constraint? Revision 05 of an ACME Working Group…

IETF
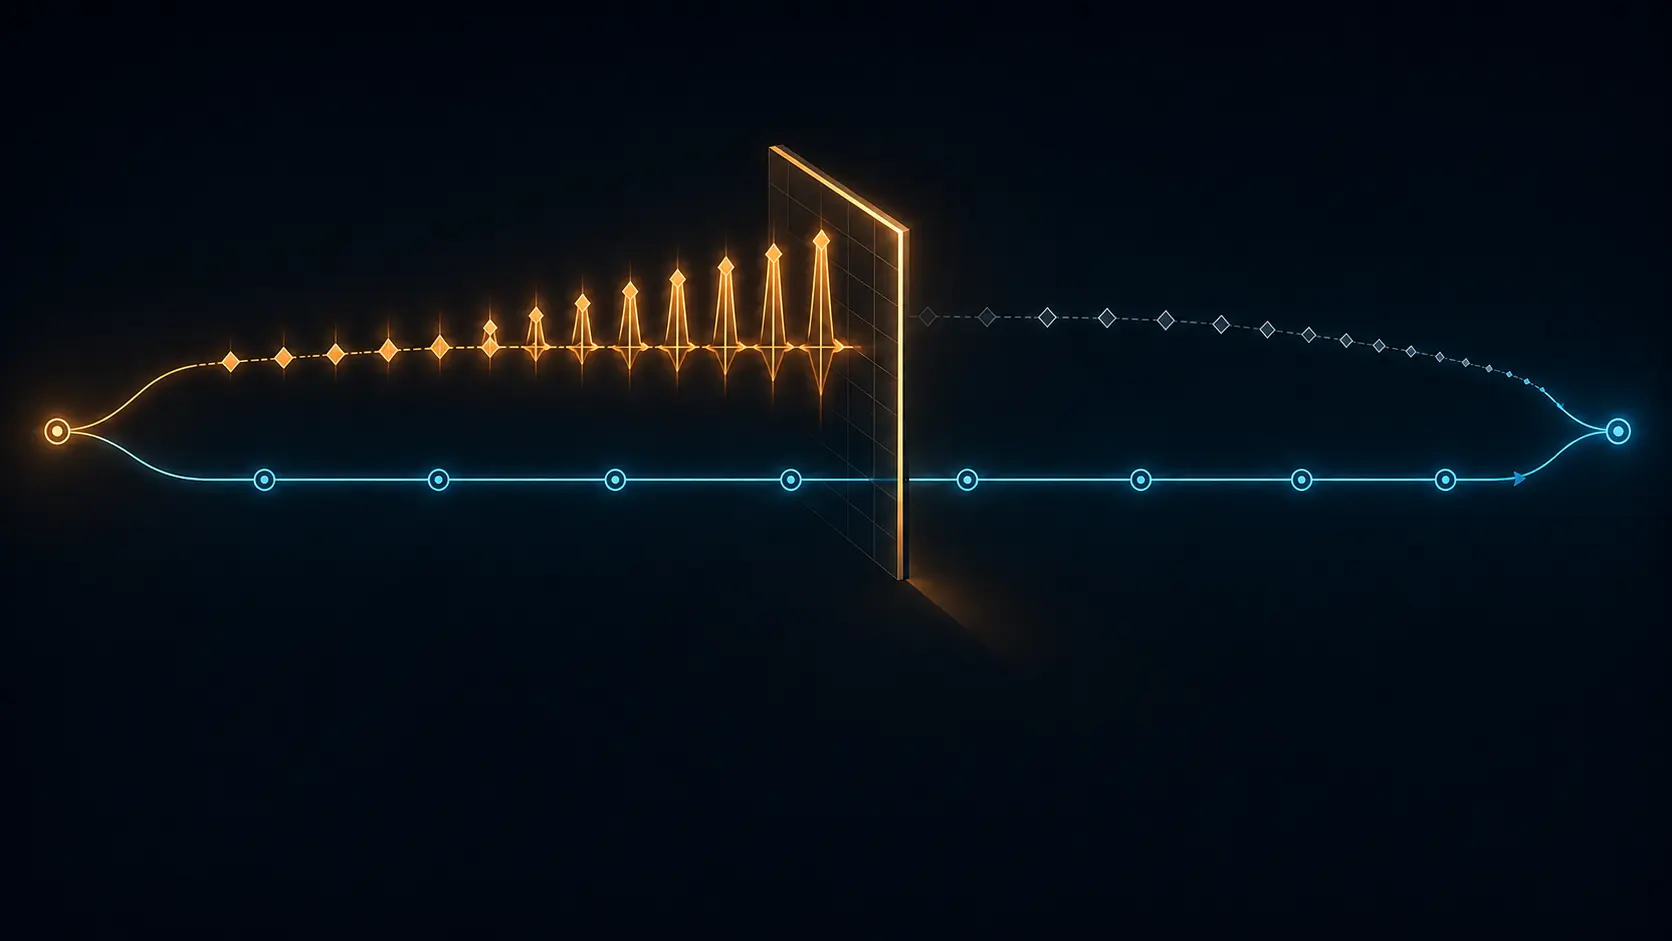
QUIC PTO Is a Progress Probe, Not a Packet-Loss Verdict
A Probe Timeout asks QUIC to seek acknowledgment progress; it does not turn an unanswered packet into a proven loss.
IETF
Route Flap Damping Converts Churn into Suppression—and the Threshold Decides Who Disappears
A route can be reachable and still vanish from local use because its recent history crossed a configured penalty threshold. Route flap damping protects BGP peers from repeated updates, but it also turns a stability estimate into a reachability decision. RFC 7196 makes that…

IETF
QUIC ACK Delay Is Not Network Latency
ACK Delay is a receiver’s report of intentional waiting for one acknowledged packet. It is useful to RTT estimation, but subtraction alone cannot turn it into a network-only measurement.

IETF
A Route Reflector Scales IBGP by Centralizing Dissemination, Not Route Authority
The full mesh disappears, but the decision point does not. RFC 4456 lets a route reflector redistribute an IBGP-learned route to selected internal peers, replacing a session-count problem with a governed dissemination hierarchy. The reflector can scale reachability, yet its…

IETF
RGIP’s New Stop Rule: Repair Can Erase Evidence
Automation is useful when a public record has lost a redundant copy. It becomes dangerous when the fault is inside the record’s own integrity history. Revision 02 of the proposed Reilly Government Integrity Protocol draws that line explicitly: a machine may retry limited…

IETF
The Ports That Outlived Their Protocols: RFC 9900 and the Discipline of Giving Numbers Back
Ports 831, 832, and 833 can persist in diagrams, service files, and filters even after the NETCONF transports once attached to them never reached known production deployment. RFC 9900 therefore retires the number bindings without erasing their semantic history.

IETF
QUIC Coalescing: Efficient Wire Use, Separate Delivery
Putting several complete QUIC packets into one UDP datagram can reduce carriage overhead during the handshake. It does not turn those packets into one protected entity, one acknowledgment event, or one application result.

IETF
Four-Octet ASNs Expand the Namespace While Compatibility Still Rewrites the Path
Four-Octet ASNs Expand the Namespace While Compatibility Still Rewrites the Path intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that…

IETF
One Name, Many Rules: RFC 9899 and the Control Surface of Reusable ACL Sets
A security team changes one named prefix set once, and every ACL that references it can inherit the change without rewriting each parent rule. That mechanism is the promise—and the control problem—behind RFC 9899’s reusable policy entities.

IETF
Shrink the Trust Domain: RFC 9898 and the IPv6 Neighbor-Discovery Isolation Choice
On one IPv6 access segment, three different root causes can surface together: multicast load, implicit trust of every on-link node, and router Neighbor Cache Entries created on demand. The practical question is therefore not which symptom to patch, but which part of the Neighbor…
IETF
QUIC Handshake Confirmation Is Not Application Readiness
A green dashboard can hide an important distinction: HANDSHAKE_DONE marks a transport and cryptographic transition, not a completed application transaction. Confirmation retires Handshake keys, but it does not certify early-data acceptance, backend health, durable storage, or…
IETF
A BGP Shutdown Message Explains the Decision Without Delegating the Restart
A session can disappear before an email thread catches up. RFC 8203 lets an operator place a short UTF-8 explanation inside an Administrative Shutdown or Administrative Reset notification. The explanation can connect a protocol event to a maintenance record, but it is not an…
IETF
RDAP Dropped Two DELEG Fields. Its Referenced Write Model Still Carries Them
Registration data moves through more than one protocol before it reaches a public query. A 4 September revision of the proposed RDAP extension for DNS DELEG has caught its read model up with DELEG-11 by removing two old fields. The EPP provisioning draft it cites still includes…

IETF
Authenticated Is Not Reachable: RFC 9897 and the MP-DCCP Path-Join Boundary
An authenticated `MP_ADDADDR` advertisement is control data, not permission to send traffic on a new path. That path becomes usable only when `MP_JOIN` binds a new subflow to the original connection and completes the nonce/HMAC reachability handshake.

IETF
A BGP Large Community Carries a Policy Signal Without Granting the Sender Authority
A BGP Large Community can carry an operator’s intent across network boundaries in a form that still fits four-octet ASNs. That portability is useful precisely because it is not command authority. The Global Administrator identifies the namespace whose documentation gives a value…
Member Unlock
Restricted Profile Intelligence
Login is required to unlock full profile briefings and deep-dive sections.
Strategic Circle Briefing
Join to unlock strategic briefings after signing in.
Join Strategic CircleLeadership Alliance Briefing
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance