
Summary
- RFC 3012 let a visited Mobile IPv4 foreign agent issue its own fresh challenge and reject a missing, already-used or unknown value before remote AAA authentication had finished.
- Returning the right challenge was only local replay evidence: the request still needed an authentication extension, an external or home-domain decision, registration acceptance, forwarding state and delivered traffic.
A mobile node arriving on a foreign network presented an awkward timing problem. The visited network had to decide whether to spend resources processing a registration, yet it might share no security association with the visitor. The credentials able to answer the larger identity question could live elsewhere, in the home domain or in an Authentication, Authorization and Accounting system.
Waiting for that remote machinery did not remove the local replay problem. An attacker could resend an old request while it still looked structurally valid. The foreign agent—the visited network’s Mobile IPv4 gateway—needed a fact of its own before the trust chain beyond it had spoken.
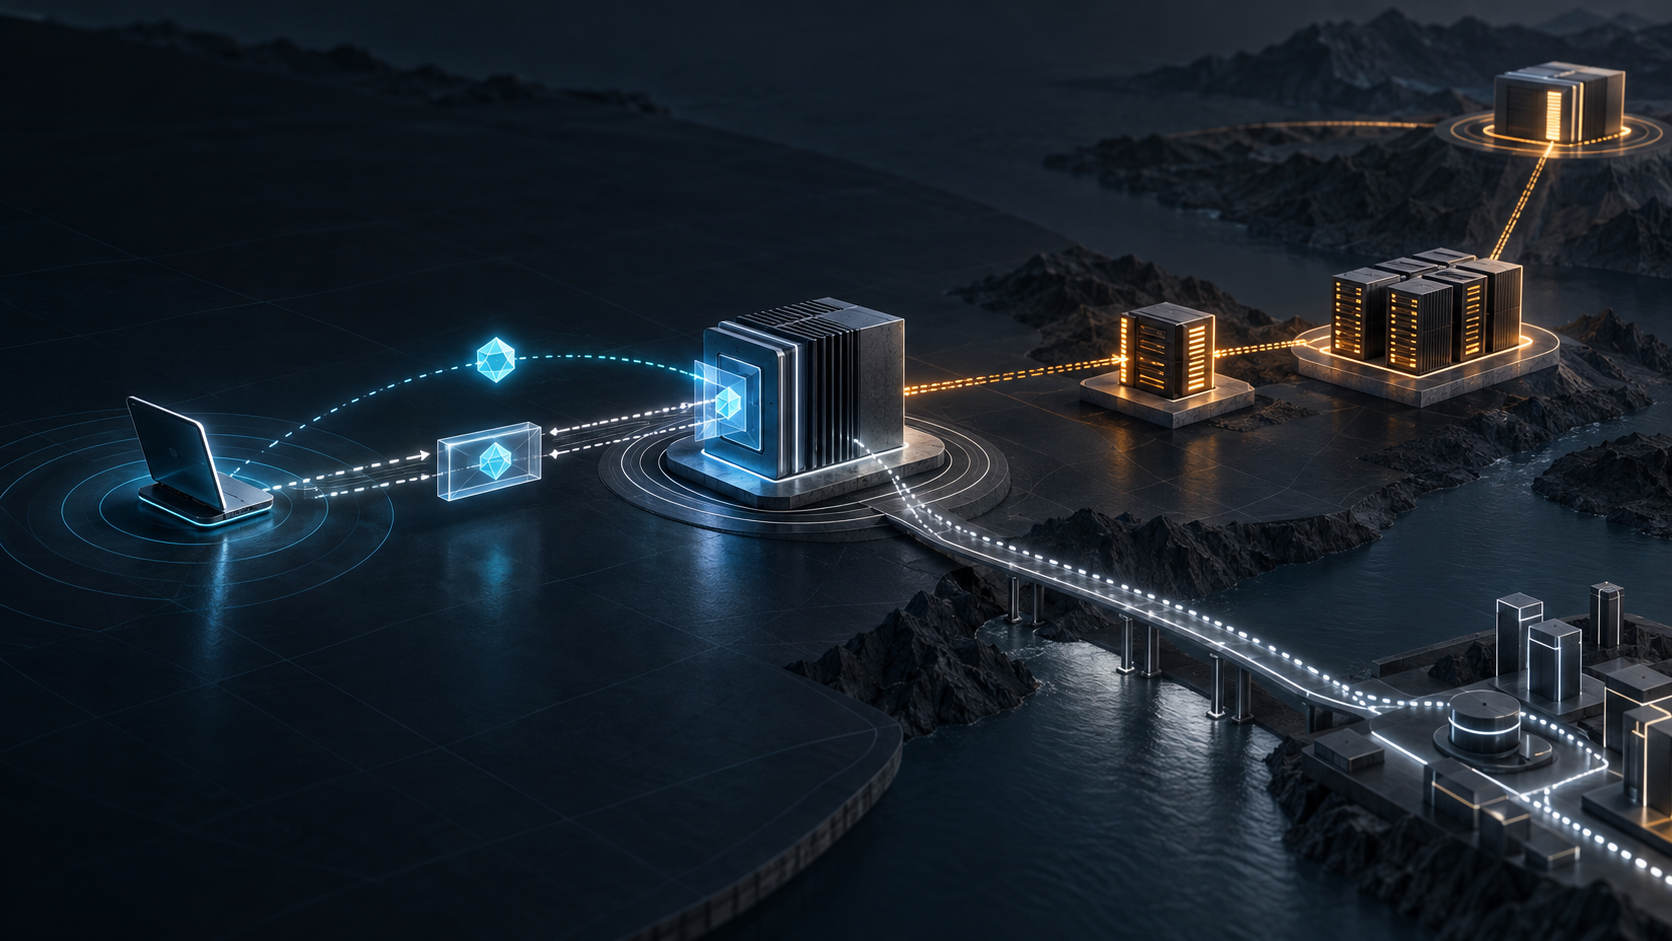
RFC 3012, published as a Proposed Standard in November 2000, gave the foreign agent that fact. It could place a Challenge extension in its Agent Advertisements. The value was to be random and at least 32 bits long. A mobile node copied the latest acceptable value into an MN-FA Challenge extension in its Registration Request.
The move sounds like ordinary challenge-response, but its institutional location mattered. The foreign agent chose the challenge on the visited link. It could therefore recognize a response to its own recent act without first asking the home network who the visitor was. Freshness became locally testable even when identity remained remotely dependent.
That did not make the challenge a credential. RFC 3012 required the MN-FA Challenge extension to be followed by an authentication extension. If the mobile node and foreign agent already shared a security association, the request carried Mobile-Foreign Authentication. If they did not, the node had to carry MN-AAA Authentication and was encouraged to include the Network Access Identifier defined by RFC 2794.
The ordering rule expressed an evidence rule. The challenge named the recently issued token; the authenticator bound protocol material to a secret and an algorithm selected by a Security Parameter Index. A request containing a challenge but neither Mobile-Foreign nor MN-AAA Authentication had to be silently discarded. Correct token, absent binding: no acceptable claim.
The Network Access Identifier did another job. It gave the system a user-style name whose realm could help route a verification request across administrative domains. But a routable name was not proof that the speaker owned it. Identifier, authenticator and authorization remained different objects.
RFC 3012 made the challenge state visible through three errors. MISSING_CHALLENGE meant the required field was absent. STALE_CHALLENGE meant the same mobile node had already used the value. UNKNOWN_CHALLENGE meant the value was not the last one returned successfully to that node and was not among the recent advertisements inside the configured challenge window. IANA's Mobile IPv4 registry preserves those public code points.
These were not synonyms for “authentication failed.” Each located a different failure before or around authentication. Absence, prior use and lack of local issuance history called for different operational responses. The specification thereby prevented one generic rejection from erasing the state transition that caused it.
There was also a carefully bounded exception. Networks retransmit. If a mobile node resent a Registration Request with the same 64-bit Identification value and the same challenge while the foreign agent still held the matching request as pending, the foreign agent forwarded it again. Outside that pending record, reuse normally became stale.
The exception shows why replay protection cannot be reduced to “never accept the same bytes twice.” A retransmission can represent the same live transaction rather than a second attempt to create authority. The foreign agent needed memory—Identification, challenge, mobile-node association and pending lifetime—to tell those cases apart.
The downstream reply had to be bound as well. When the foreign agent kept the challenge in a request sent onward to the Home Agent, it was expected to retain that value with the pending registration. A Home Agent reply lacking the same challenge had to be rejected and relayed to the mobile node as a missing-challenge failure. The match was a transaction receipt: this downstream result belonged to that locally witnessed request.
Alternatively, if a directly shared Mobile-Foreign security association allowed the foreign agent to validate and remove its challenge material before forwarding, it was expected to retain the Registration Request’s Identification field locally. The representation could change; the duty to preserve a replay boundary did not.
The external decision remained deliberately outside the protocol. RFC 3012’s appendix called it “verification infrastructure.” A foreign agent could hand authentication material to that infrastructure and wait for a secure result. The document did not specify the AAA protocol or require the verifier to be a Mobile IPv4 entity. Local deployments could use mechanisms available to them.
That was a thin standard with a precise seam. Mobile IPv4 described what the visitor carried and what the foreign agent could check. The verification system decided credentials and authorization by another path. The foreign agent later acted on a positive or negative result. Standardization connected the layers without pretending to own all of them.
One reserved SPI, CHAP_SPI 2, supplied a CHAP-style MD5 calculation aligned with contemporary RADIUS practice. That accommodation made existing AAA systems easier to use, but RFC 3012 did not present it as timeless cryptography. Its security section said the construction was weaker than HMAC-MD5 and should be avoided whenever possible.
This warning matters historically. Interoperability often begins by fitting new protocol control into installed verification systems. The compatibility bridge may be the reason deployment is possible and the reason later revision is necessary. A standard can record the compromise without turning it into a permanent security ideal.
The document also admitted a denial-of-service boundary. A malicious mobile node could replay traffic and provoke a rejection-looking response even while a legitimate acceptance was on its way. A user might act as if registration had failed although the successful reply was still in flight. Freshness checks constrained one attack class; they did not remove races, spoofed indications or every way to consume agent state.
Short challenges sharpened the problem. If the foreign agent chose fewer than four bytes, it was advised to preserve the Identification field as additional evidence that requests were unique. Entropy, retained state and transaction identity were substitutes only within explicit limits. The system could not recover uniqueness by describing a short token as “random.”
Six years later, RFC 4721 obsoleted RFC 3012 and tightened the design. It required the foreign agent to record applicable challenge values for each mobile node. A node that had registered with one value could not later use a value advertised before it. The revision clarified reply and advertisement processing, added defenses against bogus messages and introduced an HMAC-MD5 option.
Those changes are not proof that a named network suffered an exploit. They are stronger evidence of something more general: a challenge's meaning depends on ordered history. The bytes are fresh only relative to which agent issued them, which node used them, which prior value was accepted, which request remains pending and which authenticator covers the exchange.
The distinction from RFC 2002 is equally important. Base Mobile IPv4 created a temporary binding between a stable home address and a current care-of address. A successful, authenticated Registration Reply could establish that the Home Agent accepted that binding. RFC 3012 addressed an earlier and more local uncertainty at the visited edge. It did not prove the node's physical location or that tunneled packets would arrive.
Nor was it merely a replay of PPP CHAP. CHAP's authenticator and peer operated within a PPP authentication exchange. RFC 3012 inserted a foreign-agent freshness token into Mobile IPv4 registration and allowed a separate AAA infrastructure to supply the broader credential decision. Borrowing a digest style did not make the control planes identical.
Through Lu Heng's minimum-specification lens, the achievement was restraint. The common layer defined a challenge, its ordering, its acceptable history and its errors. It did not constitutionalize one AAA vendor, one business policy or one home-domain arrangement. Local operators retained the right—and the burden—to choose verification infrastructure and admission policy.
Running-code primacy adds the necessary brake. An RFC can prove that a state machine was published. An advertisement capture can prove that a foreign agent emitted a challenge. A request capture can show that a value returned beside an authenticator. Only verifier records can show the cryptographic result; only policy records can show authorization; only agent state can show registration; only traffic observations can show service.
The temptation is to compress that chain because “challenge-response” sounds conclusive. RFC 3012's own structure resists the compression. A challenge without authentication is discarded. An authenticator may still require remote infrastructure. A positive verification result still precedes registration state. Registration still precedes usable forwarding. Each transition has a different principal and a different receipt.
The gate issued a challenge because it needed one fact it could establish locally. Trust still had to arrive from elsewhere. That was not a defect in the design. It was the design's most honest statement about where knowledge and authority actually lived.
Sources
- RFC 3012, Mobile IPv4 Challenge/Response Extensions
- RFC Editor information page for RFC 3012
- RFC 2002, IP Mobility Support
- RFC 2794, Mobile IP Network Access Identifier Extension for IPv4
- RFC 1994, PPP Challenge Handshake Authentication Protocol
- RFC 2865, Remote Authentication Dial In User Service
- RFC 4721, Mobile IPv4 Challenge/Response Extensions (Revised)
- IANA Mobile IPv4 Numbers
- Lu Heng, Minimum Initial Specification, Localized Future Decision, and Voluntary Adoption
- Lu Heng, Running-Code Primacy
- Lu Heng, On Reality Layers, Symbolic Power, and Why Clarity Feels So Hostile
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance