
Topic
Security Automation
Within the Topic facet, Security Automation topic intelligence connects articles that share a specific subject, signal focus, or monitoring theme. The page gives readers a richer path through related reporting, source evidence, market actors, and infrastructure implications, with enough context to understand why the topic matters across company movements, governance decisions, regional exposure, and operational risk. Readers can compare recurring signals, affected organisations, public evidence, market context, service continuity, procurement, competition, compliance, and strategic planning questions behind the subject instead of stopping at a thin list of matching articles. It explains what the topic covers, which infrastructure actors or policies are involved, what evidence supports the coverage, and why the subject may matter for operators, customers, investors, and policy readers.

North America Cloud Services
247.ai's Real Test Is Whether Support Ends Cleanly
247.ai, Inc. sells into one of the hardest corners of enterprise automation: the moment a customer needs a useful answer, a safe resolution, or a clean escalation. Its value is not proved by chatbot deflection alone. It is proved when intent recognition, knowledge freshness…
Europe and Middle East Cloud Services
Deutsche Telekom MMS Is Measured After the Digital Service Goes Live
Deutsche Telekom MMS GmbH has the brand cover, partner network and specialist range to win enterprise transformation work, but the harder test starts after a cloud migration, application rebuild, security program, customer portal or AI service is accepted by the organization that…

North America Cloud Services
Roblox's Real Test Is the Accepted Creator Platform State
Roblox is not tested only by how many people open the app or how large bookings become in a quarter. Its harder test is whether a creator build, asset, safety action, payout signal or live-experience update can be moved into an accepted platform state that players, creators…

North America Cloud Services
Plaid Inc. Is Measured by the Bank Link That Keeps Working
Plaid Inc. has made the bank-link screen feel like a small moment in a fintech onboarding flow. In repeated use, however, the value of Plaid is decided after that moment: whether consent remains valid, whether the data is fresh enough, whether the institution supports the needed…

North America Cloud Services
Tenable and the remediation decision that survives the backlog
Tenable is easiest to understand as a scanner company because Nessus made the brand familiar. That frame is now too small. The harder test for Tenable is whether exposure evidence from assets, vulnerabilities, identities, cloud services, operational technology and external…
North America Cloud Services
Intercom's AI Support Test Is the Resolution Customers Accept
Intercom's strongest claim is not that a customer-service team can add an AI chat surface. The harder claim is that a live customer request can move through knowledge retrieval, policy rules, account context, escalation and ticket state into an answer, update or handoff that the…

North America Cloud Services
Netskope's Hardest Test Is the Access Decision That Users Never See
Netskope is often described through the wide language of secure access service edge, security service edge, cloud access security, zero-trust access and data protection. The more useful test is narrower. Its value depends on whether an enterprise can move a live request from a…

North America Cloud Services
Stripe's real test is the state after the payment
Stripe is often judged by the grace of its developer interface, but the harder production question starts after a checkout looks complete. The company earns its place in a commerce stack when payment, invoice, tax, risk, dispute, balance and payout state remain consistent enough…

Europe and Middle East Cloud Services
Adyen Is Tested by the Payment That Actually Clears
Adyen has become one of the most important payment infrastructure companies for large merchants because it sits close to the decision that matters most in commerce: whether a customer payment attempt becomes an accepted, defensible, settled transaction. Its scale, banking…

Global Cloud Services
Oscilar's real test is the risk decision someone can defend
Oscilar sells into a market where speed is useful only when the decision can survive review. The company's risk platform is strongest when it helps fraud, onboarding, compliance and credit teams accept more good customers, stop more bad activity, explain borderline calls, route…
Global Cloud Services
Fingerprint is tested by the trust decision, not the browser match
Fingerprint sells a deceptively simple promise into a difficult operating environment: identify the device or visitor behind a digital session well enough that a company can accept, challenge, or block the action with less fraud and less customer friction. The question is not…

Asia-Pacific Cloud Services
Hitachi Systems' Security Test Is the Response the Customer Will Accept
Hitachi Systems sits in a difficult part of the cybersecurity market: close enough to the customer environment to be judged on handoff, approval and cleanup, but broad enough that its value is often described through group scale, systems integration and acquired security…

North America Cloud Services
EnStream's real test is the accepted mobile-identity decision
EnStream sits at a hard junction in Canadian digital trust: banks, fintechs, marketplaces and other services want a fast answer about whether a phone number still belongs to the person in front of them, while mobile carriers hold signals that can make that answer more reliable…

Global Cloud Services
Fortinet Put to the Test When a Security Action Must Be Accepted and Reversible
Fortinet, Inc. sits close to where security advice becomes production changes: a firewall rule, a quarantine, a policy installation, a firmware step, a SOC playbook, a generated query, or a remediation recommendation. This makes the company's real test less glamorous than the…

North America Cloud Services
Tailscale is tested when the private-network policy change has to be trusted
Tailscale Inc. has made private networking feel simple enough that many teams describe the setup rather than the control problem. The harder question starts after the first machines connect: whether a requested access change grants exactly the right reach, blocks everything else…

North America Cloud Services
Rubrik and the accepted restore test
Rubrik Inc. is not really tested by how many terabytes it protects or how persuasive its cyber-resilience language sounds. The harder denominator is the accepted restore: a recovery that brings the right data, identity state, application order, permissions, and evidence back at…
North America Cloud Services
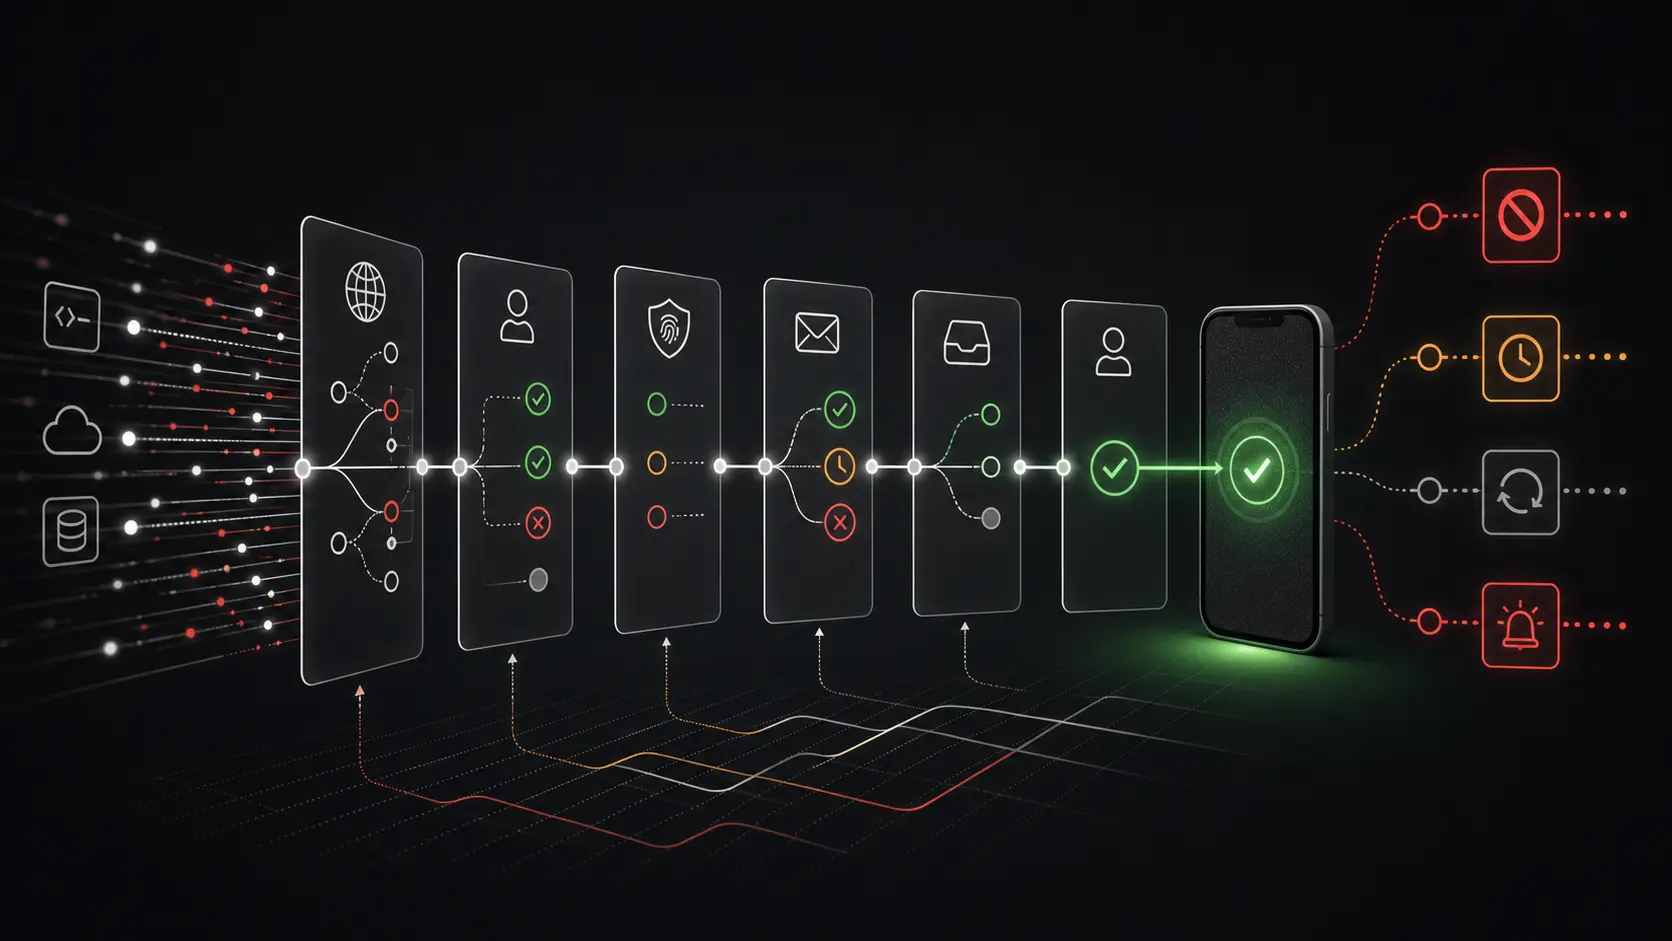
Twilio and the Cost of the Accepted Message
Twilio can make customer communication programmable, but the real unit of value is not a green API response. It is the message, verification or email that survives consent rules, carrier filtering, delivery evidence, fraud pressure and user acceptance at a cost the customer can…

North America Cloud Services
Cloudflare's Edge Control Test Is Whether Every Rule Can Be Reversed
Cloudflare Inc has made a powerful commercial promise out of one operating idea: put traffic, security policy, application code and developer storage close to users, then let teams change that edge layer faster than they could change origin infrastructure. The hard question is…
North America Cloud Services
Zscaler's Zero Trust Test Is Policy Reversal, Not Protected User Count
ZSCALER, INC. has turned zero trust from a security architecture into a large cloud-service operating contract: route work through Zscaler, let identity, device posture, application context and policy decide what is allowed, and replace broad network trust with narrower…

North America Cloud Services
Splunk and the Cost of an Accepted Detection
Splunk's value is not the number of events an enterprise can pour into an index; it is the detection, investigation or operational answer that remains trusted after sources drift, fields break, searches slow down, evidence ages out and analysts still have to decide what happened.