
Topic
Security Automation
Within the Topic facet, Security Automation topic intelligence connects articles that share a specific subject, signal focus, or monitoring theme. The page gives readers a richer path through related reporting, source evidence, market actors, and infrastructure implications, with enough context to understand why the topic matters across company movements, governance decisions, regional exposure, and operational risk. Readers can compare recurring signals, affected organisations, public evidence, market context, service continuity, procurement, competition, compliance, and strategic planning questions behind the subject instead of stopping at a thin list of matching articles. It explains what the topic covers, which infrastructure actors or policies are involved, what evidence supports the coverage, and why the subject may matter for operators, customers, investors, and policy readers.
Story
One Revoked Certificate, Three Browser Outcomes at APNIC 62
The certificate was on the revocation list. That was not the end of the story. Geoff Huston's APNIC 62 demonstration put the same adverse record in front of three browser policies and obtained different results—a useful warning about the distance between publishing a security…

Global Cloud Services Trends
Corero’s 42% revenue growth has a second clock
Corero’s half-year sales and margin improved sharply. Its recurring contract base moved at a different pace, and the revenue table shows why both observations can be true.

IETF
Composite ML-KEM for CMS Cleared the IESG — Its Operational Dependency Chain Did Not
The IETF’s 18 September 2026 approval of `draft-ietf-lamps-cms-composite-kem-03` is an important standards milestone, but it is not the end of the delivery chain. The CMS companion is now in the RFC Editor queue while its normative Composite ML-KEM/X.509 dependency remains under…
IETF
A Batch Receipt Is Not a Security Action: The IETF’s Multi-SET Push Test
An IETF draft would send many security-event tokens in one HTTPS request. Its individual receipts may cut transport cost, but they leave a separate question for every receiving organisation: which event actually changed a local account or credential, and when?

IETF
Two “Not Ready” Reviews Put ACTN’s Packet–Optical Control Boundary on Trial
The IETF’s packet–optical ACTN draft has reached Last Call with an extensive map of controller interactions. Security and operations reviewers now ask what the map cannot settle: who trusts a topology update, and what survives when only one layer completes a change.
IETF
The Last Call Is for the Question, Not the Filter
The IESG has opened a final comment period on how to describe the limits of inter-domain source address validation. The October 1 deadline concerns an Informational problem statement and requirements, not approval of a universal filtering protocol. The distinction matters at the…

History
Version 3 Stayed. The Service Changed: RFC 2126’s Compatibility Trap
An old peer could return a perfectly parseable Class 0 confirmation to a Class 2 request that offered no alternative. The TCP connection was open, the TPKT version was familiar, and the reply was still unacceptable. RFC 2126 made that difference explicit.

CASE FILE
RFC 9647 and the Missing Evidence Chain Between Babel State and Network Behaviour
A Babel route row can report that a path is selected while the operational proof behind that selection remains incomplete: the YANG datastore may show intent, the interface may appear enabled, the neighbour may exist, and the route may be marked feasible, yet the chain from…

IETF
The IESG Cleared Revision 12. The Publication Handoff Is Now on Revision 14
The reviewed entity and the production entity are no longer the same file. That is normal in editorial work, but only if the handoff preserves which judgement applied to which bytes, which comments changed the text, and which authority made each decision. Safe-IOC now offers a…
History
Permission Came Before the Call: RFC 2125’s Two-Stage Bandwidth Decision
Two peers could agree that another line should be tried and still have no new bandwidth. RFC 2125 made that gap explicit: BAP first obtained a response to the proposed action, then a separate Call-Status message reported what happened when somebody actually placed the call.
History
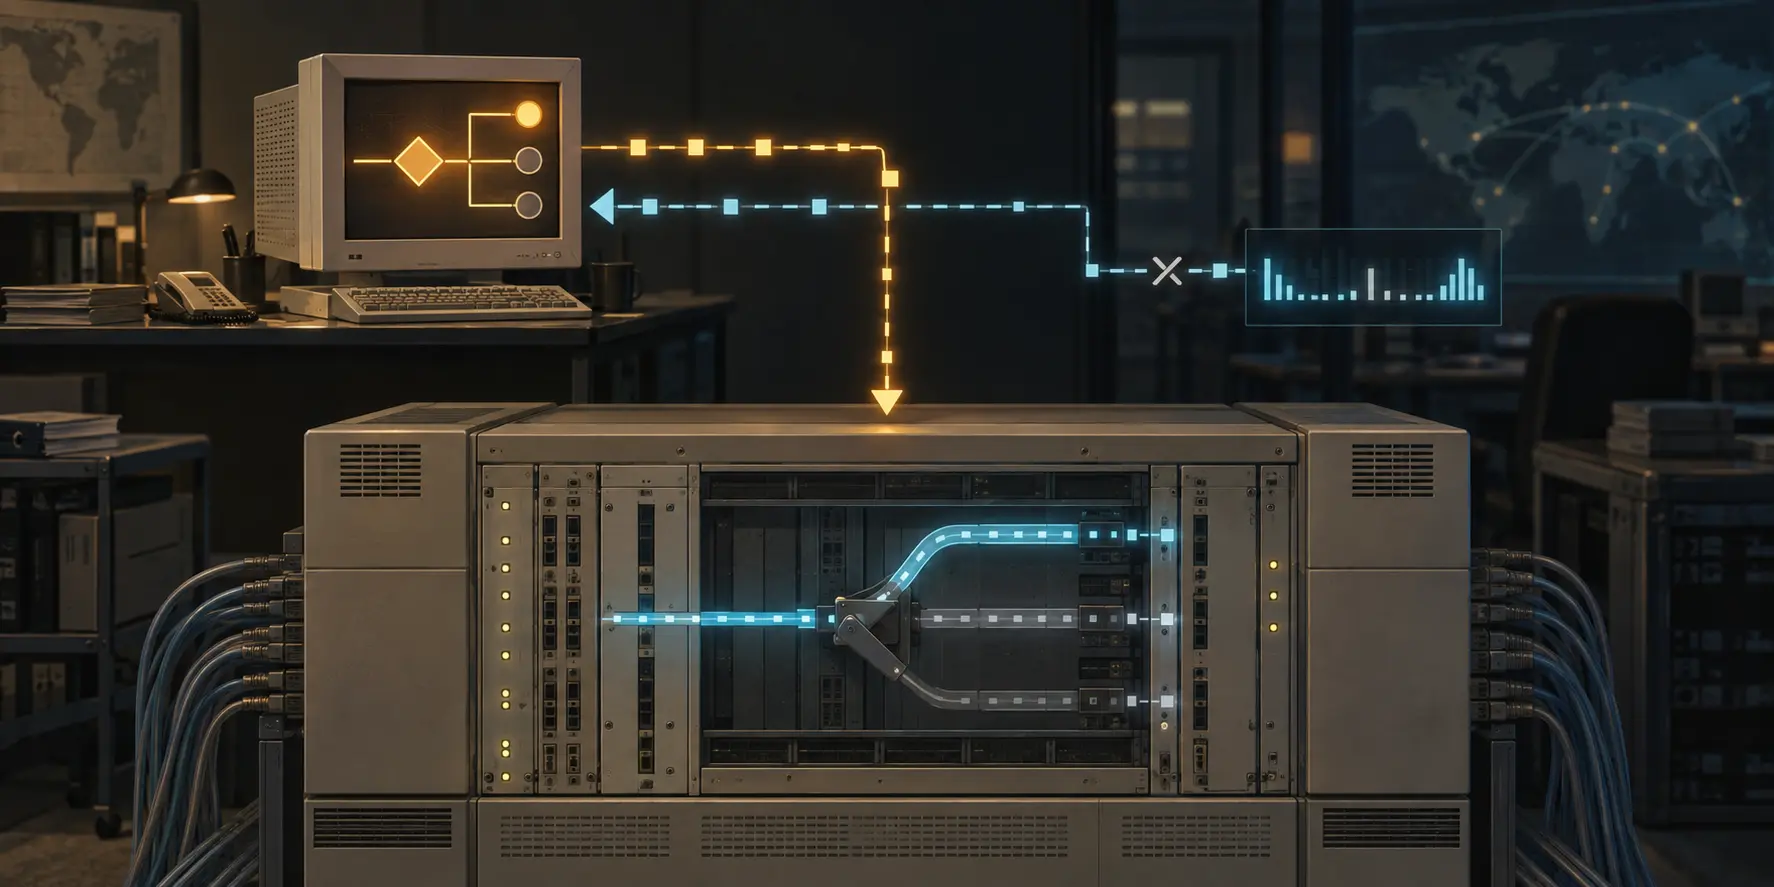
The Verdict Left the FAS. The Switch Still Had to Make It Real
RFC 2124 put connection policy in an external service, but it never made the service’s answer identical to the connection that followed. Its message chain preserved a more useful truth: a decision, an execution and an accounting record are different events.
IETF
When a BGP-SPF Restart Restores Transit Eligibility
A BGP-SPF node can remain reachable for its own services while losing the one signal that kept it out of transit paths. RFC 9815 makes that distinction explicit: omitting Node SPF Status 2 does not declare failure, but it does remove the non-transit constraint. The operational…

Europe and Middle East Cloud Services Trends
PCI Pal’s £27.9m Contracted ARR Is Still Not Audited Revenue
PCI Pal lifted two operating run-rate estimates while postponing the date of its FY26 results. The useful signal is not that one disclosure cancels the other, but that commercial deployment, accounting recognition and audit completion run on separate clocks.

History
The Reset Was in the Next Packet: RFC 2118’s MPPC Recovery
RFC 2118 gave Microsoft Point-to-Point Compression a continuous memory and a deliberately spare recovery signal. When packet loss broke that shared history, the receiver asked for a reset—but it was the sender’s next `FLUSHED` data packet, not a separate Reset-Ack, that…
IETF
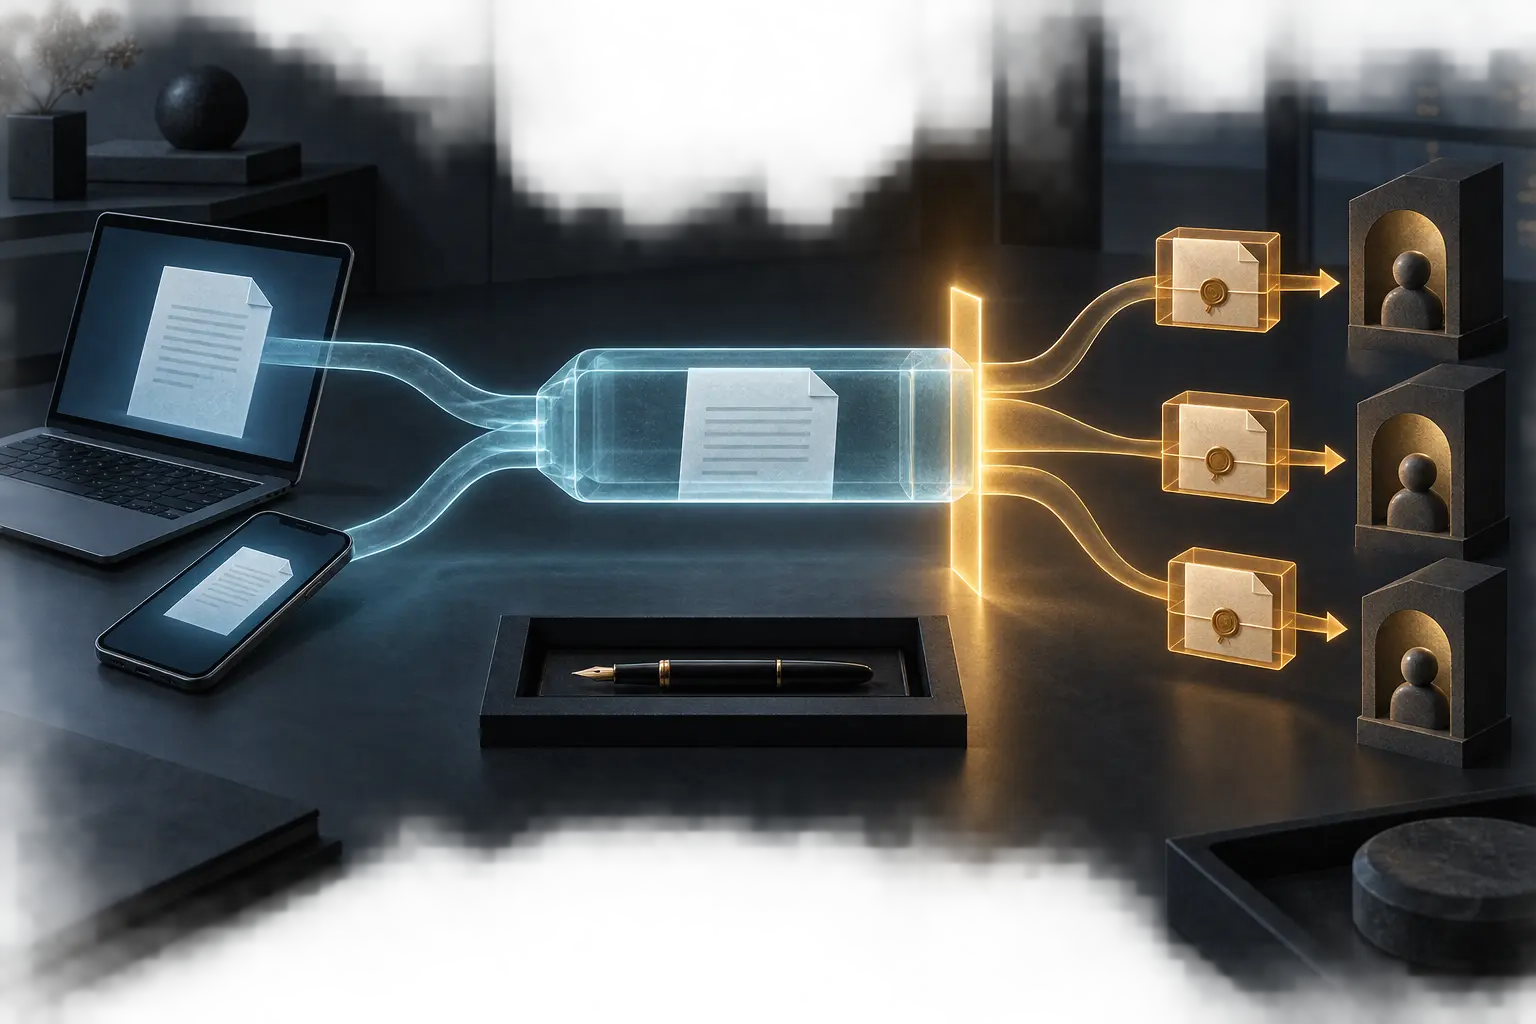
RFC 9787 and the Moment a Draft Becomes a Message: Encryption, Commitment and Cross-Device Custody
A protected email draft is not merely an early copy of a sent message. RFC 9787 treats it as a different authority state: unfinished text may need confidentiality from the mailbox service while remaining unreadable to intended recipients and unendorsed by the user's ordinary…

History
The MIB Located the Address. The Repeater Still Had No MAC
A management station could ask which hub port had carried a source address, rank the busiest ports and reconstruct a shared-Ethernet topology. RFC 2108 made those answers comparable without pretending that the repeater itself understood a packet.

IETF
When Fast Reroute Must Stop: RFC 9791 and the Responsibility Boundary Behind NFFRR
RFC 9791 gives a deceptively simple answer to a hard failure problem: once fast reroute has already redirected a packet, a downstream node may need to refuse another local repair. The difficult part is not the idea of a marker. It is the authority embedded in that marker—the…

CASE FILE
The Grammar Changed. Your Acceptance Boundary Might Not.
RFC 9682 repairs CDDL’s collected grammar and adds a cleaner hexadecimal escape form, but the important compatibility boundary is not the publication date of the RFC. It is the point at which a particular source model meets a particular parser, becomes a particular validator…

History
Two Hash Passes Made a Reusable MAC. The Tag Did Not Make a Trust Decision: RFC 2104
RFC 2104 gave protocol designers a compact way to turn existing iterative hash functions into a message authentication code: one keyed inner pass, one differently keyed outer pass, and an interface that could survive replacement of the hash beneath it. What endured was the…

IETF
When “Lease” Stops Meaning “Address Assigned”
An operator upgrades a DHCPv6 inventory schema and discovers that one familiar dashboard label—“lease”—now conceals two different origins of authority. In one record, the server selected or delegated the resource. In another, the device selected a SLAAC or static address and…