
Topic
Security Automation
Within the Topic facet, Security Automation topic intelligence connects articles that share a specific subject, signal focus, or monitoring theme. The page gives readers a richer path through related reporting, source evidence, market actors, and infrastructure implications, with enough context to understand why the topic matters across company movements, governance decisions, regional exposure, and operational risk. Readers can compare recurring signals, affected organisations, public evidence, market context, service continuity, procurement, competition, compliance, and strategic planning questions behind the subject instead of stopping at a thin list of matching articles. It explains what the topic covers, which infrastructure actors or policies are involved, what evidence supports the coverage, and why the subject may matter for operators, customers, investors, and policy readers.
North America Institutional Trends
EigenQ’s $45 million headline buys a conditional commercialisation clock
The quantum-security company has not received a $45 million operating cheque. Its filed financing is a two-stage, discounted and secured bridge in which cash, closing risk, dilution and collateral must be reconciled before the valuation story can be judged.
IETF
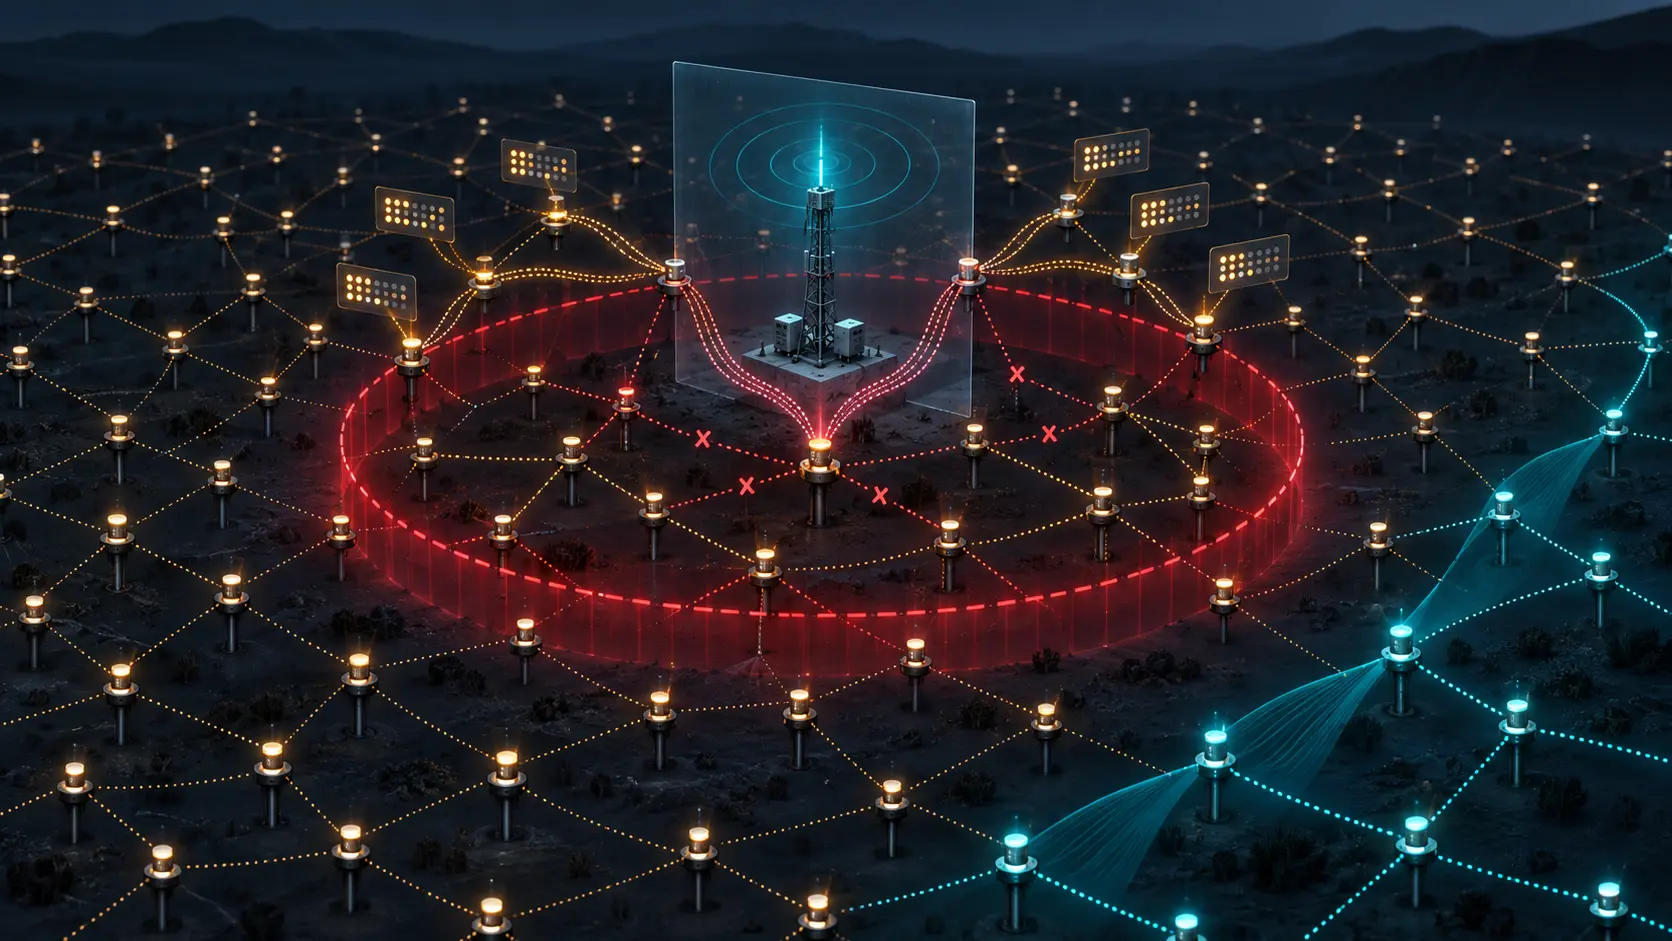
The Network Agreed the Root Was Down. It Did Not Prove a Crash: RFC 9866
RFC 9866 lets a low-power network reach a coordinated decision that its current routing root is no longer usable. The decision can be operationally correct even when the root is still powered and the physical cause is unknown. Treating `GLOBALLY DOWN` as a forensic verdict would…

IETF
The Hash Looked Expensive. The Login Fleet Had Not Been Measured
RFC 9106 makes Argon2id's memory, passes and lanes explicit. That is the start of an engineering decision, not evidence that a verifier can carry its real login load or that a stolen hash will cost an attacker what the defender imagines.

IETF
The Dialog Continued. The Authority Did Not Travel With the Identifier
Agentproto's proposed dialog context can keep one interaction legible across agents, tools, networks and interruptions. That continuity is operationally valuable precisely because it is narrow: a shared identifier can correlate a dialog without proving who was entitled to act…

IETF
The Link Colour Arrived. The Policy Decision Did Not: RFC 9104
A controller can receive a perfectly formed Extended Administrative Group through BGP-LS and still lack the evidence needed to say what the bits mean, which policy used them, which path won or what happened to traffic. RFC 9104 standardises carriage across that boundary—not the…

History
The Green Tunnel Light Is Not a Service Receipt: Reading RFC 2341 Precisely
An operations screen can show a tunnel as open while the user's application is still waiting. RFC 2341 makes that gap unusually easy to see. Its Layer Two Forwarding protocol coordinates a tunnel between an access provider's Network Access Server and a Home Gateway, then carries…

IETF
SIMAP Can Trace a Service to Its Hardware. That Does Not Make the Map the Network
Revision 13 gives network software a common way to walk from a service through logical layers to physical resources and back again. The result can be operationally valuable without being a certificate that the graph is complete, current or authorised to act.

IETF
The Transfer Was Encrypted. The Zone Still Needed a Custodian: RFC 9103
Encrypting AXFR or IXFR removes a powerful observer from the path: anyone who could read the transfer in cleartext. RFC 9103 makes that result precise—and, just as importantly, leaves authorization, replica custody and the rest of the DNS exposure surface as separate questions.

IETF
The Backup Nameserver Answered. The Cached Key Did Not Fit: RFC 8901
A second authoritative DNS provider can keep answering after the first one fails and still leave validating resolvers without an acceptable answer. RFC 8901 shows why DNSSEC redundancy is a synchronization contract across signers, not a count of nameservers.

History
The Alias Reached the Child Zone. Nothing Else Was Proven: RFC 2317
A reverse query for one address can cross two administrative boundaries before it returns a name. RFC 2317 made that path possible for IPv4 blocks smaller than a /24, but the records along the path remain narrow receipts: they show how DNS reached a PTR answer, not who owns the…

History
The Association Was Mature. The Security Result Was Not: RFC 2367
A diagnostic console shows an IPsec Security Association in the `MATURE` state. Its SPI, algorithms, addresses and lifetime are all present. That is useful evidence—but only of what one local Key Engine reported. RFC 2367 drew the interface boundary clearly enough to show why the…

CASE FILE
The resolver address was not the resolver
APNIC Labs added a second dual-stack authoritative nameserver and watched average queries per test fall from 3.43 to 2.57. The experiment did not reveal a cause. It revealed something more operationally awkward: a public recursive-resolver address is often a routing handle, not a…
IETF
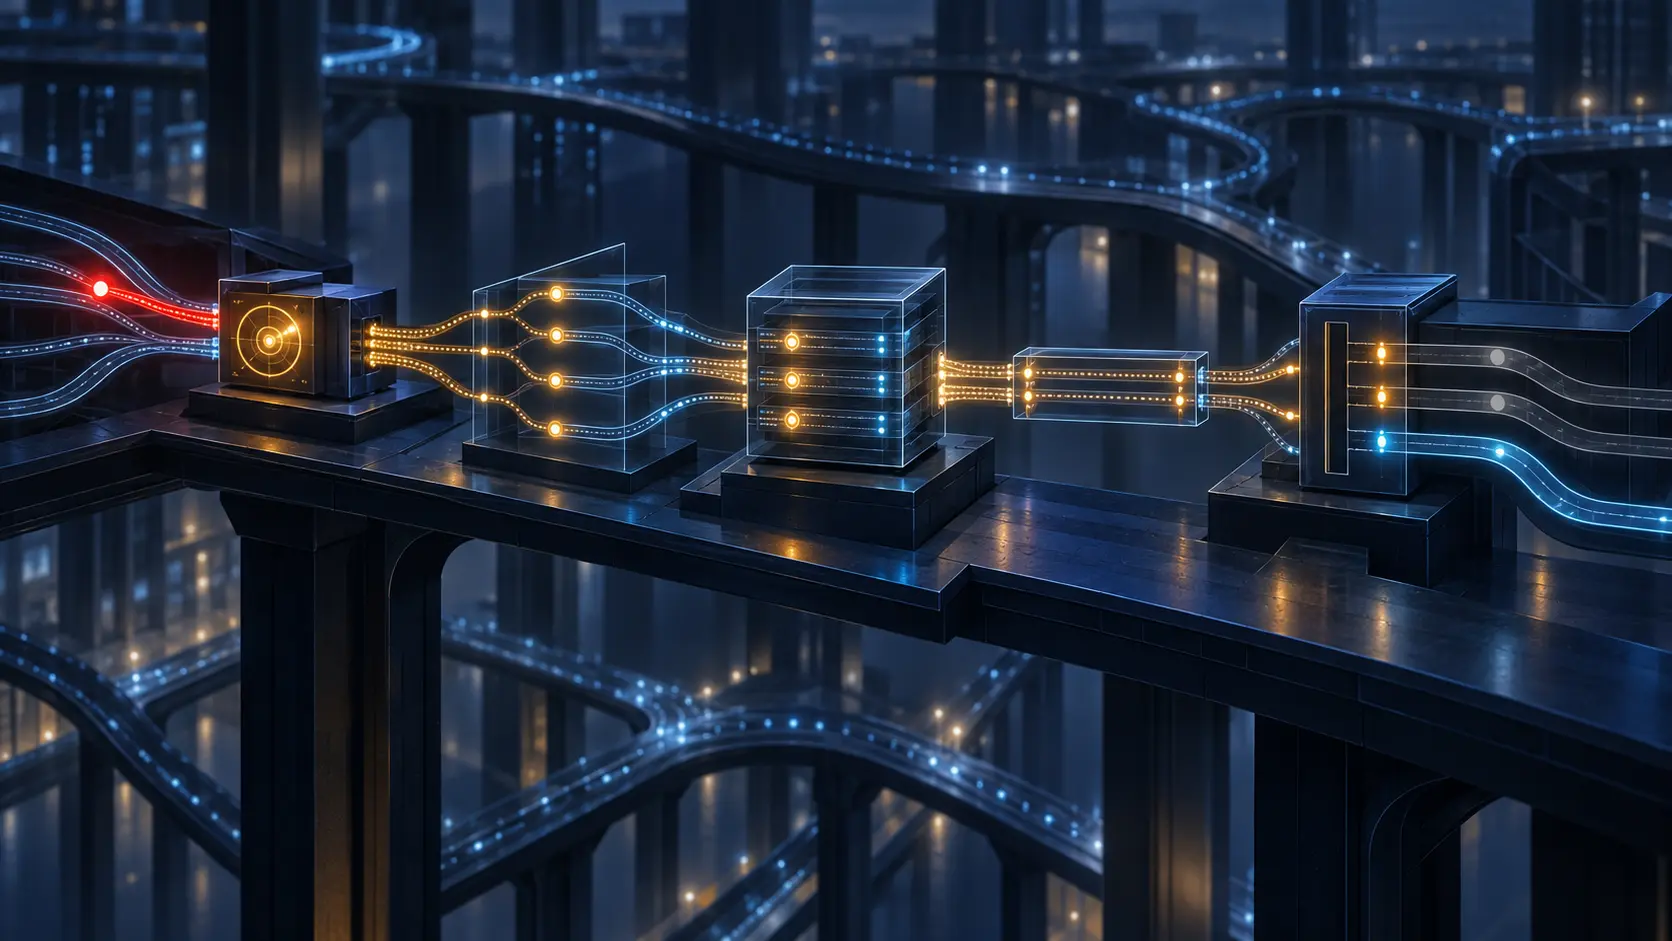
When One Bad Route Becomes Everyone Else’s Risk: The Authority Question in BGP DRIP
A router sees one suspect announcement. Minutes later, routes that were never themselves invalid have lost preference because they share an origin, a neighbour or an AS-path pattern. That is the consequential idea inside the first BGP DRIP draft: not simply faster warning, but a…

History
The Backup Route’s Invoice
A second Internet provider promised resilience, but the extra route appeared only after the first path failed. RFC 2260’s enduring insight was that multihoming never removed the bill for reachability; it decided whether that bill would be paid in global routing state, provider…

IETF
A 202 batch is not a receipt for every security event
The final day of IETF Last Call for HTTP Multi-SET Push sharpens a deceptively simple operational question: when one request carries many security events, what exactly has a successful HTTP response proved?

IETF
The P Flag Is a Trigger, Not Proof of a Complete Path
MPLS PBT-M asks a marked packet to solicit postcards from capable nodes. Its small wire footprint is useful precisely because most of the proof lives elsewhere: in node configuration, export records, loss counters and a collector that can say what is missing.

IETF
One Bearer Token, One Audience: WIMSE Revision 07 Draws the Receiver Boundary
An external identity provider that accepts the same bearer token as a Kubernetes API server does not merely validate the workload. It acquires a credential it can present back to the API server as that workload. Revision 07 of the WIMSE practices draft turns the separation of…

CASE FILE
The SYN Could Be Actionable Before the Application Had a Receipt: RFC 1644
RFC 1644 asked a server to make an unusually consequential decision at the first packet: if a connection count in a SYN was newer than the value remembered for that client, the request data could be delivered immediately. That accelerated a transport exchange. It did not tell…

IETF
An ACME profile name can open an order. It cannot promise a certificate
The same profile name can be visible in a CA’s Directory today, accepted under a private arrangement while absent from that Directory, or rejected when an already-created order reaches finalization. That flexibility makes profile selection explicit; it also makes the surrounding…
IETF
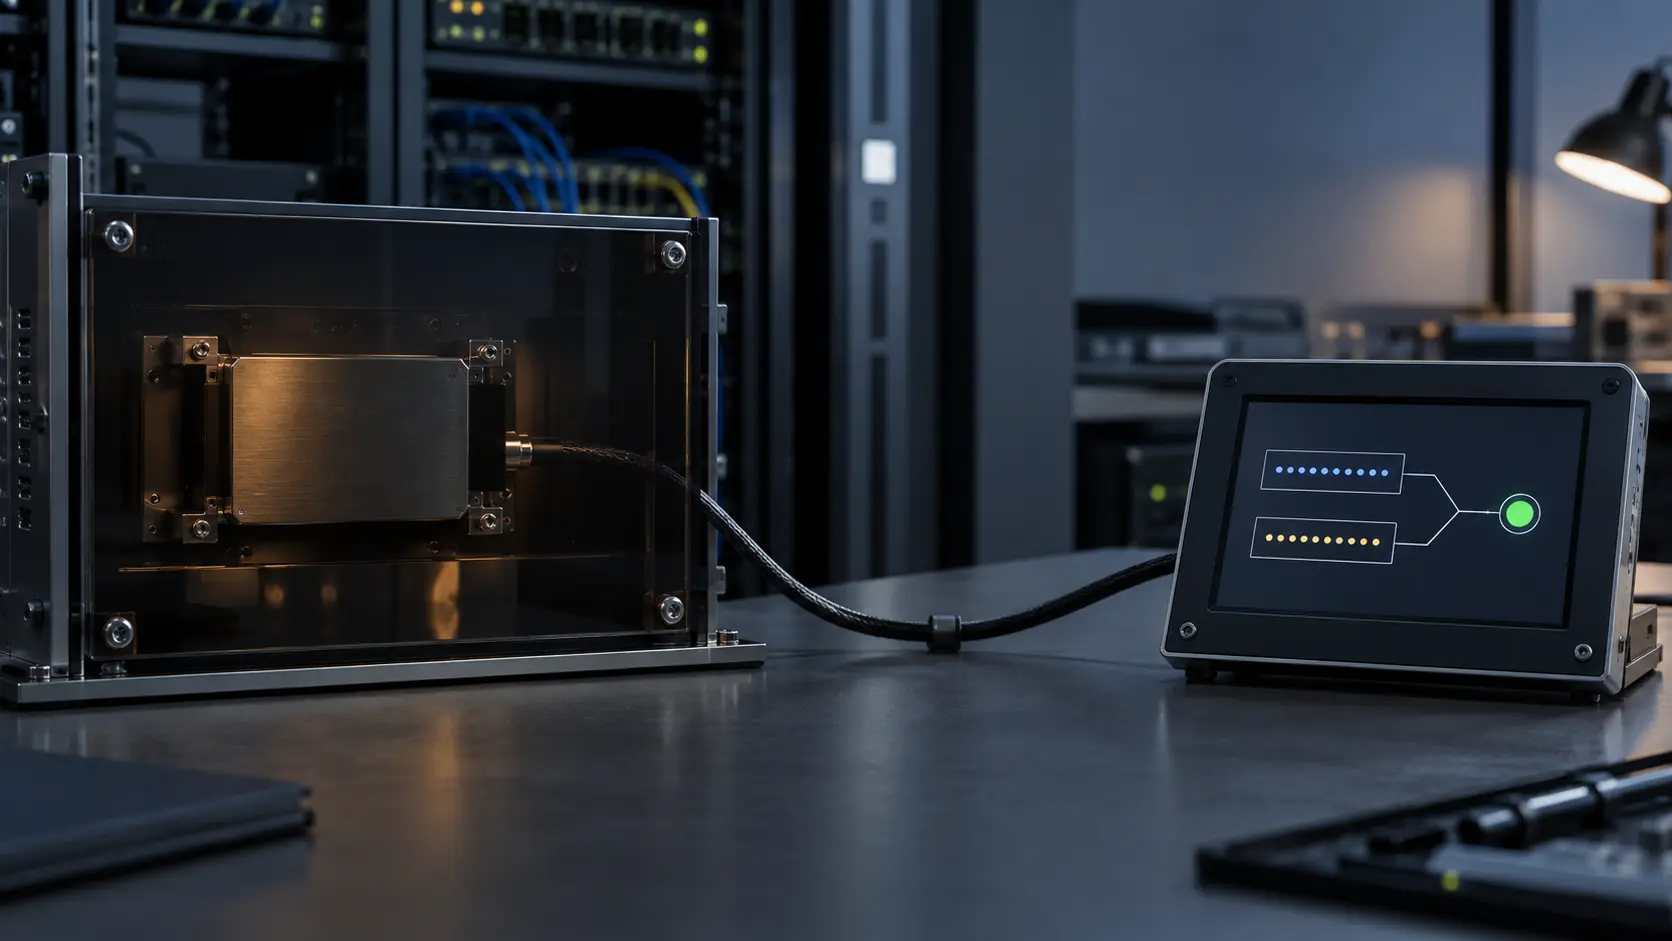
Babel’s Hidden Key and the Authority Behind a Boolean Answer
An operator barred from reading a Babel MAC key may still, with effective authorisation, ask the device to use it in a local comparison. That separation can support maintenance without distributing secret material. It also requires a decision about who controls the test and how…