
Topic
Network-resource Evidence
Within the Topic facet, Network-resource Evidence topic intelligence connects articles that share a specific subject, signal focus, or monitoring theme. The page gives readers a richer path through related reporting, source evidence, market actors, and infrastructure implications, with enough context to understand why the topic matters across company movements, governance decisions, regional exposure, and operational risk. Readers can compare recurring signals, affected organisations, public evidence, market context, service continuity, procurement, competition, compliance, and strategic planning questions behind the subject instead of stopping at a thin list of matching articles. It explains what the topic covers, which infrastructure actors or policies are involved, what evidence supports the coverage, and why the subject may matter for operators, customers, investors, and policy readers.
Story
LACNIC and the economics of ICP-2 reform
The rule for recognising an Internet registry is also a rule about who must bear the cost of proving that institutional change is safe. LACNIC makes that trade-off unusually visible: regional legitimacy is built through members and an open policy process, while recognition…

History
The Birth Record That Could Outlive the Group: How ACTIVE.TIMES Separated Provenance from Availability
One list says a newsgroup can be selected now but remembers nothing about its beginning. Another preserves a group's local creation record after that group has disappeared from the selectable catalogue. NNTP made both answers valid on the same server. The apparent contradiction…

History
The Write That Returned Before It Was Safe
The server had returned success, yet the client was not free to discard the bytes. They might exist only in memory that the next restart would erase. NFS version 3 made that interval explicit, then attached a narrow piece of evidence to it: a write verifier that could tell the…
Story
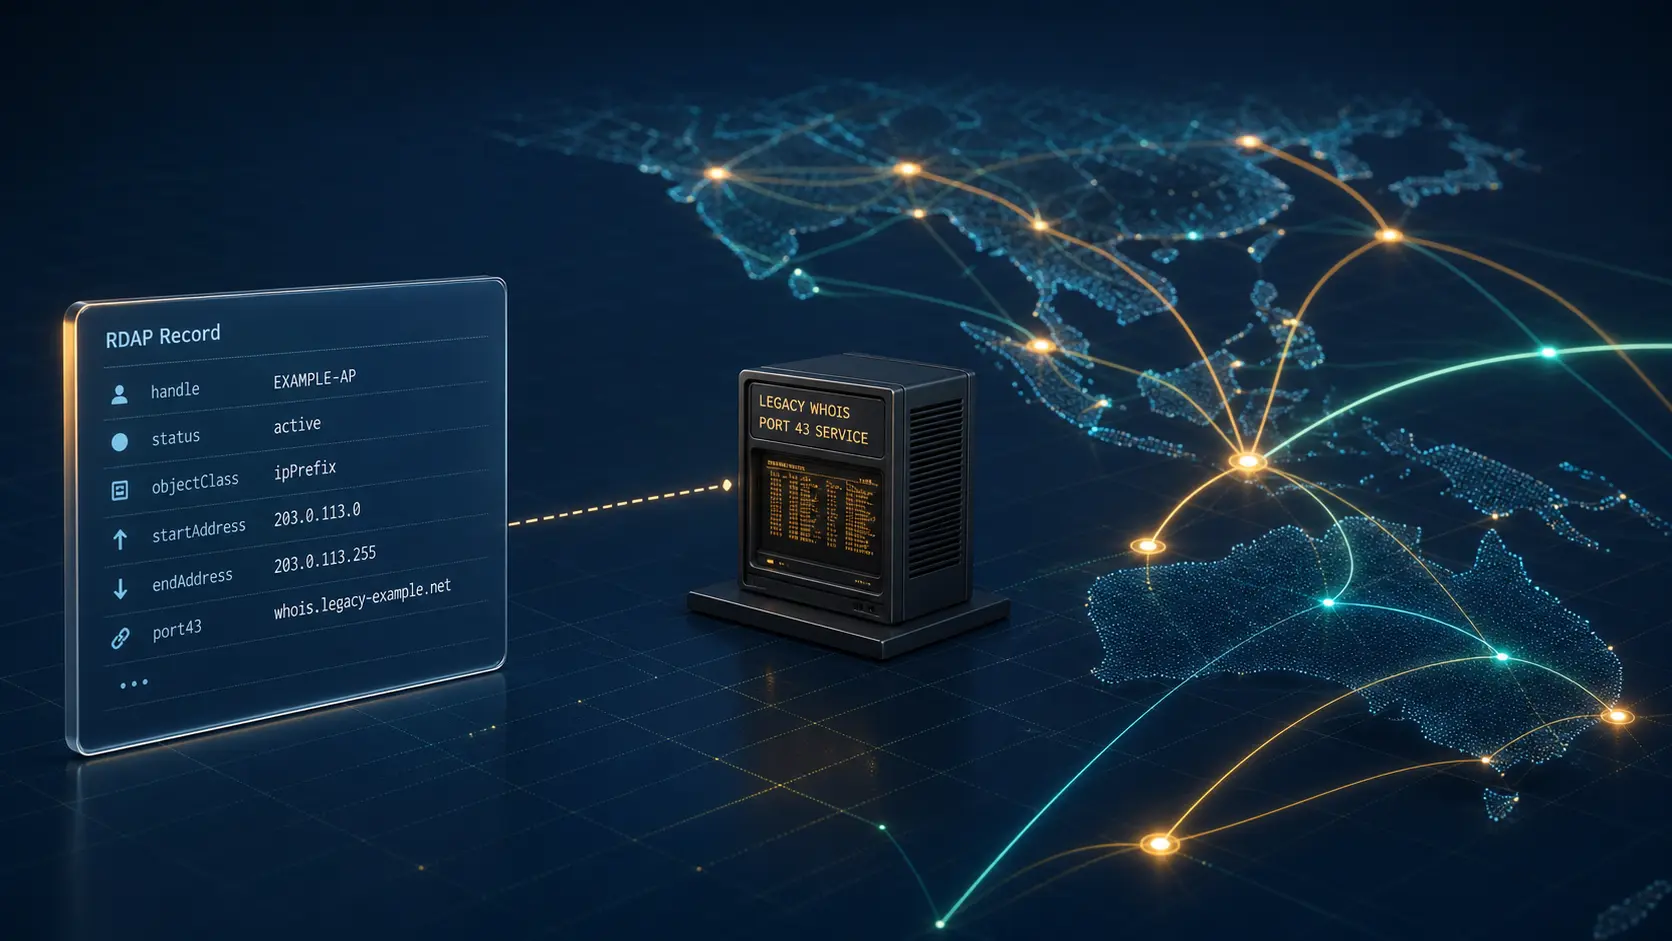
APNIC's RDAP port43 Points to a Legacy WHOIS Service, Not Network Authority
In a live APNIC RDAP record, `port43` names `whois.apnic.net`. That is useful evidence about where to query the legacy registration service—but it is not a statement about who operates, routes or controls the addressed network.
CASE FILE
The Route Said Valid. The Evidence Was Local.
One RPKI service fails. A customer network changes its view a second before its provider; the provider changes next, about five minutes later. If both networks export validation results as route attributes, one dependency failure becomes two waves of BGP UPDATEs. Nothing about…
History
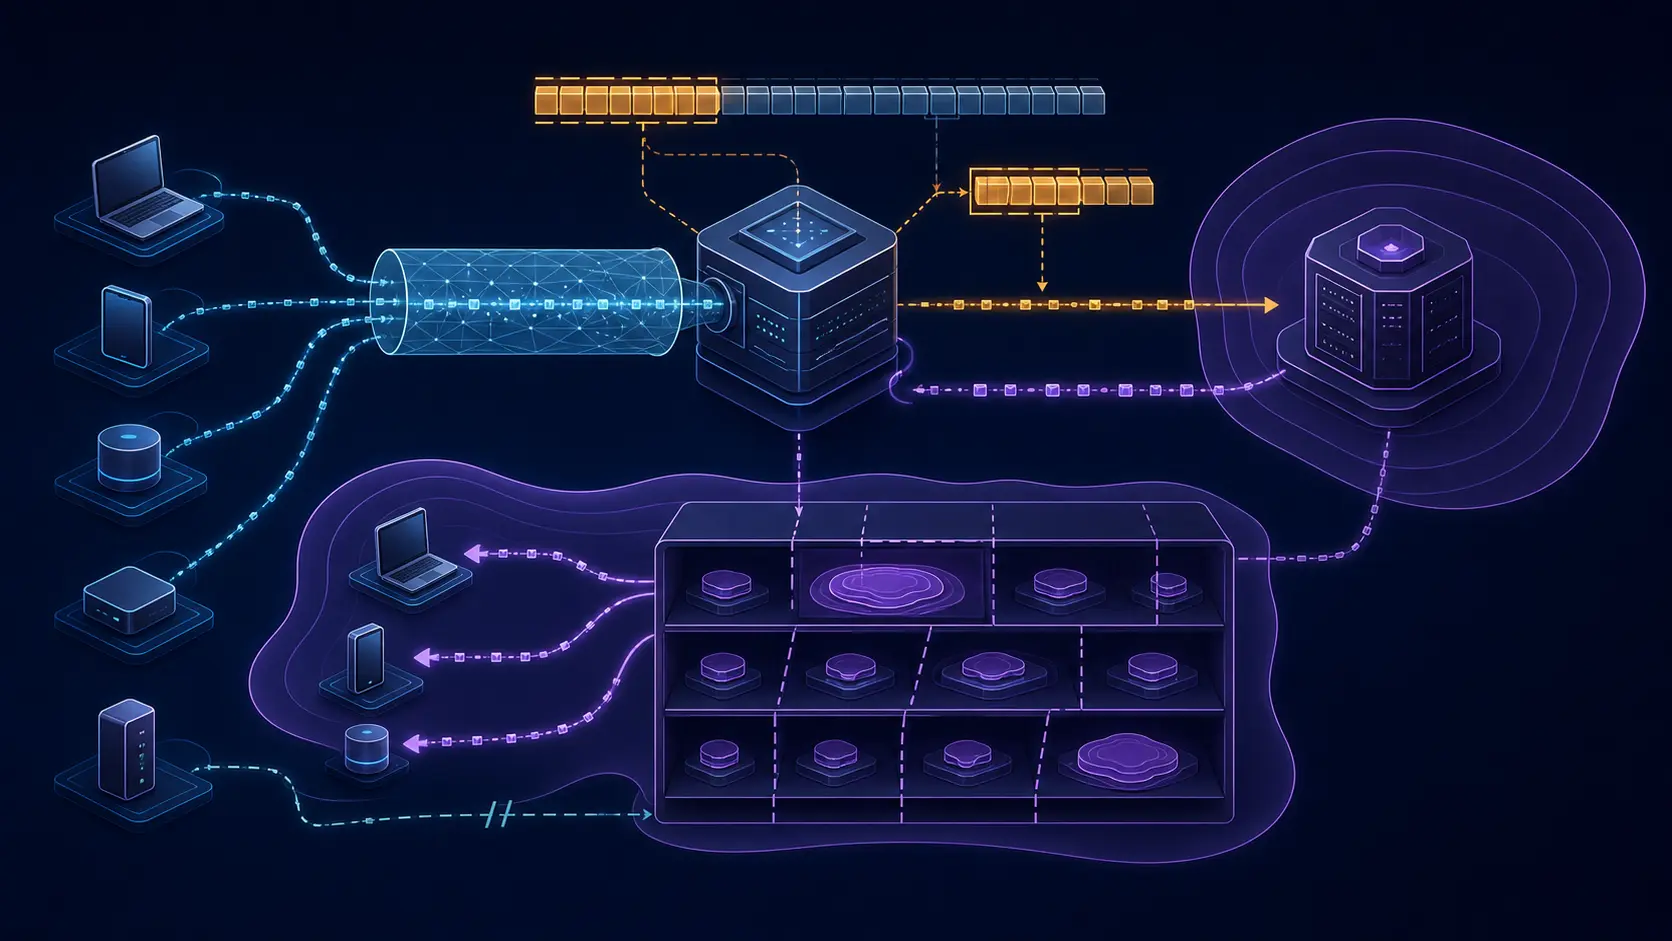
The Prefix the Resolver Sent on Someone Else’s Behalf: EDNS Client Subnet
A recursive resolver usually speaks to an authoritative server from its own address. EDNS Client Subnet changed the message: the resolver could send part of a client's network instead, asking the authority to tailor an answer for someone who had not made that upstream query. The…

Europe and Middle East Regional ISP Trends
SeaTelecom Nord-West’s shared routing boundary complicates customer continuity claims
SeaTelecom Nord-West’s shared routing boundary complicates customer continuity claims intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences…
CASE FILE
The signed chain skipped a delegation that still existed
NSEC3 Opt-Out allows a large parent zone to leave eligible insecure delegations out of its signed hash chain. That omission can be fully valid. It is also why the chain cannot serve as a complete delegation register: the proof authenticates a limited statement about a hash…

History
The Layer That Had to Come Last: How NNTP Compression Turned Order into Security
Two clients want the same three things: an encrypted channel, an authenticated account and fewer bytes on the wire. One asks for compression first. The server replies `206`, and two doors close: this connection can no longer begin TLS or accept `AUTHINFO`. The other client…
Story
A Private Registry Still Needs Public Limits
LACNIC is private infrastructure governance with public consequences: legitimacy depends on a bounded mandate, published rules, evidence, review and an operational record that affected networks can understand.

History
The Reservation That Might Reserve Nothing
Before sending a file, an FTP client could announce how much storage it expected to need. The server might answer `202`, a positive completion, while setting aside no space at all: advance allocation was superfluous on that system. The exchange let unlike machines keep working…

IETF
BGP Maintenance Needs Two Different Meanings of Graceful
Two change tickets can both say “graceful” while asking the network to do opposite things. One must move traffic away before a link or router stops forwarding. The other must keep forwarding on existing entries while the BGP control plane restarts. Treating those operations as…
History
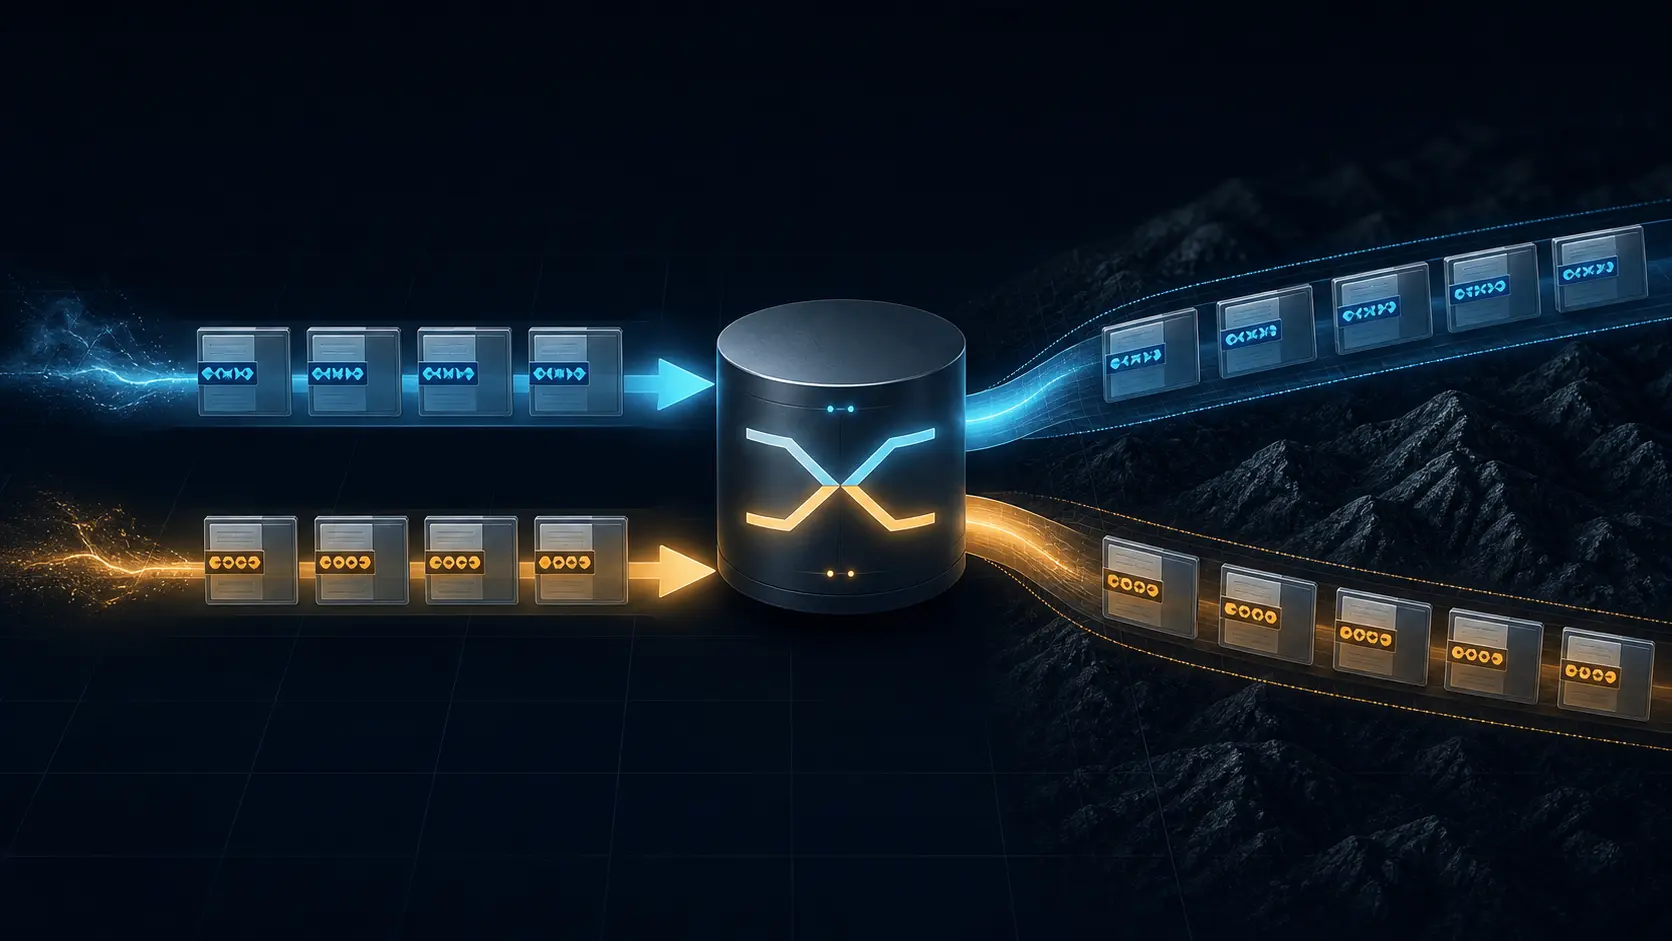
The Label Routers Could Read Without Knowing the Flow: IPv6 Flow Labels
Two encrypted flows can cross the same IPv6 tunnel with the same outer source and destination addresses. To a router that will not—or cannot—inspect transport headers, they may look identical. The Flow Label offers a deliberately narrow alternative: twenty visible bits in a fixed…
History
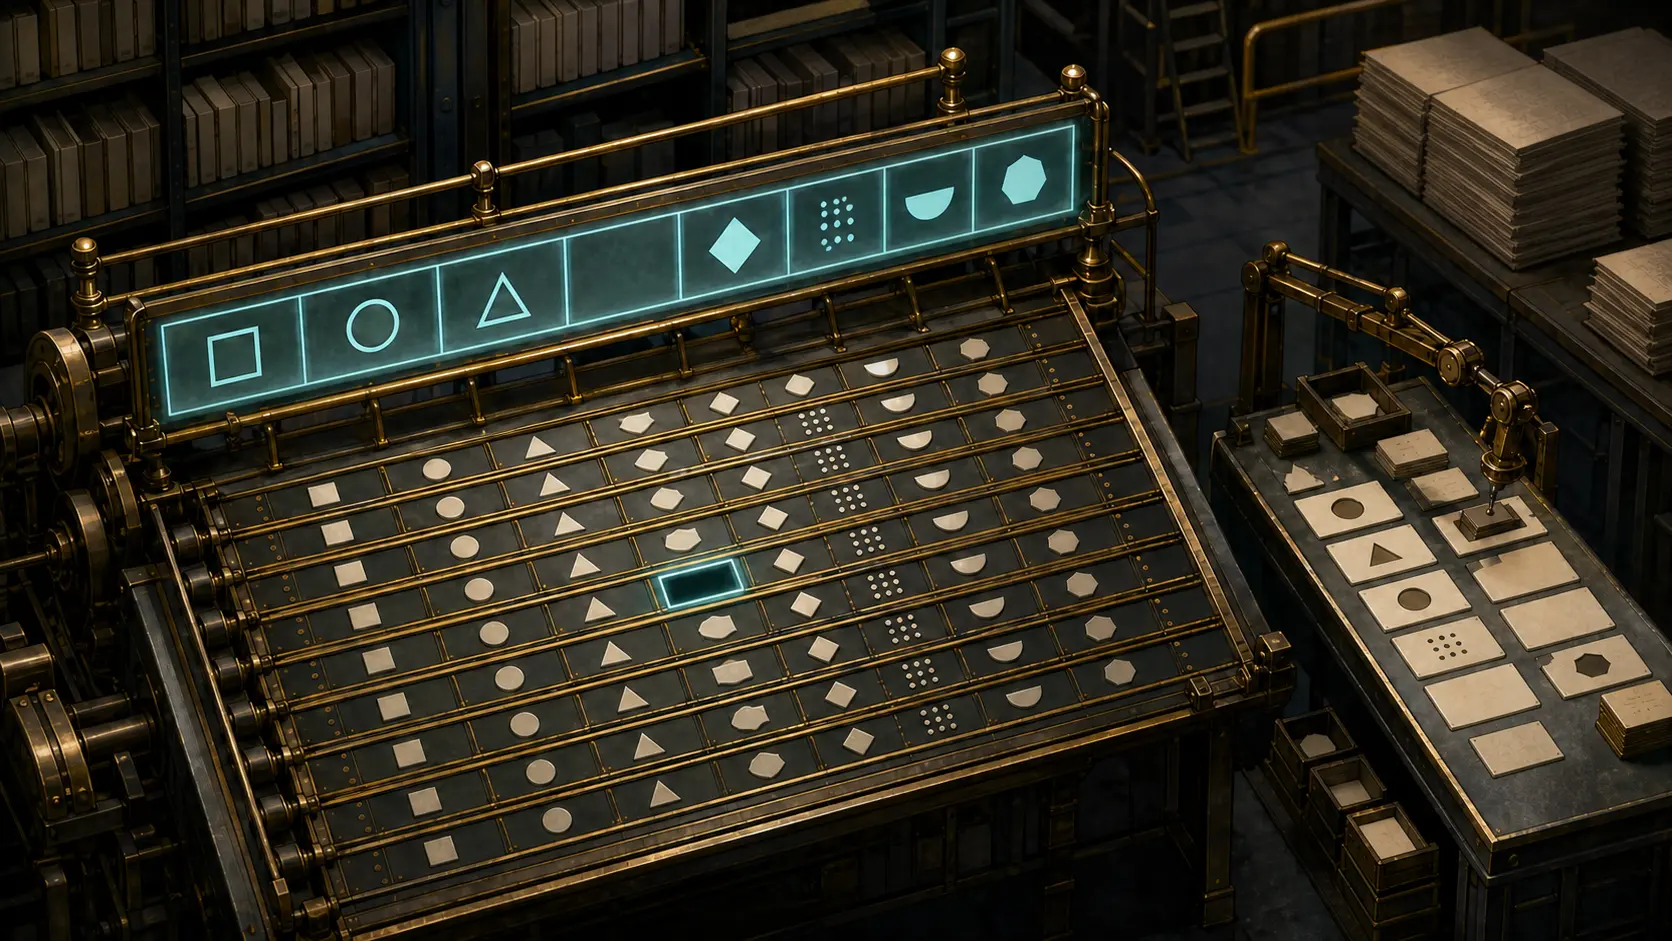
The Blank Field That Had to Be Earned: How NNTP Overview Made Absence Trustworthy
A newsreader receives a tab-separated summary of hundreds of articles. In one row, two tabs touch. Does that blank mean the article lacked a header, or only that the server never indexed it? NNTP could make bulk browsing fast only by answering that question. Its overview format…
Story
A Court Order Is Not a Registry Runbook
A court can determine rights and impose duties. It does not thereby describe every safe registry, credential and routing step. LACNIC needs a disciplined bridge from legal command to operational execution.
Story
LACNIC’s 11 IXP Collectors Need a Vantage-Point Receipt
LACNIC has opened a useful window onto local routing: eleven BGP collector views, public MRT files and charts of prefixes, origin networks and paths. The problem begins only when a window is mistaken for the landscape. The portal does not bind each result to the peer cohort…

History
The Timestamp Saved Before the Search: How NEWNEWS Chose Duplicates Over Missing Articles
A news reader asks a server what arrived since its last visit. The obvious bookkeeping move is to save the time when the answer comes back. It is also the dangerous one. An article can arrive while the server is searching: too late for the current result, yet earlier than the…

History
The Relay That Added Context by Cutting Off the Message
A nearly full syslog packet arrived without a recognizable timestamp. To make the record usable, the relay had to prepend its own local time and, if it could, the name by which it knew the sending device. The envelope did not grow with the explanation. At 1,024 bytes, the new…
CASE FILE
The files matched. The authority did not
An RPKI Signed Checklist can bind exact file bytes to a declared set of Internet Number Resources. That is a useful and unusually precise proof. It is also much narrower than the green result can appear: the entity does not identify a company, certify a document's truth, prove a…
IETF
Clarence Filsfils and the Segment List That Learned to Share an Address
An SRv6 path can be perfectly explicit and still carry waste: the same locator block repeated across instruction after instruction, plus zero padding that moves through the network without adding a decision. RFC 9800 removes that repetition. Its deeper achievement is to specify…