
Topic
Institutional Legitimacy
Within the Topic facet, Institutional Legitimacy topic intelligence connects articles that share a specific subject, signal focus, or monitoring theme. The page gives readers a richer path through related reporting, source evidence, market actors, and infrastructure implications, with enough context to understand why the topic matters across company movements, governance decisions, regional exposure, and operational risk. Readers can compare recurring signals, affected organisations, public evidence, market context, service continuity, procurement, competition, compliance, and strategic planning questions behind the subject instead of stopping at a thin list of matching articles. It explains what the topic covers, which infrastructure actors or policies are involved, what evidence supports the coverage, and why the subject may matter for operators, customers, investors, and policy readers.

History
The Old Address Fit Inside IPv6. Its Routing Model Did Not: RFC 1888
A twenty-octet address can be placed beside a sixteen-octet one, sliced, tagged and reconstructed. That arithmetic says nothing about whether the route hierarchy survives the move. RFC 1888 recorded this distinction in 1996: its encodings could preserve address bits, while the…
CASE FILE
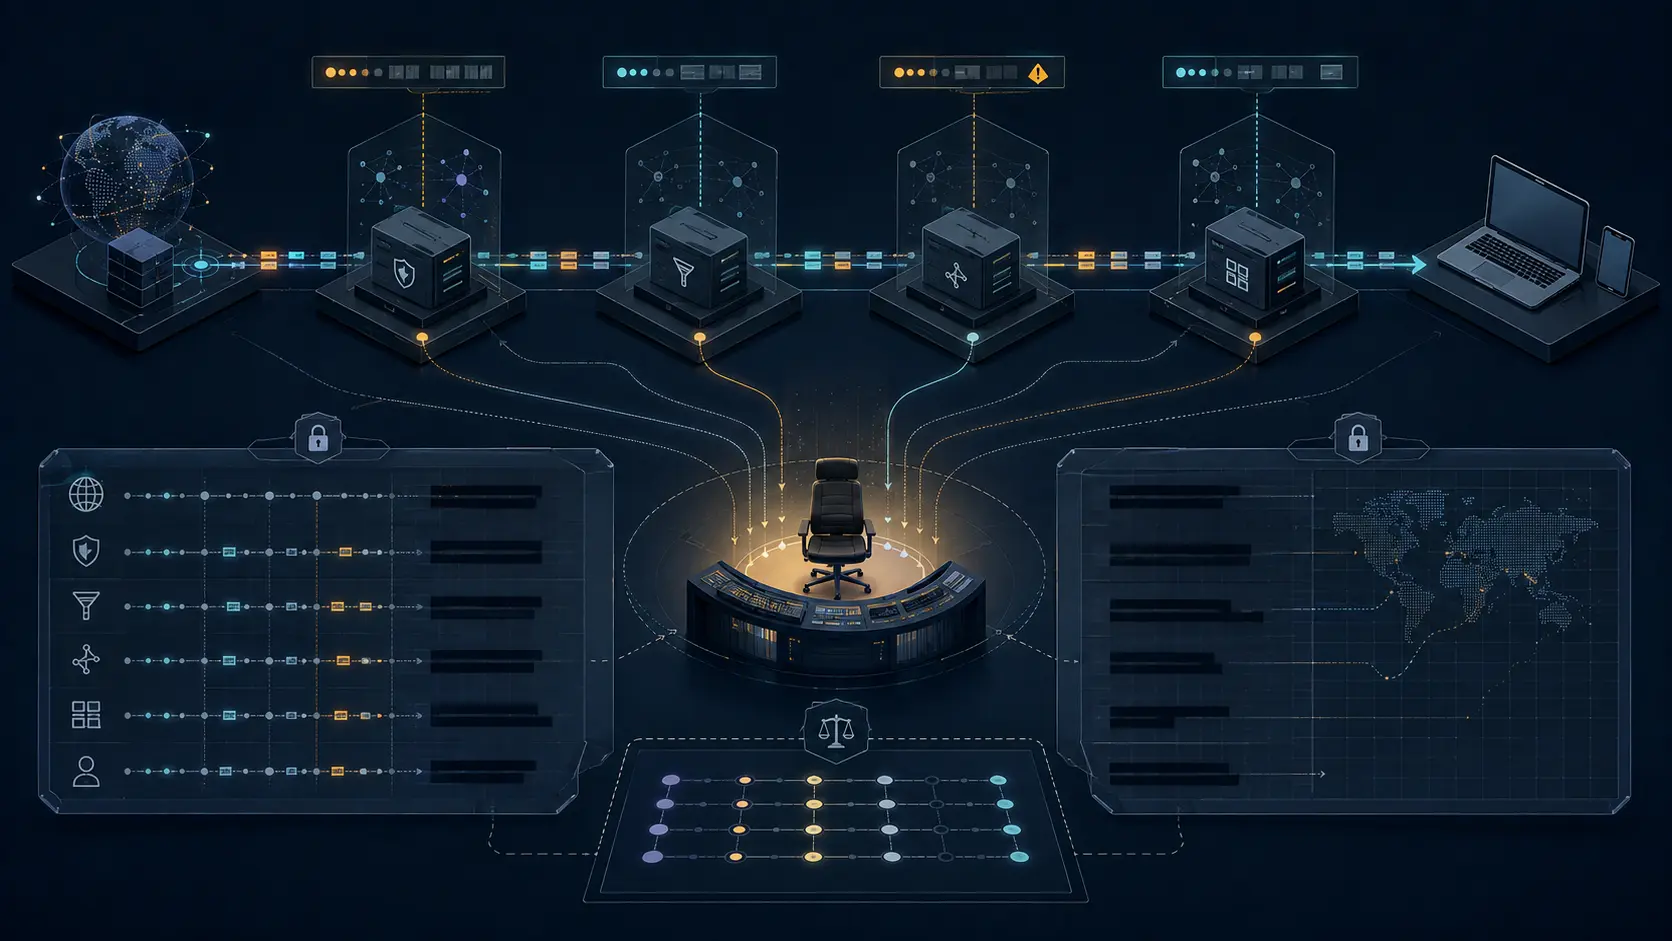
A Proxy-Status Chain Does Not Name the Incident Owner
RFC 9209 can make a failure path legible without making anyone accountable for repairing it. The missing entity is an intermediary fault-handoff matrix: a private governance record that connects each visible or redacted hop to an operator, an escalation clock, retained evidence…

Story
ARIN Adopted an Amended IPv6 Task Force Charter. The Public Index Does Not Show It
ARIN’s Board minutes record the creation of an IPv6 Task Force, an amendment that shortened its planned life, and three people who volunteered to do the work. What the public record does not yet supply is the operative text that joins those facts into a mandate. The missing…
History
The Test Address Came With Its Eviction Notice: RFC 1897 and the 6bone
In 1996, an IPv6 address could be useful, globally coordinated and routable across an experimental backbone while still carrying no promise of permanence. RFC 1897 made that distinction explicit: its addresses were for prototype testing, would be reclaimed and required their…
CASE FILE
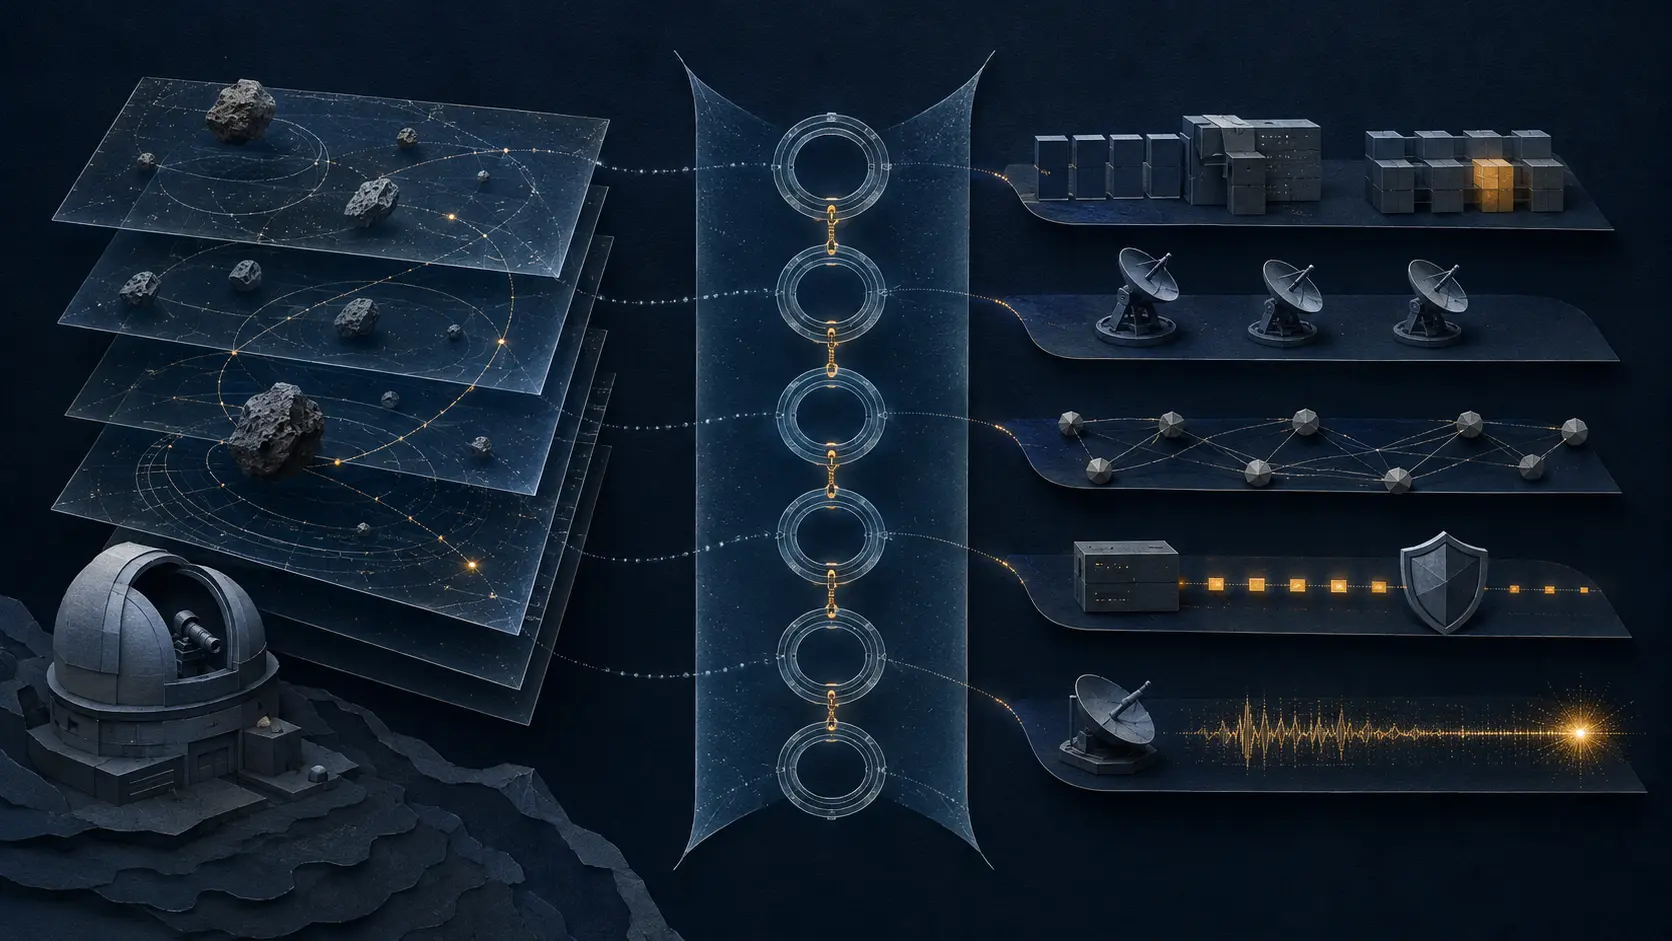
A Celestial Name Is Not a Network Address: The Authority Split TIPTOP Has to Preserve
One entity can be discovered under a temporary tag, receive several provisional designations, gain a permanent number and acquire a name years later. A route cannot afford to mistake any one of those labels for proof of where a packet should go.
CASE FILE
A Deprecation Date Is Not a Client Migration Plan
The response is still `200 OK`, but it now carries a date after which the resource will be deprecated. That date can warn a client. It cannot identify who owns the client, whether a replacement preserves its assumptions, or what must be true before the old endpoint can be…

NANOG
The Mailing List Is an Operations Room, Not a Legislature
NANOG's mailing list is valuable because operators can expose a fault, compare evidence and correct a diagnosis in public. That practical authority should not be confused with permission to speak for networks whose operators did not join the thread.
CASE FILE
A security.txt File Needs a Live Disclosure-Channel Receipt
The `Expires` line says the coordinates are still publishable. It cannot tell a researcher whether anybody is listening. That gap between a fresh file and a working response operation is where a small disclosure-channel receipt becomes useful.

CASE FILE
The Message Was Encrypted. Its Headers Still Needed Their Own Receipts: RFC 9788
An encrypted-mail badge compresses a complicated evidence chain into one reassuring symbol. RFC 9788 shows why the symbol cannot answer which header was hidden, which sender identity was authenticated, what an intermediary changed, or where a reply may safely go.
IETF
VIRP Moves Write Authority Outside the Gate, but Its One-Use Grant Is Still Unbuilt
Revision 07 of VIRP proposes a sharper control boundary for autonomous network operations: the automation gate keeps a read-only device identity, while a separate service decides whether any write may proceed. That is a real change in where authority sits. It is not yet the…

CASE FILE
An OSPS Baseline Claim Needs a Version, a Level and a Date
“OSPS compliant” looks tidy in a supplier register. It is also incomplete. The Baseline is versioned, divided by project maturity and explicitly assessed at a point in time; a useful claim must preserve those coordinates and the evidence behind them.

CASE FILE
A CA Audit Is Not a Certificate-Issuance Verdict
An annual assurance report can show that a certificate authority’s controls were examined over a bounded period. It cannot, on its own, answer the smaller and more consequential question a relying party often needs to ask: why was this exact certificate for this exact name and…
History
The Message Reached the Partner’s System. The Transaction Had Not Been Accepted: RFC 1865
A purchase order can cross the Internet without crossing the final boundary that matters. In 1996, RFC 1865 described a dedicated SMTP connection delivering EDI directly to a trading partner’s system and called that delivery assured. The phrase was useful at the transport layer…

CASE FILE
A GitHub Actions workflow_run Trigger Is Not an Artifact-Trust Verdict
A GitHub Actions `workflow_run` trigger can create a useful separation between an upstream check and a downstream, more privileged workflow. It does not establish that the upstream result, the artifact consumed downstream, or a later target operation deserves trust.

CASE FILE
A GitHub Actions OIDC Token Is Not a Cloud-Authorization Verdict
A GitHub Actions OIDC token can identify a bounded workflow context to an external provider. It does not, by itself, establish that a cloud trust policy matched, that a cloud session was issued, that a resource permitted an action or that a target changed.
History
The Address Was Supposed to Declare the Charging Rule Before Contact: RFC 1681
In 1994, one IPng paper imagined a Gopher server redirecting a caller to a paid destination before any useful warning could appear. Its answer was to make the destination address speak first: some bits would identify who paid, or point to a charging algorithm. RFC 1681 exposed a…

CASE FILE
A GitHub Actions Concurrency Group Is Not a Deployment-Serialization Verdict
A GitHub Actions concurrency group can reduce conflicts between named jobs or workflow runs. It does not, on its own, establish the order of every consequential action against a target or the effect of those actions.
CASE FILE
A Dismissed Dependabot Alert Is Not a Remediation Verdict
A dismissed Dependabot alert records a triage decision about a repository-facing signal. It can be sensible and well documented. It still does not prove that vulnerable code is absent from a deployed system, that an upgrade was accepted, or that a remediation has happened.

History
The Etiquette RFC Assigned Responsibility. It Did Not Create a Global Referee
The Internet wrote down its manners in 1995 and immediately limited what the document could mean. RFC 1855 was Informational, not an Internet Standard. It offered a minimum that organizations could adapt, not a universal code that the IETF would enforce. That restraint was more…

CASE FILE
A Yanked PyPI Release Is Not a Package Withdrawal Verdict
A PyPI yank changes how a repository presents a release to selection tools. It can be an important signal for maintainers and consumers, particularly when a release is broken or violates a compatibility promise. It is not, by itself, a record that a package has been deleted, that…