
Topic
Institutional Legitimacy
Within the Topic facet, Institutional Legitimacy topic intelligence connects articles that share a specific subject, signal focus, or monitoring theme. The page gives readers a richer path through related reporting, source evidence, market actors, and infrastructure implications, with enough context to understand why the topic matters across company movements, governance decisions, regional exposure, and operational risk. Readers can compare recurring signals, affected organisations, public evidence, market context, service continuity, procurement, competition, compliance, and strategic planning questions behind the subject instead of stopping at a thin list of matching articles. It explains what the topic covers, which infrastructure actors or policies are involved, what evidence supports the coverage, and why the subject may matter for operators, customers, investors, and policy readers.
Global Institutional
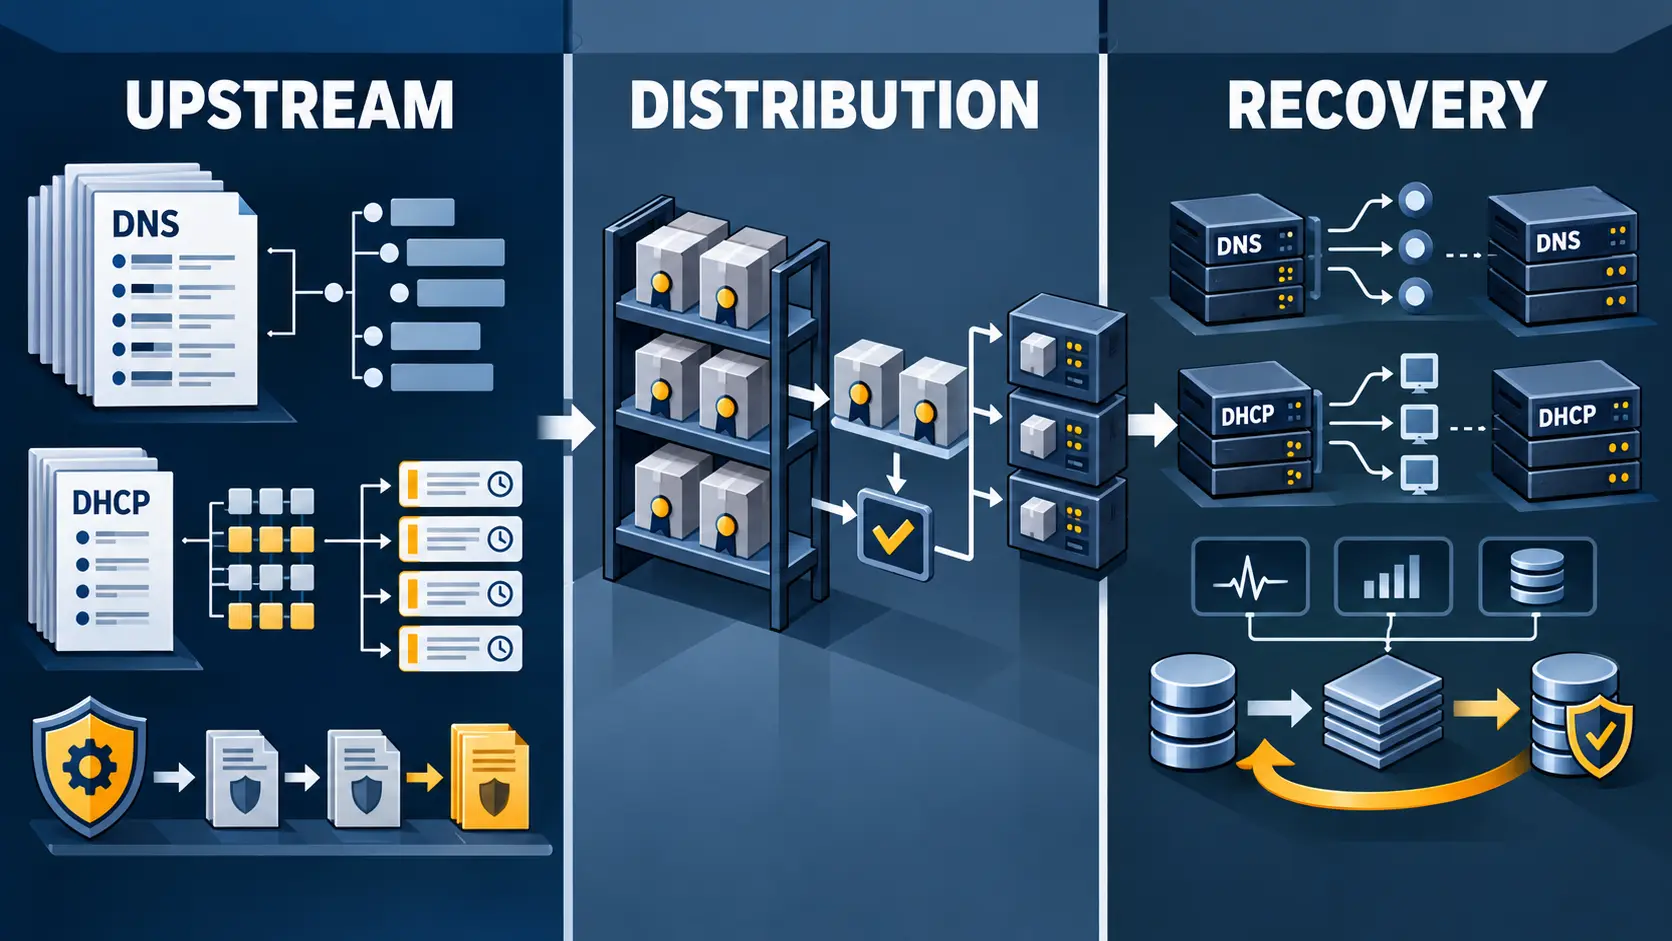
The Dependency Chain Behind ISC Software
ISC’s BIND and Kea influence network resilience through a chain that runs from upstream release work to distributor packaging and operator-controlled recovery. The public record documents important mechanisms and distribution channels. It does not show how many operators deploy…
History
The List Expired on 16 June: RFC 2000 and the Two Axes of Protocol Status
RFC 2000 was itself an Internet Standard, yet it carried a use-by date. That was not a paradox. The document was authoritative as a dated classification, not a permanent measurement of what the Internet had implemented.
ICANN
ICANN’s Authority Is a Chain, Not a Crown
ICANN can influence the global domain-name system without being a government. Its practical authority is assembled across several instruments: a California nonprofit charter, corporate bylaws, multistakeholder policy procedures, contracts with registries and registrars, technical…

IETF
A Valid YANG Schedule Is Not Evidence That Its Action Is Still Authorized
At 02:00, a controller executes the seventh occurrence of a maintenance schedule created six months earlier. The recurrence is enabled, its version is current, the clock is trusted and no scheduling conflict is reported. Yet the team that approved the action has been reorganized…

History
The Group Did Not Need Consensus. Its Charter Still Had to Answer: RFC 2014
In 1996, BCP 8 made a bargain that looks contradictory only if research is mistaken for standards-making. An IRTF research group could stay small, work for years and publish competing conclusions without choosing one consensus answer. In return, it had to say what it was for…

IETF
IETF Opened an AI Standards List Without Defining Its Decision Path
The IETF has given a disputed question a dedicated address. On 9 September, its Secretariat created `[email protected]` for discussion of artificial intelligence in the standards process. That is a useful institutional act: it makes participation and the public archive…

ICANN
ICANN’s Authority Is Contractual Before It Is Public
ICANN can influence the global identifier system without being a government and without possessing unilateral control over every technical action that follows its decisions. Its authority is assembled from several instruments: corporate bylaws, operational agreements, registry…

Story
ARIN’s 2026 Candidate Forum Page Still Carries the 2025 Voting Window
ARIN opened registration for an October forum on its 2026 Board candidates. The event page gets the year, forum date and subject right, then tells readers that voting runs from 30 October through 7 November—the window ARIN published for 2025, not the 22–30 October window on its…

IETF
A YANG Service Model Can Match While Its Lifecycle Semantics Diverge
At 18:00, a time-bounded network service reaches the end written in its order. The BSS marks it complete. The orchestrator begins decommissioning. One controller still calls the connection active, another has already removed a segment, and the assurance system reports a healthy…
Leaders
What AFRINIC’s Registry Records Can—and Cannot—Attribute to Maina Mukhangu Noah
A public registry listing connects Maina Mukhangu Noah to ORG-BITL1-AFRINIC, but the available record does not establish that he held institutional authority inside AFRINIC. The distinction matters because a contact field can guide operational communication without identifying…

CASE FILE
When a BIND Fix Is Not Yet a Repair
A resolver vulnerability becomes an institutional accountability test when the patch is available but the evidence of recovery is not. ISC’s public record establishes how two BIND failures can turn hostile DNS input into an availability risk—and identifies a remediation…

ICANN
ICANN Kept Its Strategy Unchanged Without Showing the Trigger Test
ICANN’s latest annual strategy review ended with a clear Board decision and an incomplete public chain of reasoning. After eight environmental-scan sessions involving nearly 210 entities, the Board affirmed on 6 September that its FY26–30 Strategic Plan would remain unchanged.…

IETF
IETF–W3C: A Relationship Record, Not a Single Institution
The label “IETF–W3C” compresses two standards institutions into one directory entry. The public record supports a narrower description: the organizations have documented channels of cooperation, but the evidence reviewed does not establish one legal entity, one administrative…

IETF
A Company-Certs Endpoint Cannot Prove Who Approved a Trust-Anchor Rollover
At 10:00, an application retrieves two valid private-CA chains from its company’s well-known HTTPS endpoint. The older chain still works; the newer chain has the later `valid_from`, so the client selects it exactly as the draft describes. TLS validation passed, the JSON parsed…
Leaders
Noor Helmi’s Control Surface—and the Missing Transfer Record
A closer look at what can be attributed to IX Telecom’s co-founder and CEO, and what the public record still cannot show about capability surviving beyond the individual.
CASE FILE
The EU’s Cyber-Product Reporting Clock Is Running Before Its Main Security Rules
Europe has switched on one of the Cyber Resilience Act’s most consequential mechanisms fifteen months before the law’s main product-security duties take effect. From 11 September 2026, manufacturers must report actively exploited vulnerabilities and severe security incidents on…

IETF
A Workload Credential Can Outlive the Attestation Decision Behind It
At 09:00 a workload proves that it is running in Germany and receives an eight-hour credential. At 09:05 the orchestrator moves it to France. The credential still verifies, the key is still under the workload’s control, and the unchanged service still accepts it. Yet one fact…

IETF
A Key Transparency Proof Cannot Audit Who Was Allowed to Look
Alice searches a Key Transparency log for Bob and receives a valid proof. Fred makes the same request and is stopped by the application before the log sees it. The proof can show that Alice’s answer fits an authenticated, globally consistent tree. It cannot show why Alice was…

CASE FILE
The EU Named Three Very Large Services. Their Exact DSA Compliance Dates Are Not Public
The European Commission has put ChatGPT, Reddit and Roblox inside the Digital Services Act’s highest-supervision tier. It also says their additional duties apply by January 2027. What the public record does not yet provide is the day that matters in law: four months after each…
Story
APNIC's Governance Score Is 77%. Its Don't-Know Average Is 20%.
APNIC's new survey does not produce one verdict on governance. It produces a positive score among people able to judge eight claims, and a separate measure of how often members could not judge them. Any decision that carries the first number forward should carry the second one…