
Topic
Data Sovereignty and Locality
Within the Topic facet, Data Sovereignty and Locality topic intelligence connects articles that share a specific subject, signal focus, or monitoring theme. The page gives readers a richer path through related reporting, source evidence, market actors, and infrastructure implications, with enough context to understand why the topic matters across company movements, governance decisions, regional exposure, and operational risk. Readers can compare recurring signals, affected organisations, public evidence, market context, service continuity, procurement, competition, compliance, and strategic planning questions behind the subject instead of stopping at a thin list of matching articles. It explains what the topic covers, which infrastructure actors or policies are involved, what evidence supports the coverage, and why the subject may matter for operators, customers, investors, and policy readers.

Europe and Middle East Cloud Services
Safe Swiss Cloud: what 'sovereign' actually holds up in the record
A Zurich-based cloud provider markets itself as 100% Swiss, privately owned and independent of US jurisdiction. The public record tells a more layered story — and the differences matter for any enterprise betting on it.
Asia-Pacific Cloud Services
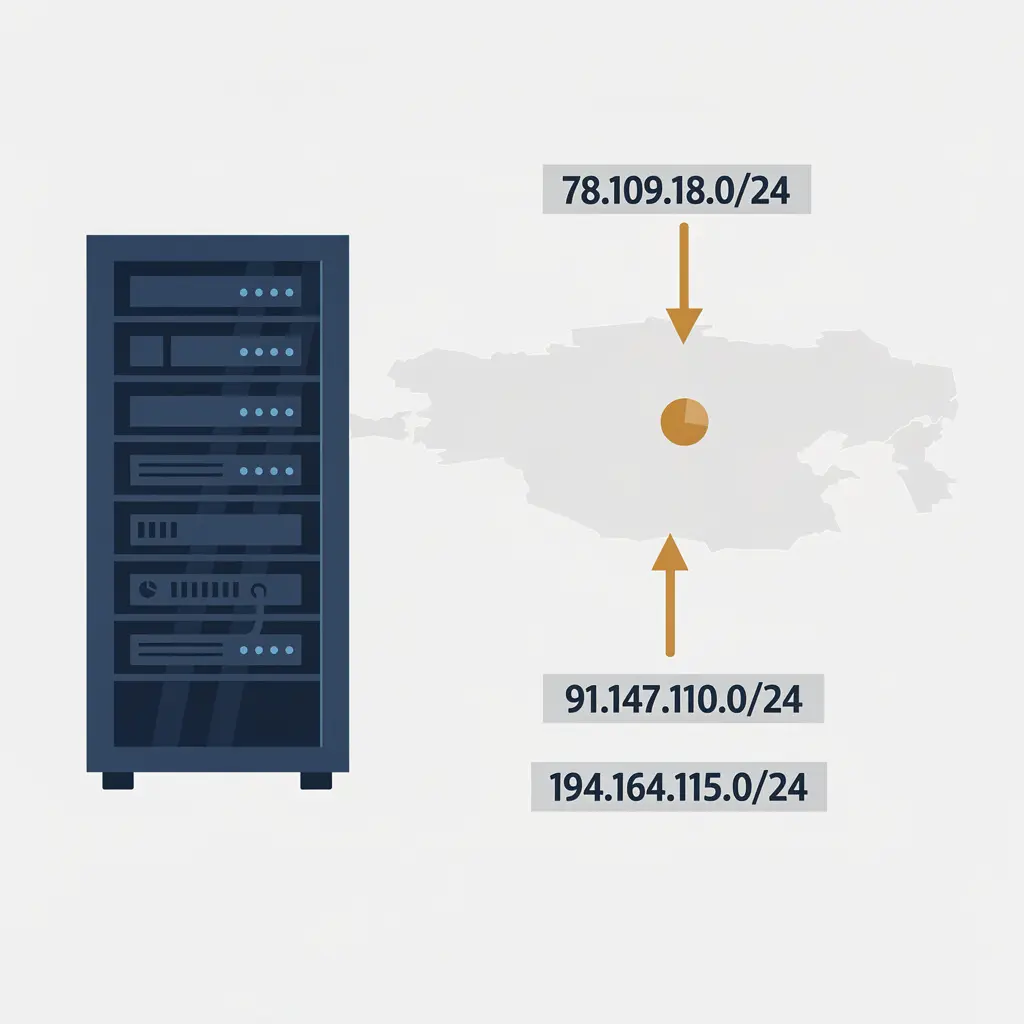
NovaCloud: two autonomous systems, one brand, and the gap between marketed cloud and routed reality
NovaCloud: two autonomous systems, one brand, and the gap between marketed cloud and routed reality intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure…

Asia-Pacific National Telecom Trends
VEON has approval for a Bangladesh digital bank. The operating licence is still a gate
A corporate announcement can compress a regulatory sequence into one noun. Bangladesh Bank's own rulebook does the opposite: it separates sponsor eligibility from the final licence, and turns the distance between them into cash, governance, local infrastructure and audit…
Europe and Middle East Datacenter Trends
Mistral Compute: four megawatt figures, one signed loan
Public statements about [Mistral Compute](https://btw.media/en/directory/mistral-compute) mix a 1,400 MW design ceiling at Fouju, 700 MW pre-reserved with transmission operator RTE, connection tranches of 240 MW and 700 MW, and 44 MW at Eclairion's Bruyères-le-Châtel site. Those…

CASE FILE
The Data Was Split. The Operator Could Still Reassemble the Person: RFC 9614
The relay could identify the client but could not read the request. The gateway could read the request but could not see the client's address. Then one operator aligned the two logs by time and size. Every box kept its local promise; the system did not keep the privacy promise.…

History
One Record, Five Different Directories: RFC 2378
RFC 2378 described a people directory in which a field could exist without being discoverable, be discoverable without being searchable, be searchable without being returned, and be editable without being changeable over the network. The important invention was not a phone book.…

Europe and Middle East Cloud Services
NVIDIA's European AI factories: announced capacity is not operated capacity
NVIDIA's European AI programme now spans a Munich industrial AI cloud, UK capacity commitments and a USD 2bn investment in Nebius. The announcements describe computing that is promised; they do not yet describe facilities, power contracts and network paths that are operating.

Global Cloud Services Trends
IBM puts digital-asset control on premises; settlement still crosses the boundary
Putting wallets, policies and signing keys inside a bank's own data centre changes who can authorise a transaction. It does not bring the whole payment chain home. IBM's new Digital Asset Haven betas expose a more useful market question: can a bank prove each handoff from local…
Global Cloud Services Trends
VAST DataEnclave brings models to private data; the market gate is key release
Confidential computing can prevent a host from casually inspecting a model or a dataset. It cannot decide whether the model owner and the data owner should do business. VAST DataEnclave matters because it makes that second question operational: two owners keep separate keys…

IETF
A Regionalized ROA can sign a place. It still cannot prove a hijack
An individual Internet-Draft would add geography to route-origin validation. The useful part is a new, explicit signal. The dangerous shortcut is to treat that signal as the event it is meant to detect.
IETF
RFC 9998: A Failed Age Check Is Not Consent to a More Intrusive One
Age checks are often presented as a door: prove the required range and it opens; fail and it stays shut. The harder governance problem begins when the first check produces no reliable answer. A system may then ask for a document, a face scan, a phone number or a longer behavioral…

Europe and Middle East Cloud Services Trends
NetCloud Private turns Gulf sovereignty into two operating models
Ericsson is moving its router-management platform into locally controlled environments. The Gulf deployments reveal that “local” can mean a customer running its own system or a domestic service provider running one for several enterprises. Those structures produce different…
Global Datacenter Trends
AXG and Digital Realty Offer 31 Markets, Not a Deployment Ledger
The partnership gives integrators a broad channel for hosted private infrastructure. Its commercial promise will be proved one customer, facility, acceptance test and exit schedule at a time.
CASE FILE
Four VPN Restrictions, One Label, No Shared Authority
On 9 September, the Internet Society grouped four very different interventions under the heading “VPN restrictions”. The taxonomy is useful; the label is dangerous. An age rule, a blocking order, a logging duty and a prohibition do not regulate the same actor or need the same…
North America Datacenter Trends
Canada’s Data-Centre Principles Still Need a Project-Level Receipt
“Must” is a strong word, but it is not a receipt. Canada now says a data centre must pay the electricity-system costs it causes, limit water impacts, disclose local effects, leave durable benefits and add strategic value. That is a useful national test. Yet a mayor, utility…

CASE FILE
A Million Government URLs Can Show Dependency. They Cannot Prove Who Chose It
A new cross-country study compares the companies behind government websites with those serving commercial sites. Its distinction between market-shaped and government-specific concentration is a useful diagnostic. But an infrastructure measurement cannot identify the official who…

Global Cloud Services Trends
Rackspace’s Sovereign Pod puts model changes on the buying agenda
Blackwell hardware and Palantir software are to sit inside a Rackspace-operated environment. The purchasing question extends beyond keeping it running: who may change the model, and who still owns the decision?

History
The Certificate Was Public. The Private Key Was Not: RFC 1984’s Trust Boundaries
In July 1996, two Internet standards bodies accepted that a government could operate a certification authority and still rejected the idea that a government, or any other third party, should hold a user’s private key. That is not a contradiction. It is the organising distinction…

Story
LACNIC Says to Email the Bulk WHOIS Form. The Same Page Says Email Is Not Accepted
LACNIC’s public instructions give a Bulk WHOIS applicant two doors and no label for the threshold between them. The signed form is to be emailed first, the original is to be posted after approval, yet the same page ends by saying emailed forms are not accepted. The problem is not…

Global Regional ISP Trends
RapidSeedbox's routing handoff makes location an evidence problem
RapidSeedbox's own guidance draws a useful line: an address range used on its dedicated server can be routed by RapidSeedbox, while a range used on a customer's server is announced by that customer's data centre or provider under a Letter of Authorization. A location label alone…