
Summary
- The Internet Society's 9 September policy brief identifies four families of VPN restriction: age assurance, content blocking, surveillance requirements and bans. Its concerns and recommendations are the organisation's policy position, not legislation or a finding that every example has the same effect.
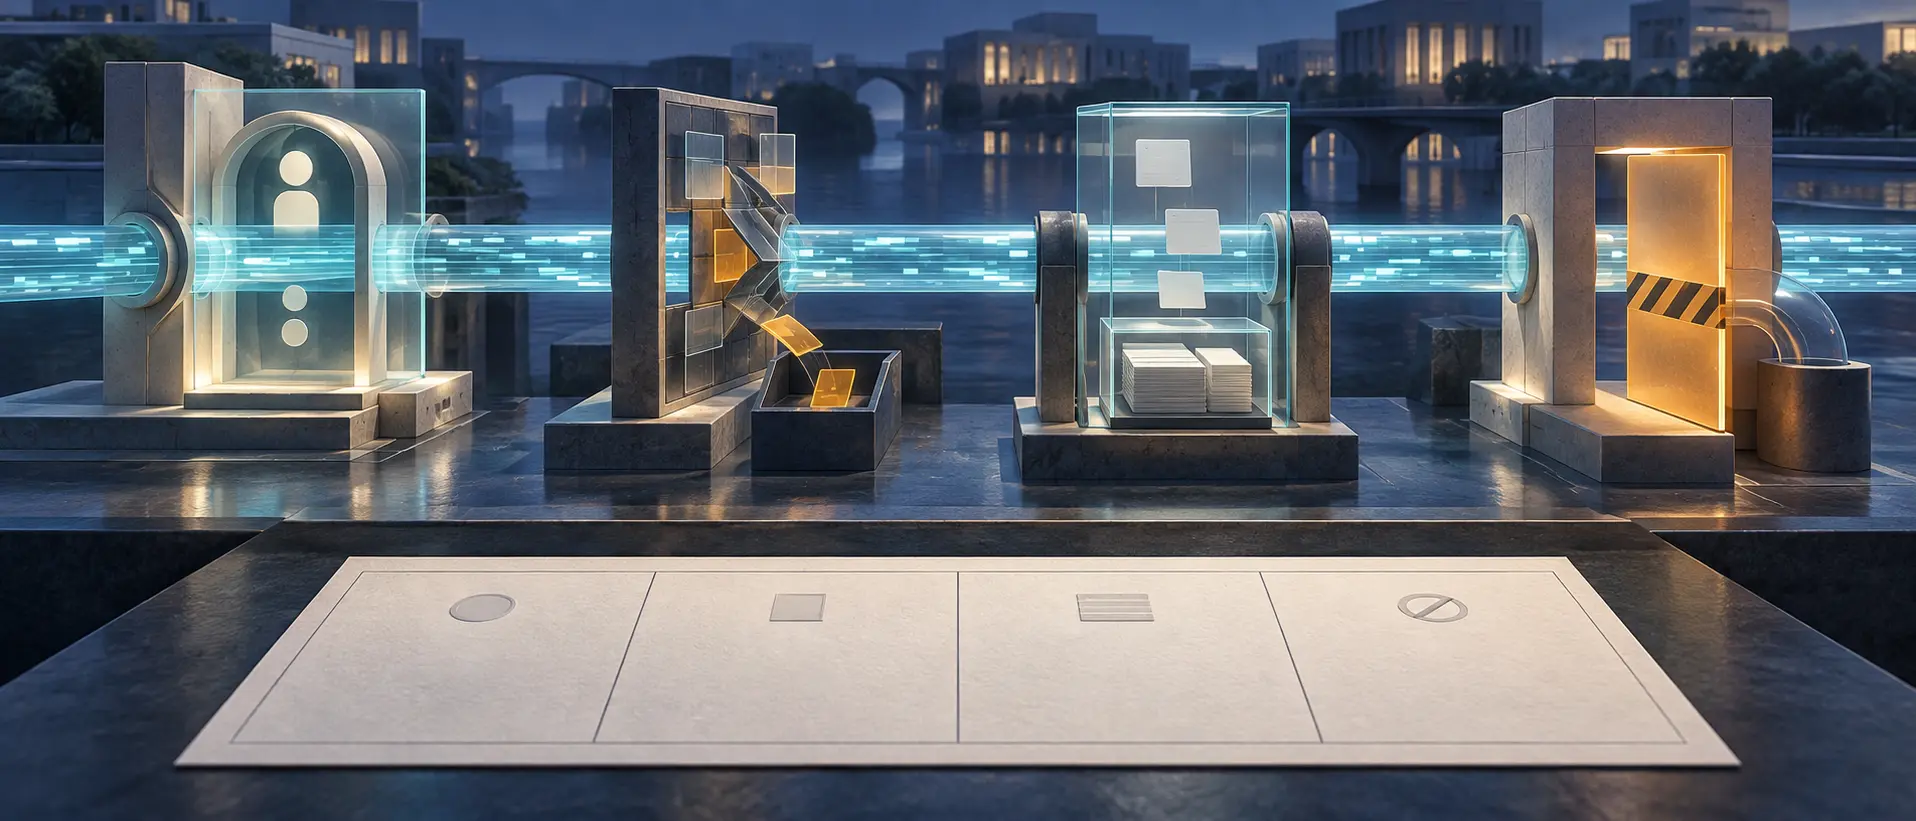
- Official records from Utah, Italy, India and China show why the families cannot be governed as one object. They attach duties to different parties, require different data, extend across borders differently and offer very different correction paths.
- I propose a public, measure-level restriction receipt. It should name authority, target, enforcement point, data, geographic reach, exceptions, review, expiry and observed outcome before the shorthand “VPN restriction” is allowed to carry the argument.
A legislature can mention a VPN without regulating a VPN provider. A regulator can make a VPN service implement a block without banning encrypted tunnels. A cyber-security direction can require customer records while excluding a company's internal remote-access system. And a cross-border telecom rule can be described abroad as a “VPN ban” even when the issuing authority says lawful office use is unaffected.
Those are not semantic details. They determine who must act, whose data enters a new store, where an order executes and who can reverse an error.
The Internet Society policy brief published on 9 September supplies a helpful opening map. It separates VPN age-assurance requirements, VPN content blocking, VPN surveillance requirements and VPN bans. The brief argues that these interventions can weaken security, privacy, access and trust, and recommends action closer to illegal content or conduct. Those are Internet Society's assessments and recommendations. They are not a common legal rule, and the four-part map does not itself prove what any particular measure does.
The legal subject changes before the packet moves
Utah's enrolled S.B. 73 is a useful age-assurance example precisely because it does not turn the tunnel provider into the age gate. Its provisions address a site publisher making material harmful to minors available. Access is treated as coming from Utah even when a person disguises location through a VPN or proxy, and the publisher may not facilitate that circumvention. The same text says identifying information used for access should not be retained after access, provides a public-interest and news exception, and draws boundaries around intermediaries such as Internet access, search and cloud services.
The word VPN therefore appears inside a publisher-facing rule. The regulated target, the verification event and the data-retention limit sit at the destination surface. Calling it simply a “VPN age restriction” would conceal the most important allocation.
The United Kingdom provides a second boundary, but not the centre of this article. Its July 2026 response said government would neither ban VPNs nor require VPN services to age-assure users. That shows a government can reject two members of the taxonomy while pursuing the underlying child-safety objective elsewhere. The earlier BTW case file examined that platform-enforcement question in depth; the point here is narrower: a policy objective does not identify the lawful enforcement point by itself.
Blocking is an execution order, not an identity rule
Italy's regulator describes Piracy Shield as a rights-enforcement platform active since February 2024. AGCOM says orders can require access to specified fully qualified domain names and IP addresses to be disabled within 30 minutes, and that a complaint may be filed within ten days without automatically suspending execution. In Delibera 401/24/CONS and its institutional explanation, the regulator brings access-related services, including VPN and DNS providers, within the accreditation and implementation surface, including providers outside Italy in the circumstances it describes.
This family operates on reachability. Its accountability questions are the source and precision of the identifiers, propagation time, collateral reach, notice, correction and restoration. It need not know a user's age. It need not maintain a five-year subscriber record. It can nevertheless have immediate cross-border effects because an order addressed in one jurisdiction may be implemented by a provider, resolver or service architecture located elsewhere.
A claimant's account of a Paris Judicial Court order illustrates a related but distinct route: CANAL+ says five VPN providers were ordered in May 2025 to block 203 domains. That number and description belong to the claimant's press release unless the court order itself is examined. Even within “content blocking”, the issuing body, evidence, appeal and technical object must remain attached to the individual order.
A record-keeping duty creates a different asset
India's CERT-In FAQ explains customer-information duties under its 2022 cyber-security directions for public VPN services. It expressly says the relevant definition does not extend to enterprise or corporate VPNs, and it discusses the production of records kept outside India when a foreign provider serves users in India.
Nothing has to be blocked for this measure to change the system. The intervention creates or standardises a record: who subscribed, for how long, under which identifying particulars and under what production expectation. Its enforcement point is the provider's customer and logging system. Its cross-border question is jurisdiction over service and records. Its irreversible risk is accumulation: a store created for one cyber-security purpose can outlive the incident that justified it and become attractive for other uses.
That is why “surveillance requirement” needs a data inventory, not a blocking metric. The meaningful denominator is not domains disabled but accounts covered, data fields collected, retention periods, production demands, challenges and deletions.
The word “ban” needs the strongest proof
A ban removes a lawful operating or usage category rather than adding a gate, an identifier list or a record duty. It therefore needs a precise legal object: provision, sale, advertising, installation, possession or use are not interchangeable.
China's 2017 official notice about cleaning up the Internet access-service market targeted unauthorised cross-border telecom business and required approval for establishing or leasing dedicated cross-border lines, including VPN services, for such operations. The accompanying official explanation said lawful office use by enterprises and ordinary users was unaffected. Whatever later enforcement may require in a specific case, those two records do not support compressing that measure into an unqualified blanket ban.
Internet Society cites bans as a distinct family and criticises them. That is its policy assessment. A publisher should still refuse the family label unless the operative text answers: banned for whom, doing what, from when, with which licence or exception, enforced by which body and reviewable where?
Publish one receipt for each measure
The repair is not another universal test for VPN policy. It is a rule against universality.
I propose that every public intervention receive a restriction receipt with nine fields. First, the legal authority and current status: bill, enacted rule, court order, regulator direction, voluntary request or announced intention. Second, the protected objective. Third, the regulated target and decision owner. Fourth, the technical enforcement point. Fifth, the data required or generated. Sixth, territorial reach and cross-border spillover. Seventh, exceptions and protected uses. Eighth, appeal, correction and restoration. Ninth, sunset, renewal and an observed outcome with its denominator.
This receipt is my editorial recommendation. It is not contained in the Internet Society brief, promised by AGCOM or CERT-In, or required by the statutes cited here. It applies three editorial tests: follow the mandate rather than the label, as The Policy Mirror urges; test what a running system actually needs, following Running-Code Primacy; and keep observable structure separate from institutional positioning, the discipline set out in Why BTW.Media Exists.
The receipt would not decide whether a measure is wise. It would make disagreement possible without allowing four different powers to borrow legitimacy from one familiar acronym.
Sources
- Internet Society: Policy Brief — VPN Restrictions
- Utah Legislature: enrolled S.B. 73
- AGCOM: Piracy Shield
- AGCOM: Delibera 401/24/CONS
- AGCOM: anti-piracy competence and covered services
- CERT-In: FAQ on the 2022 Cyber Security Directions
- China: official market-clean-up notice
- China: official explanatory Q&A
- UK government response, July 2026
- CANAL+ account of the Paris order
- RFC 4301
- Heng Lu: The Policy Mirror
- Heng Lu: Running-Code Primacy
- Heng Lu: Why BTW.Media Exists
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance