
Profile
Research
Research profile intelligence connects person, company, institution, and other entity coverage for readers comparing the subjects behind BTW.MEDIA reporting. The page helps compare public profiles, related events, evidence packs, role changes, operating footprints, governance exposure, organisational links, and market relevance while keeping organisation and people records distinct from ordinary news chronology. Readers can understand the subject behind the headline, the evidence supporting that profile, and the infrastructure or market relationships that make the profile relevant. They can see who or what the profile represents, which public sources support it, how it connects to companies, markets, governance bodies, or events, and what changes may deserve continued attention as the subject evolves.

Global Cloud Services
DATAMATIX and AS210973: From Network Visibility to a Testable Operating Business
DATAMATIX and AS210973: From Network Visibility to a Testable Operating Business intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that…

Leaders
Mohamed Awang Lah and the Institutional Continuity of MyCERT
Malaysia’s MyCERT is best understood not as a personal possession that moved from one job to another, but as an incident-response function that survived changes in institutional placement. Dr. Mohamed Awang Lah can be connected to the security initiatives associated with MyCERT’s…

IETF
RFC 9990 Counted the Receiver’s Claims, Not the Mailstream Itself
A dashboard can show 240,000 messages, three alignment rates and a red segment labelled as a policy override. The numbers may be perfectly formed and genuinely useful. They still do not let the domain owner walk back through 240,000 individual decisions. RFC 9990 standardizes…
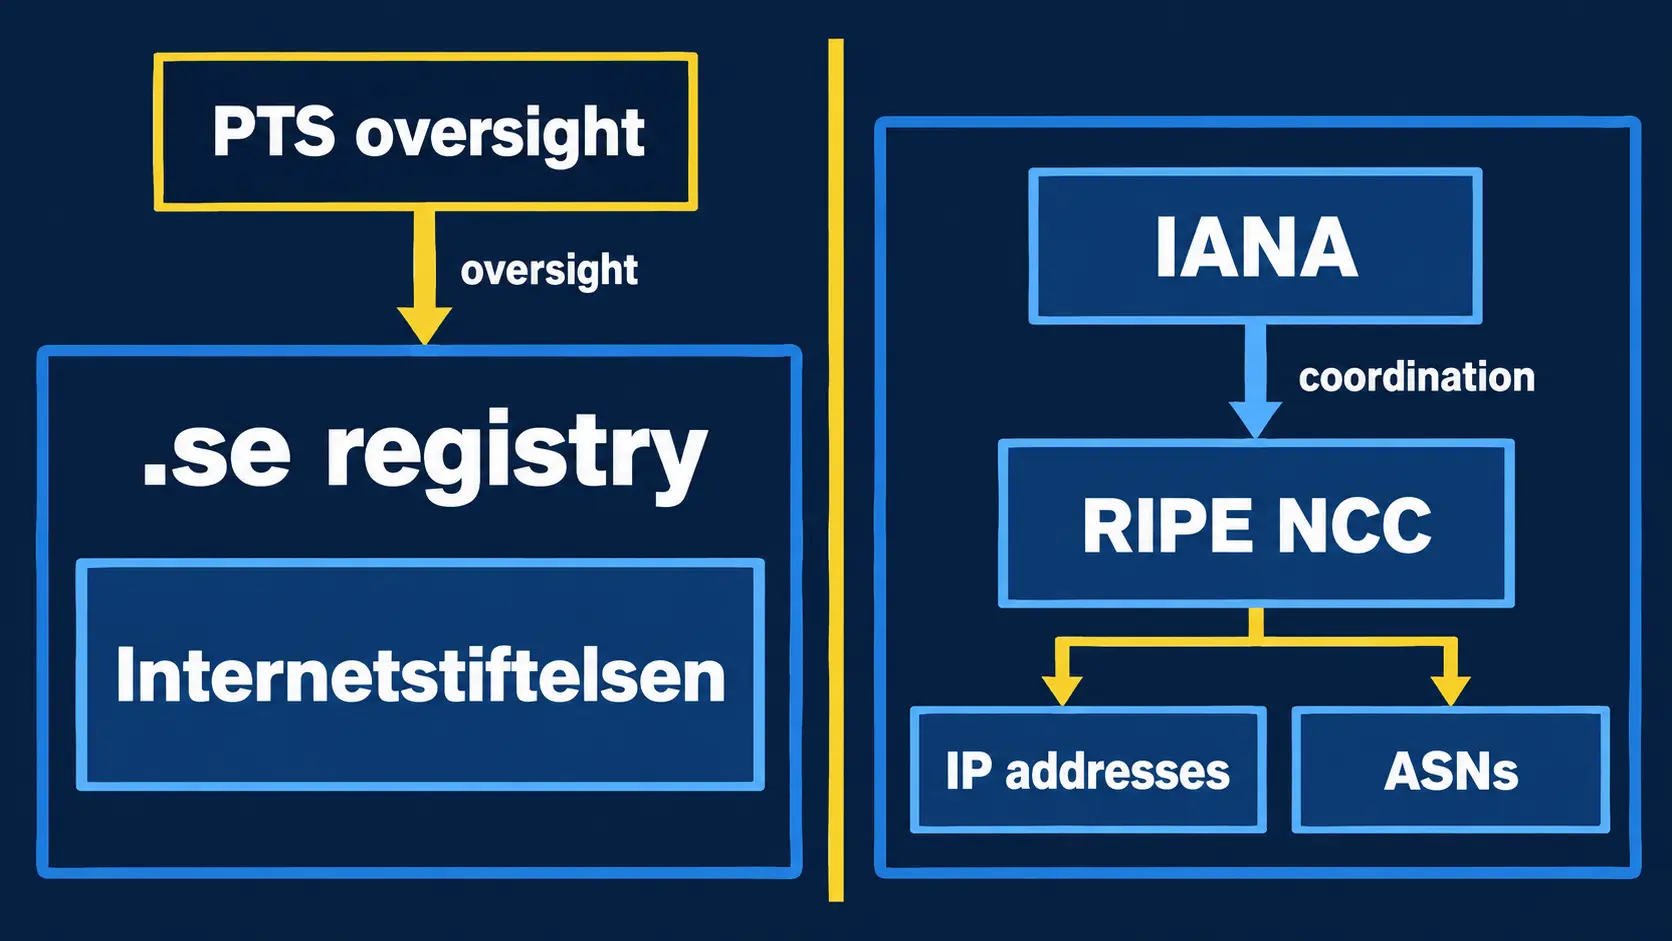
Europe and Middle East Institutional
What Internetstiftelsen Controls—and What It Does Not
A sparse directory label points toward Sweden’s .se registry, but the evidence separates domain-name stewardship from the Internet’s IP-address and autonomous-system infrastructure.

IETF
RFC 9996 Registered the Media Type, Not the Schema Version
A label can tell a receiver what kind of parcel arrived without telling it which rulebook gives the contents meaning. RFC 9996 gives Protocol Buffers two proper media types and draws useful boundaries around binary and JSON handling. It does not place the Protobuf schema, its…
Leaders
From Registry Association to Operational Authority: What AS211867 Records Can—and Cannot—Show
From Registry Association to Operational Authority: What AS211867 Records Can—and Cannot—Show intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure…

IETF
RFC 9997's PEN-Derived SID Range Is Not a Provenance Stamp
A number can be globally unique and still tell the wrong story about its origin. RFC 9997 gives eligible Private Enterprise Number holders a deterministic block of YANG Schema Item iDentifiers, eliminating a central allocation round trip. That is useful coordination. It is not an…

IETF
RFC 9979’s `$istrusted` Badge Needs a Correction Record
A green check can outlive the judgment that painted it. A mail server marks a message `$istrusted`; several clients synchronize the shared keyword; a reader acts because the interface presents the sender as verified. Later, the server discovers that its evidence or policy was…

IETF
An SSH Agent Signature Is Not a Consent Receipt
A private key never left its protected agent, the requested bytes were signed correctly, and the remote service still received an act that nobody had meaningfully approved. Those facts can coexist. Keeping a key non-exportable answers where the secret stayed. It does not answer…

IETF
The manifest followed the telemetry. The verdict did not
Revision 14 gives collected network data a companion record of its platform, schema and collection conditions. That makes a datapoint easier to read later; it does not make the datapoint complete, the clock trustworthy or the resulting decision correct.

IETF
The log line parsed. The authority to read the connection did not: RFC 9850
RFC 9850 gives diagnostic tools a common way to read TLS connection secrets. The grammar is small; the authority it can transfer is not. A usable key-log record proves neither permission nor safe closure.

IETF
Set-Cookie Is Not a Storage Receipt
A response crossed the network with a valid `Set-Cookie` field, and the release dashboard marked the session step complete. The next request arrived without the cookie. Nothing in those two observations is contradictory. RFC 10025 gives the server authority to issue an…

IETF
A CoAP Group Address Is Not a Security Membership Roster
RFC 10020 separates three groups that operational dashboards often collapse: endpoints listening on a multicast address, servers exposing a common application function, and devices holding shared security material. A packet can cross the first boundary and authenticate at the…

IETF
The verifier subscribed. The evidence chain still had seven tests
An IETF draft turns device attestation from a polling exercise into a stream. That is a useful change in tempo, but a signed notification is still only one link between a measurement and a decision.
Story
RIPE NCC Says Its 2027 Invoicing Changes Are Complete. The Bill Still Waits for 31 December
RIPE NCC has finished the applications work for its 2027 charging scheme before the data that will determine the first bills exists. That is sensible project management. It is also why “complete” needs a second, more operational meaning in January: can each charge be reproduced…

CASE FILE
AlmazCloud’s ASN Is Registered. What Can Be Shown as Operating?
AlmazCloud’s ASN Is Registered. What Can Be Shown as Operating? intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that may follow. The…

ICANN
ICANN’s Authority Is a Chain, Not a Sovereign Grant
ICANN can shape the global identifier system without possessing a general public-law mandate over the internet. Its authority changes form as it moves from corporate purpose to Bylaws, from multistakeholder policy to contractual obligation, and from contract to technical…

Number Resource Society
AS210837’s Continuity Question Is an Evidence-Chain Problem
AS210837’s Continuity Question Is an Evidence-Chain Problem intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that may follow. The Number…
Global Institutional Trends
ISC’s control chain: what public evidence shows about prevention, detection and durable repair
ISC’s public record presents a recognizable operational control chain: vulnerability information is coordinated, supported software releases are published, high-availability behavior is documented and tested, service status is exposed, and F-Root operations are described across…

Number Resource Society
AS210057’s visible network footprint still stops short of proving who operates it
AS210057’s visible network footprint still stops short of proving who operates it intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that…