
Profile
Research
Research profile intelligence connects person, company, institution, and other entity coverage for readers comparing the subjects behind BTW.MEDIA reporting. The page helps compare public profiles, related events, evidence packs, role changes, operating footprints, governance exposure, organisational links, and market relevance while keeping organisation and people records distinct from ordinary news chronology. Readers can understand the subject behind the headline, the evidence supporting that profile, and the infrastructure or market relationships that make the profile relevant. They can see who or what the profile represents, which public sources support it, how it connects to companies, markets, governance bodies, or events, and what changes may deserve continued attention as the subject evolves.
CASE FILE
The Token Knew the Address, Not the Actor: DNS Cookies and the Authority of Weak Authentication
A valid DNS Server Cookie proves something useful and deliberately small: a requester using this Client Cookie at this source address previously received a value derived from a server secret. Trouble begins when an operations system promotes that narrow fact into identity, trust…

CASE FILE
An IANA Code Point Is Not a Licence to Deploy
The Internet needs common numbers, strings and names so that independently built systems can understand one another. IANA protocol-parameter registries supply that shared vocabulary. Their authority is real, but deliberately narrow: a registry entry can settle which value carries…
Global Cloud Services Trends
Encrypted ClientHello Is Becoming a DNS-to-Edge Configuration Contract
A DNS operator can publish a fresh ECH public key in seconds. The matching private key may reach five edge clusters in seconds too, and the sixth after a maintenance window, a stalled secret distributor or the discovery that clocks remain an optional feature of distributed…

North America National Telecom Trends
A Cable-Landing Permit Has More Than One Clock
A financing model may show one date for a United States submarine-cable landing permit. The real schedule has separate clocks for application completeness, national-security review, mitigation and final regulatory action—and some do not start when the application is filed.

Number Resource Society
The Proposal Competition After Its Deadline
Rules can explain how a competition is supposed to end. Only a dated decision and fulfilment record can show which ending actually occurred.

Global Cloud Services Trends
A billion-dollar security alliance still needs an evidence ledger
NTT DATA and Palo Alto Networks have set a large commercial ambition for a deeper global alliance. The useful test is not the headline value but whether customers can see where platform responsibility ends, managed-service responsibility begins, and an outcome becomes measurable.
Global Institutional Trends
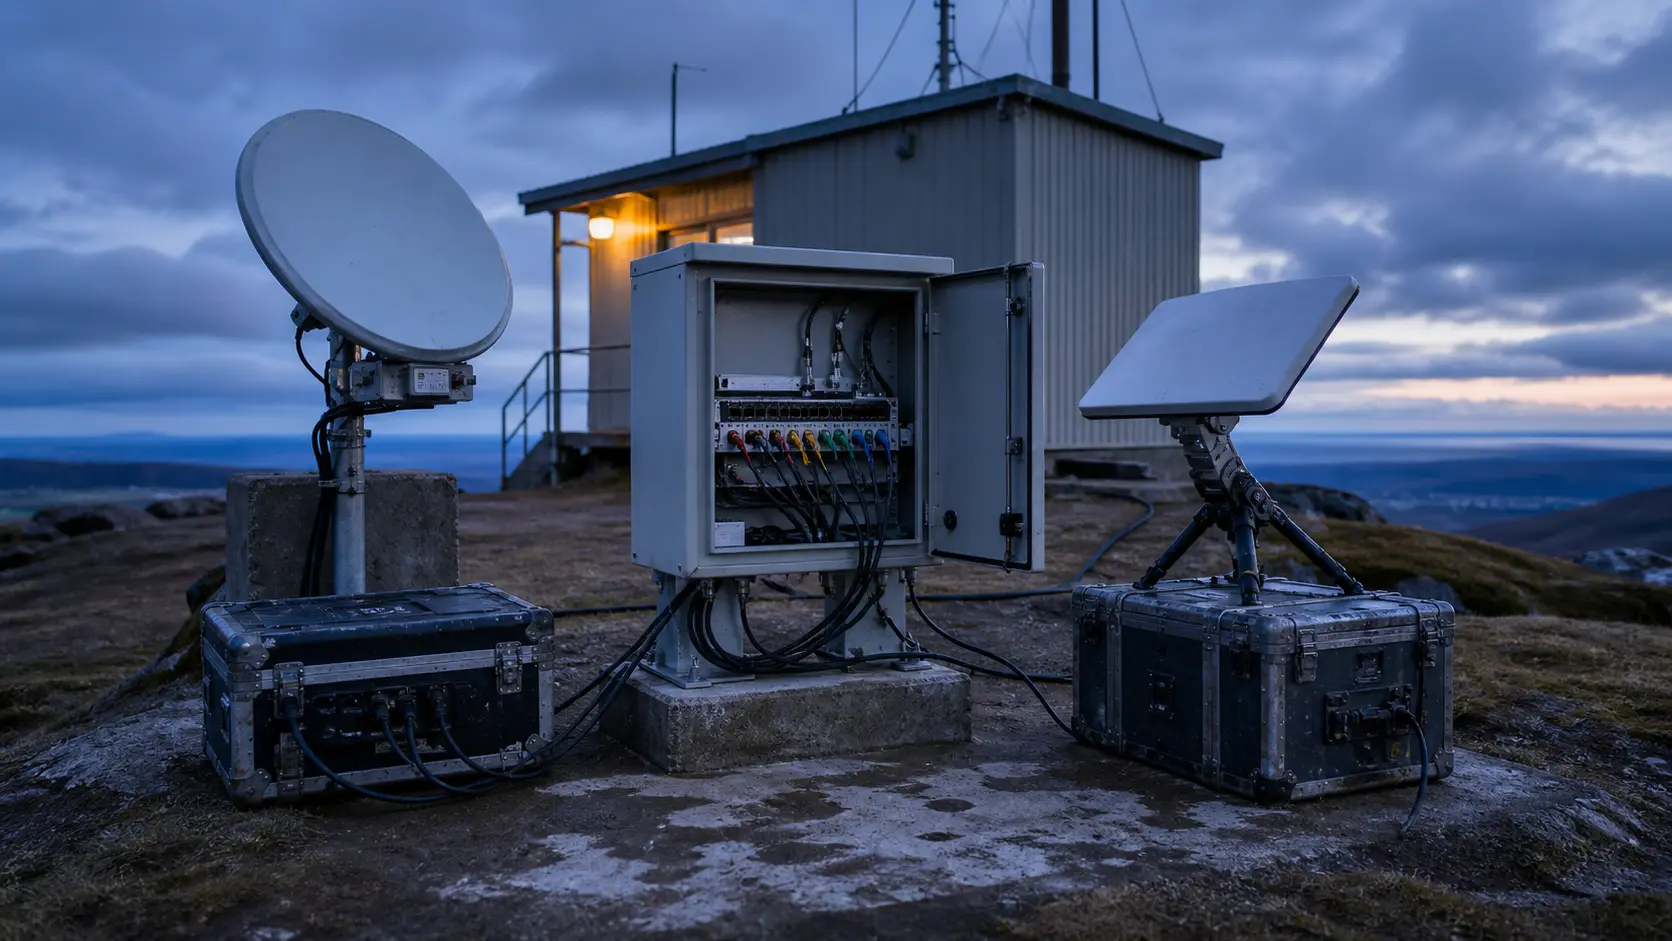
A satellite terminal is not public infrastructure until the buyer can leave
A dish on a roof is visible, countable and easy to photograph at launch. The harder public asset is the right to keep that site connected when the account holder changes, the subscription ends, a licence moves or the original supplier is no longer the right one.

History
When the Warning Reached the Wrong Server: The History of Path MTU Discovery
In 2015, Cloudflare found that a TCP flow and the ICMP warning meant to repair it could enter the same data centre and still reach different machines. The path had stated its limit. The server handling the connection never heard it. That incident exposed the institutional bargain…
Global Regional ISP Trends
IPv6 Extension Headers Are Becoming a Path-Compatibility Tax
The address answers. Ping works. Then the transport header moves 64 bytes deeper into an otherwise valid IPv6 packet, and the path goes quiet. Basic reachability survived; optional capability met the smallest parser on the route. It is a compact demonstration of how a protocol…
Asia-Pacific National Telecom Trends
Y.3335 standardizes the path, not the service
ITU-T has approved a common framework for low-latency, energy-efficient communication across operator domains. Y.3335 can align how networks describe the problem, but it does not yet prove that a multi-operator path will meet a latency target, consume less energy or survive a…

CASE FILE
The Public Path Looked Cleaner. Its History Had Been Rewritten: BGP Private-AS Removal and the Authority to Erase a Hop
The customer route arrived with three private autonomous systems in its path. At one public exit they vanished. At another, one survived. At a third, all three returned wearing the provider's number. Each operator had configured something called private-AS removal. The public…

CASE FILE
Trusted channels, no command: who can speak for FIRST in a cyber crisis?
A warning enters a trusted channel during a cross-border incident. Three decisions follow, and they do not belong to the same institution: who may enter the room, who may speak for the network, and who may act on an affected system. FIRST has substantial control over the first…

CASE FILE
Empowered without a vote: what the IGF Leadership Panel can actually command
The IGF Leadership Panel was designed to carry messages, recruit senior attention and find resources. Appointment by the UN Secretary-General gives that work institutional access. The operative rules still leave the annual programme with the MAG, execution with the Secretariat…

ICANN
The drafting room behind root advice: who controls the RSSAC Caucus pipeline?
Most RSSAC reports are built in a body far larger than the committee that formally approves them. The current rules make that division visible: experts may propose, research and draft; root server operator representatives keep the gates for admission, scope, amendment and…
ICANN
The security advisers the Board appoints: where SSAC authority stops
Three dates describe the gate. On 25 November 2025, an internal membership committee recommended three candidates. On 10 December, SSAC approved them by consensus. On 25 January 2026, the ICANN Board appointed them. Expertise entered through a committee of incumbents and acquired…

CASE FILE
A database governed by its entries: who gets a vote in PeeringDB?
A legal business entity can cross PeeringDB's membership threshold with two credentials: an active account and a representative or role subscribed to the governance list. The vote that follows is real. It is also only the first layer of authority over a database whose daily…

CASE FILE
The Tag Fit. The Authority Did Not: BGP Large Communities and the Namespace That Executes Policy
The route carried exactly the value the interconnection handbook prescribed. One provider acted on it, another erased it, and a third would have accepted the same instruction from a party that had never been authorized to give it. Twelve octets solved the numbering problem. They…

IETF
Jana Iyengar and the Connection That Outlived Its Address
A QUIC connection can continue when a device changes networks, but the old session cannot lend every old assurance to the new path. RFC 9000 preserves connection state narrowly, then demands fresh evidence for reachability, sending limits, congestion, ECN and privacy.
CASE FILE
The Route That Knew Nothing and Reached Everything: BGP Default Origination and the Authority of Last Resort
A customer still had an Established BGP session, a selected `0.0.0.0/0` and several successful probes. Most of the Internet had nevertheless become unreachable. The route with the widest scope had survived the loss of the service it was supposed to summarize.

CASE FILE
The Path Was Shorter Because the Evidence Was Gone: BGP ATOMIC_AGGREGATE and the Authority to Compress
The `/22` remained visible, its origin stayed valid and every external session was green. One of the four `/24`s beneath it had nevertheless disappeared. The public path looked cleaner at precisely the moment when the network knew less about the destinations it claimed to reach.