
Profile
Research
Research profile intelligence connects person, company, institution, and other entity coverage for readers comparing the subjects behind BTW.MEDIA reporting. The page helps compare public profiles, related events, evidence packs, role changes, operating footprints, governance exposure, organisational links, and market relevance while keeping organisation and people records distinct from ordinary news chronology. Readers can understand the subject behind the headline, the evidence supporting that profile, and the infrastructure or market relationships that make the profile relevant. They can see who or what the profile represents, which public sources support it, how it connects to companies, markets, governance bodies, or events, and what changes may deserve continued attention as the subject evolves.

History
The Window That Closed Without Ending the Connection: TCP Persist
When a TCP receiver says it has no room left, the sender stops sending ordinary data. The harder question is how either side escapes that pause if the one message announcing new room never arrives.

IETF
One Header Can Invalidate a Whole Site Section: RFC 9875 and HTTP Cache Groups
A response can label related stored responses inside one cache and one URI origin, while a later unsafe request can name those labels for possible invalidation. The useful boundary is local coordination, not a promise of synchronization across caches, CDNs, or origins.

IETF
Catalog Zones Turn a DNS Member List into Fleet-Wide Provisioning Authority
An empty file is usually absence. An empty DNS catalog can be an instruction. If a generator accidentally publishes a catalog without its members, every consumer that originally provisioned those zones from that catalog may begin removing them and their associated state. RFC 9432…
History
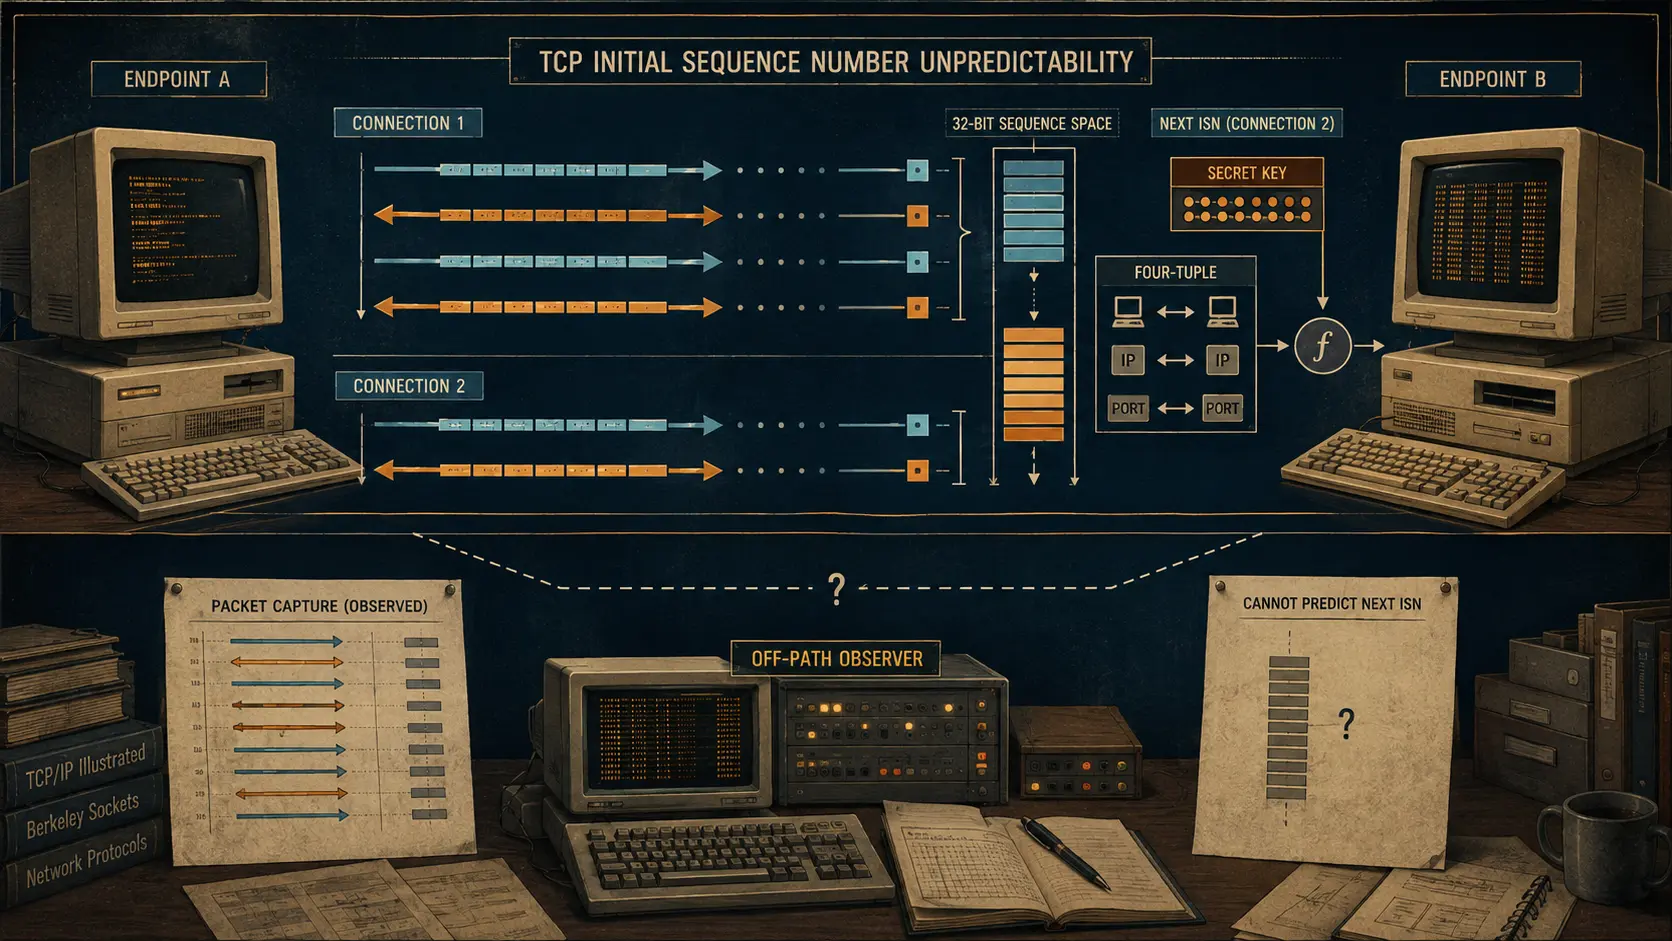
The Number Made Harder for an Off-Path Attacker to Predict: TCP Initial Sequence Numbers
A TCP connection begins by exchanging numbers. The security change was not to hide that exchange, but to stop one visible number from revealing the next connection's starting point.
ICANN
A Zone File Is Shared Access, Not Permission to Republish the Namespace
At 09:00, an approved researcher downloads a gTLD zone file through ICANN's Centralized Zone Data Service. The archive is complete enough for the contracted transfer, and its checksum matches. Those facts establish delivery. They do not establish who owns every listed domain, why…

IETF
One Delete Command Can Break Someone Else's Domain: RFC 9874 and EPP Dependency Control
A destructive EPP transition is not necessarily local to the client that requests it. When a subordinate host is still associated with domains sponsored by other clients, deleting that host can alter their DNS dependencies, consistency, and ability to resolve. RFC 9874 is a…

IETF
The Second Address Became the Primary One: What RFC 9873 Changes in EPP Contact Data
RFC 9873 turns a contact update into a more explicit state transition: an EPP contact may carry one additional email address, and an optional `primary` attribute says which address is to be treated as primary. The protocol records that relationship; it does not certify the…
IETF
Default Reject Turns Missing EBGP Policy from Silent Authority into an Explicit Failure
An external BGP session can be established while its authority to receive or advertise routes remains undefined. RFC 8212 changes the default at that boundary: without import policy, accept no routes; without export policy, announce none. The leadership question is not whether a…

History
The Chain That Made a Public Key Believable: PEM Certificate Management
A public key does not identify its owner by itself. RFC 1422 addressed that gap for Privacy Enhanced Mail by specifying certificates, certification authorities, validation paths, and revocation information—the institutional machinery needed before a relying party could treat a…

IETF
Enhanced uRPF Lets an Operator Admit Feasible Source Paths Without Trusting Every Route
A valid packet from a multihomed customer can arrive on a link that the receiving router would not choose for the return journey. Strict reverse-path forwarding may discard it; loose checking may accept any routed source. RFC 8704 defines a narrower middle ground: build an…
IETF
The Prefix Arrived Before the Query: How RFC 9872 Changes NAT64 Discovery
An IPv6-only host that must reach IPv4 services needs to know which IPv6 prefix its network uses for address synthesis. RFC 9872 turns that knowledge into an access-network signal: learn PREF64 from Router Advertisements first, and use DNS discovery only when that signal is…
History
The Pointer That Was Never Out of Band: TCP Urgent Data
TCP urgent data is a small control surface with a long history. The URG flag makes a 16-bit urgent pointer meaningful, but RFC 793 described the boundary it marks in two contradictory ways. That ambiguity crossed from the specification into implementations and application APIs.

IETF
ZONEMD Lets a Secondary Verify the Zone After the Transfer Ends
A completed zone transfer proves that a delivery procedure finished. It does not, by itself, prove that the receiver assembled the exact zone the publisher intended. ZONEMD adds a digest over the zone as a whole, creating a verification boundary after transport and before a…
IETF
The Bitmap Says a UDP Option Appeared—not What It Did: RFC 9870
RFC 9870 gives IPFIX exporters a compact way to report which UDP Option kinds appeared in a Flow. Its bitmaps are useful precisely because their claim is narrow: they preserve observed presence, not a packet history, a receiver’s processing decision or an application outcome.
IETF
A Negative Trust Anchor Lets the Resolver Suspend DNSSEC Without Changing the Zone
When a signed domain breaks, a validating recursive resolver can either preserve the failure or create a narrow local exception. A negative trust anchor restores reachability without repairing the zone, but it transfers temporary authority over DNS authentication to the resolver…

IETF
Mukul Srivastava and the BMP Gauge That Counted a RIB but Did Not See a Route
A number can be both useful and radically incomplete. RFC 9972 gives BMP operators a more precise way to report how many routes occupy a named RIB view at a particular moment. It does not turn that count into a route record, a policy explanation or a delivery observation. Mukul…

IETF
BGP Roles Turn a Peering Relationship into a Route-Leak Boundary
Before two networks exchange a single route, each can state what kind of neighbour it believes it has. RFC 9234 turns that bilateral statement into a control: incompatible roles can stop the session, while the Only-to-Customer attribute can stop a marked route from crossing the…

Leaders
Abdiel Marin and the Workflow Architecture Behind Specialty Eye Care Software
Abdiel Marin built EyeMD EMR around a practical premise: ophthalmology software has to follow the clinic's real work, not force clinicians into a generic record system. His operating decisions connected specialty imaging, interoperability standards, edge computing and patient…

IETF
Cédric Fournet and the Receipt That Did Not Make a Log Complete
A signed receipt can answer a sharp question about an entry and a particular tree state. It cannot, merely by looking formal, answer the larger question operators often want to ask: whether every event that mattered reached a complete, trusted and still-current log.

Leaders
Aaron Moreck and the Network-Service Decisions Behind NaaS and SD-WAN
Aaron Moreck’s public record sits at the operating edge of a regional technology company: network services, customer connectivity, managed firewalls and SD-WAN. The evidence supports a profile of a technical decision surface, not a claim that one director owns every customer…