
Profile
Research
Research profile intelligence connects person, company, institution, and other entity coverage for readers comparing the subjects behind BTW.MEDIA reporting. The page helps compare public profiles, related events, evidence packs, role changes, operating footprints, governance exposure, organisational links, and market relevance while keeping organisation and people records distinct from ordinary news chronology. Readers can understand the subject behind the headline, the evidence supporting that profile, and the infrastructure or market relationships that make the profile relevant. They can see who or what the profile represents, which public sources support it, how it connects to companies, markets, governance bodies, or events, and what changes may deserve continued attention as the subject evolves.

Story
RIPE Database 1.124.1 Fixed Certificate Selection. Its “No Evidence” Finding Needs a Search Boundary
RIPE NCC was right to ship a reported authentication vulnerability without waiting for a routine test interval. The next duty is different: show members what time, traffic and registry history were actually examined before “no evidence of exploitation” became the public…

IETF
Who pays to keep a search alive?
A mailbox search can finish correctly while its request for continuing updates is refused. IMAP makes that distinction explicit. The harder question is whether the product, its resource budget and its promises to users do the same.

IETF
An Enrollment Voucher Arrives After Identity Leaves the Device
A constrained device can withhold its operational identity and still disclose enough to be enrolled. In Lightweight Authorization using EDHOC, that disclosure is deliberate: an authenticated domain authenticator receives the device’s enrollment identity and sends it to a trusted…

IETF
The deadline arrived before permission to send
A scheduled email can ask a server to keep it still while a second instruction demands that it arrive sooner. SMTP's answer is not a faster queue. It is a refusal to accept incompatible obligations—and a careful division of responsibility for the promises that remain.

IETF
A Cryptographic Malfeasance Report Cannot Revoke Trust
Three time servers sign answers that cannot all be true in the order they were received. Roughtime lets a client preserve that contradiction as portable cryptographic evidence. Yet the proof does not name the guilty server, appoint the reviewer, alter a trusted-server list or…
IETF
The fallback folder was not an overflow bin
A mail filter can name both a preferred role and a default folder. Sieve does not treat that pair as a licence to put mail wherever storage happens to work. The distinction protects placement consistency—and leaves someone responsible for restoring the destination that failed.
Story
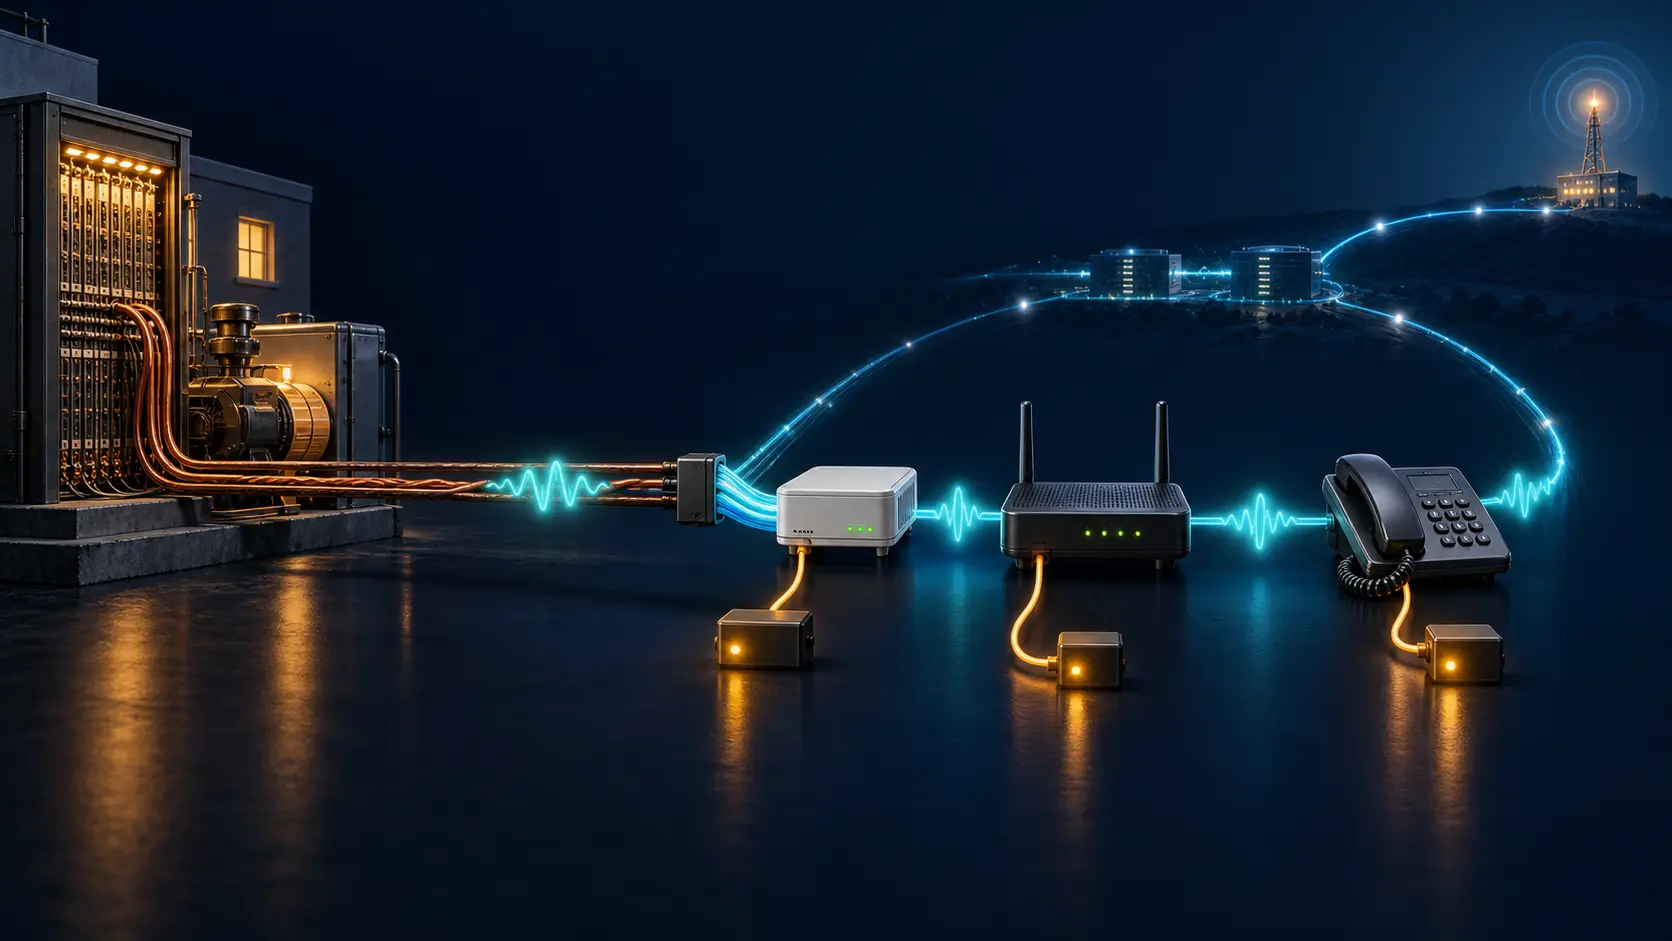
A LACNIC Telecom Essay Moves Voice to IP. It Leaves Backup Power Unassigned.
A new LACNIC Blog essay catches the most consequential detail in the retirement of traditional telephony: the call may look unchanged, but its power supply has moved. That observation deserves a more exact public answer about who keeps an IP call alive when the lights go out.
IETF
The recovered client that could not end everyone else's grace
After an NFSv4.1 server loses its lock state, the quickest client cannot decide when the slower ones have had enough time. Recovery completion is a withdrawal of its own remaining claims, not a command to reopen the whole service.
Story
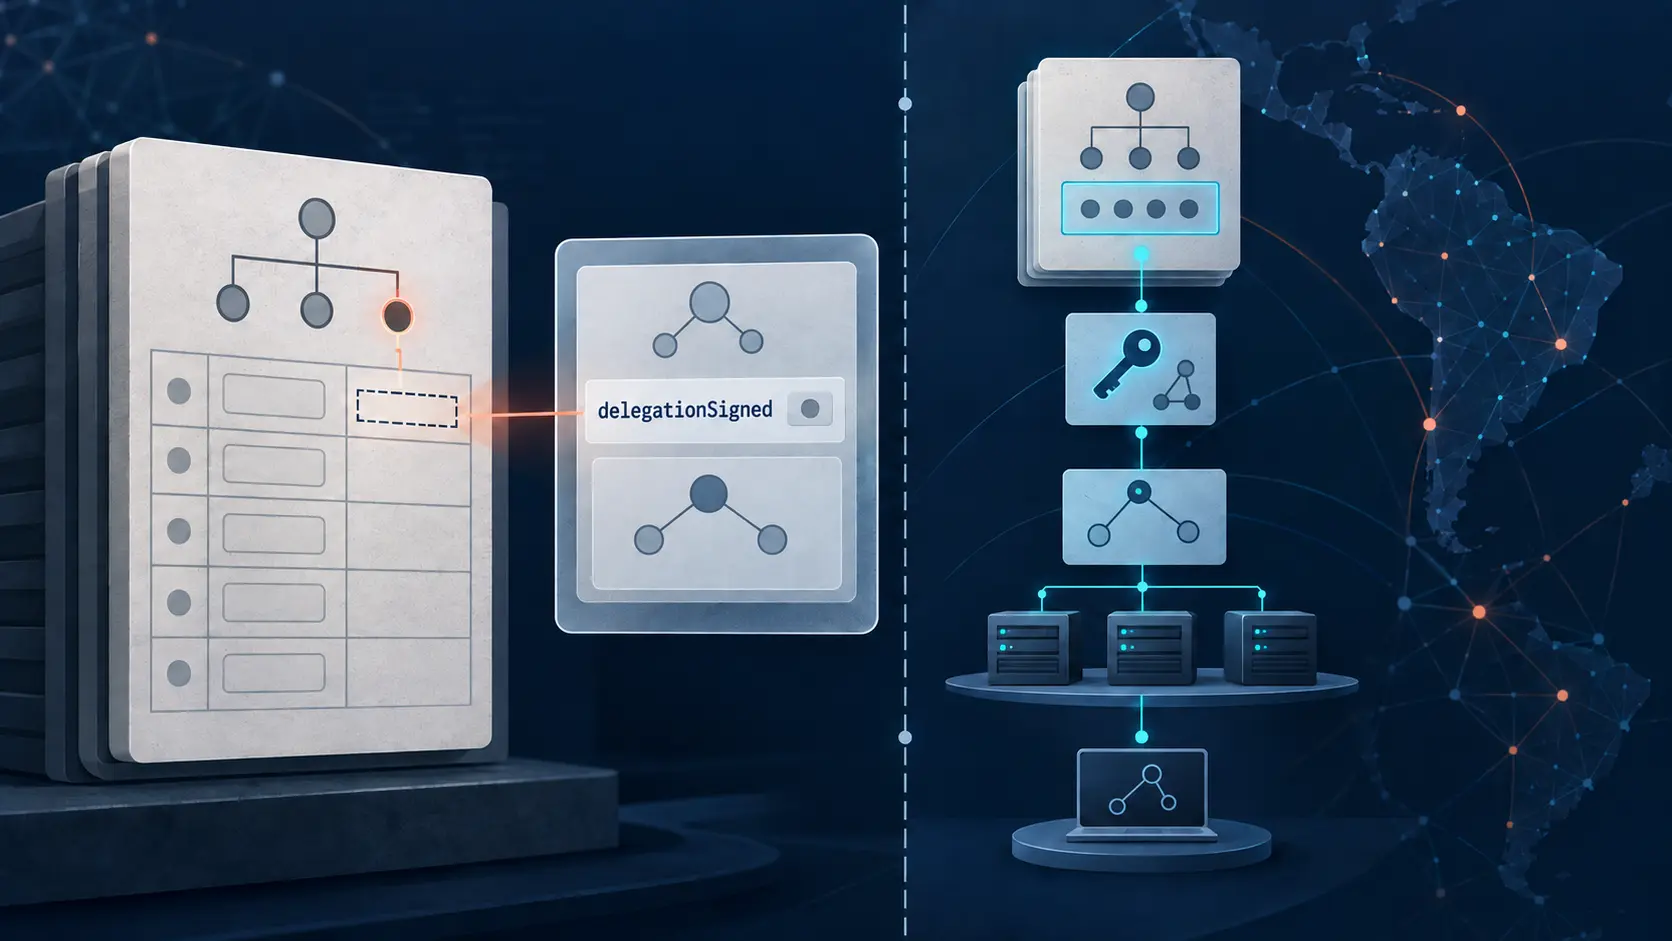
LACNIC's RDAP delegationSigned Records Parent DS Presence, Not DNSSEC Validation
A boolean in a registry response can look like a verdict on the security of a DNS chain. LACNIC's RDAP `delegationSigned` field answers a narrower question: whether the registration view reports DS records in the parent. It does not run a resolver, test the child keys or prove…

Global Institutional Trends
FreeBSD’s GRAND Work Shows Why a Faster Hello Needs Its Own Queue Rules
An account of proactive IPv6 discovery puts the less glamorous half of an optimisation in view: limiting announcements without treating ordinary replies as expendable duplicates.

IETF
A Private Candidate Does Not Explain Why One Intent Won
Two engineers are authorized to change the same router. Each works in a private configuration branch, so neither can accidentally commit the other’s unfinished commands. Then both change the same node. The server can identify the collision and offer disciplined ways to resolve…
IETF
The SCTP association that outlives its original socket
Peeling an established association out of a shared socket can contain buffer pressure. It also moves the place where that association must be controlled and closed.
IETF
MPTCP can keep the stream and lose the way back
After infinite-mapping fallback, regular TCP may keep carrying the bytes. The multipath capability cannot return on that same connection, leaving renewal to a different decision.

Global Datacenter Trends
NSD’s Second Certificate Rule Should Not Veto the First
NSD 4.15.2 repairs a zone-transfer check that could reject a legitimate client when another certificate identity was configured. The important unit of acceptance is the complete access rule, not the successful TLS handshake.
Global Datacenter Trends
FRRouting’s 34 Gbps Fix Makes Encoding Mode Part of the Upgrade Test
August maintenance releases correct the handling of large BGP bandwidth values. The useful acceptance question is not whether every peer now reports a bigger number, but whether each encoding produces the right one.

Story
ARIN Described a Two-Person Rule for AI Drafts. It Did Not Describe the Receipt
ARIN’s public answer was unusually concrete: generative AI may assist a narrow class of drafts, the drafter remains responsible, and a second person reviews the result before release. The missing piece is not another principle but the durable record that proves those decisions…

IETF
A YANG Minimum Version Is Not a Compatibility Floor
An importer asks for version 3.1.0 of a YANG module. On the shelf it finds 3.1.2 marked `_non_compatible` and 4.1.2, whose major number announces a breaking change. Both can satisfy the request. The result is not a loophole hidden in an implementation: it is the deliberately…

IETF
A second Netnews cancel lock can add another cancellation authority
A field that looks like extra protection can preserve a second actor’s ability to authenticate withdrawal. For an archive operator, the consequential questions are who retains the secret, which old articles it covers and what happens when the service relationship ends.

IETF
A guest TURN relay still needs an admission policy
Letting a visitor use a network’s communications relay without long-term credentials simplifies arrival. It does not decide whose capacity the visitor consumes—or who must return an allocation that the application never uses.

IETF
A Packet-Discard Counter Needs an Intent Epoch Before Automation Acts
At 02:14, an egress no-buffer counter starts climbing. The automation can move traffic in seconds. What it cannot see in the number is that a new service profile went live at 02:12, the line card restarted at 02:13, and the approved loss budget belongs to the configuration that…