
Impact
Medium
Within the Impact facet, Medium impact intelligence highlights articles where the expected effect level, operational exposure, or decision relevance is comparable. Readers can use the page to separate routine market updates from higher-consequence governance, infrastructure, security, and investment signals that may affect planning, procurement, policy, or customer exposure. The page connects the consequence band to public evidence, related organisations, regional context, operating dependencies, service continuity, competition, investment timing, compliance, and customer risk. It helps readers decide which developments deserve deeper monitoring, which actors are most exposed, and how a signal may affect operations or market planning.

Asia-Pacific Datacenter Trends
Sterlite’s Credit Upgrade Puts the Next Capex Cycle in Focus
A stronger credit rating recognises the optical-fibre maker’s financial reset. Keeping that improvement while it invests in equipment is a separate task.

ICANN
The ccNSO Council Plans No Comment on gTLD Abuse Rules
A 31 August notice says the country-code council does not intend to file a collective response to ICANN’s proposed gTLD abuse rules. It still invites individual operators to contribute—a useful distinction between sharing experience and accepting somebody else’s policy…

Global Cloud Services Trends
Netskope’s Annual Billing Shift Moves the Cash Test to the Second Half
Revenue guidance has risen, but the cash-flow target has narrowed. A change in payment terms helps explain why subscription growth and the money available to fund it can move on different schedules.

Global Cloud Services Trends
Snowflake's AI Budgets Follow Entry Points, Not Just Agents
A budget attached to a Cortex Agent does not necessarily follow every request that reaches it. Snowflake's treatment of CoWork-originated activity exposes a wider question for enterprise AI: where spending is counted, whose access can be stopped, and how long the stop takes to…

North America Regional ISP Trends
Rightfiber’s $1.6bn Facility Brings Build-or-Buy Choices Forward
The merged operator has financing for expansion and potential acquisitions. Turning that scope into paying connections requires careful sequencing while legacy customers stay on their existing arrangements.

Story
The Refill Behind LACNIC’s Falling ASN Forecast
The Refill Behind LACNIC’s Falling ASN Forecast intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that may follow. The Story intelligence…
ICANN
ICANN’s Diacritics Plan Would Tie Registry Exits Together
A new GNSO report would let certain ASCII and Latin-diacritic top-level domains operate together. The price of that exception is a shared operating future: related suffixes would move together when providers or control change, while removal would follow a different set of rules.
IETF
CATS OAM Can Verify a Steering Policy. It Cannot Choose a Remedy.
The active CATS OAM draft is trying to close a real visibility gap. A service instance can remain reachable at the network layer while the application behind it is slow, exhausted or unavailable. A system that steers traffic only by network reachability may therefore send clients…
North America Cloud Services Trends
ScanSource Buys MicroAge—and the Job of Settling Channel Conflicts
The US$220.5m acquisition gives ScanSource services to sell through its partners and an integrator that already sells to end users. Management says the distributor can adjudicate competing claims. The commercial test is whether that discretion makes partners more willing to bring…
Story
Inside AFRINIC’s Reverse-DNS Cleanup
The registry’s public data distinguish delegation records, domain entities and resource holders. They also distinguish an error inventory from removal events. Those differences explain why a falling count can reflect worthwhile maintenance without measuring the restoration of…

IETF
IETF's Survey Can Diagnose a Governance Problem. It Cannot Ratify a Repair.
The IETF Community Survey 2025 gives the organisation a more useful picture of itself than a slogan ever could: a large but imperfect sampling frame, a modest voluntary response, a clear account of what was counted, and a set of concerns that should not be wished away. That is…

CASE FILE
ITU’s Agent-Security Agenda Makes Deployment Part of the Test
A draft programme for ITU’s 7 September workshop asks what evidence integrators should demand from suppliers of agents, tools and models. That puts the security claim where the system acquires its powers—and raises a question about how far a supplier’s earlier test can travel.

Story
ARIN Publishes IPv6 Requests Beside Delegations. The Cohorts Are Not Joined.
An IPv6 request can enter ARIN’s system, pass automatically or move into staff review, prompt a request for more information, receive approval, wait for fees and a signed agreement, and only then become an issuance. ARIN publishes useful numbers at the entrance and the exit of…

IETF
IETF Separates Training Scripts From Slides. Now Test the Handover.
The IETF's latest training-procurement answers make captions, transcripts and narration scripts separate source assets. That is a useful move toward maintainable course material. Its value will become visible when someone other than the original producer has to correct a module.

Story
APNIC's Directory Terms Proposal Turns Query Access Into a Governance Question
Prop-173 would replace ambiguity around ordinary APNIC WHOIS and RDAP queries with a public, versioned acceptable-use policy. The consequential question is not whether terms should exist, but whether their rules distinguish legitimate operational reuse from a substitute data…
IETF
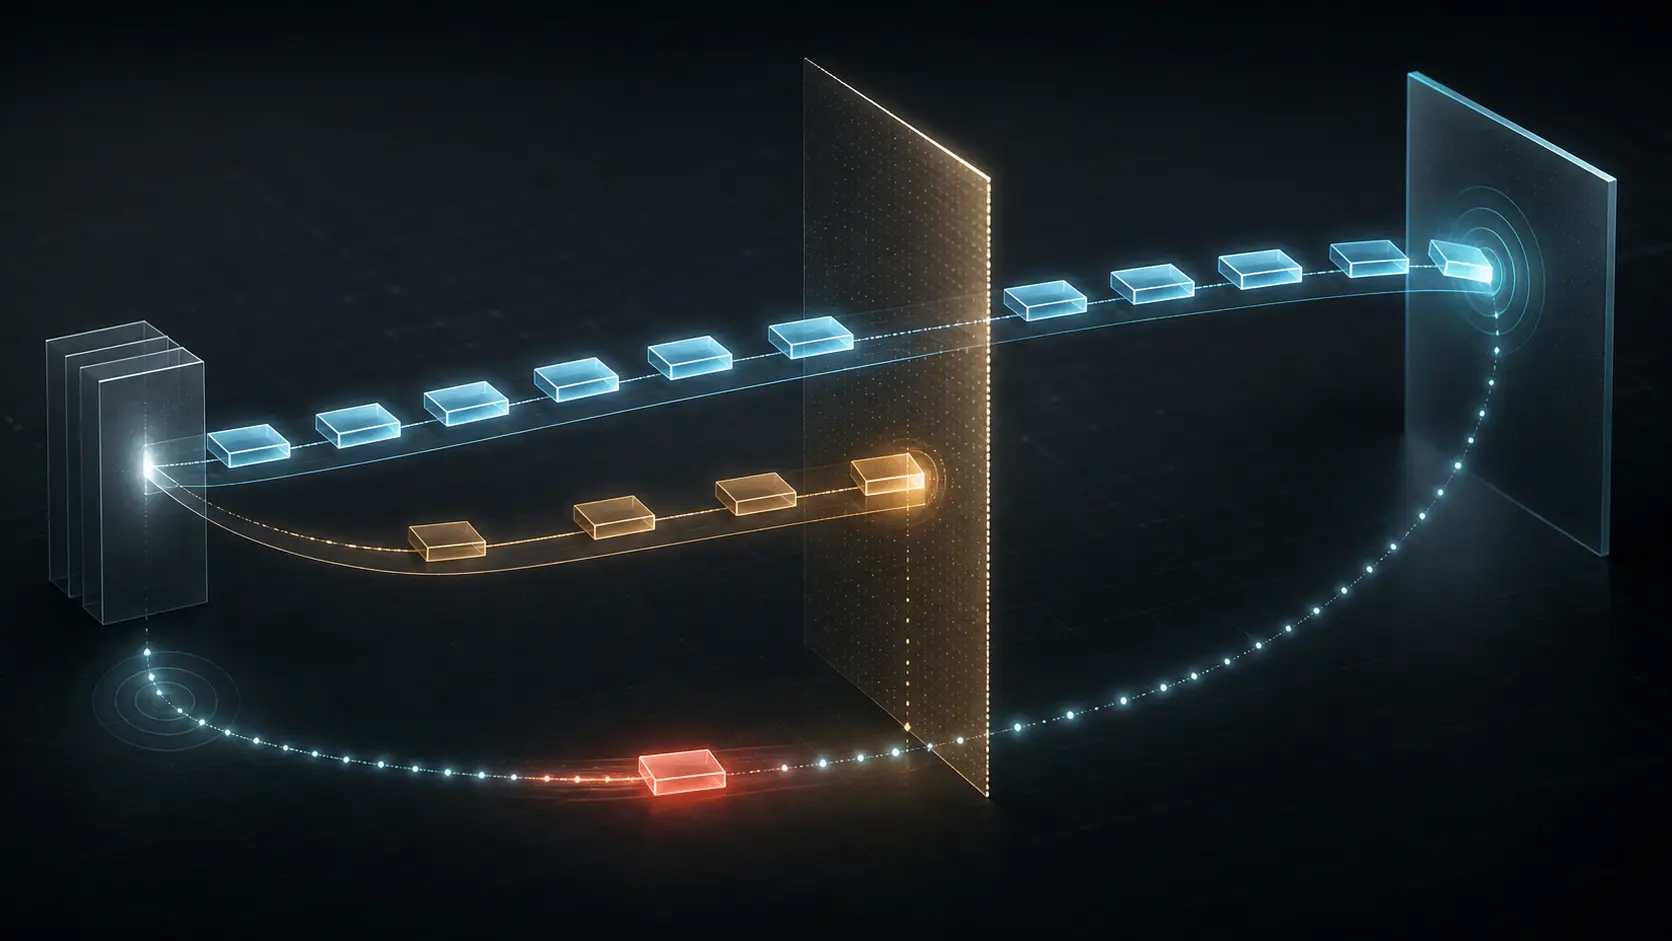
The Newer Packet Arrived First: How TCP RACK Used Time to Find Loss
RACK changes the evidence TCP can use when looking for loss: not only sequence-space gaps, but also the transmission times of data known to have arrived.

CASE FILE
WebAuthn's Report Has Four Browser Columns. Independence Needs a Key.
W3C's new WebAuthn Level 3 Recommendation links a fixed test report with four browser columns. The transition record adds that part of Chrome's implementation differs from Edge's. That caveat is important—and incomplete. Product names show where tests ran; they do not tell a…

Story
APNIC Can Define Internet Abuse Without Becoming Its Judge
Prop-172 would give APNIC policy a common vocabulary for abuse involving IP addresses. Its usefulness depends on a harder boundary: naming conduct must not quietly become authority for the registry to decide allegations, monitor networks or impose remedies.

CASE FILE
W3C's ARIA Implementation Report Says March. Its File Changed in May.
W3C's updated *ARIA in HTML* Recommendation points readers to an implementation report whose visible date is 22 March 2026. The public file history shows a large revision on 20 May and another change on 27 May. Both can be true: March may be the evidence cutoff and May the…

Leaders
Prawijaya Prawijaya and the Human Name Inside a Network Record
Prawijaya Prawijaya and the Human Name Inside a Network Record intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that may follow. The…