
Impact
Medium
Within the Impact facet, Medium impact intelligence highlights articles where the expected effect level, operational exposure, or decision relevance is comparable. Readers can use the page to separate routine market updates from higher-consequence governance, infrastructure, security, and investment signals that may affect planning, procurement, policy, or customer exposure. The page connects the consequence band to public evidence, related organisations, regional context, operating dependencies, service continuity, competition, investment timing, compliance, and customer risk. It helps readers decide which developments deserve deeper monitoring, which actors are most exposed, and how a signal may affect operations or market planning.
IETF
Dave Thaler: A Block Observation Is Not Policy Attribution
An unavailable page, a reset connection or an altered DNS answer can be a real observation. It does not, by itself, identify who made a policy, what they intended, or whether the effect was deliberate at all.

IETF
Suresh Krishnan: Link Up Is Not an End-to-End Reachability Receipt
A radio, Wi-Fi or wired interface can be ready to pass frames while the path a customer needs remains unresolved. Suresh Krishnan’s RFC 4957 is useful precisely because it keeps that boundary visible.

IETF
Peter van der Stok and the Resource Registration That Was Not Endpoint Presence
A directory can make a resource easier to find without making the resource present. That is the operational boundary in RFC 9176, the CoRE Resource Directory specification collectively authored by Peter van der Stok with Christian Amsüss, Zach Shelby, Michael Koster and Carsten…

Story
APNIC’s Resource Quality Check Is Not an Address Attribute
APNIC made a careful change in 2019: “assurance” became “check”. The distinction matters because a registry can observe routes, filters and reputation signals, but it cannot make thousands of other networks carry the result forward.

Global Cloud Services Trends
Kaleris Gained 25 EDI Links, Not One Repair Ledger
Newport Systems gives Kaleris an installed transport network between equipment owners and repair providers. The harder asset is common meaning for every estimate, authorisation, exception and invoice.
North America Datacenter Trends
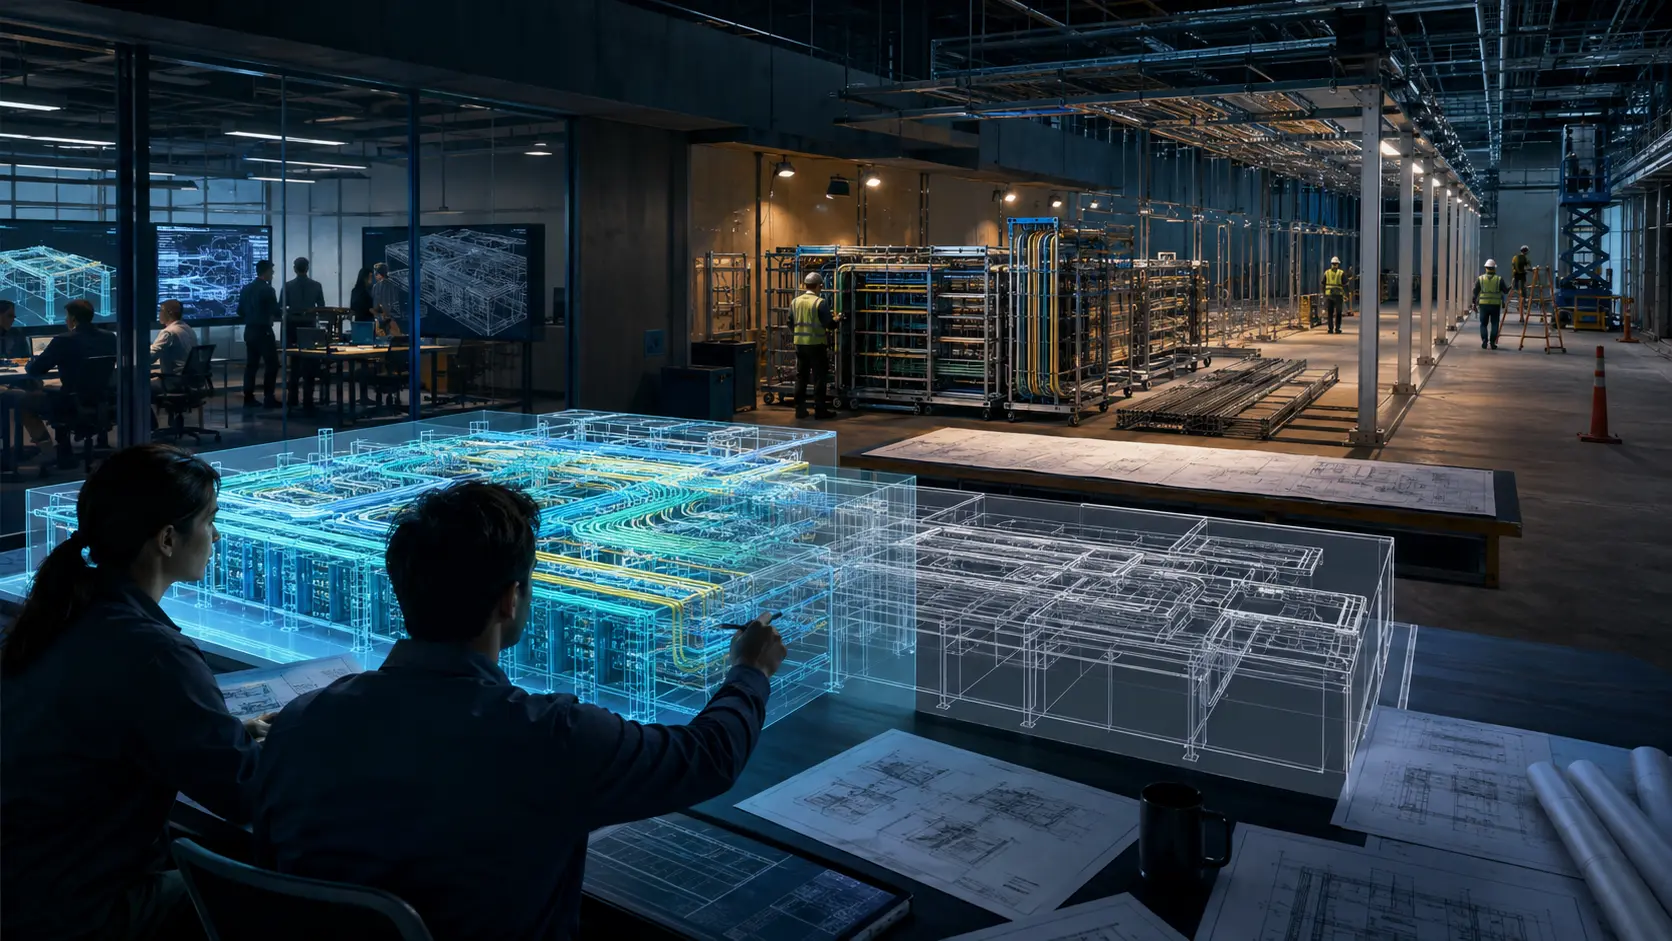
Augmenta's 8.5x clock stops at the first populated model
An 82-hour model-population result may be commercially useful on a large data-centre job. It is not yet a clock for design approval, fabrication, installation or the finished building.

CASE FILE
A Wikimedia Foundation Budget Has a Fiscal Clock, Not a Page-Level Editorial Verdict
A fiscal-year resolution has an unusually clean kind of clarity. It has a date, a decision-maker, a stated amount, a time period and an identified management path. A page-level editorial conclusion has a different kind of clarity: an applicable policy, evidence, discussion…

Story
A Locally Served DNS Root Has a Refresh Bill
Serving the root zone beside a recursive resolver removes many outward queries, but it does not remove network traffic. A new measurement highlighted by APNIC shows that the bill moves into the update loop—and that software behaviour can matter more than the name of the…
CASE FILE
At Kubernetes, a KEP Marked Implementable Is Neither a Release Inclusion Nor a Cluster-Support Promise
“Kubernetes approved the feature” can sound like a finished operational fact. The project’s public process says something more useful and more limited. An impacted SIG can approve a Kubernetes Enhancement Proposal for implementation; a release team can track a milestone; a…
CASE FILE
A CVE Record Is a Coordination Reference, Not a Patch or Remediation Receipt
The most useful thing a CVE record does is also the reason it is so easily overstated. It gives parties a stable way to mean the same vulnerability. That shared reference permits a finder, a CNA, a supplier, a distribution, a security team and an asset operator to exchange…

IETF
Rohan Mahy and the Certificate Purpose That Did Not Deliver an Instant Message
An IM certificate can say that a key is meant for an instant-messaging identity. That narrower purpose is useful security design. It does not say that an application submitted a message, that a service accepted it, or that any person received and read it.

IETF
Neil Jenkins and the StateChange That Did Not Audit a Mailbox
A JMAP client that sees a new state string has learned something important: its local view may no longer match the server. That is a signal to synchronize. It is not, by itself, a record of which message changed, which mailbox moved, which principal made a request, which policy…
North America Datacenter Trends
A 54-MW turnkey promise still needs an acceptance sequence
Northampton and Provident have formed a joint venture for a North Dallas data centre targeted for late 2027. The commercial test is how utility, fit-out, network and customer obligations turn a site figure into accepted computing capacity.

IETF
A Signature Is Not Proof of the Other Key: RFC 9883 and Private-Key Possession Statements
A second certificate request can be validly signed by an already certified signature key, yet that signature is only an assertion—not technical proof—that the requester controls the different private key behind the requested key-establishment certificate. RFC 9883 defines how a…

IETF
The Signature Algorithm Is Not the Signed Byte Sequence: RFC 9882 and ML-DSA in CMS
Two CMS systems choose ML-DSA-65 for identical content, yet verification fails when one signs a final implicit-tag representation and the other verifies the complete DER SignedAttrs value with its explicit SET OF tag. The algorithm is the same; the signed byte domain is not.

Story
APNIC prop-164 Turns Smaller IPv6 Allocations into a Reservation Test
APNIC prop-164 would let account holders begin with IPv6 allocations smaller than `/32` while preserving room for growth. The proposal may improve Whois and RDAP accuracy, but its durable test is whether reserved address space becomes a visible, reviewable registry commitment…

IETF
The Algorithm Name Is Not the Certificate Profile: RFC 9881 and ML-DSA in PKIX
The Algorithm Name Is Not the Certificate Profile: RFC 9881 and ML-DSA in PKIX intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that may…

IETF
A Registry TTL Is Policy State, Not a Live DNS Observation
RFC 10037 lets a registry publish configured DNS time-to-live values through RDAP. That sounds like a small JSON extension. Its more important effect is to expose a piece of registry policy without pretending that a registration-data service is watching the live DNS. The…

IETF
A Data Model Is Not a Wire Contract: RFC 9880 and SDF Protocol-Binding Boundaries
Two implementations can claim the same Thing model yet disagree on the wire: one chooses a URL and JSON payload convention, while the other expects a numeric identifier and different invocation rules. The gap appears when a protocol binding was implicit rather than versioned and…

Story
APNIC's Larger IPv4 Delegations Need a Queue Rule Before a Bigger Ceiling
APNIC's prop-168 would let eligible account holders grow toward an aggregated /22 while proposing a separate /12 transition reserve. The proposal defines who may ask and how much they may receive; its own scarcity arithmetic shows why it must also define who goes first when…