
Summary
- Before validating a peer address, a responding QUIC endpoint can send no more than three times the bytes it has received from that address.
- The ledger limits source-address-spoofed amplification during a specific protocol phase; it does not authenticate the client or remove other denial-of-service risks.
- Operators need byte-accounting and validation-transition evidence to distinguish a compliant pre-validation stall from loss, overload or attack.
Consider a server that receives a QUIC Initial datagram, prepares its handshake flight and sends until its permitted credit is exhausted. The remaining handshake bytes are ready. The network may still be reachable. The process may have ample CPU and memory. Yet the server must wait for more bytes from the client or for the client's address to become validated.
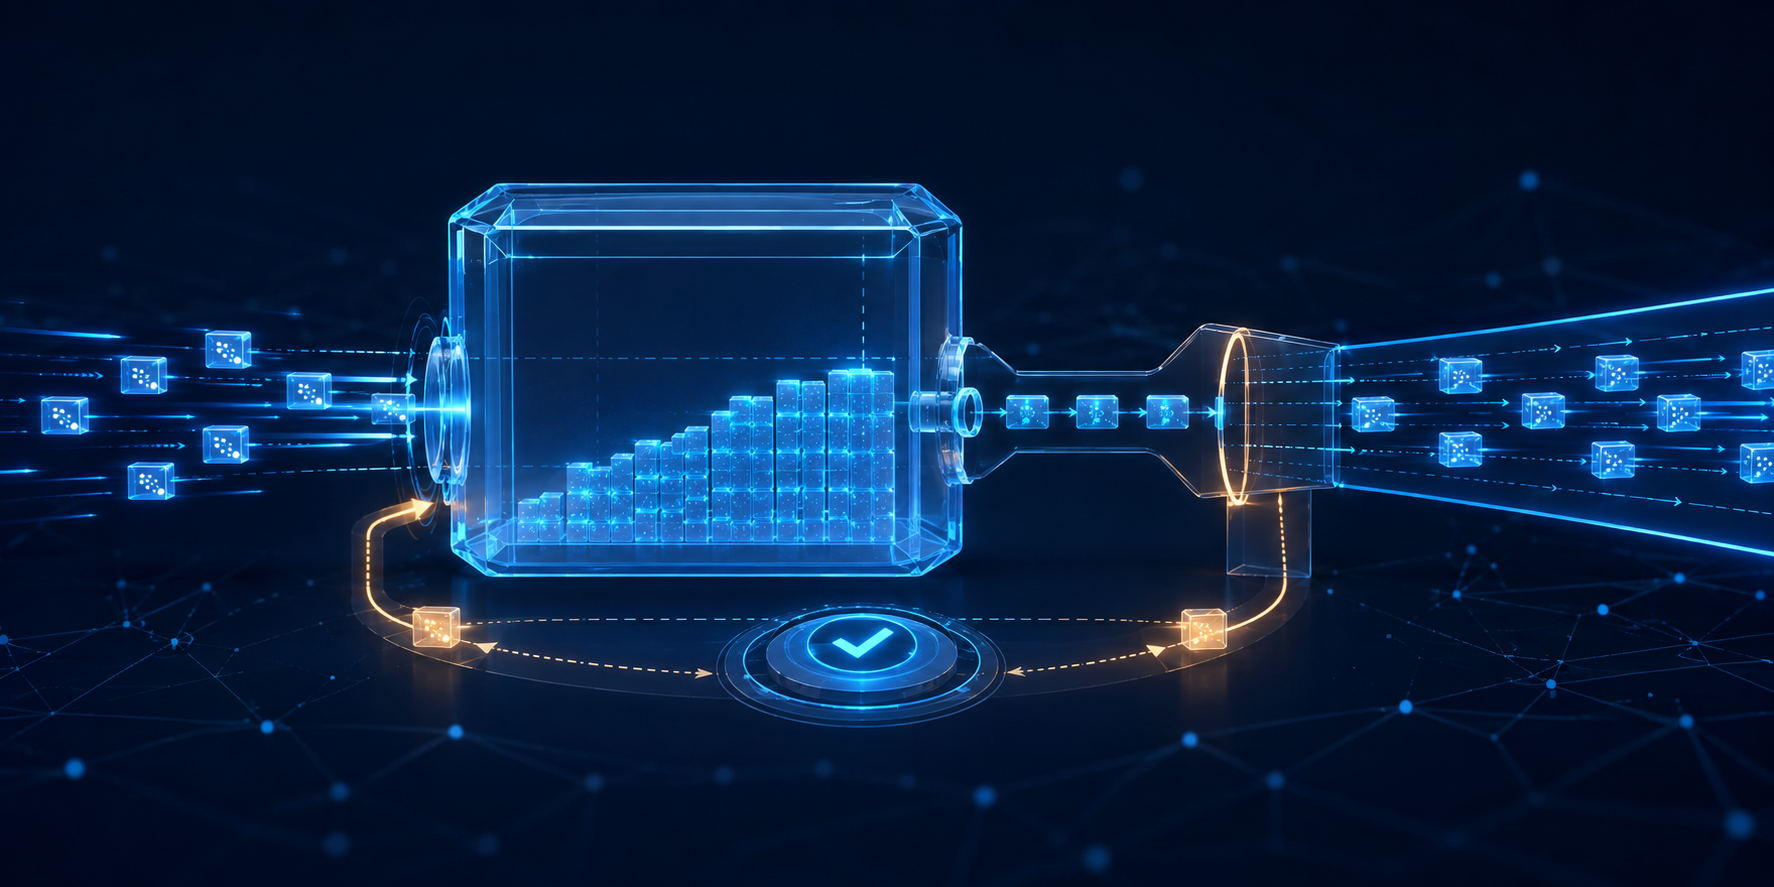
That pause is not an implementation curiosity. It is the visible consequence of a security boundary in RFC 9000. An attacker can forge a victim's source address and induce a server to direct traffic at the victim. QUIC limits this reflected traffic by requiring an endpoint that responds to an unvalidated address to send no more than three times the amount it has received from that address.
The useful mental model is a ledger. Bytes received from the unvalidated address increase the ceiling; bytes sent to it consume the available budget. The rule is cumulative for the relevant connection and address context. It is not permission to multiply each incoming packet independently, nor is “three times the last datagram” a sufficient implementation or monitoring record.
Section 8.1 applies that ledger during connection establishment. Before validating the client address, a server must count all payload bytes received in datagrams uniquely attributed to the connection. Loss can matter twice: a lost server flight consumes transmission budget, while a client that has received acknowledgements for everything it sent may have no reason to provide more incoming bytes. RFC 9000 describes the resulting possibility of deadlock at the anti-amplification limit.
This gives operations teams a precise alternative to vague labels such as “QUIC handshake timeout”. A useful incident record asks how many bytes were received from the unvalidated address, how many were sent, what the current ceiling was, when sending became limit-blocked, which handshake bytes remained pending, and whether new client traffic or address validation released the block. Without that evidence, packet loss, an exhausted validation budget and server resource pressure can look alike from a coarse request timer.
Address validation is itself a bounded claim. During connection establishment, the server can validate the address through protocol evidence such as receipt of a Handshake packet or successful token processing. Retry can require the client to demonstrate that it received a server-supplied token at the claimed address before the server commits to the larger handshake response.
For a new path, Section 8.2 defines a challenge-response reachability test for a specific pair of local and peer addresses. A matching PATH_RESPONSE validates the path on which the corresponding PATH_CHALLENGE was sent. A mere acknowledgement of the challenge packet is not enough, because RFC 9000 notes that such an acknowledgement can be spoofed.
None of those transitions proves who sits behind the address. They establish that the peer can receive packets at a transport address, or that presented token state satisfies the server's validation rules. They do not authenticate a subscriber, device, account or application. Converting reachability evidence into identity would give the protocol signal a claim it was not designed to make.
Validation also changes the scope of the three-times rule. Once the address is validated, the endpoint can send beyond that pre-validation ceiling. The connection remains governed by congestion control, flow control, cryptographic state and application policy, but the anti-amplification ledger is not a permanent rate cap. A dashboard that keeps applying it after validation will invent throttling that the transport does not require.
The reverse mistake is to market the ledger as complete DDoS protection. RFC 9000 Section 21.2 discusses handshake denial of service, while Section 21.9 covers abuse that consumes processing or connection state. Separately, Section 21.3 describes residual amplification risk involving validation tokens and address reassignment. A three-times bandwidth bound before validation does not price CPU work, memory commitment, connection-table occupancy, authenticated floods, post-validation application load or every form of request forgery.
As an editorial operational recommendation, separate three questions in telemetry. First, is the peer address unvalidated, and what exact evidence will change that state? Second, what are the received, sent and remaining byte totals for that address context? Third, are independent resource controls showing pressure in packet rate, CPU, memory or connection state? The first two explain the protocol budget. The third addresses the wider denial-of-service problem.
As an editorial operational recommendation, the resulting receipt should travel with every diagnosis: connection and path identifier; local and peer IP/port tuple; observation time; validation state and transition; validation method; bytes received from the unvalidated address; bytes sent to it; current three-times ceiling; remaining budget; handshake-flight bytes pending; Retry or token result; PATH_CHALLENGE/PATH_RESPONSE result where applicable; loss and retransmission context; first and last limit-blocked timestamps; outcome after validation; and separate indicators for CPU, memory, connection-state and packet-rate pressure.
That record makes the boundary legible. The three-times rule can show that a server correctly constrained traffic toward an address it had not yet validated. It cannot show that the client was legitimate, that the service had enough capacity, that no attack occurred, or that every later byte was safe.
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance