
Content Type
Research
Within the Content Type facet, Research intelligence gathers BTW.MEDIA articles that share the same editorial format, helping readers compare briefings, profiles, risk notes, market analysis, and event coverage without mixing different kinds of evidence. The page explains how this content type frames internet infrastructure events, company movements, governance decisions, operational signals, and public evidence across the site. Readers can compare which actors or infrastructure systems appear most often, how source quality changes interpretation, and whether the material is a durable profile, a time-sensitive event, a strategic market signal, or a governance development. The result is a useful search page for operators, investors, customers, analysts, and policy stakeholders who need to understand the consequence, timing, and evidence behind similar article formats.

IETF
A Key Transparency Proof Cannot Audit Who Was Allowed to Look
Alice searches a Key Transparency log for Bob and receives a valid proof. Fred makes the same request and is stopped by the application before the log sees it. The proof can show that Alice’s answer fits an authenticated, globally consistent tree. It cannot show why Alice was…

IETF
The Stream Was Ordered. The Network Was Not Yet Proven
At the instant a controller receives `<rpc-reply><ok/></rpc-reply>`, the change can feel complete. The bytes arrived in order, the peer was authenticated, and the server returned success. Yet each of those facts belongs to a different evidentiary layer from the question operators…

IETF
Agent Discovery Leaks Intent Before Any Agent Is Chosen
A procurement agent asks for a French-hosted inference service that accepts a rare credential, supports a particular model family and can start within an hour. No supplier has been contacted and no agent has been selected. Yet the query has already described the buyer’s…

History
George Varghese and the Deficit Counter That Made Round Robin Count Bytes
Round robin looks fair when a scheduler gives every queue one turn. On a packet link, however, turns are not equal units: one queue may send 1,500 bytes while another sends 500. M. Shreedhar and George Varghese changed the accounting unit. Deficit Round Robin lets each queue…

History
Jennifer Rexford and the Nearest BGP Exit That Was Never an End-to-End Optimum
An engineer changes one interior link weight. No external route is withdrawn, no new neighbour appears, and the destination prefix stays the same. Yet traffic leaves through another border router. Jennifer Rexford and her collaborators made this seam between IGP and BGP visible…

IETF
An RPKI Validator Needs an Audit Trail, Not Just a Green Cache
The routing dashboard is green at 09:10. At 09:40 a repository refresh succeeds, the cache changes and the earlier state disappears. When an operator later asks which RPKI objects, failures, trust anchors and local exceptions informed a route decision at 09:10, the green light…
IETF
The Envelope Parsed. The Observation Is Not Yet Proven
`draft-ietf-netconf-notif-envelope-05` gives YANG-Push notifications a header that can travel with the message. That makes correlation easier. It does not collapse identity, continuity, time, provenance and operational truth into one successful parse.

IETF
A Delegation Chain Narrows Authority but Cannot Carry Intent
An OAuth resource server may one day receive a chain whose signatures, key links, audiences, time bounds and permission subsets all validate. That green result would be meaningful: no downstream client could have validly enlarged the authority it received. It would still leave a…

CASE FILE
The Two Routes Arrived. Their Bits Still Did Not Belong Together: RFC 9819
An ingress PE can possess the two BGP advertisements required to construct an SRv6 Service SID and still lack permission to treat their bits as one executable instruction. RFC 9819 makes the missing proof visible: identity, argument size, insertion boundary, local acceptance…
CASE FILE
The Datastore Was Complete. The Control Plane Was Still Unproven: RFC 9826
A clean PCEP management tree can show an entity, its peers, live-looking sessions, notifications and counters in one coherent view. That coherence is a major operational gain. It is also where evidence from a management projection is most easily mistaken for proof of the network…

IETF
The Message Reassembled. The Telemetry May Still Be Incomplete
`draft-ietf-netconf-udp-notif-26` makes high-frequency YANG notifications cheaper to move across a controlled network. It also makes an important distinction unavoidable: transport evidence can show what a receiver assembled, but only a wider chain can show what the network…
IETF
RFC 10041 Makes OSPF Unreachability an Area-Wide Decision
The hexadecimal value `0xffff` can describe a link that remains reachable at the highest cost or a link that must be excluded from a shortest-path calculation. RFC 10041 does not resolve that ambiguity with a local switch. It makes the meaning depend on evidence from every router…

IETF
The First Packet Left Before the Image Existed. It Still Did Not Prove Low Latency: RFC 9828
A sender can now begin carrying a JPEG 2000 image while that image is still being encoded. That is a useful reduction in one waiting stage. It is not a receipt for the time at which a receiver recovered, decoded and displayed a usable picture.
IETF
The Merge Was Clean. The Baseline May Not Be: NETCONF Private Candidates
`draft-ietf-netconf-privcand-10` gives each client a private place to prepare configuration and a defined way to detect and resolve overlap before commit. The operational mistake would be to let isolation, an empty comparison or a successful merge inherit authority over…
IETF
RFC 10003 Makes CMC Transport a Separate Evidence Layer
A CMC request can cross HTTP successfully and still be pending, rejected or incomplete at the certificate authority. RFC 10003 gives the carrier a precise form; RFC 10002 gives the PKI operation its result. Governance fails when those two receipts are collapsed into one green…
Story
DAOport’s RIPE NCC Membership Shows Governance Access, Not Yet an Operating Network
DAOport’s RIPE NCC Membership Shows Governance Access, Not Yet an Operating Network intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that…

Global Cloud Services
AlmazCloud’s AS210328: What the Public Record Can—and Cannot—Verify
A fresh review of the available registry, routing, DNS, web, certificate and PeeringDB sources finds a useful monitoring baseline, but not a verified operating or customer-service footprint. The central distinction is between a recorded network identity, an independently observed…

CASE FILE
Internet Society’s Authority Has a Documented Structure, but Its Remedies Remain Conditional
The Internet Society’s public governance record points to a layered institution rather than a single source of power. Its articles of incorporation, bylaws, Board of Trustees and the District of Columbia nonprofit statute occupy different positions in that structure. The…
Global Cloud Services
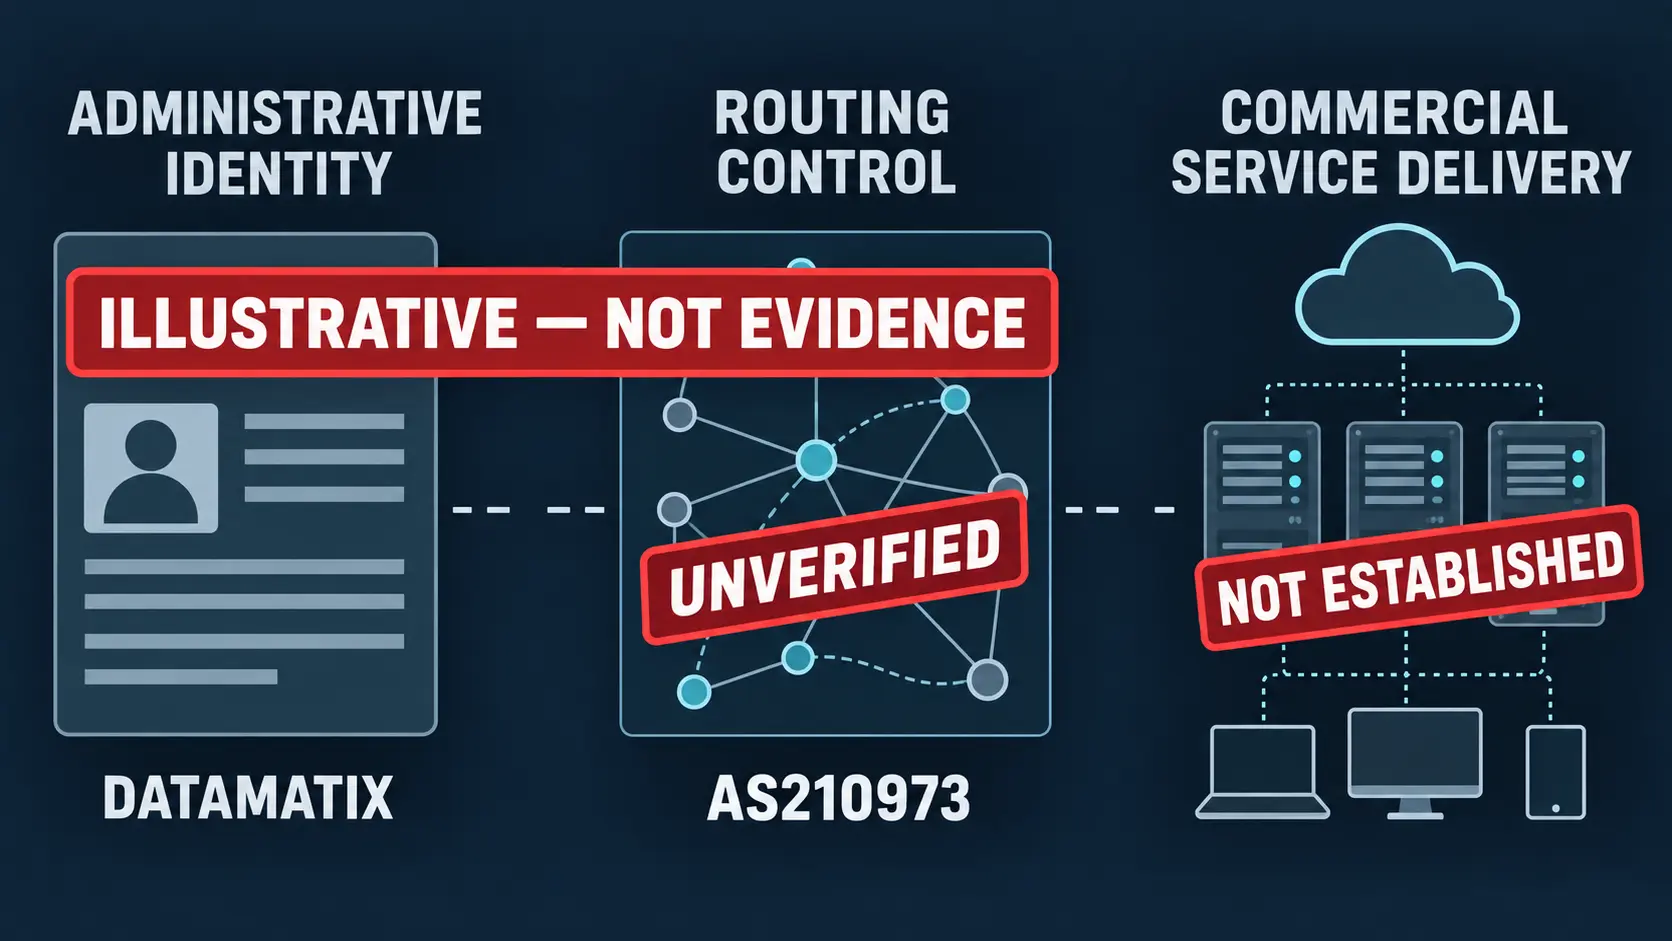
DATAMATIX and AS210973: The Operating Business Still Has to Be Proven
DATAMATIX and AS210973: The Operating Business Still Has to Be Proven intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that may follow.…

IETF
The Transform Was Agreed. The Replay Was Not Yet Rejected: RFC 9827
RFC 9827 gives IKEv2 a broader and more honest contract for packet sequence numbers. The selected Transform ID describes what should be true when an SA's packets enter the network; it does not certify sender coordination, receiver anti-replay policy, the packet stream that…