
Content Type
Research
Within the Content Type facet, Research intelligence gathers BTW.MEDIA articles that share the same editorial format, helping readers compare briefings, profiles, risk notes, market analysis, and event coverage without mixing different kinds of evidence. The page explains how this content type frames internet infrastructure events, company movements, governance decisions, operational signals, and public evidence across the site. Readers can compare which actors or infrastructure systems appear most often, how source quality changes interpretation, and whether the material is a durable profile, a time-sensitive event, a strategic market signal, or a governance development. The result is a useful search page for operators, investors, customers, analysts, and policy stakeholders who need to understand the consequence, timing, and evidence behind similar article formats.

History
The Acknowledgment That Waited for a Second Segment: TCP Delayed ACKs
TCP does not always answer one received data segment with one immediate acknowledgment. The receiver may wait briefly, but that silence is governed by a second-segment threshold, a timer, and exceptions that preserve loss evidence.

IETF
QNAME Minimisation Is a Query-Sequence Contract, Not a Privacy Switch
A resolver may advertise QNAME minimisation while exposing very different names, costs and failure modes from one lookup to the next. The feature matters only when operators can reconstruct the bounded sequence produced by delegation knowledge, cache state and negative proofs.

IETF
An SRv6 Locator Lease Makes DHCPv6 Part of the Routing Control Plane
An SRv6 locator is the address-space foundation from which a segment endpoint creates SIDs. RFC 10038 allows that foundation to arrive as a DHCPv6 lease. The convenience is real, but so is the transfer of authority: pool selection, lease renewal, route installation and withdrawal…

IETF
A Header Allowed Here Is Not Trusted Everywhere: RFC 9878 and SIP P-Header Scope
A call can fail at the trust boundary when a sender puts a P-Header in a SIP message that its receiver believes must not contain it. One implementation strips the field, another rejects the message, and a third accepts it. The disagreement can affect charging context…

CASE FILE
The Registrant Was Abroad; the Dot-Com Registry Was in Virginia: CNN v CNNews.com
The Registrant Was Abroad; the Dot-Com Registry Was in Virginia: CNN v CNNews.com intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that…

IETF
The Link Is Not the Location: RFC 9877 and RDAP Geofeed Control
A geofeed link tells a client where to look; it does not turn every location claim in that file into verified truth. RFC 9877 makes RDAP a scoped discovery and authority signal, with controls that keep lookup scope, freshness, authenticity and privacy separate.

History
The Window That Refused to Open One Byte at a Time: TCP Silly Window Syndrome Avoidance
A TCP receiver can have room for more data without advertising that room immediately. That deliberate silence prevents a small permission from becoming a self-repeating stream of small packets.

IETF
A Two-Byte Number Can Lie About the Payload: RFC 9876 and CoAP Registry Control
CoAP defines Content-Format as a small integer that identifies a payload's media type and any content coding. RFC 9876 makes the registration procedure behind that integer stricter, because the code point is meaningful only when its media type, parameters, coding and semantics…

BDNOG
bdNOG Publishes Who Oversees Its Executive Committee, Not How
bdNOG’s public governance pages draw a clean line: the Board is the highest authority, while the Executive Committee (EC) manages the community’s work. The Board page says it approves yearly activities and holds the EC accountable. The EC page names the operating committee and…

IETF
A Resolver Can Choose Encryption Before DNS Operators Coordinate
Encryption between a user and a recursive DNS resolver does not protect the next hop. The resolver may still send the resulting query in cleartext to an authoritative server, exposing another part of the path to passive observation. RFC 9539 proposes an experimental compromise…

History
The Window That Closed Without Ending the Connection: TCP Persist
When a TCP receiver says it has no room left, the sender stops sending ordinary data. The harder question is how either side escapes that pause if the one message announcing new room never arrives.

IETF
One Header Can Invalidate a Whole Site Section: RFC 9875 and HTTP Cache Groups
A response can label related stored responses inside one cache and one URI origin, while a later unsafe request can name those labels for possible invalidation. The useful boundary is local coordination, not a promise of synchronization across caches, CDNs, or origins.

IETF
Catalog Zones Turn a DNS Member List into Fleet-Wide Provisioning Authority
An empty file is usually absence. An empty DNS catalog can be an instruction. If a generator accidentally publishes a catalog without its members, every consumer that originally provisioned those zones from that catalog may begin removing them and their associated state. RFC 9432…
History
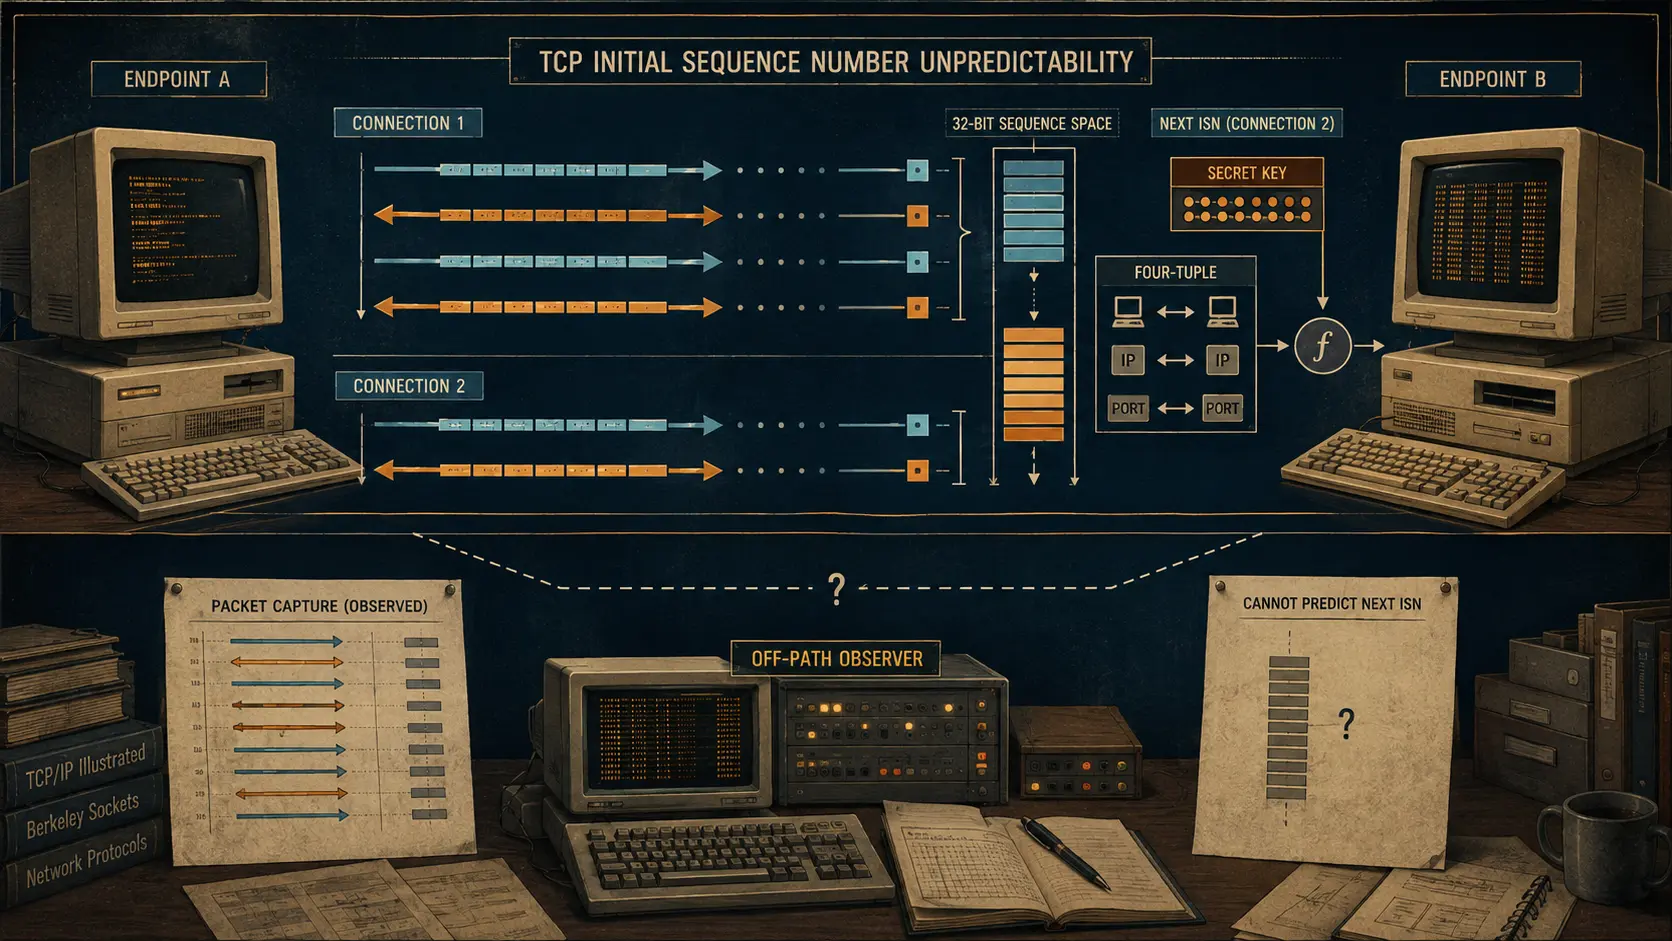
The Number Made Harder for an Off-Path Attacker to Predict: TCP Initial Sequence Numbers
A TCP connection begins by exchanging numbers. The security change was not to hide that exchange, but to stop one visible number from revealing the next connection's starting point.
ICANN
A Zone File Is Shared Access, Not Permission to Republish the Namespace
At 09:00, an approved researcher downloads a gTLD zone file through ICANN's Centralized Zone Data Service. The archive is complete enough for the contracted transfer, and its checksum matches. Those facts establish delivery. They do not establish who owns every listed domain, why…

IETF
One Delete Command Can Break Someone Else's Domain: RFC 9874 and EPP Dependency Control
A destructive EPP transition is not necessarily local to the client that requests it. When a subordinate host is still associated with domains sponsored by other clients, deleting that host can alter their DNS dependencies, consistency, and ability to resolve. RFC 9874 is a…

IETF
The Second Address Became the Primary One: What RFC 9873 Changes in EPP Contact Data
RFC 9873 turns a contact update into a more explicit state transition: an EPP contact may carry one additional email address, and an optional `primary` attribute says which address is to be treated as primary. The protocol records that relationship; it does not certify the…
IETF
Default Reject Turns Missing EBGP Policy from Silent Authority into an Explicit Failure
An external BGP session can be established while its authority to receive or advertise routes remains undefined. RFC 8212 changes the default at that boundary: without import policy, accept no routes; without export policy, announce none. The leadership question is not whether a…

History
The Chain That Made a Public Key Believable: PEM Certificate Management
A public key does not identify its owner by itself. RFC 1422 addressed that gap for Privacy Enhanced Mail by specifying certificates, certification authorities, validation paths, and revocation information—the institutional machinery needed before a relying party could treat a…

IETF
Enhanced uRPF Lets an Operator Admit Feasible Source Paths Without Trusting Every Route
A valid packet from a multihomed customer can arrive on a link that the receiving router would not choose for the return journey. Strict reverse-path forwarding may discard it; loose checking may accept any routed source. RFC 8704 defines a narrower middle ground: build an…