
Content Type
Research
Within the Content Type facet, Research intelligence gathers BTW.MEDIA articles that share the same editorial format, helping readers compare briefings, profiles, risk notes, market analysis, and event coverage without mixing different kinds of evidence. The page explains how this content type frames internet infrastructure events, company movements, governance decisions, operational signals, and public evidence across the site. Readers can compare which actors or infrastructure systems appear most often, how source quality changes interpretation, and whether the material is a durable profile, a time-sensitive event, a strategic market signal, or a governance development. The result is a useful search page for operators, investors, customers, analysts, and policy stakeholders who need to understand the consequence, timing, and evidence behind similar article formats.

IETF
ZONEMD Lets a Secondary Verify the Zone After the Transfer Ends
A completed zone transfer proves that a delivery procedure finished. It does not, by itself, prove that the receiver assembled the exact zone the publisher intended. ZONEMD adds a digest over the zone as a whole, creating a verification boundary after transport and before a…
IETF
The Bitmap Says a UDP Option Appeared—not What It Did: RFC 9870
RFC 9870 gives IPFIX exporters a compact way to report which UDP Option kinds appeared in a Flow. Its bitmaps are useful precisely because their claim is narrow: they preserve observed presence, not a packet history, a receiver’s processing decision or an application outcome.
IETF
A Negative Trust Anchor Lets the Resolver Suspend DNSSEC Without Changing the Zone
When a signed domain breaks, a validating recursive resolver can either preserve the failure or create a narrow local exception. A negative trust anchor restores reachability without repairing the zone, but it transfers temporary authority over DNS authentication to the resolver…

IETF
Mukul Srivastava and the BMP Gauge That Counted a RIB but Did Not See a Route
A number can be both useful and radically incomplete. RFC 9972 gives BMP operators a more precise way to report how many routes occupy a named RIB view at a particular moment. It does not turn that count into a route record, a policy explanation or a delivery observation. Mukul…

IETF
BGP Roles Turn a Peering Relationship into a Route-Leak Boundary
Before two networks exchange a single route, each can state what kind of neighbour it believes it has. RFC 9234 turns that bilateral statement into a control: incompatible roles can stop the session, while the Only-to-Customer attribute can stop a marked route from crossing the…

Leaders
Abdiel Marin and the Workflow Architecture Behind Specialty Eye Care Software
Abdiel Marin built EyeMD EMR around a practical premise: ophthalmology software has to follow the clinic's real work, not force clinicians into a generic record system. His operating decisions connected specialty imaging, interoperability standards, edge computing and patient…

IETF
Cédric Fournet and the Receipt That Did Not Make a Log Complete
A signed receipt can answer a sharp question about an entry and a particular tree state. It cannot, merely by looking formal, answer the larger question operators often want to ask: whether every event that mattered reached a complete, trusted and still-current log.

Leaders
Aaron Moreck and the Network-Service Decisions Behind NaaS and SD-WAN
Aaron Moreck’s public record sits at the operating edge of a regional technology company: network services, customer connectivity, managed firewalls and SD-WAN. The evidence supports a profile of a technical decision surface, not a claim that one director owns every customer…
IETF
CATS OAM Can Verify a Steering Policy. It Cannot Choose a Remedy.
The active CATS OAM draft is trying to close a real visibility gap. A service instance can remain reachable at the network layer while the application behind it is slow, exhausted or unavailable. A system that steers traffic only by network reachability may therefore send clients…

Leaders
Amit Thapa Chhetri and the Long Build Behind Nepal's Cable Internet
Subisu's origin was not a clean founder myth. The public record instead shows a team testing an idea against a regulatory system that was not yet ready for it, then carrying the operating work forward until the venture became an institution. Amit Thapa Chhetri's role is useful…

IETF
IETF's Survey Can Diagnose a Governance Problem. It Cannot Ratify a Repair.
The IETF Community Survey 2025 gives the organisation a more useful picture of itself than a slogan ever could: a large but imperfect sampling frame, a modest voluntary response, a clear account of what was counted, and a set of concerns that should not be wished away. That is…

SANOG
SANOG 34 Moved Cities Without Publishing Its Crisis Authority Chain
SANOG 34 did something operationally difficult: it moved a regional conference from Colombo to Kolkata for what SANOG described as the recent security situation in Sri Lanka, while keeping the dates intact. SANOG's own archive records the move, names the original and replacement…
IETF
Thomas Graf and the MPLS Label Number That Did Not Identify Its Control Plane
An MPLS label can look like an answer: a compact number at the top of a stack, captured in an export record and ready to be counted. Thomas Graf’s RFC 9160 begins with the smaller, more useful proposition. The number alone does not reliably tell an observer which control-plane…

IETF
SCITT Can Log a Statement. It Cannot Authorize a Release.
RFC 9943 gives software-supply-chain evidence a useful public property: a signed statement can be recorded in a transparency service and accompanied by a verifiable receipt. That can make an issuer’s assertion easier to inspect and harder to rewrite quietly. It does not answer…

IETF
DNSOP Can Recommend a Domain-Control Check. It Cannot Govern an Application Identity’s Lifecycle.
The DNSOP working group is in Last Call on a useful document about applications that use global-DNS names as identifiers. Its central discipline is easy to miss. A service may need proof that a registrant or an authorized party controls a domain when an integration is…
IETF
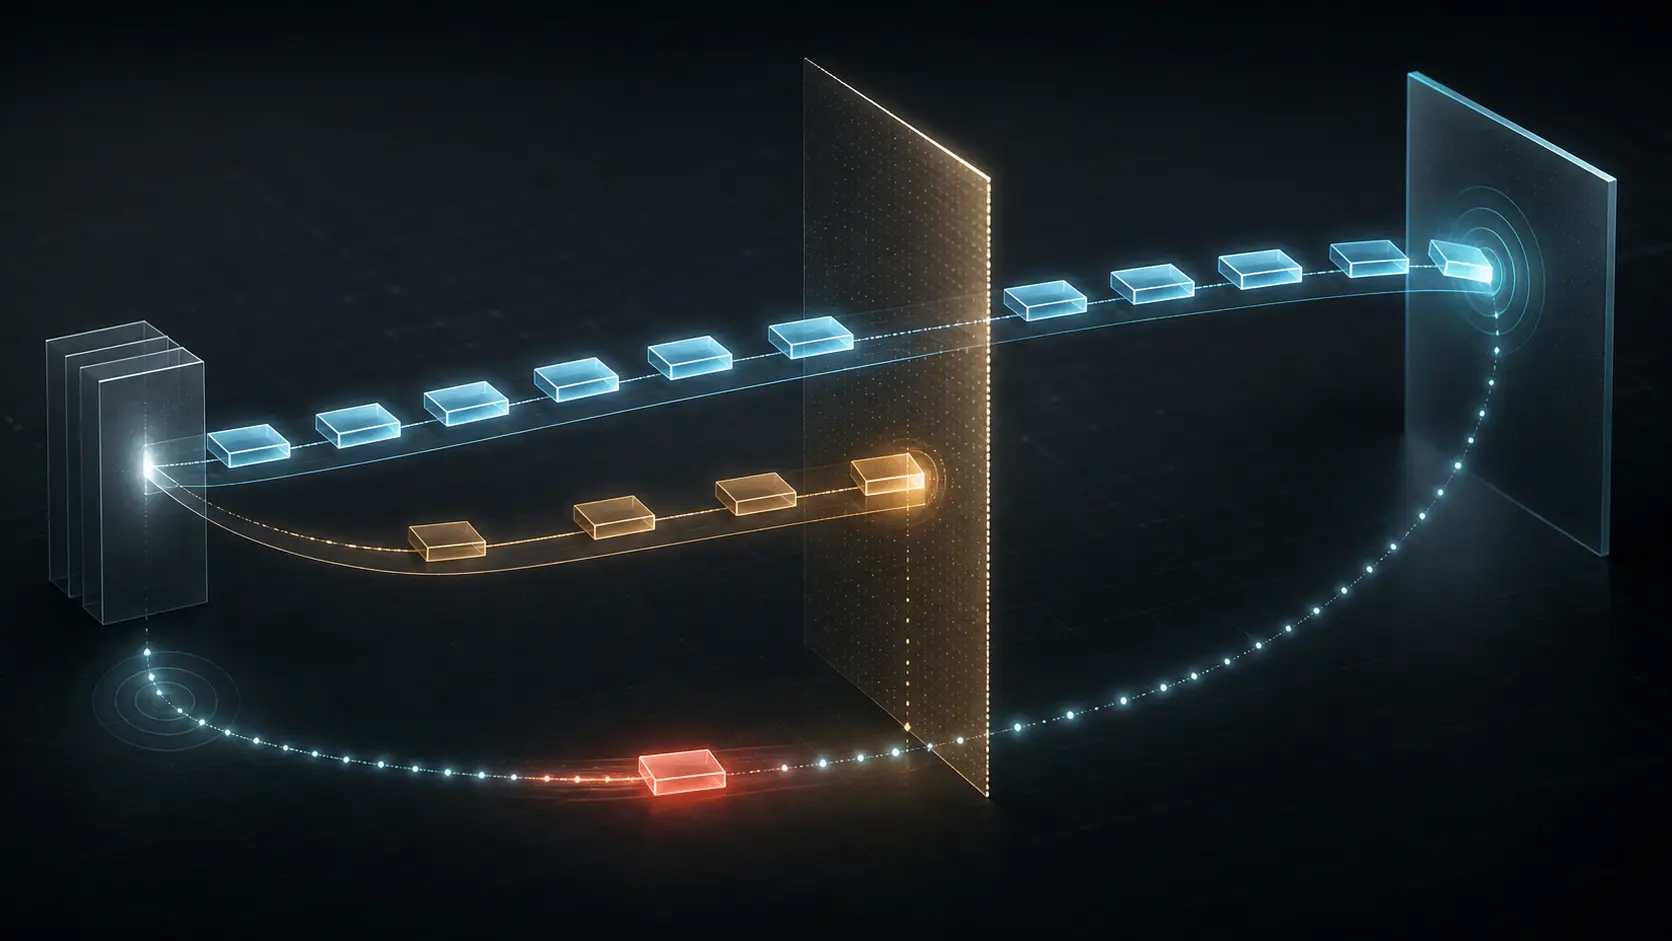
The Newer Packet Arrived First: How TCP RACK Used Time to Find Loss
RACK changes the evidence TCP can use when looking for loss: not only sequence-space gaps, but also the transmission times of data known to have arrived.

IETF
A Device-Assignment Token Can Carry Evidence. It Cannot Carry a Relying Party’s Decision.
RATS is asking whether it should adopt a draft that describes an EAT profile for assigning a device to a confidential virtual machine. The question is useful and bounded. It concerns a text, `draft-poirier-rats-eat-da-10`, and the possibility of working-group work. It does not…

AFNOG
AfNOG Publishes Host Preferences but Makes the Convenors’ Choice Final
AfNOG’s public hosting page gives a prospective Africa Internet Summit host an unusually detailed list of obligations. It also publishes three selection preferences. What it does not publish is how those preferences are compared before AfNOG Convenors and AFRINIC Management make…
IETF
Colin Perkins and the Sent Event That Did Not Say Transmitted
A local transport API can report that it has finished with a message while the network has not yet made the message observable anywhere else. RFC 9622, co-authored by Colin Perkins, makes that boundary unusually explicit: a `Sent` event marks a handoff below the API, not a…
IETF
Marco Tiloca and the Revocation Notice That Did Not Withdraw Access
An authorization server can place a token on a revocation list and send a notification while a constrained resource server has not yet learned the change. RFC 9770, co-authored by Marco Tiloca, creates a disciplined way to distribute that information in ACE. It does not collapse…