
Content Type
Briefing
Within the Content Type facet, Briefing intelligence gathers BTW.MEDIA articles that share the same editorial format, helping readers compare briefings, profiles, risk notes, market analysis, and event coverage without mixing different kinds of evidence. The page explains how this content type frames internet infrastructure events, company movements, governance decisions, operational signals, and public evidence across the site. Readers can compare which actors or infrastructure systems appear most often, how source quality changes interpretation, and whether the material is a durable profile, a time-sensitive event, a strategic market signal, or a governance development. The result is a useful search page for operators, investors, customers, analysts, and policy stakeholders who need to understand the consequence, timing, and evidence behind similar article formats.
CASE FILE
The Redirect Stayed Reachable. RRDP Still Had to Reject the Session
RFC 9674 gives an RRDP notification a precise authority boundary: its scheme, host and port constrain every Snapshot, Delta and redirect target. A resource can be fast, available and byte-perfect yet remain outside that boundary. Conversely, staying inside it proves authorized…
Story
AFRINIC Logs Four Fliber Blocks to Level 7; BGP’s Origin Shifts Later
AFRINIC records a 24 September transfer event involving four IPv4 prefixes. RIPE NCC’s route collectors later observed a different origin for those prefixes, but the two records do not establish that the transfer caused the routing change.

CASE FILE
A Web API Call Is Not a Browser Permission
A page can ask a browser for a capability. The moment of asking is visible in application code; the point at which the browser decides what to allow is a different event. A revised W3C draft now draws that distinction into its simplest Web threat model.

IETF
One Recipient Decrypted the JWE. The Recipient Policy Was Still Undecided
The new HPKE profile for JSON Web Encryption can return plaintext after one recipient path succeeds. In a multi-recipient envelope, that is the cryptographic floor. It is not yet the organisation’s answer to who was required to succeed, which algorithms were acceptable, or…

CASE FILE
The Probe Arrived. That Did Not Mean Any Router Processed the Option
RFC 9673 makes IPv6 Hop-by-Hop Options more practical by allowing routers to protect forwarding capacity and process only what local policy enables. That pragmatism changes the evidence question: successful delivery can show that a packet crossed one observed path, but not which…
CASE FILE
YAML-LD’s New Security Warning Puts the Parser Outside the Conformance Claim
A few lines of linked-data YAML can become a much larger tree before an application sees the data it intended to check. W3C’s latest draft makes that risk explicit, but the implementation decision remains with the operator.

IETF
SATP’s Final Receipt Is Signed. The Proof Beneath It Is Still Network-Specific
An auditor can reconstruct SATP’s gateway conversation from a chain of signed, hash-linked messages. The harder question begins one layer lower: which record proves that each asset network actually reached the state the gateways asserted, and which record lets a replacement…

CASE FILE
The Standard Changed Custody. None of the Access Points Rebooted
RFC 9672 moved future maintenance of Opportunistic Wireless Encryption from the IETF to IEEE 802.11. The handoff is real; so is its limit. Institutional authority can move in one document, while products, certifications, configurations and live associations remain exactly where…

IETF
JOSE Put Three Security Goals at the Registry Gate. That Is Not a Deployment Verdict
The most consequential part of a new JOSE Last Call is easy to miss behind the two legacy algorithms in its title. The draft would give registry reviewers three explicit security goals for future algorithms—and, in one case, require them to judge the encryption process as a whole…
CASE FILE
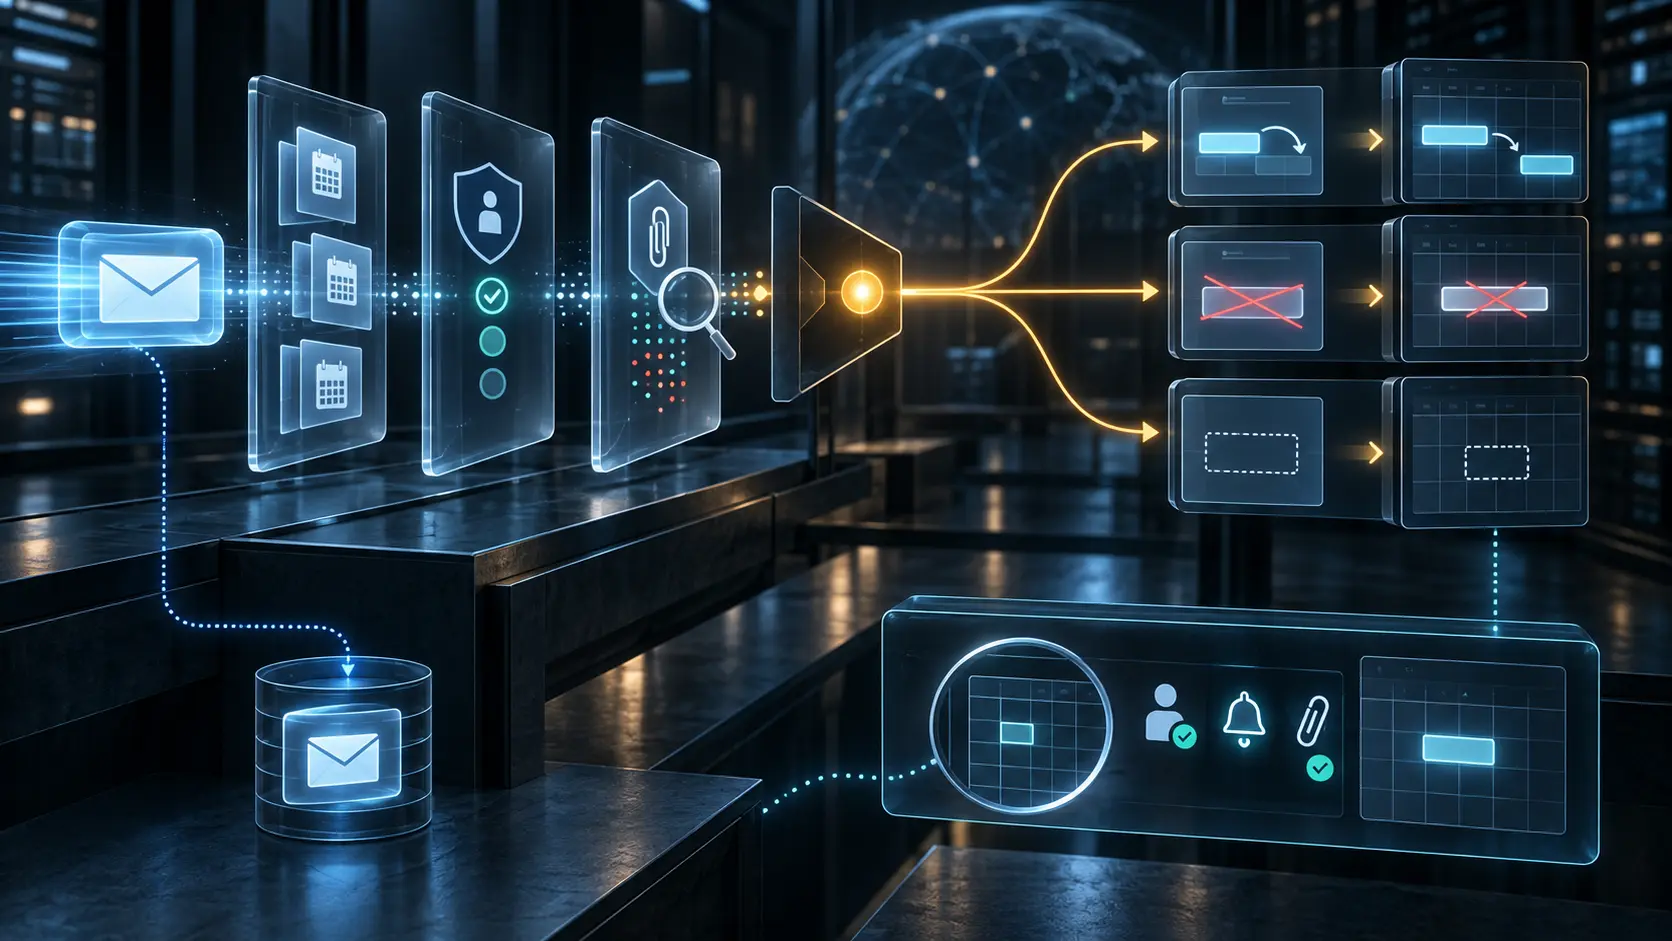
The Outcome Said Updated. The Event Had Actually Been Deleted
RFC 9671 gives Sieve a disciplined way to process calendar attachments, but its `updated` result deliberately covers update, cancellation and removal. For leadership, that is the point where a useful automation signal must stop pretending to be a complete mutation receipt.
CASE FILE
GPC’s Public Support File Is Not a Receipt for a Privacy Choice
The W3C’s latest Global Privacy Control Working Draft describes a request a browser can send and a declaration a website can publish. Neither record, on its own, says what happened to the person’s data after the request arrived.

Asia-Pacific Cloud Services
NxtGen's AI infrastructure bet: real GPUs, contested money
NxtGen Datacenter & Cloud Technologies Private Limited, a Bengaluru-headquartered enterprise cloud and data-centre provider, has delivered 512 of the roughly 1,000 GPUs it committed to India's IndiaAI Mission, according to BW Businessworld on 1 July 2025 — yet the funding round…

IETF
One Network Function, Four Security Jobs: The Certificate Portfolio RFC 9509 Left Local
A 5G Network Function may authenticate a TLS peer, sign its own client assertion, receive protected inter-operator JSON and rely on an OAuth access token. RFC 9509 names three missing certificate purposes, but it does not choose whether those jobs share one credential.

CASE FILE
The Share Was Saved. The Intended User Still Could Not Open the Object
RFC 9670 gives collaborative systems a common JMAP vocabulary for Principals, rights and sharing changes. Its cleanest operational lesson is also its limit: a stored share is one control-plane fact, not proof of identity, visibility, enforcement, revocation or user outcome.

ICANN
Who Controls the .jp Registry? The Instrument Chain Above JPRS
Japan Registry Services Co., Ltd. (JPRS) sits at the center of a layered control surface for the .jp country-code top-level domain: IANA and ICANN grant its international authority, JPNIC and Japan's government can challenge it, and a 2025–2026 evaluation cycle plus a second…
Europe and Middle East Regional ISP
AS210837: a registry record without a network, read only through its mirrors
AS210837: a registry record without a network, read only through its mirrors intelligence summary explains the development, the public evidence available to readers, the organisations involved, the regional context, market exposure, and the infrastructure consequences that may…
Story
RIPE NCC’s Geneva Briefing Invoked Measurable Progress, Without Naming a Measure
At a 17 September session co-hosted with the ITU and the Permanent Mission of Lebanon in Geneva, the RIPE NCC placed the RIR function between digital-policy goals and operational delivery. Its post-event account describes partnerships, capability and capacity building as routes…

IETF
The Byte Was the Same. The Timeout Was Not: RFC 9510
A one-byte CCNx lifetime can mean a fraction of a second to one forwarder and years to the next. RFC 9510 buys a wide time range without buying a new TLV—and makes software-version identity part of the evidence.
CASE FILE
The Runtime Said It Supported BPF. The Program Never Reached the Hook
A compiler selected an atomic instruction from a capability label, the loader returned a program identifier, and the release dashboard called the policy active. None of those facts proved that the intended hook had accepted that program generation.

CASE FILE
NIST’s Multi-Cloud Draft Exposes the Boundary a Service Bundle Cannot Prove
A managed bridge between cloud providers can move integration work away from a customer. It cannot, by itself, establish which system, control and evidence an authorizing decision actually covers. NIST’s draft asks readers to confront that distinction.