- ESpanix has deployed Nokia Deepfield Defender across its Madrid and Barcelona internet-exchange infrastructure
- The optional service lets participating networks filter identified DDoS traffic inside the exchange instead of always diverting it to an external scrubbing centre
The fact
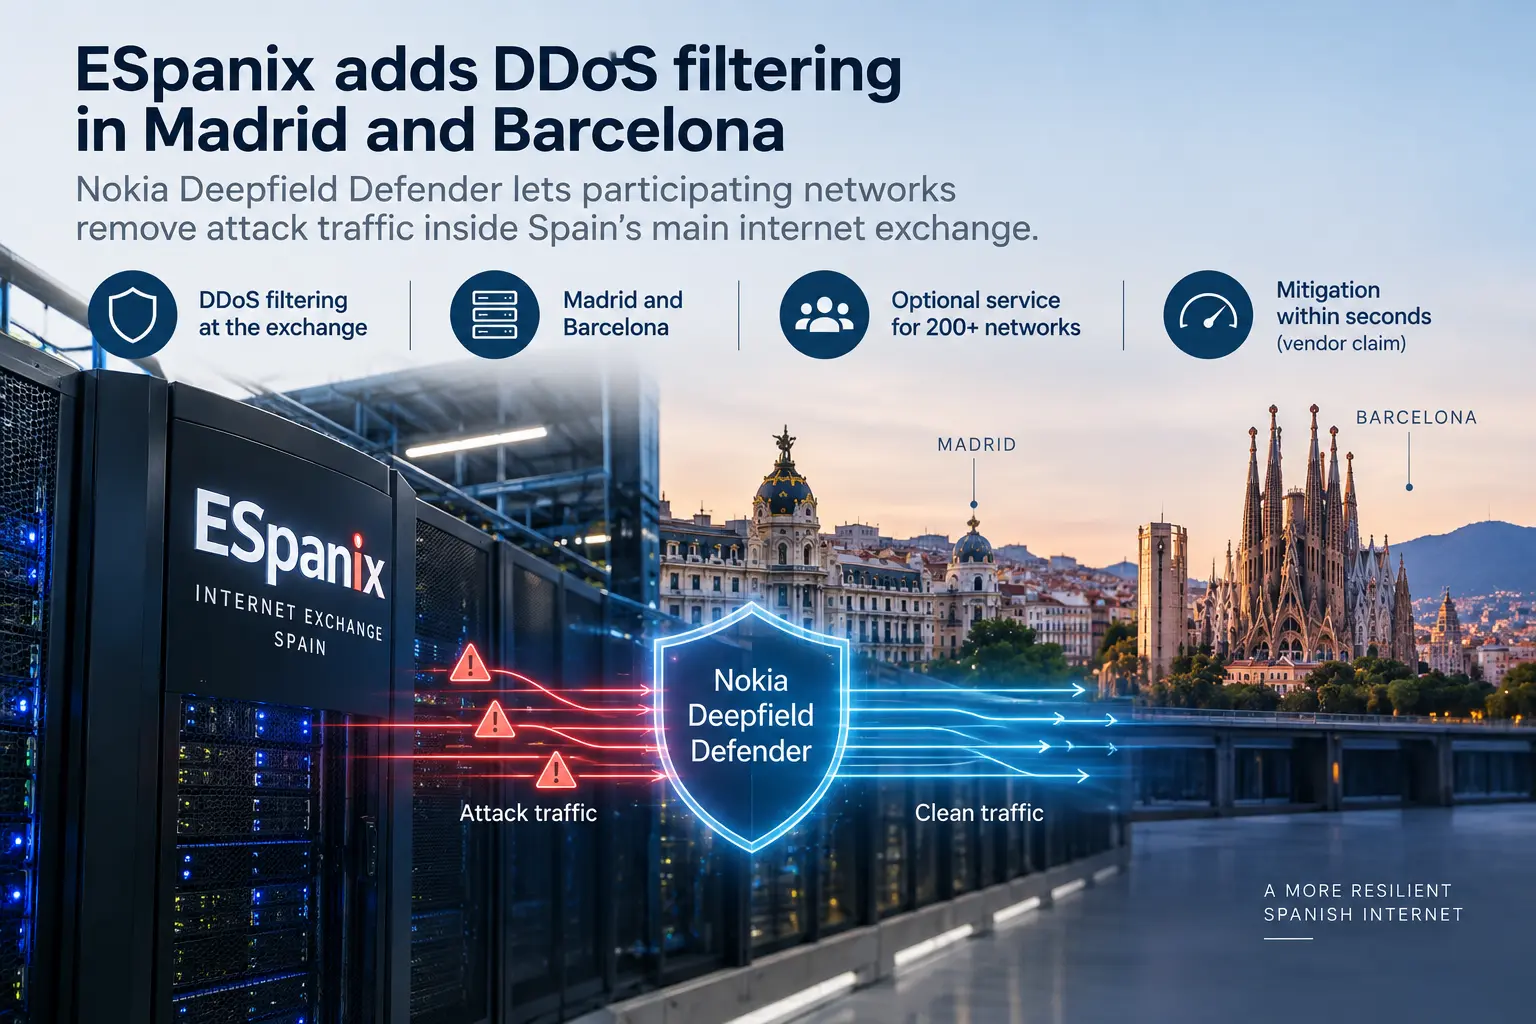
ESpanix has deployed Nokia Deepfield Defender across its internet-exchange infrastructure in Madrid and Barcelona. The optional DDoS-protection service is available to more than 200 national and international networks connected to the exchange.
Deepfield Defender analyses network telemetry alongside Nokia's security intelligence to identify attack traffic. It can then instruct network equipment to drop that traffic while allowing legitimate packets to continue. Nokia says detection and mitigation can take place within seconds, although that is a vendor performance claim rather than a guarantee for every attack.
ESpanix says mitigation can take place within its Spanish infrastructure across six data-centre locations. That means participating networks can filter some attacks without first diverting their traffic to a third-party scrubbing centre. The service only covers traffic that reaches the relevant ESpanix infrastructure and does not replace security controls inside a member's own network or applications.
The assessment
ESpanix is moving one part of DDoS defence closer to the point where its members exchange traffic. When an attack arrives through the exchange, identified traffic can be dropped there instead of being sent to a remote scrubbing centre and then returned after cleaning. That can simplify the response path for traffic already crossing ESpanix.
The limit is coverage. Many operators reach the internet through several exchanges and transit providers, and ESpanix cannot filter traffic that arrives by another route. A member protecting the same public service through several connections may still need upstream or on-network DDoS protection elsewhere.
For BTW readers, the service becomes useful when operators know which prefixes and routes it protects and how it works alongside their existing defences. Controlled tests should show whether attacks arriving through ESpanix are removed quickly without disrupting legitimate traffic, while separate routes remain covered by other measures.
What to watch
Watch how many ESpanix members adopt the service and how it performs during controlled tests or real attacks. Mitigation time, legitimate-traffic impact and the handling of attacks arriving through other exchanges or transit providers will show how much of a member's exposure the service actually covers.
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance