
Summary
- RFC 3053 separated a user-facing Tunnel Broker, which authorized requests and ordered configuration, from Tunnel Servers, which terminated IPv6-over-IPv4 tunnels and carried traffic.
- A successful registration, allocation, DNS update or configuration response did not prove that both endpoints applied compatible state, that the IPv4 underlay passed the encapsulation, or that any application exchanged data.
In January 2001, getting an isolated host onto the emerging IPv6 Internet could require a network administrator to build a configured tunnel by hand. The user already had IPv4 connectivity. The missing part was an IPv6 link across it: endpoint addresses, a prefix, routes, tunnel interfaces and often DNS records. Each new user could create another small configuration project.
RFC 3053 proposed turning that project into a service. A user would contact an IPv4-reachable Tunnel Broker, authenticate, provide an IPv4 endpoint and receive the parameters needed to activate IPv6. The attraction was real. Automation could replace a queue of hand-edited tunnel requests.
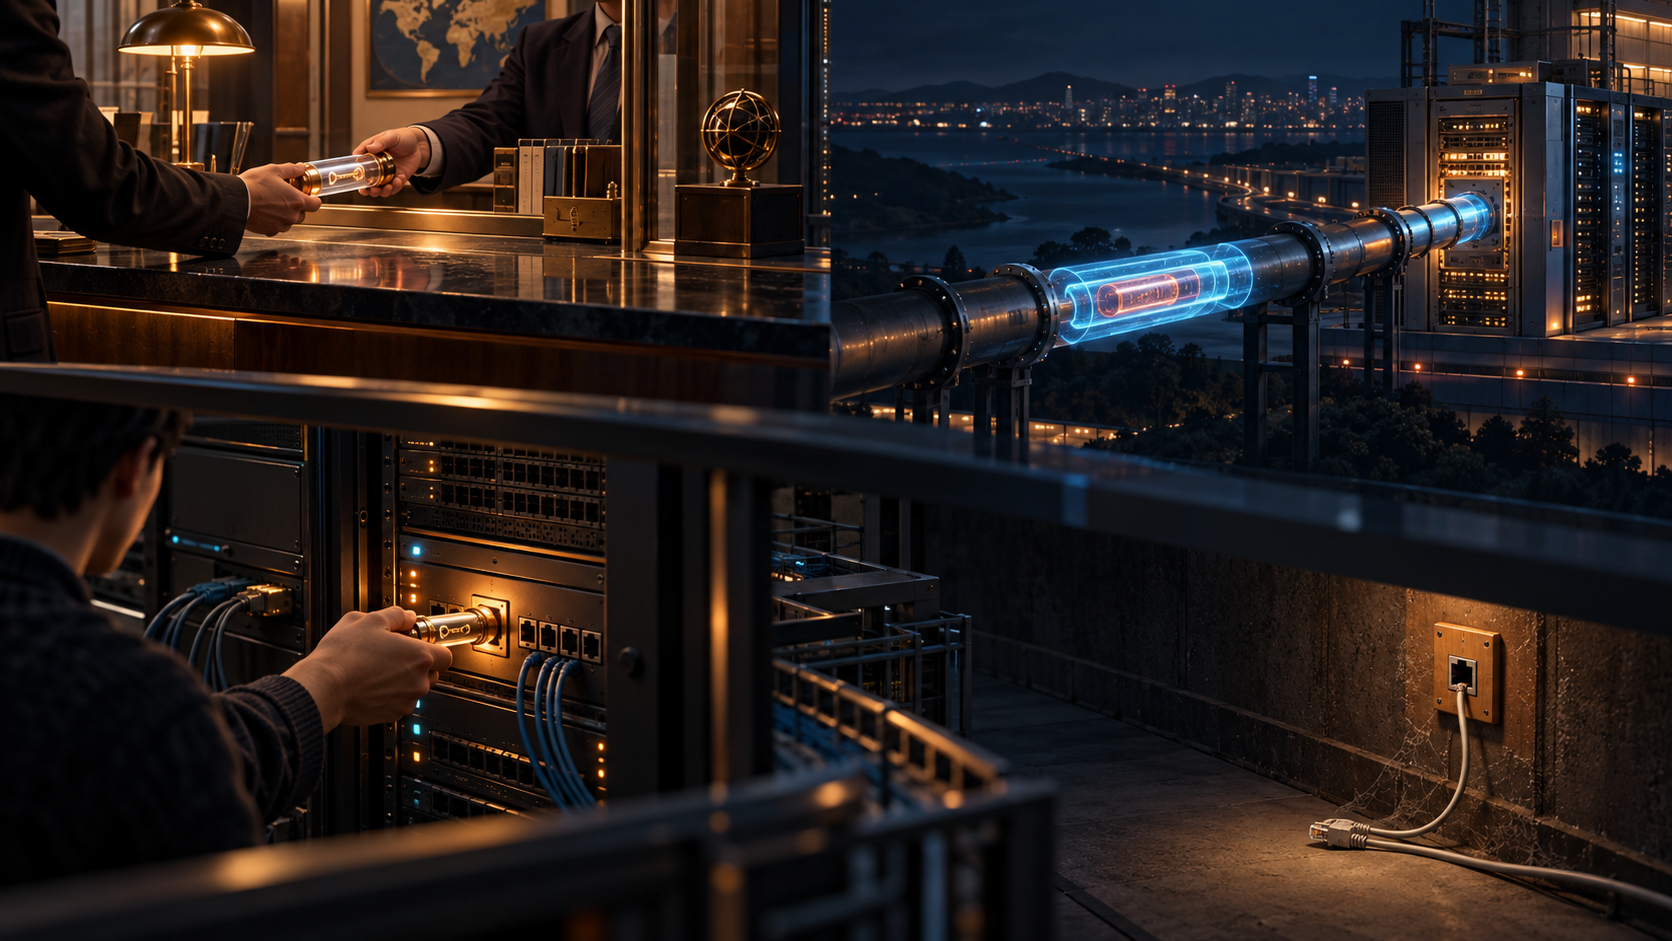
But the document, published as Informational, did not specify a new protocol. It described a framework. Its most durable contribution may be the way that framework separated the friendly front desk from the machines and networks that had to make the promise true.
The broker was a control point, not necessarily the packet path
RFC 3053 gave the Tunnel Broker three central duties. It was where users registered and activated service. It managed creation, modification and deletion. And it distributed network-side endpoints among one or more Tunnel Servers, sending orders to whichever server it selected.
The Tunnel Server had a different role. It was a dual-stack router connected to the Internet. When instructed by the broker, it created, changed or removed its side of a tunnel. It could also report usage statistics for active tunnels. The IPv6-over-IPv4 data path ran between the client and this server, not through the broker merely because the broker owned the account page.
That split allowed scale. One administrative service could allocate work across several forwarding devices. It also divided evidence. A broker database row proved that the broker recorded an intention. A successful management message showed that an order was delivered. Server state showed that one endpoint was configured. None of those receipts alone demonstrated compatible state at the client, a usable IPv4 path or a returned IPv6 packet.
The architecture resembles many later control-plane services: the easiest interface is often several layers away from execution. A green provisioning page may be accurate about its own transaction and still know nothing about the last packet.
Authorization came before parameters
The client was expected to be a dual-stack host or router already attached to the IPv4 Internet. It first supplied identity and credentials so the broker could authenticate, authorize and optionally account for service use. RFC 3053 mentioned existing AAA facilities such as RADIUS and described the broker as an access-control server for IPv6 users connected through IPv4.
After authorization, the client supplied at least three things: its IPv4 tunnel endpoint, a name for DNS registration and whether it acted as a standalone host or a router. The broker then selected a Tunnel Server, chose an IPv6 allocation, fixed a lifetime, could update DNS, configured the server endpoint and returned tunnel parameters and names to the client.
Each verb had a bounded subject. Authentication supported the decision to let an account request service. It did not prove that the supplied IPv4 address belonged to the user, remained reachable or could pass the encapsulated traffic. Allocation reserved IPv6 coordinates inside the broker's service. DNS registration published a name. Neither one configured the remote host.
The client still had to install its side. Only after the broker's decisions, the server's action and the client's action did the RFC describe the tunnel as up and working. Even then, “working” in the architecture was a design outcome, not a packet trace from every implementation.
A script made installation easy by borrowing root
The framework considered a simple way to finish the client side: the broker could generate personalized activation and deactivation scripts for the user to run. This required no new client software. It also transferred a large amount of local authority into a downloaded artifact.
Changing tunnel interfaces requires administrative privilege. RFC 3053 warned that users might struggle to verify whether the script performed illegal or dangerous operations once executed. Its alternative was a structured MIME type carrying tunnel parameters over HTTPS, interpreted by a trusted local component. The document sketched that safer direction but left its definition to later work.
This was not merely a user-interface choice. A script combined instructions, executable authority and a particular operating-system environment. A parameter object separated the requested state from the local code authorized to apply it. Both could automate configuration, but they placed trust and review at different boundaries.
The same issue appeared behind the broker. Broker-to-server management might use protected RSH commands, secure SNMP or another system. Broker-to-DNS updates might use Dynamic DNS Update or protected commands. RFC 3053 did not collapse them into one protocol. The security and success of each link depended on its implementation.
A stable IPv6 identity sat on a changing IPv4 floor
The design aimed to give users relatively long-lived IPv6 addresses and DNS names even when their IPv4 connection was dial-up and dynamically addressed. On reconnect, a user could contact the broker, rebuild the tunnel against a new IPv4 endpoint and reuse the earlier IPv6 allocation.
That was a useful separation. The upper-layer address and name did not need to change merely because the lower-layer access address did. But continuity became a coordinated operation rather than a property of the IPv6 string. The broker had to retain the allocation, recognize the returning user, select a server, replace endpoint state, update any affected records, and deliver new client configuration. The underlay still had to reach the new address.
A persistent IPv6 address was therefore not a persistent path. It was a promise backed by records and reconfiguration. If the broker record survived but the user did not reconnect, the stored allocation proved history, not reachability.
Lifetime was cleanup policy, not proof of life
Active tunnels consumed memory and processing time on Tunnel Servers. RFC 3053 recommended giving each tunnel a lifetime and deleting it at expiry unless the client requested an extension. That bounded abandoned state, but it fit dynamic dial-up service poorly: a tunnel might remain recorded long after the IPv4 session ended.
The framework considered traffic and reachability statistics, inactivity deletion and keep-alives. These could help a broker retire unused tunnels earlier. They still had to be interpreted carefully. Silence might mean disconnection, filtering, an idle user or a broken return path. A counter could show bytes without proving the intended subscriber was still at the endpoint. A keep-alive receipt could establish a narrow moment, not continuing application delivery.
The risk was sharper than wasted capacity. If a dial-up user disconnected without tearing down the tunnel, the server could continue sending IPv6 traffic toward the old IPv4 address. The ISP might already have assigned that address to another subscriber. A stale mapping could therefore become a confidentiality failure.
The broker needed more than an expiry calendar. It needed current authority over who occupied the endpoint.
NAT revealed the underlay's veto
RFC 3053 stated a blunt limitation: the mechanism might not work when the user held a private IPv4 address behind a NAT device. The broker could accept a form, authenticate an account and allocate IPv6 space while the underlay still refused the tunnel.
The problem illustrated the difference between naming an endpoint and reaching it. A private address might be meaningful inside the user's network but not as the remote coordinate a public Tunnel Server could use. An intervening device might not pass protocol 41 as required. Neither the broker's control-plane confidence nor its DNS state changed that forwarding fact.
Later tunneling and setup mechanisms addressed other environments and automated more negotiation. They should not be projected backward into RFC 3053. A framework that identified an underlay constraint did not thereby solve it.
Access control did not secure the carried conversation
The RFC required all three administrative interactions—client to broker, broker to Tunnel Server and broker to DNS—to be secured. HTTPS, ordinary credentials, AAA, secure SNMP and IPsec-protected management were among the implementation possibilities.
Those protections guarded service control. They did not automatically protect the IPv6 packets inside the configured tunnel. Authentication answered whether an account could ask the broker to act. It did not encrypt every application packet, authenticate every IPv6 peer or authorize every route reached through the service.
The distinction matters because the same system exposed several authorities. A user could be authorized to request a tunnel. The broker could be authorized to configure a server. The broker could separately be authorized to update a DNS zone. The server could forward packets according to its routes. None of these permissions inherited all the others.
RFC 3053 also anticipated denial of service against the provisioning layer: a malicious user could exhaust Tunnel Server resources by requesting many tunnels. Per-user limits were one suggested defense. Automation reduced operator labor while making the request interface itself a resource-control surface.
A configured tunnel was still a chain of receipts
Later standards supplied more details. RFC 4213 specified configured tunneling behavior. RFC 4891 discussed protecting configured tunnels with IPsec. RFC 5572 defined a concrete Tunnel Setup Protocol. RFC 7059 compared tunnel families and their operational trade-offs. These documents illuminate the design space; they do not prove that an RFC 3053 deployment gained every later feature.
The historical lesson is narrower. The broker made tunnel provisioning legible and repeatable. It did not merge the people and machines involved. Account registration, authorization, address allocation, DNS publication, server configuration, client configuration, IPv4 passage, IPv6 routing, reverse reachability and application success remained separate state transitions.
The front desk could order the tunnel. Another machine had to carry it. The packet was the receipt that neither one could issue in advance.
Sources
- RFC Editor record for RFC 3053
- RFC 3053 in HTML
- RFC 3053 in text
- RFC 1933: Transition Mechanisms for IPv6 Hosts and Routers
- RFC 2473: Generic Packet Tunneling in IPv6
- RFC 2529: IPv6 over IPv4 Domains without Explicit Tunnels
- RFC 2893: Transition Mechanisms for IPv6 Hosts and Routers
- RFC 3056: Connection of IPv6 Domains via IPv4 Clouds
- RFC 4213: Basic Transition Mechanisms for IPv6 Hosts and Routers
- RFC 4891: Using IPsec to Secure IPv6-in-IPv4 Tunnels
- RFC 5572: IPv6 Tunnel Broker with Tunnel Setup Protocol
- RFC 6180: Guidelines for IPv6 Transition Mechanisms
- RFC 7059: A Comparison of IPv6-over-IPv4 Tunnel Mechanisms
- Lu Heng on Running-Code Primacy
- Lu Heng on Minimum Initial Specification
- Lu Heng on Reality Layers
Lu Heng did not author or endorse RFC 3053 or the related standards. His essays are used here as disclosed analytical lenses.
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance