
Summary
- Revision 01 of Anti-Money Laundering Methods Values, dated 2 October 2026, adds that an
amlclaim value means use of the named method succeeded. The proposed array can name OFAC compliance, sanctions, watchlist, politically exposed persons and adverse-media screening. - A successfully executed method is not a clean result, a resolved match, proof of legal compliance or permission to serve a customer. The proposed claim carries no disposition vocabulary and none of the evidence coordinates needed to reconstruct that judgment.
A compliance engine can finish its job and leave the important question unanswered. That is the ambiguity introduced into portable form by draft-skyfire-oauth-aml-methods-01.
The draft proposes an aml JSON array of case-sensitive strings. Its initial vocabulary is compact: ofac, sanc, watch, pep and adv. Revision 01 adds that presence of a value indicates that use of the corresponding anti-money-laundering method succeeded. Like the established amr authentication-method claim, the field reports which method families were used.
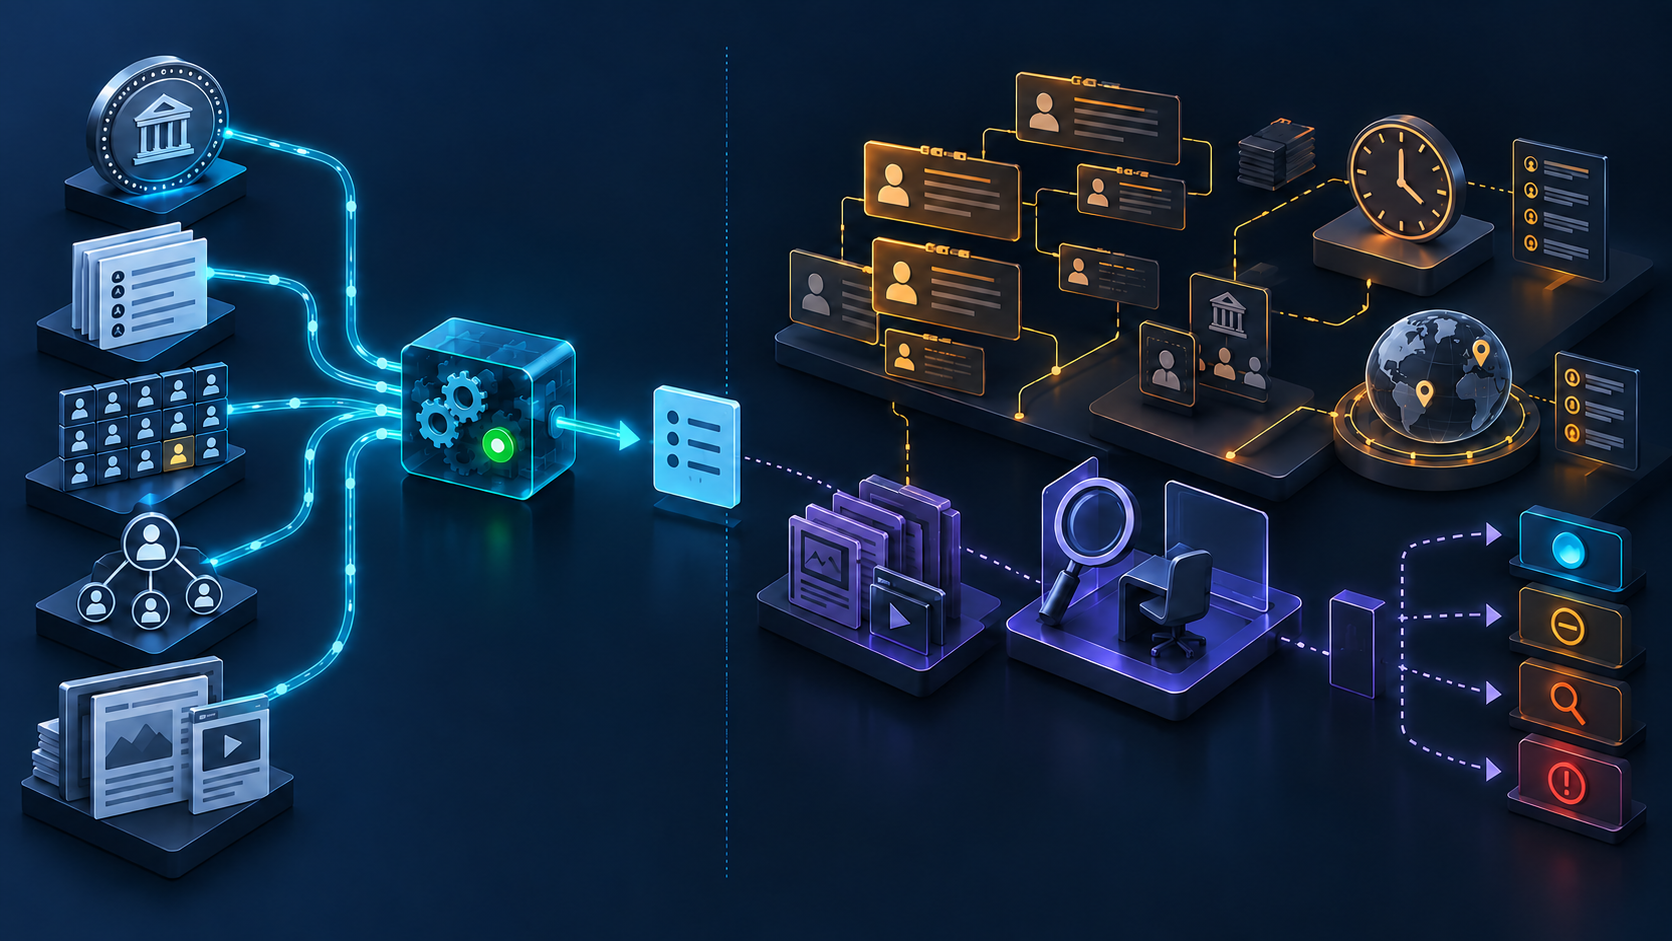
That can be useful interoperability. One system no longer has to guess whether another means sanctions screening, a watchlist check, a politically exposed person review or adverse-media screening. Logs can be searched, assertions can be compared and downstream systems can ask whether a required family of checks was invoked.
But the word “succeeded” has two possible audiences. To an engineer, it can mean the process completed without an execution error. To a business user, auditor or receiving system, it can sound like the person or transaction passed. The draft defines the former data shape and supplies no separate result or disposition field capable of establishing the latter.
Consider sanc. The value does not identify the sanctions regime, list publisher, programme, jurisdiction, list version or retrieval time. It does not record the subject identifiers, aliases, transliterations, beneficial owners or counterparties that were queried. It does not expose the similarity threshold, candidate hits, false-positive analysis, unresolved ambiguity or human reviewer. It does not say proceed, restrict, escalate, investigate, report or reject.
Those omissions are not evidence that the proposal is defective. They show that the claim is a method vocabulary, not a compliance case. The risk begins when a receiver treats the small field as if it were the larger judgment.
The official compliance material makes that distinction concrete. OFAC's Framework for Compliance Commitments describes a risk-based sanctions programme through management commitment, risk assessment, internal controls, testing and auditing, and training. Its internal controls include identifying, interdicting, escalating, reporting and keeping records. The framework's appendix points to screening-software faults, stale lists, missing identifiers, alternate spellings, incomplete due diligence and weak escalation among root causes seen in apparent violations.
An aml value cannot compress those controls into a proof of compliance. A filter can execute exactly as configured while using yesterday's list. A name can return no candidate because the transliteration was absent. A provider can produce a candidate that another threshold suppresses. A reviewer can resolve the same evidence differently under a different jurisdiction or risk appetite.
Time matters as much as method. OFAC FAQ 65 tells insurers to consider screening at several events, including issuance, renewal, amendment, claim submission, claim payment and updates to sanctions programmes or lists. It notes that lists change frequently. A truthful assertion that screening succeeded at onboarding does not answer what was known when a later payment was made.
Customer due diligence is also a continuing relationship, not one checkpoint. FinCEN describes four core elements: identify and verify customers; identify and verify beneficial owners for covered legal-entity customers; understand the nature and purpose of the relationship to form a risk profile; and conduct ongoing monitoring to identify and report suspicious transactions and maintain or update customer information on a risk basis. Its consolidated FAQs make the updating trigger event- and risk-dependent rather than a universal periodic reset.
Jurisdiction cannot be inferred from a generic code either. The European Commission's sanctions overview separates adoption and publication of EU measures from investigation, implementation, enforcement and penalties by Member States, while the Commission monitors and provides guidance. sanc cannot say which authority, law, licence, exception or enforcement practice governed a particular decision.
The proposed IANA machinery has a narrower purpose. Revision 01 requests an aml JWT claim and a registry of method values, with Expert Review, three weeks of list review and criteria such as non-duplication, general applicability, actual use and a clear description. Those criteria can improve the vocabulary. They do not accredit a screening provider, validate its data, approve a threshold or turn a method name into a legal conclusion.
The active IANA registries remain authoritative for real allocations. At the frozen capture, the JWT Claims registry contains no aml claim and there is no active Anti-Money Laundering Methods registry. The table in the individual Internet-Draft is proposed initial content. The Datatracker record has no stream, intended standards level or standards level; the OAuth discussion venue is not Working Group adoption or IETF consensus.
A signed JWT does not close the gap. Correct validation can establish which issuer made the assertion and whether included claims were altered. It cannot reveal the list, subject-resolution inputs, hits, review or legal reasoning that the issuer did not include. Cryptographic integrity protects the statement; it does not enlarge it.
The operational answer is to preserve a separate screening receipt. Record the exact token and vocabulary version, issuer, subject and transaction binding, method values, provider and policy version, jurisdiction and legal basis, list or dataset version and retrieval time, identifiers and aliases, threshold and candidates, evidence reference, reviewer and escalation, false-positive disposition, risk classification, exceptions, monitoring horizon, later correction or revocation, and the final local action.
That receipt is BTW editorial guidance, not text required by the draft or a regulator. Its purpose is to stop a portable method code from becoming portable clearance. If a list changes, a false positive is appealed, a beneficial owner changes, a provider is replaced or an authority asks why service continued, the relying organisation can reconstruct its own decision.
Heng Lu's Minimum Initial Specification provides the right governance posture: standardise the smallest useful vocabulary while leaving consequential judgment local. Running-Code Primacy asks which lists, rules, identifiers and review paths actually ran. Reality Layers prevents a registry term, issuer assertion, candidate match, reviewer disposition, legal conclusion and application outcome from collapsing into one green status.
The aml claim can coordinate systems. It cannot carry their accountability. Let method success mean that the method ran. Make clearance, restriction and reporting separate propositions with their own evidence and owner.
Sources
- https://datatracker.ietf.org/api/v1/doc/document/draft-skyfire-oauth-aml-methods/
- https://datatracker.ietf.org/doc/draft-skyfire-oauth-aml-methods/
- https://datatracker.ietf.org/doc/draft-skyfire-oauth-aml-methods/history/
- https://datatracker.ietf.org/wg/oauth/about/
- https://finance.ec.europa.eu/eu-and-world/sanctions-restrictive-measures/overview-sanctions-and-related-resources_en
- https://heng.lu/minimum-initial-specification-localized-future-decision-voluntary-adoption-internet-coordination-system/
- https://heng.lu/on-reality-layers-symbolic-power-and-why-clarity-feels-so-hostile/
- https://heng.lu/running-code-primary-the-patch-needed-to-preserve-the-internet-original-design/
- https://ofac.treasury.gov/faqs/65
- https://ofac.treasury.gov/faqs/topic/1596
- https://ofac.treasury.gov/media/16331/download?inline
- https://ofac.treasury.gov/sanctions-list-service
- https://openid.net/specs/openid-connect-core-1_0.html
- https://www.fincen.gov/resources/statutes-and-regulations/cdd-final-rule
- https://www.fincen.gov/resources/statutes-and-regulations/cdd-rule-faqs
- https://www.iana.org/assignments/authentication-method-reference-values/authentication-method-reference-values.xhtml
- https://www.iana.org/assignments/jwt/jwt.xhtml
- https://www.ietf.org/archive/id/draft-skyfire-oauth-aml-methods-00.txt
- https://www.ietf.org/archive/id/draft-skyfire-oauth-aml-methods-01.html
- https://www.ietf.org/archive/id/draft-skyfire-oauth-aml-methods-01.txt
- https://www.ietf.org/archive/id/draft-skyfire-oauth-aml-methods-01.xml
- https://www.rfc-editor.org/rfc/rfc7519.html
- https://www.rfc-editor.org/rfc/rfc8176.html
- https://www.rfc-editor.org/rfc/rfc8725.html
Member Briefing
Deeper Profile Context
Sign in with the right membership level to unlock the full briefing and source notes.
Only for Strategic Circle
Strategic Circle
Open to all readers. Unlock profile briefings after joining and signing in.
Join Strategic CircleOnly for Leadership Alliance
Leadership Alliance
For qualified IP-asset owners and management; sign in to unlock alliance briefings.
Join Leadership Alliance